Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Hacker’s Dream: NexPhone Debuts with Triple-OS Boot and 2036 Support NexPhone multi-OS smartphone, Windows 11 Linux Android phone
  • Technology

The Hacker’s Dream: NexPhone Debuts with Triple-OS Boot and 2036 Support

Do Son January 23, 2026 0

Discover the NexPhone: A 2026 breakthrough running Android, Linux, and Windows 11 on a single chip. Built for geeks with support until 2036.

“New” Path of Attack: Fully Upgraded Fortinet Devices Hit by SSO Exploits Fortinet patch bypass 2026, FortiGate SSO authentication exploit SharePoint Zero-Day, China APTs Exploited Vulnerabilities 2023
  • Vulnerability Report

“New” Path of Attack: Fully Upgraded Fortinet Devices Hit by SSO Exploits

Do Son January 23, 2026 0

Fortinet warns of a new Jan 2026 attack path bypassing December’s patches. Attackers use FortiCloud SSO to hijack firewalls. Learn the critical fix.

Wildcard Hijack: TrustAsia Revokes 143 Certificates After LiteSSL Vulnerability LiteSSL TrustAsia certificate revocation, ACME DNS-01 vulnerability
  • Vulnerability Report

Wildcard Hijack: TrustAsia Revokes 143 Certificates After LiteSSL Vulnerability

Do Son January 23, 2026 0

TrustAsia revoked 143 LiteSSL certificates in Jan 2026 after a critical ACME vulnerability allowed domain hijacking. See if your site is affected.

Outlook in Crisis: How to Fix the January 2026 Update Freezing Your Inbox Exfil Out&Look Microsoft 365 Logging Gap Outlook Classic KB5074109 freeze, January 2026 POP3 PST bug Outlook Classic POP3 freeze, KB5074109 Windows 11 bug Outlook, CPU Usage Outlook lag Outlook Lite discontinued
  • Windows

Outlook in Crisis: How to Fix the January 2026 Update Freezing Your Inbox

Do Son January 23, 2026 0

Microsoft's KB5074109 update is freezing Outlook Classic in Jan 2026. Learn how to fix POP3 and PST errors or rollback the update to save your mail.

YouTube’s 2026 Plan to Automate Shorts YouTube Shorts, digital well-being YouTube AI doppelgängers Shorts, Gemini 3 Playables games
  • Technology

YouTube’s 2026 Plan to Automate Shorts

Do Son January 23, 2026 0

YouTube CEO Neal Mohan reveals AI doppelgangers for Shorts and Gemini 3 games for 2026. Discover how the platform is fighting "AI slop" with tech.

Amazon’s Medical Move: New “Health AI” Assistant Turns Data into Doctor Visits Amazon One Medical Health AI, agentic health assistant 2026
  • Technology

Amazon’s Medical Move: New “Health AI” Assistant Turns Data into Doctor Visits

Do Son January 23, 2026 0

Amazon launches Health AI for One Medical in Jan 2026. This agentic assistant uses your medical history to book appointments and explain lab results.

Search Gets Personal: Google Integrates Gmail and Photos into AI Mode Google Search Personal Intelligence, Gemini 3 Search AI Mode Google Ad Redesign, Sponsored Results Visibility
  • Technology

Search Gets Personal: Google Integrates Gmail and Photos into AI Mode

Do Son January 23, 2026 0

Google launches Personal Intelligence in Jan 2026! Search AI Mode now uses your Gmail and Photos to provide hyper-tailored results.

Public Yet Private? Critical Appsmith Flaw Exposes Unpublished Actions (CVSS 9.4) CVE-2026-24042 Appsmith Vulnerability CVE-2026-22794
  • Vulnerability Report

Public Yet Private? Critical Appsmith Flaw Exposes Unpublished Actions (CVSS 9.4)

Do Son January 23, 2026 0

Critical Appsmith flaw CVE-2026-24042 (CVSS 9.4) allows public users to execute private, unpublished actions. Update to v1.95 now to secure your apps.
Public PoC Exploit Released for Critical Android Flaw Grants Apps Permissions Without You Knowing Android CVE-2024-23700 Zero-Interaction Exploit Candiru spyware Android vulnerability, security update
  • Vulnerability

Public PoC Exploit Released for Critical Android Flaw Grants Apps Permissions Without You Knowing

Do Son January 23, 2026 0

Public PoC exploit for Android CVE-2024-23700 allows critical privilege escalation without user interaction. WearOS & Custom ROMs are at risk.

Sabotage & Exploited in the Wild: Critical Backdoor Found in LA-Studio Element Kit CVE-2022-45359 LA-Studio Element Kit Backdoor CVE-2026-0920
  • Vulnerability Report

Sabotage & Exploited in the Wild: Critical Backdoor Found in LA-Studio Element Kit

Do Son January 23, 2026 0

Critical backdoor CVE-2026-0920 in LA-Studio Element Kit is being exploited in the wild. Former employee planted the code. Update to v1.6.0 immediately.
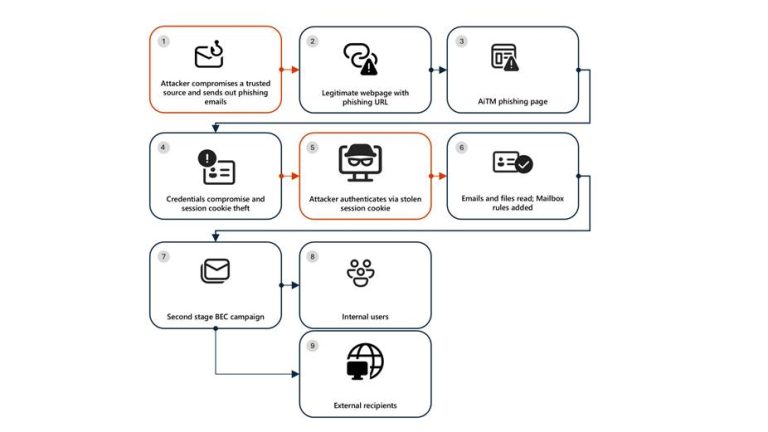
Energy Sector Under Siege: AiTM Phishing Turns Insiders Into Threats AiTM Phishing Energy Sector Business Email Compromise
  • Cybercriminals

Energy Sector Under Siege: AiTM Phishing Turns Insiders Into Threats

Do Son January 23, 2026 0

Microsoft warns of an AiTM phishing campaign targeting the energy sector. Hackers steal session cookies and abuse SharePoint to launch internal attacks.

CVE-2026-23594: High-Severity Flaw in HPE Alletra & Nimble Grants Admin Access HPE AutoPass Vulnerability, CVE-2026-23600 CVE-2024-22442 - HPE vulnerability HPE Storage Vulnerability CVE-2026-23594
  • Vulnerability Report

CVE-2026-23594: High-Severity Flaw in HPE Alletra & Nimble Grants Admin Access

Do Son January 23, 2026 0

HPE warns of critical flaw CVE-2026-23594 in Alletra & Nimble Storage. CVSS 8.8 bug allows remote admin access. Update to v6.1.2.800 now to secure data.

“SymPy” Imposter: Typosquatting Attack Turns Math Library into Crypto Miner sympy-dev Malware PyPI Supply Chain Attack
  • Malware

“SymPy” Imposter: Typosquatting Attack Turns Math Library into Crypto Miner

Do Son January 23, 2026 0

Malicious PyPI package "sympy-dev" impersonates SymPy to install XMRig miners via fileless execution. Check your dependencies immediately.

Mac Users Beware: “MacSync” Malware Tricks You Into Hacking Yourself MacSync Malware macOS ClickFix
  • Malware

Mac Users Beware: “MacSync” Malware Tricks You Into Hacking Yourself

Do Son January 23, 2026 0

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.

Crossing the Andes: Sophisticated Loan Phishing Scams Hit Peru Peru Loan Phishing Luhn Algorithm Scam
  • Cybercriminals

Crossing the Andes: Sophisticated Loan Phishing Scams Hit Peru

Do Son January 23, 2026 0

Group-IB reveals a sophisticated loan phishing campaign in Peru. Scammers use the Luhn algorithm to validate stolen credit cards via fake ads.

CVE-2026-22822: Critical Flaw in External Secrets Operator Breaks Namespace Isolation External Secrets Operator CVE-2026-22822
  • Vulnerability Report

CVE-2026-22822: Critical Flaw in External Secrets Operator Breaks Namespace Isolation

Do Son January 23, 2026 0

Critical External Secrets Operator flaw CVE-2026-22822 (CVSS 9.3) allows cross-namespace secret theft. Update to v1.2.0 now to secure your cluster.

Halo Security Achieves SOC 2 Type II Compliance, Demonstrating Sustained Security Excellence Over Time halo-security-soc-2-type-ii-pr_1769043233sBezxiKdyP
  • Press Release

Halo Security Achieves SOC 2 Type II Compliance, Demonstrating Sustained Security Excellence Over Time

cybernewswire January 22, 2026 0
Miami, Florida, 22nd January 2026, CyberNewsWire
Read More Read more about Halo Security Achieves SOC 2 Type II Compliance, Demonstrating Sustained Security Excellence Over Time
“Enjoy Your Admin Access”: Critical SmarterMail RCE Exploited in the Wild Cisco SD-WAN Vulnerability CVE-2026-20133 FortiGate Compromise Ivanti EPMM Zero-Day CVE-2026-1281 SmarterMail Vulnerability Storm-2603 WatchGuard Zero-Day, IKEv2 Out-of-Bounds Write Cisco Zero-Day, UAT-9686 Chinese APT FortiWeb RCE Exploitation CVE-2025-58034 VMware Zero-Day, Privilege Escalation Sitecore, remote code execution CVE-2025-53690 Windows CLFS, Privilege Escalation CVE-2024-47575 & CVE-2024-11120 CVE-2025-24983 vulnerability
  • Vulnerability Report

“Enjoy Your Admin Access”: Critical SmarterMail RCE Exploited in the Wild

Do Son January 22, 2026 0

Critical SmarterMail flaw WT-2026-0001 allows unauthenticated admin reset & RCE. Attackers are exploiting this in the wild. Update to Build 9511 now.

7 Million Exposed: Critical CVSS 9.8 RCE Vulnerability Hits Laravel Reverb Laravel Reverb Vulnerability CVE-2026-23524
  • Vulnerability

7 Million Exposed: Critical CVSS 9.8 RCE Vulnerability Hits Laravel Reverb

Do Son January 22, 2026 0

Laravel Reverb flaw CVE-2026-23524 (CVSS 9.8) puts 7M apps at risk of RCE via Redis. Update to v1.7.0 or disable scaling now to stay secure.

Beyond the Screen: Apple’s 2027 Plan to Kill Siri and Launch an AI Pin iOS 27 Liquid Glass slider iPhone Flip rumors 2026 Setapp Mobile iOS shutdown, Apple DMA political delay tactics Apple AI pin wearable 2027, Siri Campos Gemini integration Apple AI strategy 2026, Liquid Glass interface Apple Intelligence Mac Pro Cancelled Mac Studio Future App Store antitrust, UK lawsuit iPhone Fold Hinge, Cost Optimization MacBook Pro, OLED display Apple supply chain, manufacturing automation Apple home security, smart camera Apple Earnings, AI Investment Apple EU Fine, DMA Appeal CVE-2023-23529
  • Technology

Beyond the Screen: Apple’s 2027 Plan to Kill Siri and Launch an AI Pin

Do Son January 22, 2026 0

Apple is replacing Siri with "Campos," a Gemini-powered chatbot, and launching an AI pin in 2027. Discover the hardware that could kill the phone.

The Final Piece: Xbox App Hits Windows on Arm, Transforming Copilot+ PCs into Gaming Rigs Windows on Arm Xbox App, Copilot+ PC gaming 2026
  • Windows

The Final Piece: Xbox App Hits Windows on Arm, Transforming Copilot+ PCs into Gaming Rigs

Do Son January 22, 2026 0

Microsoft brings the Xbox App to Windows on Arm! With 85% Game Pass compatibility and AVX2 support, Arm-based gaming handhelds are now imminent.

AI Unleashed: Microsoft Reinvents Notepad and Paint for 2026 Windows 11 Notepad Paint update, AI Coloring Book Paint
  • Windows

AI Unleashed: Microsoft Reinvents Notepad and Paint for 2026

Do Son January 22, 2026 0

Microsoft updates Notepad and Paint in Jan 2026! Discover the new AI Coloring Book, Markdown support, and high-speed text streaming for Windows 11.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-125383CVSS 9.3
    INDOTALENT WHMS (Asp.Net-Core-Inventory-Order-Management-System) before 10.20261109 contains an authentication bypass vulnerability caused by a hard-coded JWT signing key, issuer...
    📅 Updated: Nov 9, 2026
  • CVE-2026-125384CVSS 9.3
    INDOTALENT WHMS before 10.20261109 contains a default credentials vulnerability that allows unauthenticated attackers to gain administrator access because...
    📅 Updated: Nov 9, 2026
  • CVE-2026-125370CVSS 9.3
    Kubero 3.0.0 through 3.1.1 contains an authentication bypass vulnerability that allows unauthenticated remote attackers to forge administrative JWTs...
    📅 Updated: Nov 9, 2026
  • CVE-2026-85295CVSS 9.8
    Chartbrew is an open-source web application that can connect directly to databases and APIs and use the data...
    📅 Updated: Nov 9, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 9, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 9, 2026
  • CVE-2026-125120CVSS 9.8
    Mongoose is a MongoDB object modeling tool designed to work in an asynchronous environment. Prior to 6.13.11, 7.8.12,...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115934CVSS 9.3
    An unauthenticated SQL injection can occur on the front end of any site that uses craft.search to perform a search,...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.