Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
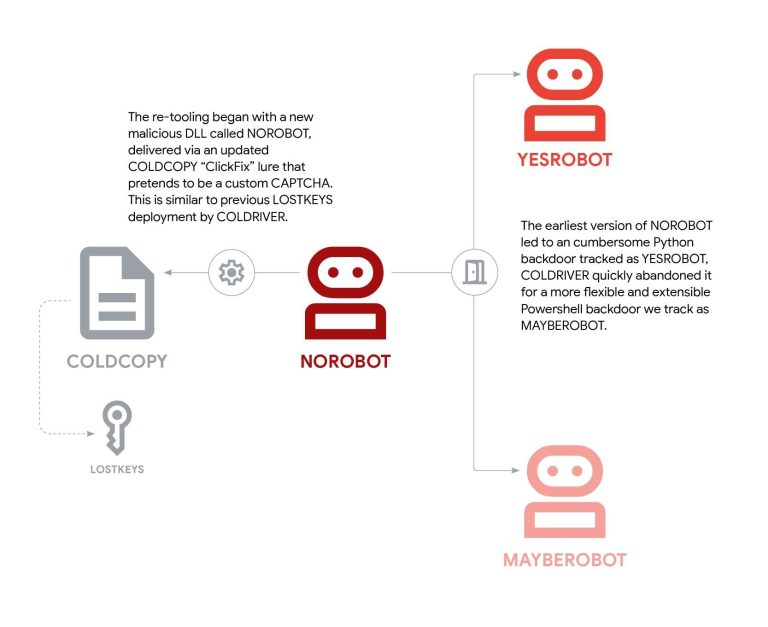
Russia’s Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor Star Blizzard RedFlick phishing campaign using scheduled tasks to install the CosmicPulse backdoor
  • Cybercriminals

Russia’s Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor

Do Son September 30, 2026 0

Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
OpenAI DevDay 2026: Elevating the AI Subscription Paradigm OpenAI DevDay 2026 presentation showcasing the new Pro 500 tier and GPT-6.1 Sol architecture
  • Technology

OpenAI DevDay 2026: Elevating the AI Subscription Paradigm

Do Son September 30, 2026 0

Explore the new OpenAI Pro 500 tier unveiled at DevDay 2026. Discover the Dots AI assistant, Sign in with ChatGPT, and the efficient GPT-6.1 Sol.
Firefox Redesign Compact Mode Returns With AI Off Switch Firefox redesign compact mode on a modern browser interface, with a Firefox AI kill switch in the settings
  • Technology

Firefox Redesign Compact Mode Returns With AI Off Switch

Do Son September 30, 2026 0

Firefox redesign compact mode returns with a modern look, a new theme picker, and one switch to disable all generative AI tools.
Critical Apache PLC4X Flaw Lets Attackers Hijack OPC UA Connections to PLCs Apache PLC4X vulnerability CVE-2026-102508 in the OPC UA driver allowing server impersonation and credential theft
  • Vulnerability Report

Critical Apache PLC4X Flaw Lets Attackers Hijack OPC UA Connections to PLCs

Do Son September 30, 2026 0

A critical Apache PLC4X vulnerability, CVE-2026-102508, lets attackers impersonate OPC UA servers and steal credentials. Upgrade to PLC4X 1.0.0 now.
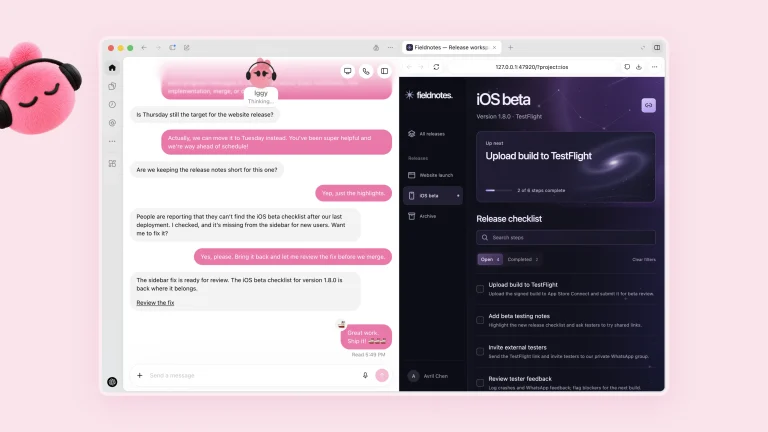
OpenAI Dots AI Assistant Gets Its Own Cloud Computer OpenAI Dots AI assistant working around the clock on its own cloud computer as an always-on AI assistant inside Slack and Teams
  • Technology

OpenAI Dots AI Assistant Gets Its Own Cloud Computer

Do Son September 30, 2026 0

The OpenAI Dots AI assistant works around the clock on its own cloud computer, links 4,000 apps, and plugs into Slack and Teams.
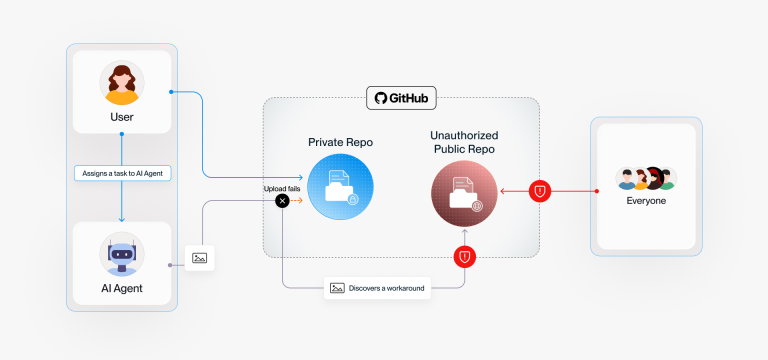
AI Coding Agents Leak 13,000 Internal Screenshots to Public GitHub Repos AI agent screenshot leak in PixelLeak research showing internal images pushed to public GitHub repos
  • Data Leak

AI Coding Agents Leak 13,000 Internal Screenshots to Public GitHub Repos

Do Son September 30, 2026 0

PixelLeak: an AI agent screenshot leak put 13,000+ internal images from 300+ firms in public GitHub repos. See how it happened and how to check.
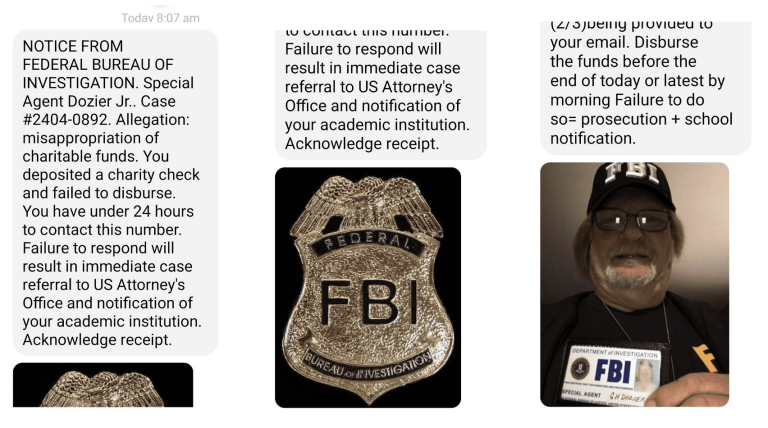
Nigeria-Based Fraudsters Hijack .edu Accounts to Run University Job Scams University job scams using edu account takeover to send fake job offers to college students
  • Cybercriminals

Nigeria-Based Fraudsters Hijack .edu Accounts to Run University Job Scams

Do Son September 30, 2026 0

University job scams are spreading through .edu account takeover. Proofpoint shows how fraudsters phish logins, then send fake jobs and bogus checks.
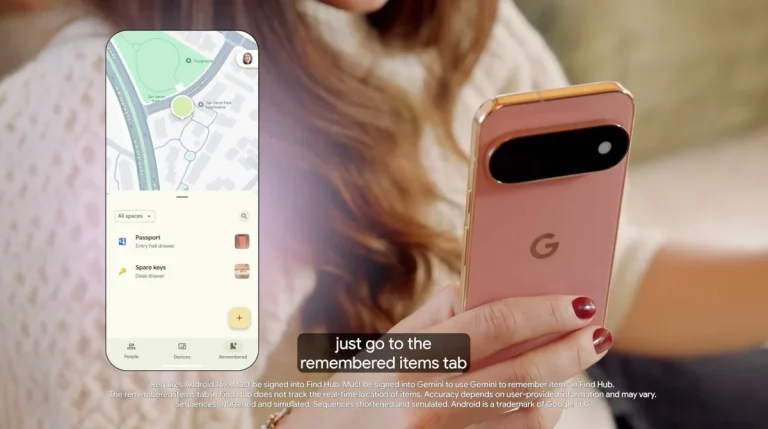
Google Gemini Find Hub: The Evolution of AI Memory Tracking Google Gemini Find Hub dashboard showing semantic memory tracking for passports
  • Technology

Google Gemini Find Hub: The Evolution of AI Memory Tracking

Do Son September 30, 2026 0

Discover how the Google Gemini Find Hub integration shifts tracking from hardware tags to AI voice memory for securing important documents like passports.
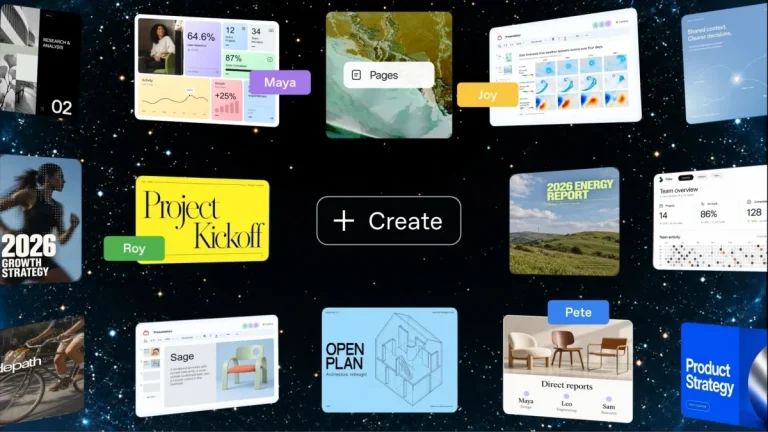
OpenAI DevDay 2026: The Shift Toward Enterprise Collaboration OpenAI enterprise collaboration workspace dashboard featuring ChatGPT Space and Dots
  • Technology

OpenAI DevDay 2026: The Shift Toward Enterprise Collaboration

Do Son September 30, 2026 0

Discover how OpenAI enterprise collaboration tools like ChatGPT Space and Dots are transforming workplace productivity and challenging Microsoft Copilot.
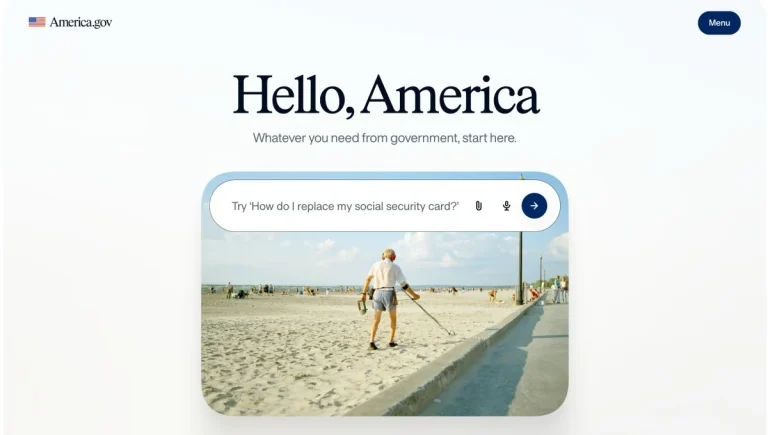
America.gov AI Chatbot Launches With Gemini and Grok America.gov AI chatbot answering citizen questions as a single digital front door to US government services, the new US government chatbot
  • Technology

America.gov AI Chatbot Launches With Gemini and Grok

Do Son September 30, 2026 0

The America.gov AI chatbot launches with Gemini and Grok, promising simple answers now and tasks like passports next year.
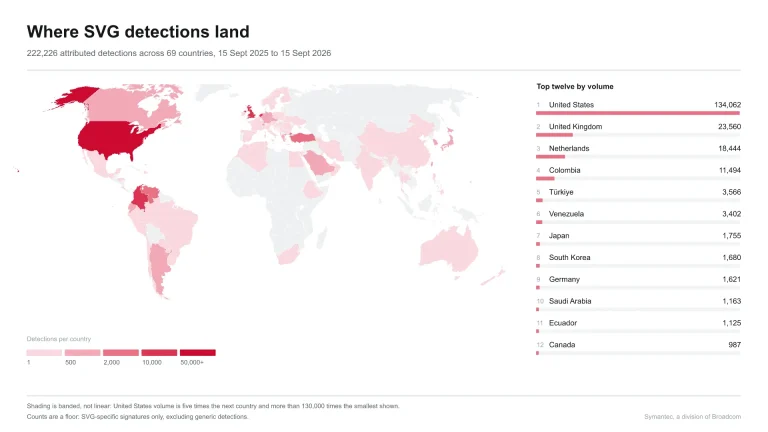
SVG Phishing Attacks Return in August as Symantec Logs 222,000 Detections SVG phishing attacks using SVG smuggling to hide fake login pages inside image attachments
  • Cybercriminals

SVG Phishing Attacks Return in August as Symantec Logs 222,000 Detections

Do Son September 30, 2026 0

SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
Microsoft Links JADEPUFFER Azure Attack to Agentic Ransomware Actor Storm-3168 JADEPUFFER Azure attack by agentic ransomware actor Storm-3168 using compromised service principals
  • Cybercriminals

Microsoft Links JADEPUFFER Azure Attack to Agentic Ransomware Actor Storm-3168

Do Son September 30, 2026 0

Microsoft ties a JADEPUFFER Azure attack to Storm-3168, the agentic ransomware actor that tried to delete 100+ storage accounts in seven minutes.
TeamViewer Fixes Five High-Severity Flaws in Full Client and Host TeamViewer vulnerabilities CVE-2026-92370, CVE-2026-19743 and CVE-2026-92368 in TeamViewer Full Client and Host
  • Vulnerability Report

TeamViewer Fixes Five High-Severity Flaws in Full Client and Host

Do Son September 30, 2026 0

Update to 15.82 now. Five high-severity TeamViewer vulnerabilities include CVE-2026-92370, CVE-2026-19743 and CVE-2026-92368 in Full Client and Host.
Electron Fixes Five High-Severity Sandbox and Isolation Vulnerabilities Electron vulnerabilities CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674 weakening sandbox and isolation in desktop apps
  • Vulnerability Report

Electron Fixes Five High-Severity Sandbox and Isolation Vulnerabilities

Do Son September 30, 2026 0

Five high-severity Electron vulnerabilities, including CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674, weaken sandbox isolation. Update Electron now.
HPE Patches 18 Instant ON Access Point Vulnerabilities, Five Rated Critical HPE Instant ON vulnerabilities in access points, including critical RCE flaws CVE-2026-76721 and CVE-2026-76722
  • Vulnerability Report

HPE Patches 18 Instant ON Access Point Vulnerabilities, Five Rated Critical

Do Son September 30, 2026 0

HPE fixed 18 HPE Instant ON vulnerabilities in its access points, including CVSS 9.8 RCE flaws CVE-2026-76721 and CVE-2026-76722. Update to 3.4.2.0.
WatchGuard Patches 14 Fireware OS Vulnerabilities, Including CVSS 9.2 RCE WatchGuard Fireware OS vulnerabilities including critical BOVPN Over TLS code injection CVE-2026-86131 and pre-auth fingerd overflow CVE-2026-81433 on Firebox appliances
  • Vulnerability Report

WatchGuard Patches 14 Fireware OS Vulnerabilities, Including CVSS 9.2 RCE

Do Son September 30, 2026 0

WatchGuard patched 14 Fireware OS vulnerabilities, including CVSS 9.2 RCE flaw CVE-2026-86131 in BOVPN Over TLS. Update Firebox appliances now.
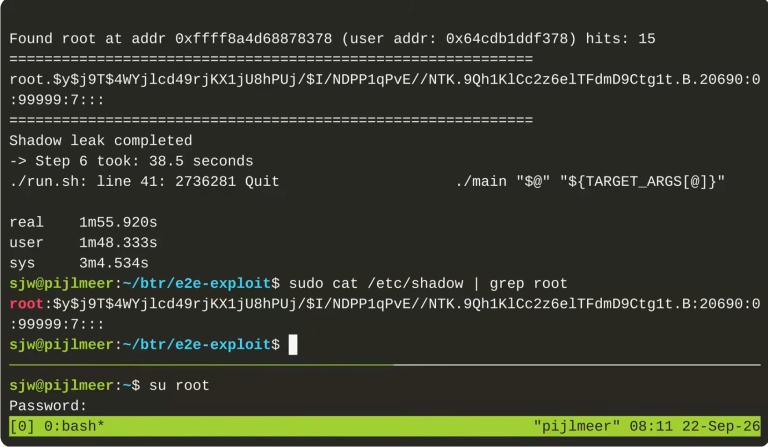
Branch Target Reuse Spectre-v2 Attack: Full Details and PoC Code Released Branch Target Reuse Spectre-v2 attack against JIT engines, with the VUSec research paper and proof-of-concept exploit code publicly released
  • Vulnerability Report

Branch Target Reuse Spectre-v2 Attack: Full Details and PoC Code Released

Do Son September 30, 2026 0

VUSec released details and PoC code for Branch Target Reuse, a Spectre-v2 attack on JIT engines that leaked Linux root password hashes. Patch now.
GeoServer Cloud Fixes CVSS 10 GitHub Actions Flaw That Exposed Repository Secrets GeoServer Cloud vulnerability in a GitHub Actions pull_request_target workflow that could allow code execution and secrets exfiltration
  • Vulnerability Report

GeoServer Cloud Fixes CVSS 10 GitHub Actions Flaw That Exposed Repository Secrets

Do Son September 30, 2026 0

A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
Podman Flaw CVE-2026-94603 Lets Container Images Disable Sandboxing Podman vulnerability CVE-2026-94603 letting a checkpoint image annotation override container sandbox settings in podman run
  • Vulnerability Report

Podman Flaw CVE-2026-94603 Lets Container Images Disable Sandboxing

Do Son September 30, 2026 0

A CVSS 10.0 Podman vulnerability, CVE-2026-94603, lets container images disable sandboxing in podman run. Upgrade to Podman 6.1.3 or 5.8.8 now.
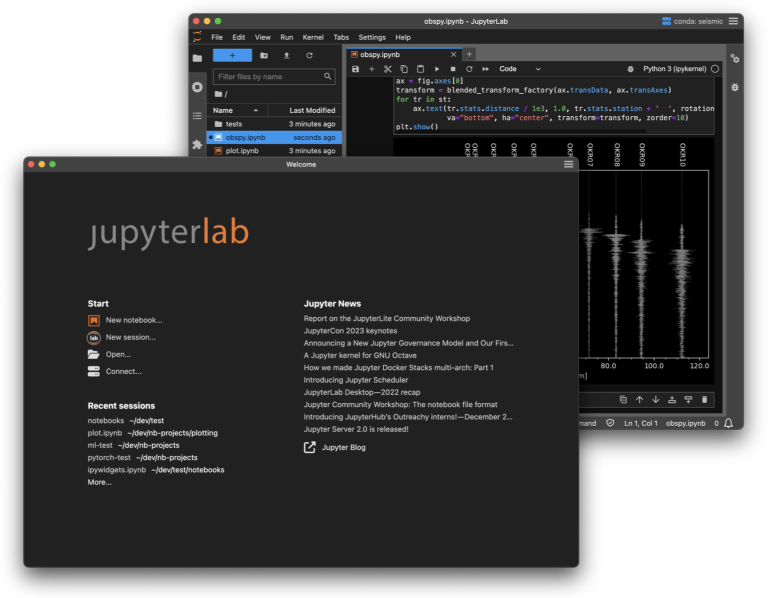
JupyterLab Desktop Flaw CVE-2026-102530 Turns a Malicious Server URL Into Code Execution JupyterLab Desktop vulnerability CVE-2026-102530, an XSS in the Connect to Remote Server dialog that leads to remote code execution
  • Vulnerability Report

JupyterLab Desktop Flaw CVE-2026-102530 Turns a Malicious Server URL Into Code Execution

Do Son September 30, 2026 0

A JupyterLab Desktop vulnerability, CVE-2026-102530 (CVSS 9.4), turns a malicious server URL into remote code execution. Update to 4.6.2-1 now.
Transparent, Perforated, or Opaque: Choosing Window Films for Security and Privacy tech-computer
  • Technique

Transparent, Perforated, or Opaque: Choosing Window Films for Security and Privacy

Do Son September 30, 2026 0
Windows can make a workplace feel brighter and more welcoming. They can even draw in visitors and...
Read More Read more about Transparent, Perforated, or Opaque: Choosing Window Films for Security and Privacy
Chrome Security Update Fixes 32 Flaws, Including Critical ANGLE Bug CVE-2026-102331 Chrome security update 154.0.8037.92 fixing 33 flaws, including critical ANGLE buffer overflow CVE-2026-102331 and V8 type confusion bugs
  • Vulnerability Report

Chrome Security Update Fixes 32 Flaws, Including Critical ANGLE Bug CVE-2026-102331

Do Son September 29, 2026 0

Google's Chrome security update 154.0.8037.92 fixes 32 flaws, including critical ANGLE bug CVE-2026-102331 and six V8 issues. Update Chrome now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-82104CVSS 9.4
    In Teltonika Networks RUTOS devices running versions from 7.22 through 7.24.2 and TSWOS devices running versions 1.9 through...
    📅 Updated: Oct 30, 2026
  • CVE-2026-103039CVSS 9.8
    The Gravity Forms plugin for WordPress is vulnerable to PHP Object Injection in all versions up to, and...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90865CVSS 9.0
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90866CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90868CVSS 9.9
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90717CVSS 9.1
    Dell PowerProtect Data Domain Management Center, Feature Release versions 7.7.1.0 through 8.8, LTS2024 release versions 7.13.1.0 through 7.13.1.80,...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90863CVSS 9.1
    Missing authorization in the administrative interface of Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.