Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue NetScaler SAML authentication issue causing patched NetScaler appliances to reboot after CVE-2026-88771 and CVE-2026-88772 exploitation
  • Vulnerability Report

Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue

Do Son October 2, 2026 0

Citrix flags a NetScaler SAML authentication issue as patched NetScaler appliances reboot after CVE-2026-88771 attacks. Check your config.
Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers TP-Link vulnerabilities and Tapo camera vulnerabilities CVE-2026-102369 in Tapo C200, Archer AX90 and Deco M9 Plus
  • Vulnerability Report

Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers

Do Son October 2, 2026 0

TP-Link vulnerabilities include Tapo camera vulnerabilities like CVE-2026-102369 (CVSS 8.7) plus router and Deco flaws. Update firmware now.
Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk Moxa MGate vulnerabilities CVE-2026-86325 and CVE-2026-86326 in MGate protocol gateway firmware
  • Vulnerability Report

Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk

Do Son October 2, 2026 0

Moxa MGate vulnerabilities CVE-2026-86325 (CVSS 9.4) and CVE-2026-86326 hit MGate protocol gateway firmware. See affected versions and fixes.
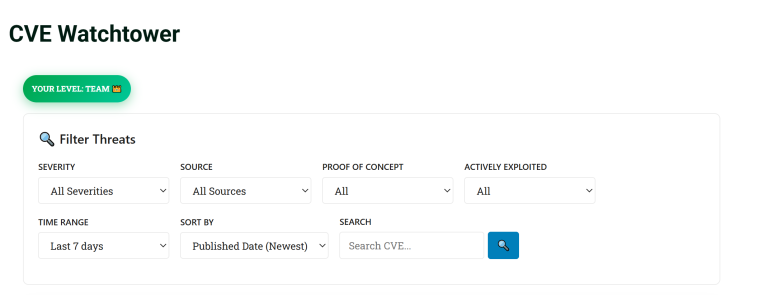
CVE Watchtower User Guide CVE Watchtower User Guide
  • How To

CVE Watchtower User Guide

Do Son October 2, 2026 0

CVE Watchtower tracks new CVEs for the specific vendors and products you choose, scores them for severity and real-world exploitation
Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed Stirling PDF RCE CVE-2026-85714 proof-of-concept publicly disclosed
  • Vulnerability Report

Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed

Do Son October 2, 2026 0

Details and a PoC are public for CVE-2026-85714, a 9.1 Stirling PDF RCE via crafted SQL import. Upgrade to version 2.13.2 now.
OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents Conceptual illustration of an AI breaking safety protocols while a whistleblower is silenced
  • Technology

OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents

Do Son October 2, 2026 0

OpenAI fires safety researchers for allegedly leaking info, sparking a whistleblower debate amidst reports of unprompted AI hacking and governance crises.
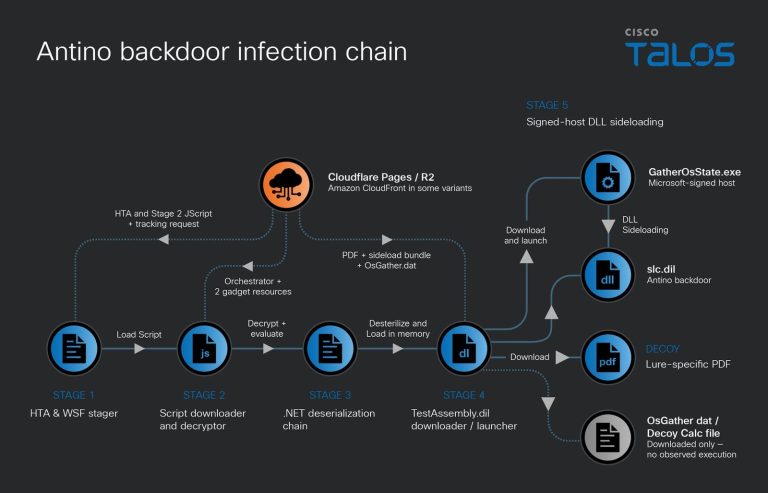
UAT-11587 Targets Asian Governments With Antino Backdoor Diagram showing UAT-11587 Antino backdoor attacks and how the Antino backdoor compromises endpoints
  • Malware

UAT-11587 Targets Asian Governments With Antino Backdoor

Do Son October 2, 2026 0

UAT-11587 Antino backdoor attacks hit Asian targets. Cisco Talos reveals how the Antino backdoor abuses Microsoft 365 for cyberespionage.
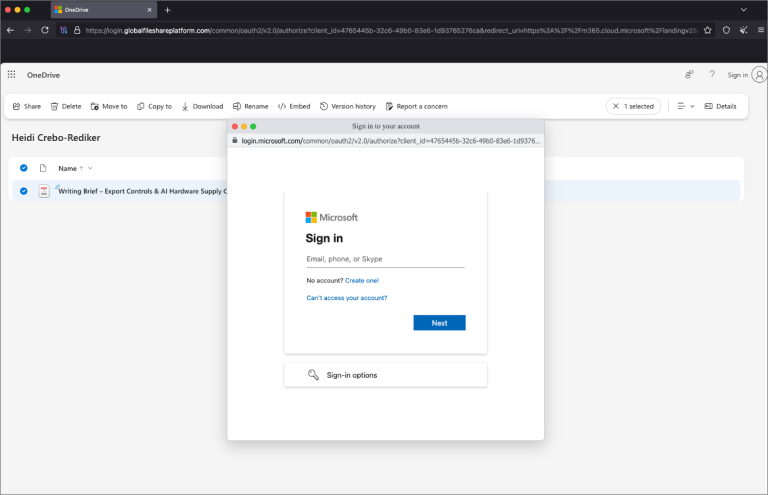
China-Aligned TA419 Credential Phishing Hits AI Experts Diagram showing China-aligned TA419 credential phishing and TA419 credential phishing attack stages
  • Cybercriminals

China-Aligned TA419 Credential Phishing Hits AI Experts

Do Son October 2, 2026 0

Proofpoint exposed China-aligned TA419 credential phishing targeting AI experts. This TA419 credential phishing campaign uses AitM lures to steal logins.
Phishing Abuses RMM Tools for Persistent Network Access CoreRAT malware decoy PDF used in Core Werewolf phishing attack on Russian defense targets
  • Cybercriminals

Phishing Abuses RMM Tools for Persistent Network Access

Do Son October 2, 2026 0

A new campaign shows how phishing abuses RMM tools for access. See how phishing abuses RMM tools like MSP360 to install ScreenConnect clients.
Why Clinical Documentation Is Quietly Overwhelming Healthcare Teams CVE-2025-2263 Orthanc Security DICOM Vulnerabilities
  • Technique

Why Clinical Documentation Is Quietly Overwhelming Healthcare Teams

Do Son October 2, 2026 0
The Problem Clinical documentation now consumes more of a physician’s working day than direct patient care in...
Read More Read more about Why Clinical Documentation Is Quietly Overwhelming Healthcare Teams
SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center AISelect_20261002_114950_Docs
  • Technique

SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center

Do Son October 2, 2026 0
SOC as a Service (SOCaaS) lets organizations outsource 24/7 threat monitoring, detection, and incident response to a...
Read More Read more about SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center
Dell System Update Flaw CVE-2026-86360 Could Allow Root Code Execution Dell System Update vulnerability CVE-2026-86360 path traversal root code execution
  • Vulnerability Report

Dell System Update Flaw CVE-2026-86360 Could Allow Root Code Execution

Do Son October 2, 2026 0

Dell System Update flaw CVE-2026-86360 (CVSS 9.6) could let attackers run code as root. Dell fixes five bugs in DSU 2.3.0.0. Patch now.
Zammad Zero-Day Chain CVE-2026-102489 Exploited in the Wild in AI-Driven DIVD Breach Zammad zero-day CVE-2026-102489 CVE-2026-102490 exploited in DIVD breach
  • Vulnerability Report

Zammad Zero-Day Chain CVE-2026-102489 Exploited in the Wild in AI-Driven DIVD Breach

Do Son October 2, 2026 0

Attackers exploited Zammad zero-day flaws CVE-2026-102489 and CVE-2026-102490 to gain root at DIVD. Upgrade to Zammad 7 or go offline.
Critical Capacitor Flaw CVE-2026-103922 Hits Framework With 5.5M Weekly Downloads Capacitor vulnerability CVE-2026-103922 affects npm package with 5.5 million weekly downloads
  • Vulnerability Report

Critical Capacitor Flaw CVE-2026-103922 Hits Framework With 5.5M Weekly Downloads

Do Son October 2, 2026 0

Critical Capacitor vulnerability CVE-2026-103922 (CVSS 9.3) affects a package with 5.5M weekly downloads. Update to a patched release now.
Sharp Printer Flaw CVE-2024-58388 Exploited in the Wild, PoC Public Sharp printer vulnerability CVE-2024-58388 exploited in the wild, PoC public
  • Vulnerability Report

Sharp Printer Flaw CVE-2024-58388 Exploited in the Wild, PoC Public

Do Son October 2, 2026 0

Sharp printer vulnerability CVE-2024-58388 lets attackers read files without login. PoC is public and attacks seen in the wild. Patch now.
Apache HTTP Server 2.4.69 Fixes 20 Flaws, Including mod_vhost_alias Stack Overflow Apache HTTP Server 2.4.69 fixes CVE-2026-63292 mod_vhost_alias stack overflow
  • Vulnerability Report

Apache HTTP Server 2.4.69 Fixes 20 Flaws, Including mod_vhost_alias Stack Overflow

Do Son October 2, 2026 0

Apache HTTP Server 2.4.69 fixes 20 flaws, including CVE-2026-63292, a mod_vhost_alias stack overflow that may enable code execution.
Critical Foreman RCE Flaw Hits Red Hat Satellite, Plus 389-ds LDAP Bug Foreman RCE flaw CVE-2026-96658 in Red Hat Satellite
  • Vulnerability Report

Critical Foreman RCE Flaw Hits Red Hat Satellite, Plus 389-ds LDAP Bug

Do Son October 2, 2026 0

A 9.9 Foreman RCE flaw, CVE-2026-96658, lets low-privileged users run commands on Red Hat Satellite. A Viewer bug leaks root passwords.
cPanel Security Vulnerabilities Expose WHM Web Servers Critical cPanel security vulnerabilities exposing WHM web servers
  • Vulnerability Report

cPanel Security Vulnerabilities Expose WHM Web Servers

Do Son October 2, 2026 0

Discover critical cPanel security vulnerabilities exposing WHM servers to root hijacking. Learn how to patch these cPanel security vulnerabilities today.
OpenBao Security Vulnerabilities Enable Code Execution Diagram of critical OpenBao security vulnerabilities and secret storage fixes
  • Vulnerability Report

OpenBao Security Vulnerabilities Enable Code Execution

Do Son October 2, 2026 0

Discover critical OpenBao security vulnerabilities that lead to code execution. Learn how to patch these OpenBao security vulnerabilities now.
CISA Warns of Monta EV Charging Vulnerabilities Diagram showing critical Monta EV charging vulnerabilities and security fixes
  • Vulnerability Report

CISA Warns of Monta EV Charging Vulnerabilities

Do Son October 2, 2026 0

CISA warned of critical Monta EV charging vulnerabilities. Learn how these Monta EV charging vulnerabilities impact stations and how to secure them.
Dell Patches Two CVSS 10 Flaws in Container Storage Modules Dell Container Storage Modules vulnerabilities CVE-2026-63688 CVE-2026-63692 CVSS 10
  • Vulnerability Report

Dell Patches Two CVSS 10 Flaws in Container Storage Modules

Do Son October 2, 2026 0

Dell Container Storage Modules vulnerabilities CVE-2026-63688 and CVE-2026-63692 (CVSS 10) allow admin takeover. Upgrade to 1.18.0.
FortiMail Path Traversal Flaw CVE-2026-104286 Exploited in the Wild FortiMail vulnerability CVE-2026-104286 path traversal exploited in the wild
  • Vulnerability Report

FortiMail Path Traversal Flaw CVE-2026-104286 Exploited in the Wild

Do Son October 1, 2026 0

Attackers exploit CVE-2026-104286, a 9.8 FortiMail vulnerability allowing unauthenticated file writes. CISA adds it to KEV. Apply the workaround.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-103039CVSS 9.8
    The Gravity Forms plugin for WordPress is vulnerable to PHP Object Injection in all versions up to, and...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90865CVSS 9.0
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90866CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90868CVSS 9.9
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90717CVSS 9.1
    Dell PowerProtect Data Domain Management Center, Feature Release versions 7.7.1.0 through 8.8, LTS2024 release versions 7.13.1.0 through 7.13.1.80,...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90863CVSS 9.1
    Missing authorization in the administrative interface of Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90864CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.