Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
JetBrains Software Vulnerabilities Impact TeamCity JetBrains software vulnerabilities TeamCity RCE bugs
  • Vulnerability Report

JetBrains Software Vulnerabilities Impact TeamCity

Do Son October 10, 2026 0

Discover the latest JetBrains software vulnerabilities, including TeamCity RCE bugs and Exposed SQLi flaws. Apply security patches immediately.
Ricardo Data Leak Exposes User Contact Details Ricardo data leak illustration highlighting the SMG security vulnerability.
  • Data Leak

Ricardo Data Leak Exposes User Contact Details

Do Son October 9, 2026 0

A recent Ricardo data leak exposed 890,000 users. SMG fixed the security vulnerability, confirming passwords remain safe.
Nginx UI RCE Vulnerability Disclosed With PoC Exploit Code Nginx UI RCE vulnerability CVE-2026-107806
  • Vulnerability Report

Nginx UI RCE Vulnerability Disclosed With PoC Exploit Code

Do Son October 9, 2026 0

A critical Nginx UI RCE vulnerability (CVE-2026-107806) is publicly disclosed with PoC exploit code. Admins must patch now to prevent system takeover.
Critical Apache Camel Karavan Vulnerabilities Threaten Servers Apache Camel Karavan vulnerabilities CVE-2026-103413 CVE-2026-103412
  • Vulnerability Report

Critical Apache Camel Karavan Vulnerabilities Threaten Servers

Do Son October 9, 2026 0

Discover how critical Apache Camel Karavan vulnerabilities (CVE-2026-103413 and CVE-2026-103412) allow code execution. Update to version 4.22.1 now.
Grid Protection Alliance openPDC and openHistorian Flaws openPDC openHistorian vulnerabilities CVE-2026-100730 CVE-2026-105281
  • Vulnerability Report

Grid Protection Alliance openPDC and openHistorian Flaws

Do Son October 9, 2026 0

Fix critical openPDC openHistorian vulnerabilities like CVE-2026-100730 and CVE-2026-105281. CISA urges patching these severe RCE flaws immediately.
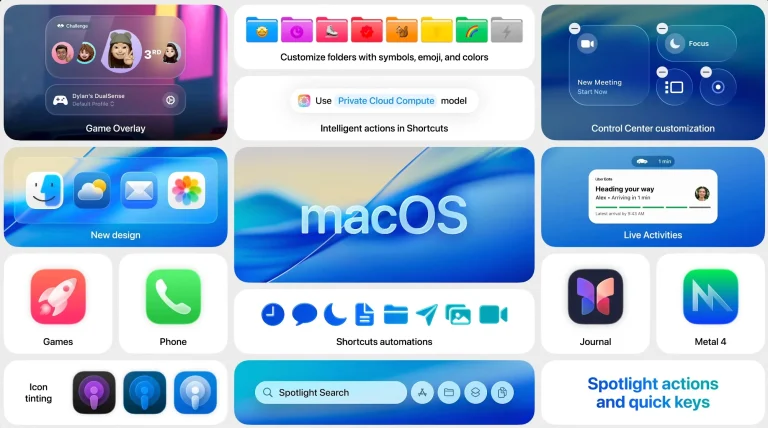
The Growing Backlash Against Apple Intelligence Integration Apple Intelligence storage macOS 27 Golden Gate enterprise security
  • Data Leak

The Growing Backlash Against Apple Intelligence Integration

Do Son October 9, 2026 0

Explore how massive Apple Intelligence storage demands in macOS 27 Golden Gate face fierce backlash regarding enterprise security and user limitations.
Controversy Surrounding the .lan Domain Application ICANN gTLD applications .lan domain OpenWrt local network configuration
  • Technology

Controversy Surrounding the .lan Domain Application

Do Son October 9, 2026 0

Discover the controversy surrounding ICANN gTLD applications for the .lan domain. Learn how this impacts OpenWrt and local network configurations worldwide.
How residential proxy networks get abused and what defenders can detect image
  • Technique

How residential proxy networks get abused and what defenders can detect

Do Son October 9, 2026 0
The alert fires on the login endpoint, but the traffic behind it looks clean. Each attempt comes...
Read More Read more about How residential proxy networks get abused and what defenders can detect
The Reality of Ransomware Recovery Services MonsterCloud ransomware decryption fraud Zohar Pinhasi data recovery
  • Cybercriminals

The Reality of Ransomware Recovery Services

Do Son October 9, 2026 0

Discover the MonsterCloud ransomware decryption fraud. Learn how Zohar Pinhasi allegedly deceived clients by secretly paying hackers for data recovery keys.
SonicWall SMA1000 Vulnerability Exploited in the Wild A security warning highlighting a critical SonicWall SMA1000 vulnerability under active exploitation
  • Vulnerability Report

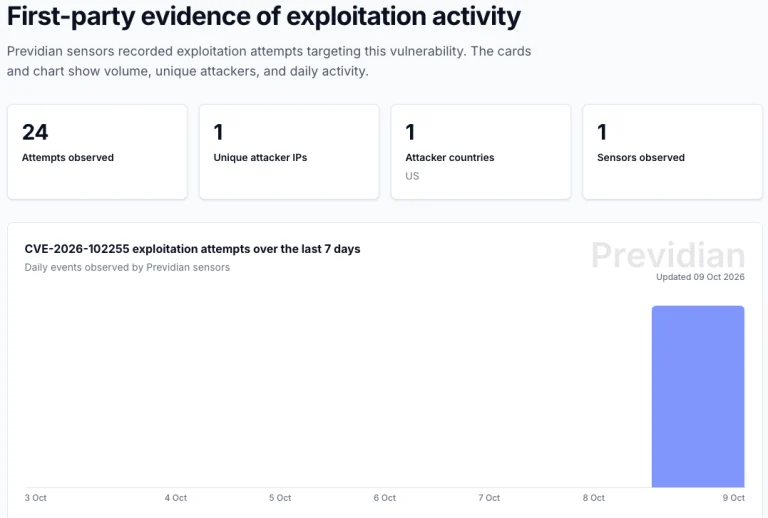
SonicWall SMA1000 Vulnerability Exploited in the Wild

Do Son October 9, 2026 0

Attackers target a critical SonicWall SMA1000 vulnerability in the wild. Apply vendor hotfixes to secure remote access gateways against CVE-2026-102255.
OpenAI GPT-6 Introduces Revolutionary Intelligent UI OpenAI GPT-6 Intelligent UI interactive interface ChatGPT upgrade
  • Technology

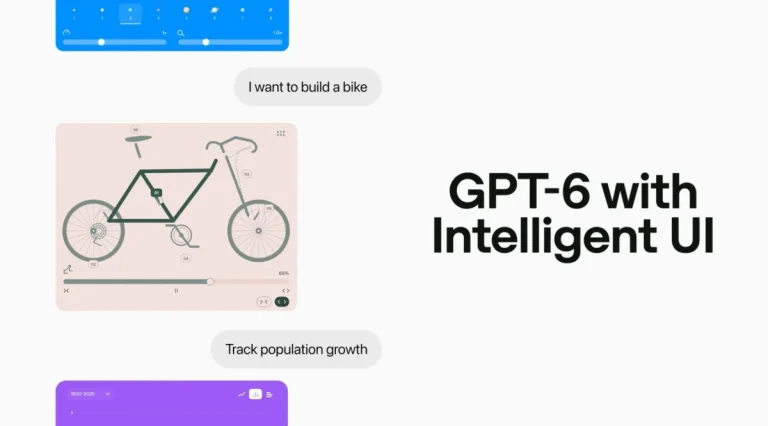
OpenAI GPT-6 Introduces Revolutionary Intelligent UI

Do Son October 9, 2026 0

Discover how the new OpenAI GPT-6 Intelligent UI transforms ChatGPT into an on-demand software factory with interactive interfaces and streaming reasoning.
SoftBank IDCF Cloud Ransomware Attack Exposed by Hackers SoftBank IDCF Cloud ransomware attack East Japan Region 1 outage
  • Cybercriminals

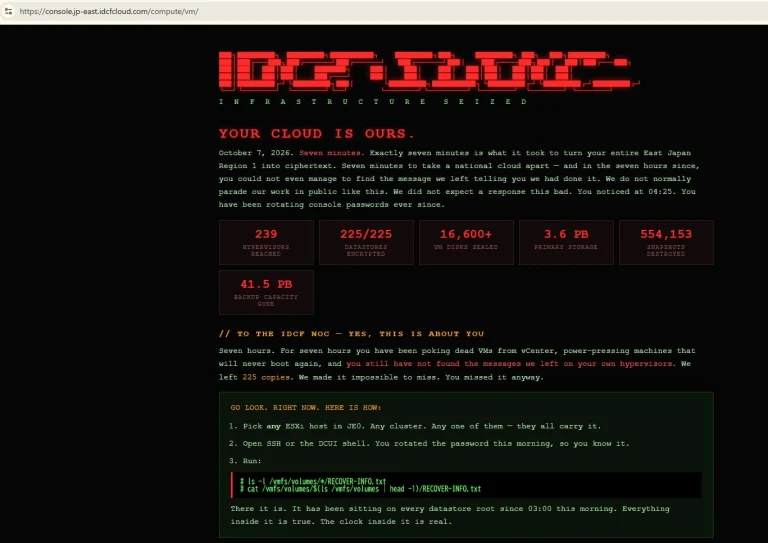
SoftBank IDCF Cloud Ransomware Attack Exposed by Hackers

Do Son October 9, 2026 0

Explore the devastating SoftBank IDCF Cloud ransomware attack. Read the hackers' humiliating note revealing the massive East Japan Region 1 outage.
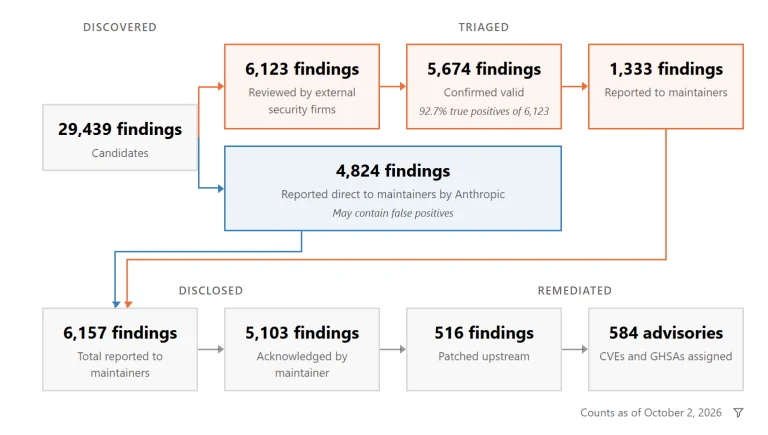
Anthropic Introduces OSS Scanner for Open Source Projects Anthropic OSS Scanner open source vulnerability scanning
  • Technology

Anthropic Introduces OSS Scanner for Open Source Projects

Do Son October 9, 2026 0

Discover the Anthropic OSS Scanner. Learn how AI models provide automated vulnerability scanning and remediation for open source projects.
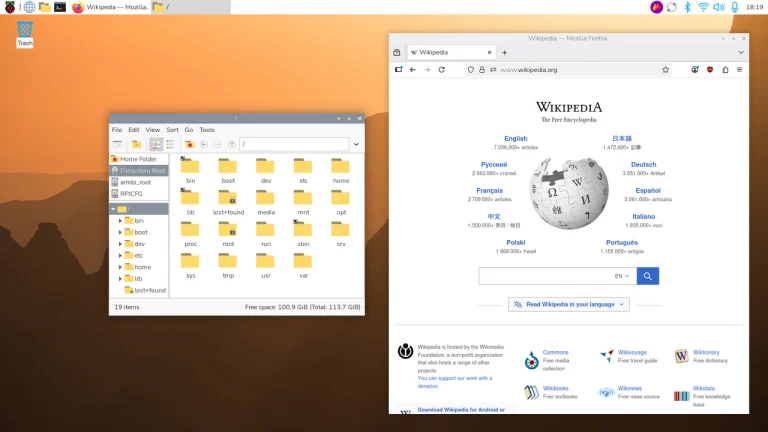
Raspberry Pi OS Update: Squashing Desktop Bugs Raspberry Pi OS update Linux desktop environments bug fixes
  • Linux

Raspberry Pi OS Update: Squashing Desktop Bugs

Do Son October 9, 2026 0

Discover the latest Raspberry Pi OS update. Learn how this release squashes critical bugs, optimizes Linux desktop environments, and refines the Dock interface.
Microsoft 365 Squeezes Family Plan Storage Microsoft 365 storage adjustments family plan OneDrive changes
  • Technology

Microsoft 365 Squeezes Family Plan Storage

Do Son October 9, 2026 0

Discover the impact of the Microsoft 365 storage changes. Learn how the new 2TB shared OneDrive limit severely squeezes Family Plan users and their files.
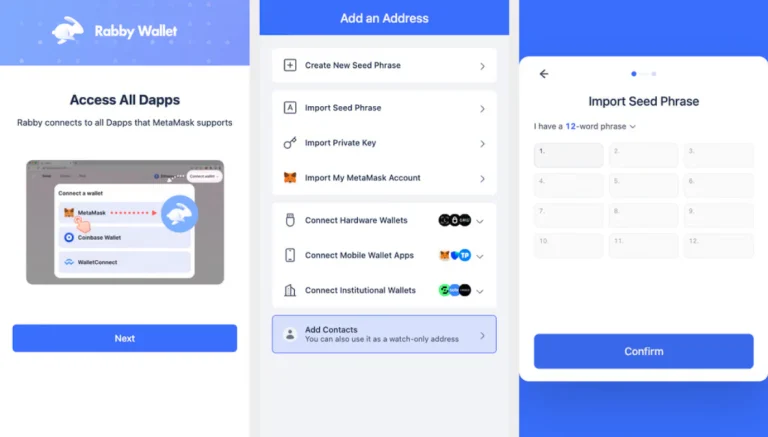
16 Fake Rabby and OKX Firefox Extensions Stole Crypto Wallet Recovery Phrases Malicious Firefox extensions posing as Rabby and OKX wallets acting as crypto wallet stealers
  • Malware

16 Fake Rabby and OKX Firefox Extensions Stole Crypto Wallet Recovery Phrases

Do Son October 9, 2026 0

Socket found 16 malicious Firefox extensions posing as Rabby and OKX. These crypto wallet stealers grabbed seed phrases. Here is what to do.
Let’s Encrypt Accelerates the Push for Automation Let's Encrypt certificate lifespan reduction automation TLS certificates
  • Technology

Let’s Encrypt Accelerates the Push for Automation

Do Son October 9, 2026 0

Discover the impact of the Let's Encrypt certificate lifespan reduction. Learn how the shift to 45-day TLS certificates demands robust ACME automated renewal.
The Silent Threat of Midnight Mimosa Malware Midnight Mimosa malware cheap Android devices Bitdefender report cybersecurity
  • Malware

The Silent Threat of Midnight Mimosa Malware

Do Son October 9, 2026 0

Discover the Midnight Mimosa malware threatening cheap Android devices. Read the Bitdefender report on how OEMs pre-install this dangerous cybersecurity threat.
CrowdStrike Links South Korean Bank Breaches to Chinese AI Pentesting Tool ARTEX ARTEX AI tool used by a suspected Chinese-speaking attacker against South Korean banks
  • Cybercriminals

CrowdStrike Links South Korean Bank Breaches to Chinese AI Pentesting Tool ARTEX

Do Son October 9, 2026 0

CrowdStrike links the ARTEX AI tool to breaches at South Korean banks, run by a suspected Chinese-speaking, profit-driven attacker.
Actively Exploited Software Vulnerabilities Demand Patching, CISA Warns Actively exploited software vulnerabilities enabling critical remote code execution.
  • Vulnerability Report

Actively Exploited Software Vulnerabilities Demand Patching, CISA Warns

Do Son October 9, 2026 0

Five actively exploited software vulnerabilities threaten critical systems. Update your servers now to prevent critical remote code execution attacks.
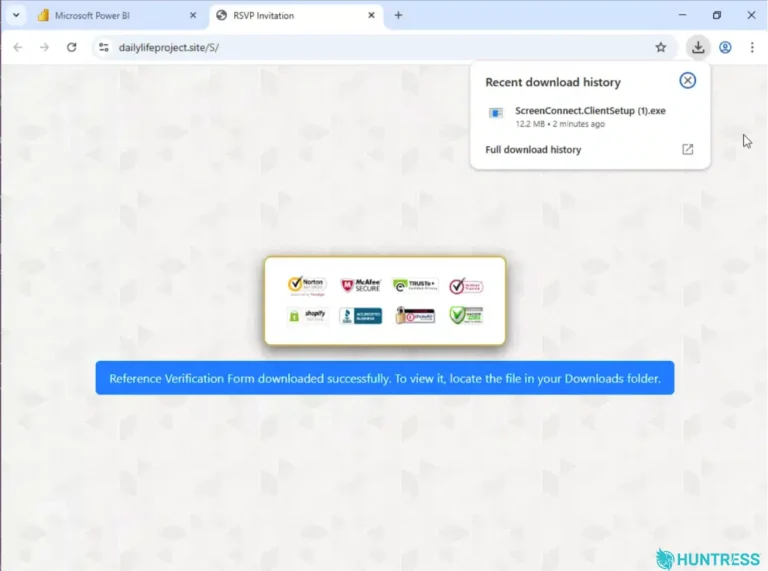
Phishing Campaign Abuses Microsoft Power BI to Install Rogue ScreenConnect Clients Power BI phishing campaign delivering rogue ScreenConnect remote access clients
  • Malware

Phishing Campaign Abuses Microsoft Power BI to Install Rogue ScreenConnect Clients

Do Son October 9, 2026 0

A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
Urgent Security Patches Fix IBM Verify Access Vulnerabilities Urgent Security Patches Fix IBM Verify Access Vulnerabilities
  • Vulnerability Report

Urgent Security Patches Fix IBM Verify Access Vulnerabilities

Do Son October 9, 2026 0

Multiple IBM Verify Access vulnerabilities expose systems to remote attacks. Update your software now to block these critical security flaws.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.