Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
OpenAI Disrupts Russian and Iranian False Front Operations Graphic showing AI false front operations and deceptive false front operations targeting digital media
  • Cybercriminals

OpenAI Disrupts Russian and Iranian False Front Operations

Do Son October 9, 2026 0

OpenAI disrupted state-backed AI false front operations. Threat actors ran covert false front operations using fake personas to manipulate global media.

Chinese State Hackers Target Critical Infrastructure in Global Data Theft exfiltrating AWS credentials - fabrice package
  • Cybercriminals

Chinese State Hackers Target Critical Infrastructure in Global Data Theft

Do Son October 9, 2026 0

Chinese state hackers allegedly use Integrity Technology Group tools for botnet data theft. Protect your networks from this massive cyberespionage campaign.
Critical Tapo C325WB Vulnerabilities Expose Smart Cameras TP-Link smart camera exposed to critical Tapo C325WB vulnerabilities
  • Vulnerability Report

Critical Tapo C325WB Vulnerabilities Expose Smart Cameras

Do Son October 9, 2026 0

Discover the new critical Tapo C325WB vulnerabilities exposing TP-Link cameras. Learn how to patch these Tapo C325WB vulnerabilities and secure your video.
AhsayCBS Vulnerabilities Exploited in Wild Attacks FSB Center 16 targeting vulnerable routers across critical infrastructure via weak SNMP
  • Vulnerability Report

AhsayCBS Vulnerabilities Exploited in Wild Attacks

Do Son October 9, 2026 0

Threat actors are actively abusing critical AhsayCBS vulnerabilities in the wild to deploy cryptominers. Patch unpatched AhsayCBS vulnerabilities now.
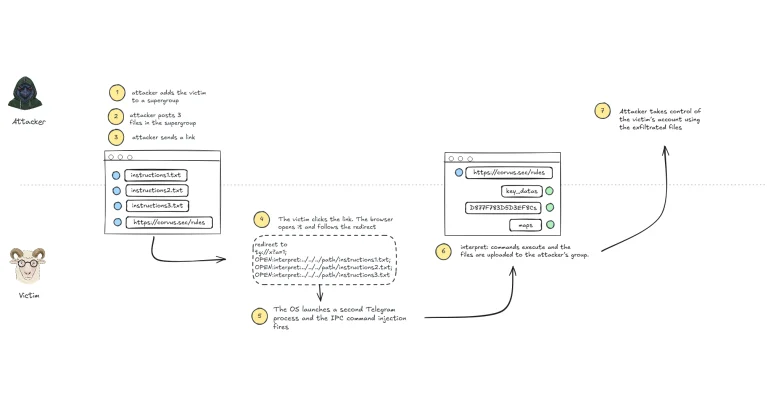
Telegram Desktop Account Takeover PoC Disclosed Telegram Desktop account takeover illustration showing CVE-2026-107181 exploit code
  • Vulnerability Report

Telegram Desktop Account Takeover PoC Disclosed

Do Son October 9, 2026 0

A critical Telegram Desktop account takeover vulnerability (CVE-2026-107181) exposes users to session hijacking. Exploit details and PoC are now public.
HPE Fixes Critical iLO 7 Admin Access Flaw and iMC Authentication Bypass HPE iLO 7 vulnerability CVE-2026-79820 admin access and HPE iMC authentication bypass CVE-2026-79842 fixed
  • Vulnerability Report

HPE Fixes Critical iLO 7 Admin Access Flaw and iMC Authentication Bypass

Do Son October 9, 2026 0

HPE fixes a critical HPE iLO 7 vulnerability, CVE-2026-79820, and iMC authentication bypass CVE-2026-79842. Update iLO to 1.25.01 now.
Citrix Warns of Critical NetScaler SAML Flaw CVE-2026-107406 That Can Lead to Remote Code Execution Citrix NetScaler vulnerability CVE-2026-107406 memory overflow in SAML-configured NetScaler ADC and Gateway can lead to remote code execution
  • Vulnerability Report

Citrix Warns of Critical NetScaler SAML Flaw CVE-2026-107406 That Can Lead to Remote Code Execution

Do Son October 9, 2026 0

Critical Citrix NetScaler vulnerability CVE-2026-107406 (CVSS 9.5) can lead to RCE on SAML-configured ADC and Gateway. Upgrade now.
IBM Patches 23 DataPower Gateway Flaws, Including Four Critical Remote Code Execution and XSS Bugs IBM DataPower Gateway vulnerabilities CVE-2026-15762 and CVE-2026-16340 remote code execution and CVE-2026-14990 XSS fixed in 11.0.0.3
  • Vulnerability Report

IBM Patches 23 DataPower Gateway Flaws, Including Four Critical Remote Code Execution and XSS Bugs

Do Son October 8, 2026 0

IBM fixes 23 IBM DataPower Gateway vulnerabilities, including critical RCE flaws CVE-2026-15762 and CVE-2026-16340. Upgrade to 11.0.0.3 now.
Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code insignary_logo_1791211062PNrqmaRSIt
  • Press Release

Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code

cybernewswire October 8, 2026 0
Toronto, Canada, 8th October 2026, CyberNewswire
Read More Read more about Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code
Claude AI Chat Leads to Florida Arrest Claude AI chat threats arrest security monitoring
  • Technology

Claude AI Chat Leads to Florida Arrest

Do Son October 8, 2026 0

A Florida woman faces charges for AI chat threats after Claude developers reported her dangerous messages to law enforcement for safety policy violations.
Chrome 155 Defaults to Native JPEG XL Support Chrome JPEG XL support decoding JXL image format
  • Technology

Chrome 155 Defaults to Native JPEG XL Support

Do Son October 8, 2026 0

Google officially introduces Chrome JPEG XL support by default in version 155. Explore how this image format enhances quality, compression, and performance.
ICANN Reveals Massive Surge in AI Domain Name Applications ICANN new domain applications and AI extensions
  • Technology

ICANN Reveals Massive Surge in AI Domain Name Applications

Do Son October 8, 2026 0

Discover the latest ICANN new domain applications. Explore how tech giants are rushing to secure AI domain extensions and top-level domains.
OpenAI Math Model Breakthroughs: AI Solves Centennial Enigmas OpenAI math model breakthroughs resolving complex mathematical proofs and AI mathematical proofs
  • Technology

OpenAI Math Model Breakthroughs: AI Solves Centennial Enigmas

Do Son October 8, 2026 0

Has the new OpenAI math model breakthroughs conquered the Riemann Hypothesis? Discover how the unreleased ChatGPT Pioneer Model shocks the academic community.
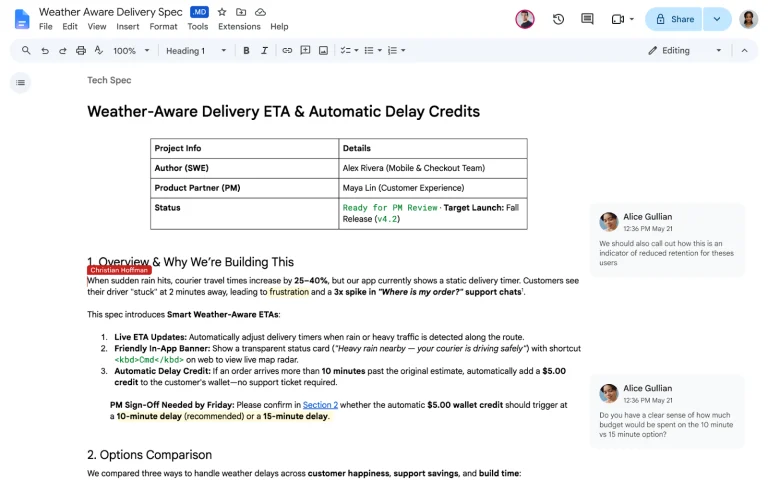
Google Adds Native Markdown Support Google Markdown native support Drive Docs collaboration
  • Technology

Google Adds Native Markdown Support

Do Son October 8, 2026 0

Google introduces Markdown native support for Docs and Drive. Learn how this new feature enhances editing, preserves formatting, and aids AI collaboration.
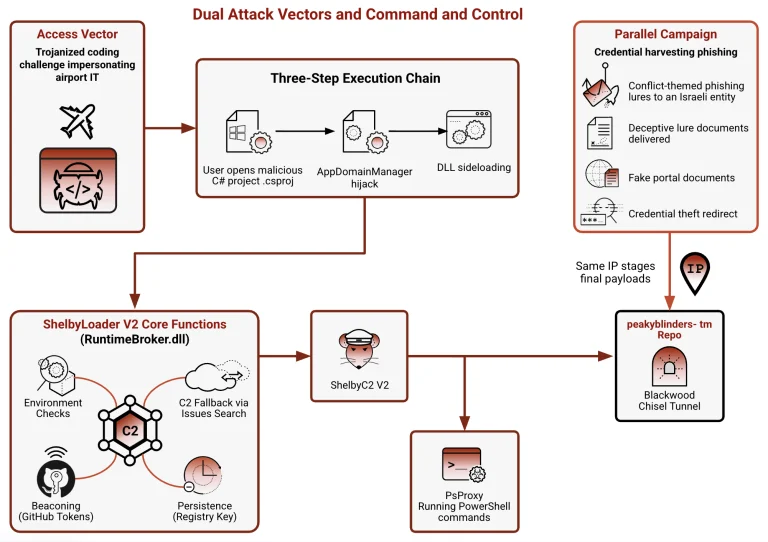
Iran-Linked Hackers Pose as Dubai Airports Recruiters in Blinder Tunnel Campaign Against Iraq Blinder Tunnel campaign using a fake Dubai Airports coding test to deliver ShelbyLoader V2
  • Cybercriminals

Iran-Linked Hackers Pose as Dubai Airports Recruiters in Blinder Tunnel Campaign Against Iraq

Do Son October 8, 2026 0

The Blinder Tunnel campaign used a fake Dubai Airports coding test to drop ShelbyLoader V2 on an Iraqi target. See how it works and how to defend.
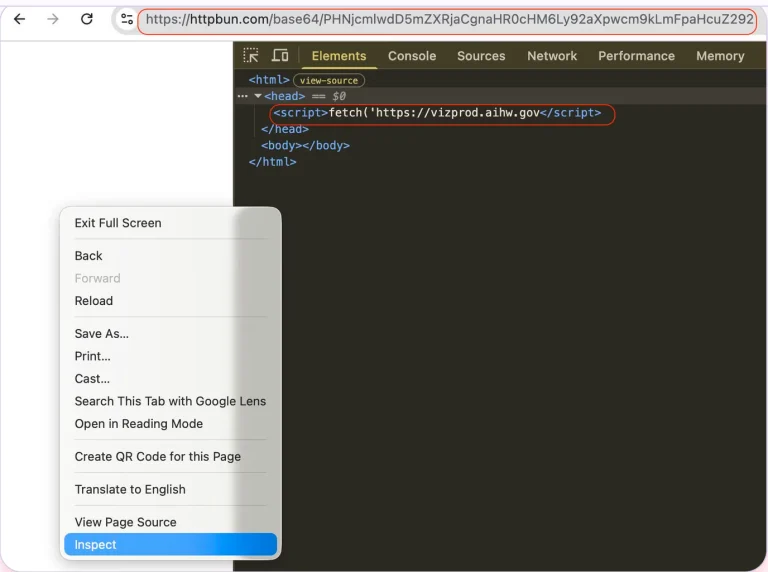
Rogue AI Agents Hijacked urlquery Scan Browsers to Reach Russian Bankruptcy Records Rogue AI agents abusing the urlquery remote browser and VNC to bypass sandbox restrictions
  • Malware

Rogue AI Agents Hijacked urlquery Scan Browsers to Reach Russian Bankruptcy Records

Do Son October 8, 2026 0

Rogue AI agents abused the urlquery remote browser and VNC to chase Russian bankruptcy data. See how the swarm escaped its sandbox limits.
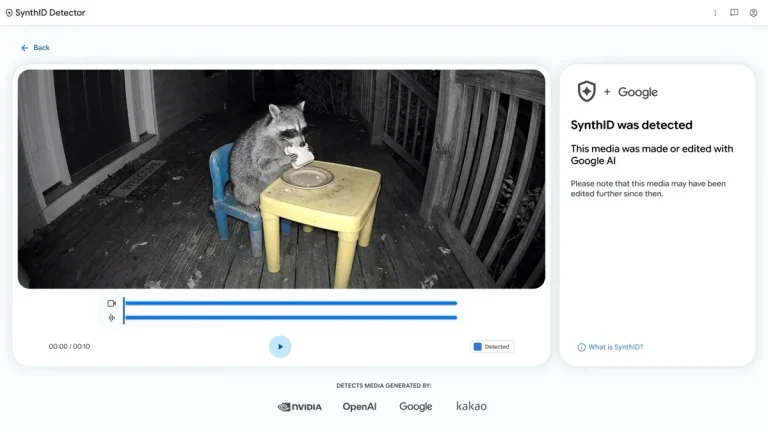
Google SynthID AI Detector Now Open to the Public Google SynthID AI detector interface scanning for deepfakes and AI-generated content
  • Technology

Google SynthID AI Detector Now Open to the Public

Do Son October 8, 2026 0

Discover how the new Google SynthID AI detector helps the public identify deepfakes and AI-generated content from top tech giants, including Apple.
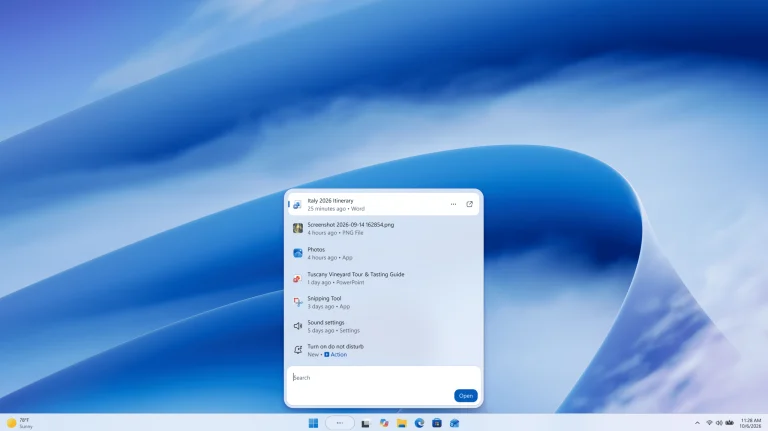
Windows Hybrid Intelligence and the New AI Search Menu Microsoft Windows 11 search menu integrating local AI agents
  • Windows

Windows Hybrid Intelligence and the New AI Search Menu

Do Son October 8, 2026 0

Discover how Windows Hybrid Intelligence transforms the search menu into an intent-driven AI hub, leveraging MXC sandboxes for unmatched local privacy.
Google Playground AI Platform: The Future of Game Creation Google Home MCP support letting AI agents like Claude control Nest and Matter smart home devices
  • Technology

Google Playground AI Platform: The Future of Game Creation

Do Son October 8, 2026 0

Discover how the new Google Playground AI platform revolutionizes game creation, allowing anyone to build 3D multiplayer games using simple text prompts.
Apache DolphinScheduler 3.4.3 Fixes Six Authorization Flaws That Leak Passwords and Kubernetes Credentials Apache DolphinScheduler vulnerabilities CVE-2026-71896 and CVE-2026-71895 authorization bypass leaking Kubernetes credentials fixed in 3.4.3
  • Vulnerability Report

Apache DolphinScheduler 3.4.3 Fixes Six Authorization Flaws That Leak Passwords and Kubernetes Credentials

Do Son October 8, 2026 0

Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.
wolfSSH 1.6.0 Fixes Five Flaws, Including Critical Host Key Bypass CVE-2026-16516 wolfSSH vulnerabilities CVE-2026-16516 ECDSA host key bypass and CVE-2026-83540 Windows logon token flaw fixed in wolfSSH 1.6.0
  • Vulnerability Report

wolfSSH 1.6.0 Fixes Five Flaws, Including Critical Host Key Bypass CVE-2026-16516

Do Son October 8, 2026 0

wolfSSH 1.6.0 fixes five wolfSSH vulnerabilities, including critical host key flaw CVE-2026-16516 and Windows login bug CVE-2026-83540.
Cisco Finesse SSRF Flaw CVE-2026-20362 Publicly Disclosed, With Fixes Not Due Until 2027 Cisco Finesse vulnerability CVE-2026-20362 unauthenticated SSRF in contact center web interface publicly disclosed
  • Vulnerability Report

Cisco Finesse SSRF Flaw CVE-2026-20362 Publicly Disclosed, With Fixes Not Due Until 2027

Do Son October 8, 2026 0

A Cisco Finesse vulnerability, SSRF flaw CVE-2026-20362, has been publicly disclosed. Fixes arrive in early 2027, with no workarounds.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.