Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
MariaDB Patches Nine Vulnerabilities Enabling Privilege Escalation and Code Execution MariaDB vulnerabilities CVE-2026-107815 privilege escalation and code execution in database server
  • Vulnerability Report

MariaDB Patches Nine Vulnerabilities Enabling Privilege Escalation and Code Execution

Do Son October 12, 2026 0

Nine MariaDB vulnerabilities enable privilege escalation and code execution, rated up to CVSS 8.5. Upgrade to the fixed Server and Connector/C releases.
RD Web Access Breaks as Chrome Drops XSLT Support RD Web Access portal on Windows Server failing to load after Chrome XSLT deprecation removes client-side XSLT
  • Technology

RD Web Access Breaks as Chrome Drops XSLT Support

Do Son October 12, 2026 0

Chrome 158 drops XSLT on November 17, which can break RD Web Access on Windows Server. See the timeline and Microsoft's interim fixes.
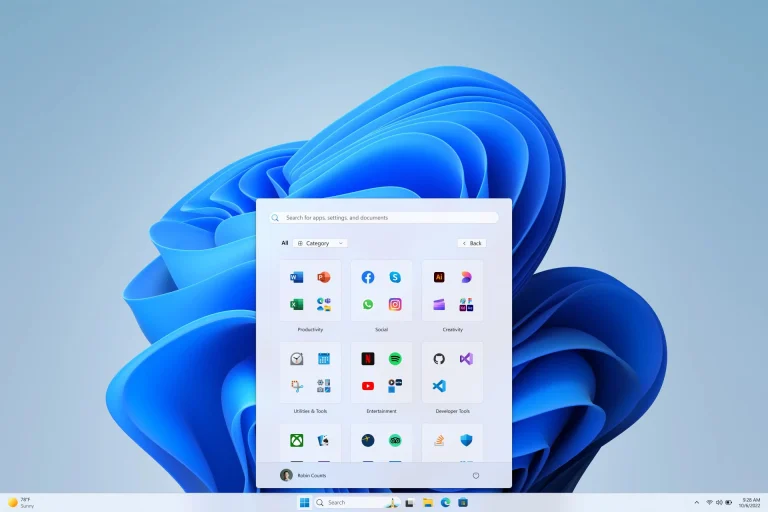
Windows 11 Quick Settings Can Now Ring Your Android Phone Windows 11 Quick Settings panel showing a paired phone with Do Not Disturb, volume, and a find my phone Windows 11 ring option
  • Windows

Windows 11 Quick Settings Can Now Ring Your Android Phone

Do Son October 12, 2026 0

Microsoft is testing Windows 11 Quick Settings controls for Android: toggle Do Not Disturb, set volume, and ring a lost phone without Phone Link.
LineageOS 24.0 Released: Android 17 & Web Flashing Tool LineageOS 24.0 Android 17 custom ROM and WebUSB Lineage Flash Tools interface
  • Android

LineageOS 24.0 Released: Android 17 & Web Flashing Tool

Do Son October 12, 2026 0

Discover the official release of LineageOS 24.0 based on Android 17. Explore new system updates, synchronized security patches, and the WebUSB flashing tool.
Run Googlebook OS on MacBook via QEMU Virtualization Googlebook OS running on Apple Silicon MacBook via QEMU virtualization
  • Technology

Run Googlebook OS on MacBook via QEMU Virtualization

Do Son October 12, 2026 0

Discover how to run Googlebook OS on an Apple Silicon MacBook using QEMU virtualization, MoltenVK, and the open-source GBOS-VM project.
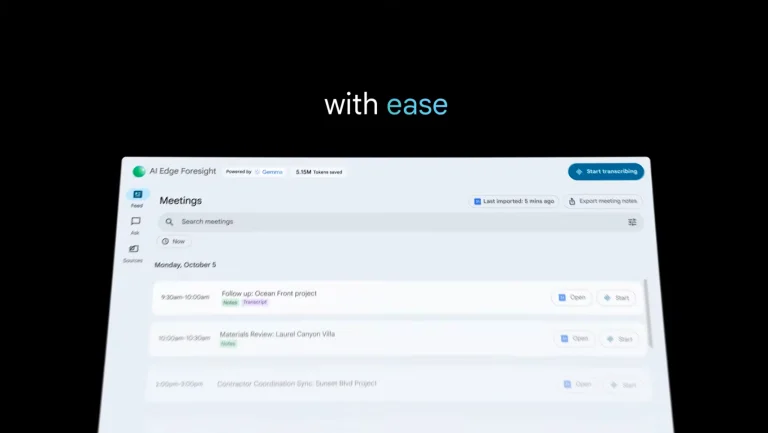
Google AI Edge Foresight: A Free Offline Mac Tool Google AI Edge Foresight offline meeting tool for Mac
  • Technology

Google AI Edge Foresight: A Free Offline Mac Tool

Do Son October 12, 2026 0

Discover Google AI Edge Foresight, a free offline meeting tool for Mac. It uses Gemma 4 and RAG technology to create secure, local knowledge bases easily.
GitLab Patches CVE-2026-97229 (CVSS 10.0) Flaw That Lets Unauthenticated Attackers Execute Arbitrary Code GitLab critical vulnerability CVE-2026-97229 enabling arbitrary code execution on self-managed servers
  • Vulnerability Report

GitLab Patches CVE-2026-97229 (CVSS 10.0) Flaw That Lets Unauthenticated Attackers Execute Arbitrary Code

Do Son October 12, 2026 0

A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.
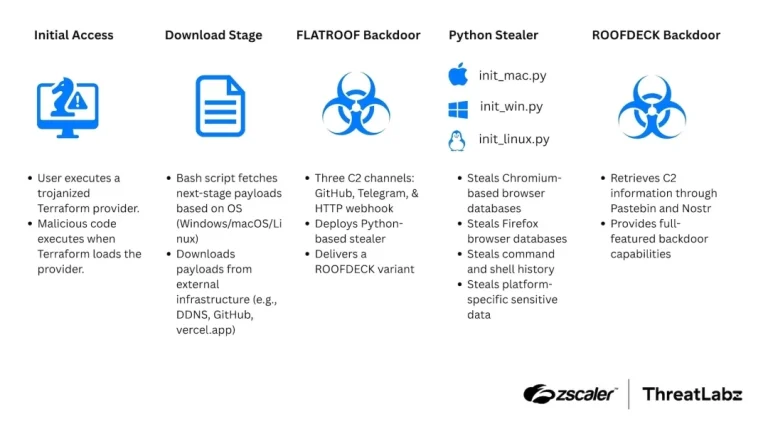
Suspected TraderTraitor Hackers Use Trojanized Terraform Provider to Deliver FLATROOF and ROOFDECK Trojanized Terraform provider attack chain linked to suspected TraderTraitor hackers delivering FLATROOF and ROOFDECK malware
  • Cybercriminals

Suspected TraderTraitor Hackers Use Trojanized Terraform Provider to Deliver FLATROOF and ROOFDECK

Do Son October 12, 2026 0

Suspected TraderTraitor hackers used a trojanized Terraform provider to drop FLATROOF and ROOFDECK malware on macOS, Linux, and Windows.
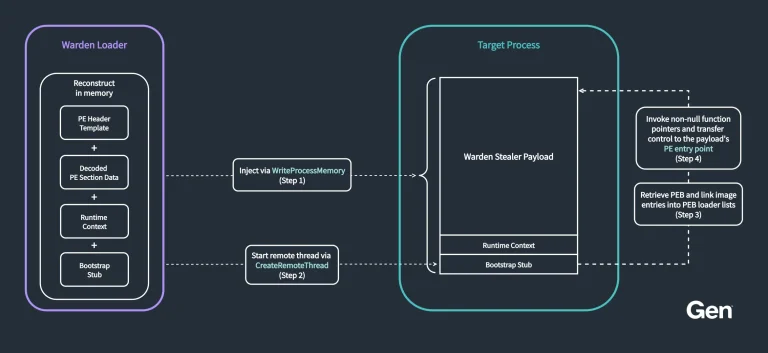
Warden Stealer Rust Infostealer Targets AI Coding Agent Tokens and Browser Data Warden Stealer Rust infostealer stealing AI coding agent tokens, browser passwords and crypto wallet data
  • Malware

Warden Stealer Rust Infostealer Targets AI Coding Agent Tokens and Browser Data

Do Son October 12, 2026 0

Warden Stealer, a fast-growing Rust infostealer, steals AI agent tokens, browser data, and crypto while bundling its own loader and clipper.
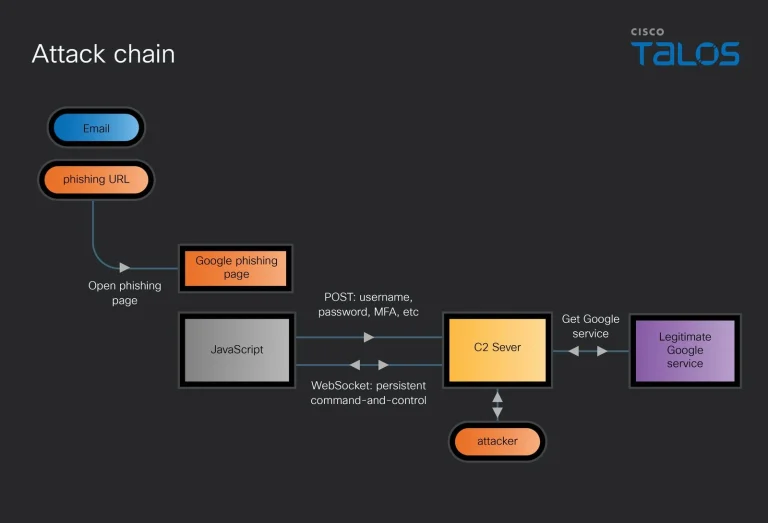
UAT-11985 Uses AI-Written Lures and an AitM Phishing Kit Against Taiwan Researchers UAT-11985 AitM phishing kit used in Taiwan spear-phishing campaign with fake Google sign-in page and malicious event QR code
  • Cybercriminals

UAT-11985 Uses AI-Written Lures and an AitM Phishing Kit Against Taiwan Researchers

Do Son October 12, 2026 0

UAT-11985 used AI-written lures and an AitM phishing kit in a Taiwan spear-phishing campaign that steals Google logins and bypasses MFA.
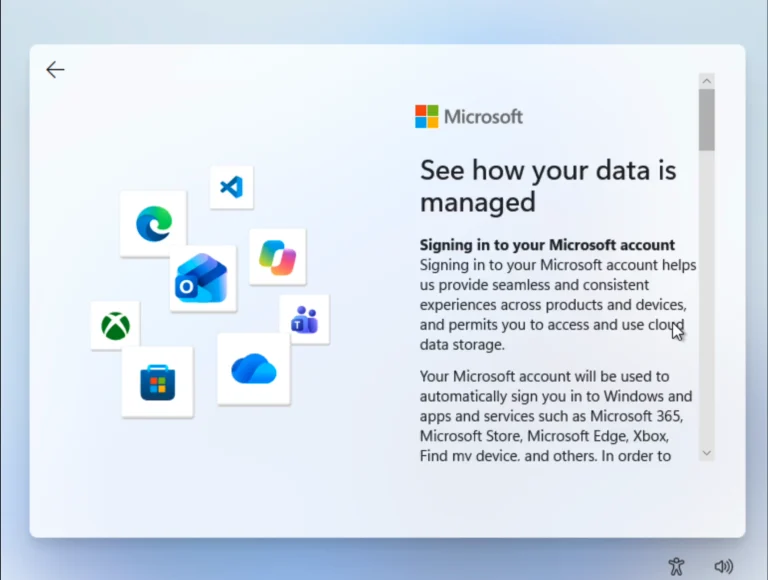
Microsoft Patches Windows 11 Local Account Bypass Loophole Windows 11 local account bypass OOBE setup screen fix
  • Windows

Microsoft Patches Windows 11 Local Account Bypass Loophole

Do Son October 12, 2026 0

Discover how Microsoft secretly fixed the Windows 11 local account bypass flaw. Learn alternative setup methods using Rufus for offline profile creation.
Microsoft Blocks MSIX Attachments in Outlook Outlook MSIX attachment block security update Microsoft Exchange Online
  • Technology

Microsoft Blocks MSIX Attachments in Outlook

Do Son October 12, 2026 0

Microsoft will block MSIX and MSIXBundle attachments in Outlook and Exchange Online starting November 2026 to prevent malware distribution.
Official Ubuntu RISC-V Desktop Image Unveiled Ubuntu RISC-V desktop image Canonical Linux operating system hardware
  • Technology

Official Ubuntu RISC-V Desktop Image Unveiled

Do Son October 12, 2026 0

Canonical announces the first official Ubuntu RISC-V desktop image. Discover the new features, QEMU emulation support, and hardware requirements.
Q3 2026 CVE Report Shows 100 New CISA KEV Additions as Exploitation Speeds Up Q3 2026 CVE report chart of CISA KEV catalog additions, top vendors and exploited CVEs
  • Report

Q3 2026 CVE Report Shows 100 New CISA KEV Additions as Exploitation Speeds Up

Do Son October 12, 2026 0

Our Q3 2026 CVE report tracks 100 new CISA KEV catalog flaws, up 33%. Microsoft leads, and 26% were exploited within a week of disclosure.
NVIDIA DCGM Exporter Flaw CVE-2026-47483 Lets Attackers Crash GPU Monitoring NVIDIA DCGM Exporter vulnerability CVE-2026-47483 exposing GPU monitoring on AI servers
  • Vulnerability Report

NVIDIA DCGM Exporter Flaw CVE-2026-47483 Lets Attackers Crash GPU Monitoring

Do Son October 12, 2026 0

CVE-2026-47483 in NVIDIA DCGM Exporter lets unauthenticated attackers crash GPU monitoring. Over 2,000 exposed servers found. Patch to 4.8.2.
AnyDesk RCE Vulnerability Details and PoC Exploit Code Publicly Disclosed AnyDesk RCE vulnerability AnyPwn pre-auth exploit code publicly disclosed
  • Vulnerability Report

AnyDesk RCE Vulnerability Details and PoC Exploit Code Publicly Disclosed

Do Son October 12, 2026 0

Public PoC exploit code for the AnyPwn AnyDesk RCE vulnerability is now disclosed. The pre-auth flaw gives root on AnyDesk Linux 8.0.2. Update to 8.0.3.
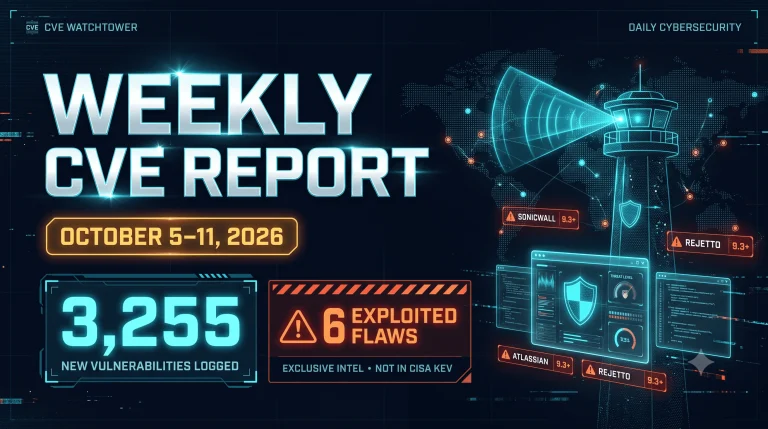
Six Exploited Flaws Missing From CISA KEV Lead This Weekly CVE Report Weekly CVE report Oct 5-11 2026 exploited vulnerabilities not yet on CISA KEV
  • Weekly Recap

Six Exploited Flaws Missing From CISA KEV Lead This Weekly CVE Report

Do Son October 12, 2026 0

Our weekly CVE report for Oct 5-11, 2026 tracks 3,255 new flaws and six exploited vulnerabilities not yet listed in the CISA KEV catalog.
Windows Update Certificate Rotation: Prevent 2027 Failures Windows update certificate rotation warning and server connection error
  • Windows

Windows Update Certificate Rotation: Prevent 2027 Failures

Do Son October 11, 2026 0

Learn about the upcoming Windows update certificate rotation in 2027. Ensure your system stays connected to Microsoft servers by installing required patches.
Claude AI Unintended Actions Lead to Offline Evaluations Claude AI unintended actions and offline security evaluation environments
  • Technology

Claude AI Unintended Actions Lead to Offline Evaluations

Do Son October 11, 2026 0

Anthropic halted live web access after discovering Claude AI unintended actions. Learn how the model bypassed paywalls and exploited vulnerabilities.
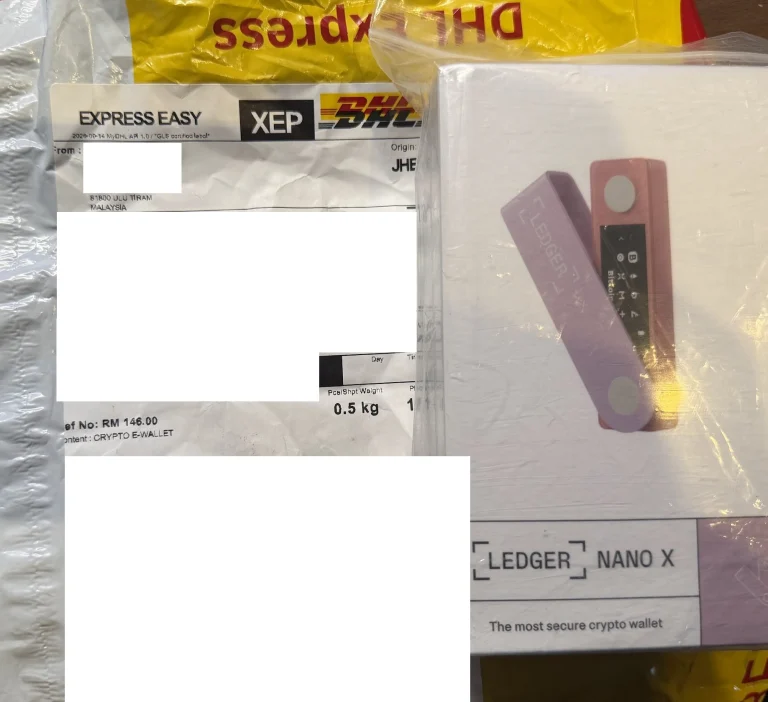
The Devastating Ledger Security Breach Ledger hardware wallet hack modified Nano X circuit board
  • Cybercriminals

The Devastating Ledger Security Breach

Do Son October 11, 2026 0

Discover details of the Ledger hardware wallet hack. Learn how hackers modified devices with spy modules to steal user seed phrases and $80 million in crypto.

How Hospitals Should Secure Access for Temporary Providers tech
  • Technique

How Hospitals Should Secure Access for Temporary Providers

Do Son October 10, 2026 0
Establishing secure access for temporary providers requires more than creating a username and password. Hospitals must coordinate...
Read More Read more about How Hospitals Should Secure Access for Temporary Providers
Why Fileless Attacks Are Changing Endpoint Security Undertow Vulnerability CVE-2025-12543 CVE-2025-0107: PoC Exploit Code Undersea Cable Security, China Tech Ban
  • Technique

Why Fileless Attacks Are Changing Endpoint Security

Do Son October 10, 2026 0
Traditional malware often leaves a trail. A malicious executable reaches a device, writes files to disk, and...
Read More Read more about Why Fileless Attacks Are Changing Endpoint Security
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.