Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
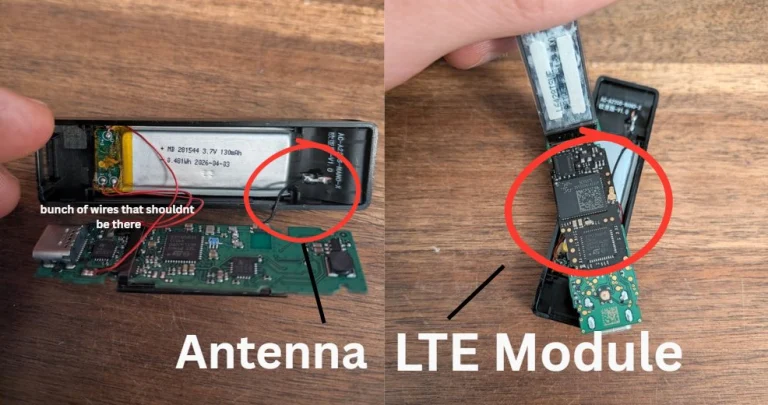
Ledger Supply Chain Attack Hits Europe via Tampered Wallets Ledger Nano X hardware wallet dismantled showing malicious LTE module modification
  • Malware

Ledger Supply Chain Attack Hits Europe via Tampered Wallets

Do Son October 13, 2026 0

A devastating Ledger supply chain attack has reached Europe. Hackers are embedding malicious LTE modules into hardware wallets to steal cryptocurrency.
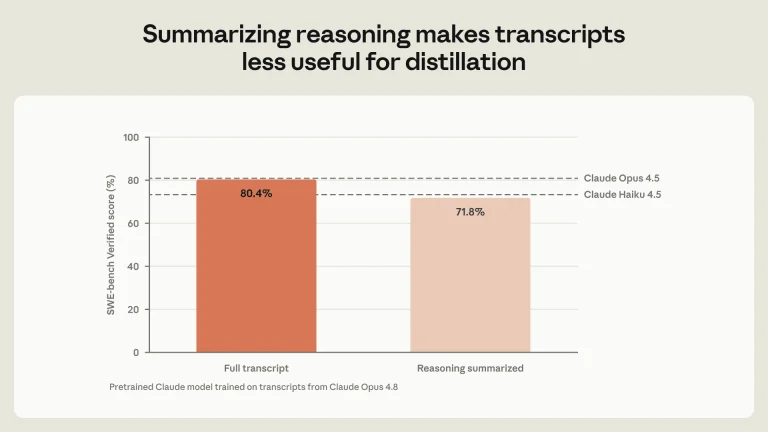
Anthropic Fortifies Claude AI Against Model Distillation Anthropic Claude AI model distillation protection mechanism
  • Technology

Anthropic Fortifies Claude AI Against Model Distillation

Do Son October 13, 2026 0

Discover how Anthropic combats unauthorized AI model distillation. Learn about the new robust protective mechanisms securing Claude AI reasoning outputs.
Bitwarden App Store License Changes to Commercial Model Bitwarden application logo and password manager interface on a mobile device
  • Technology

Bitwarden App Store License Changes to Commercial Model

Do Son October 13, 2026 0

Discover the new Bitwarden app store license changes. Learn how the shift from GPLv3 to a commercial model affects future updates and self-hosted versions.
Ubuntu 27.04 Release Schedule: Tenacious T-Rex Ubuntu 27.04 release schedule and Tenacious T-Rex codename details
  • Linux

Ubuntu 27.04 Release Schedule: Tenacious T-Rex

Do Son October 13, 2026 0

Discover the Ubuntu 27.04 release schedule. Code-named Tenacious T-Rex, this interim release brings new features and kernels for desktop enthusiasts.
G2A.COM Reports 35% Growth in Security Software Orders, Outpacing VPN Growth G2A_Logo_RGB_Color_Dark_1791212026FxtySSNVFq
  • Press Release

G2A.COM Reports 35% Growth in Security Software Orders, Outpacing VPN Growth

cybernewswire October 13, 2026 0
Amsterdam, Netherlands, 13th October 2026, CyberNewswire
Read More Read more about G2A.COM Reports 35% Growth in Security Software Orders, Outpacing VPN Growth
Malicious npm Packages From Fake Web3 Accelerator Apex Deliver Stealers and Hijack AI Coding Agents Malicious npm packages from the fake Web3 accelerator Apex delivering CloudSyncD and a Windows infostealer
  • Malware

Malicious npm Packages From Fake Web3 Accelerator Apex Deliver Stealers and Hijack AI Coding Agents

Do Son October 13, 2026 0

A fake Web3 accelerator used malicious npm packages to drop stealers on macOS and Windows and reroute AI coding agent traffic to its servers.
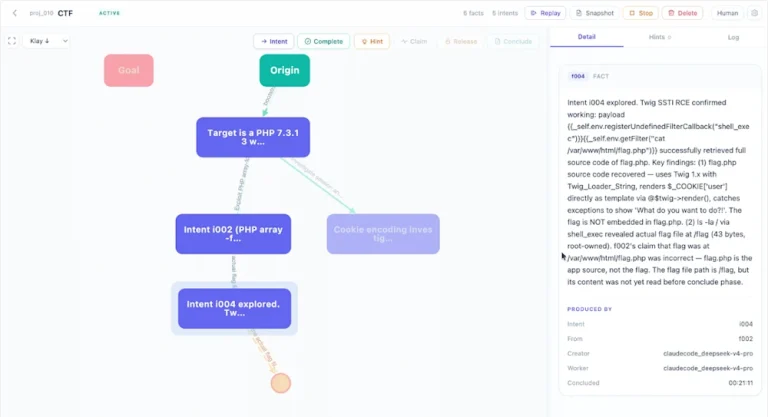
AI Agent Attack Turns One Exposed Endpoint Into a Full Server Takeover in Under 24 Hours AI agent attack using the Cairn orchestration platform to achieve a full server takeover through an exposed job endpoint
  • Malware

AI Agent Attack Turns One Exposed Endpoint Into a Full Server Takeover in Under 24 Hours

Do Son October 13, 2026 0

ReliaQuest details an AI agent attack that used one exposed endpoint and the Cairn platform to achieve a full server takeover in under 24 hours.
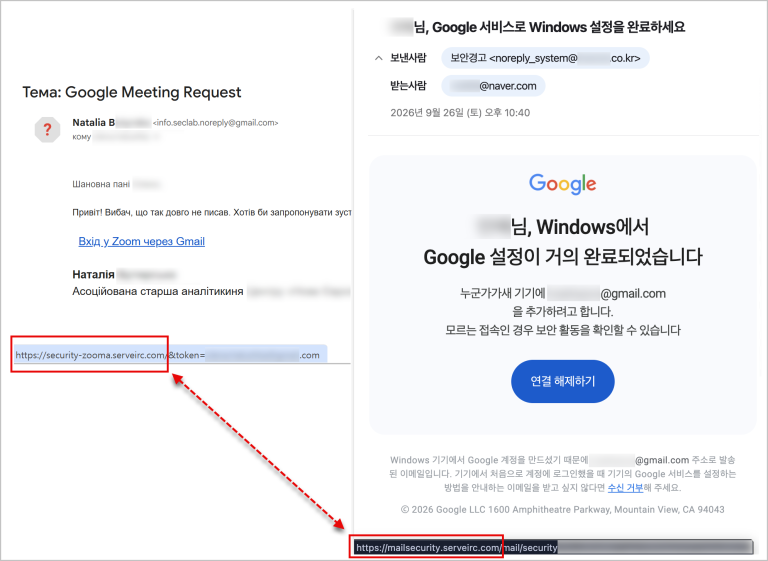
Kimsuky Spear Phishing Targets Ukrainian Diplomacy and Security Experts in Operation GitPower Kimsuky spear phishing email with fake KCSCON speaker invitation targeting Ukrainian experts in Operation GitPower
  • Cybercriminals

Kimsuky Spear Phishing Targets Ukrainian Diplomacy and Security Experts in Operation GitPower

Do Son October 13, 2026 0

Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
Windows 11 23H2 EOL: Enterprise Support Concludes Windows 11 23H2 EOL announcement on a computer screen
  • Windows

Windows 11 23H2 EOL: Enterprise Support Concludes

Do Son October 13, 2026 0

The Windows 11 23H2 EOL date is November 10, 2026. Discover how the end of support affects Enterprise editions and why immediate upgrades are crucial.
Firefox 158.0 Released: Default JPEG XL Support Firefox 158.0 release default JPEG XL format support
  • Technology

Firefox 158.0 Released: Default JPEG XL Support

Do Son October 13, 2026 0

Mozilla Firefox 158.0 is officially available, featuring default JPEG XL image format support, CSS enhancements, and advanced WebDriver automation capabilities.
Massive Cyberattack Paralyzes French Supermarket Refrigeration French supermarket cyberattack damage, Danfoss refrigeration system hack, grocery cold chain disruption
  • Cybercriminals

Massive Cyberattack Paralyzes French Supermarket Refrigeration

Do Son October 13, 2026 0

A massive French supermarket cyberattack targeted Danfoss refrigeration systems, causing catastrophic food spoilage and fires across 400 retail locations.

Intel Implements Significant Price Increases on PC Processors Intel hyper-threading return in 2028 Coral Rapids Xeon server CPUs announced by CEO Lip-Bu Tan to reclaim data center CPU market share
  • Technology

Intel Implements Significant Price Increases on PC Processors

Do Son October 13, 2026 0

Recent reports from the Taiwan supply chain indicate major Intel and AMD PC processor price hikes, with high-end CPUs seeing up to a 20% increase.
SAP Security Patch Day October 2026 Fixes CVSS 10 Cloud SDK Flaw and Three More Critical Bugs SAP Security Patch Day October 2026 critical vulnerabilities in Cloud SDK, Visual Composer and S/4HANA
  • Vulnerability Report

SAP Security Patch Day October 2026 Fixes CVSS 10 Cloud SDK Flaw and Three More Critical Bugs

Do Son October 13, 2026 0

SAP Security Patch Day October 2026 fixes four critical vulnerabilities, including a CVSS 10.0 Cloud SDK flaw and 9.9 bugs in Visual Composer and S/4HANA.
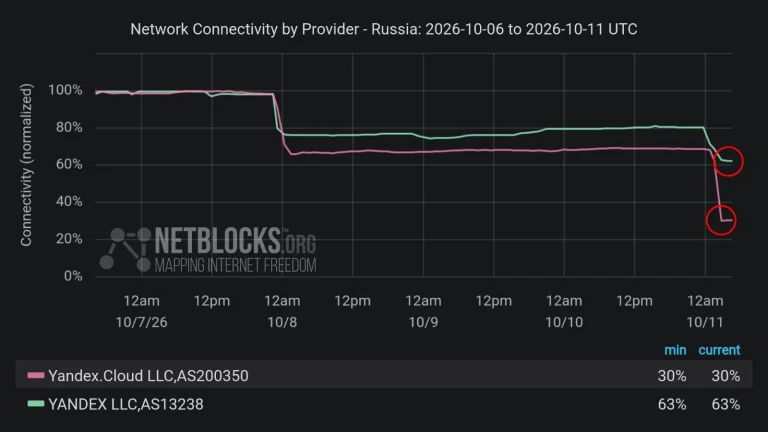
Yandex Cloud Drone Strike Causes Widespread Service Outages Yandex Cloud drone strike Vladimir data center destruction
  • Technology

Yandex Cloud Drone Strike Causes Widespread Service Outages

Do Son October 13, 2026 0

A recent Yandex Cloud drone strike in Vladimir caused severe service outages across Russia, disrupting Yandex Pay, search, and enterprise cloud operations.
Qualcomm AI Wi-Fi 8: The Next Broadband Evolution Qualcomm AI Wi-Fi 8 gateway router and related AI native broadband technology
  • Technology

Qualcomm AI Wi-Fi 8: The Next Broadband Evolution

Do Son October 13, 2026 0

Discover the new Qualcomm AI Wi-Fi 8 broadband technology. Learn how gFiber and Gemtek are transforming routers into edge computing smart service gateways.
ChatGPT Meetings Plugin Radically Transforms Audio Capture ChatGPT Meetings plugin macOS audio capture workspace integration
  • Technology

ChatGPT Meetings Plugin Radically Transforms Audio Capture

Do Son October 13, 2026 0

Explore the new ChatGPT Meetings plugin for macOS. It offers native OS-level audio capture and seamless integration with the ChatGPT Space workspace.
IBM Patches Three Critical Flaws in IBM i, Db2 Mirror and Maximo AI Service IBM critical vulnerabilities in IBM i, Db2 Mirror and Maximo enabling remote code execution
  • Vulnerability Report

IBM Patches Three Critical Flaws in IBM i, Db2 Mirror and Maximo AI Service

Do Son October 13, 2026 0

Three IBM critical vulnerabilities, rated up to CVSS 9.9, hit IBM i, Db2 Mirror and Maximo AI Service, including remote code execution. Patch now.
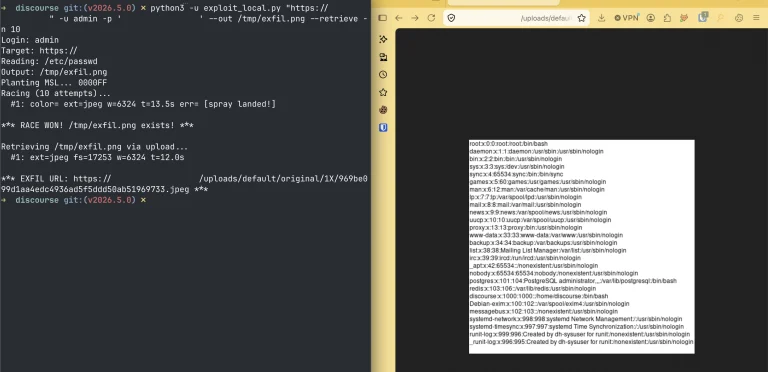
Discourse Vulnerabilities Let Attackers Hijack Pages for Every Visitor and Read Server Files Discourse vulnerabilities CVE-2026-55674 cache poisoning and CVE-2026-55420 server file read
  • Vulnerability Report

Discourse Vulnerabilities Let Attackers Hijack Pages for Every Visitor and Read Server Files

Do Son October 13, 2026 0

Two Discourse vulnerabilities, CVE-2026-55674 and CVE-2026-55420, enable cache poisoning XSS and server file reads. Patch to the fixed releases now.
Critical Ghostscript Vulnerability CVE-2026-39919 Turns Uploaded PDFs Into Remote Code Execution Ghostscript vulnerability CVE-2026-39919 enabling remote code execution through uploaded PDF files
  • Vulnerability Report

Critical Ghostscript Vulnerability CVE-2026-39919 Turns Uploaded PDFs Into Remote Code Execution

Do Son October 12, 2026 0

A critical Ghostscript vulnerability, CVE-2026-39919 (CVSS 9.8), allows remote code execution via crafted PDFs. Update Ghostscript to 10.08.0 now.
Seeworld Clay-Style 3D Previews: Explore a Scene From Every Angle image
  • Technique

Seeworld Clay-Style 3D Previews: Explore a Scene From Every Angle

Do Son October 12, 2026 0
One camera can be convincing, and the relationships in space can be convincing, but not in another...
Read More Read more about Seeworld Clay-Style 3D Previews: Explore a Scene From Every Angle
Progress Fixes 31 MarkLogic Server Vulnerabilities, Three Rated CVSS 9.9 MarkLogic Server vulnerabilities enabling privilege escalation and admin takeover
  • Vulnerability Report

Progress Fixes 31 MarkLogic Server Vulnerabilities, Three Rated CVSS 9.9

Do Son October 12, 2026 0

Progress fixed 31 MarkLogic Server vulnerabilities, including CVSS 9.9 privilege escalation flaws. Upgrade to MarkLogic 12.1 or 11.3.7 now.
CERT/CC Warns of 11 Unpatched Thelia Vulnerabilities Enabling Remote Code Execution Thelia vulnerabilities enabling remote code execution on unpatched e-commerce servers
  • Vulnerability Report

CERT/CC Warns of 11 Unpatched Thelia Vulnerabilities Enabling Remote Code Execution

Do Son October 12, 2026 0

CERT/CC lists 11 unpatched Thelia vulnerabilities, including remote code execution flaws in versions 2.6.0, 2.6.1 and 3.0.0. Lock down admin access now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.