Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Rockwell Automation Patches Privilege Escalation and Denial-of-Service Flaws Across FactoryTalk and ArmorStart Systems Rockwell Automation Warning OT Security Rockwell SQLi, Industrial Safety DoS Verve Asset Manager API OT Privilege Escalation Rockwell NAT Router, Critical Auth Bypass Rockwell ICS Privilege Escalation, MSI Repair Attack CVE-2025-7353 Critical vulnerability, industrial control systems Rockwell vulnerability, ICS security Rockwell Arena, Memory Abuse Rockwell Automation, RCE Vulnerability CVE-2025-24479 and CVE-2025-24480 - CVE-2025-0477
  • Vulnerability Report

Rockwell Automation Patches Privilege Escalation and Denial-of-Service Flaws Across FactoryTalk and ArmorStart Systems

Do Son October 15, 2025 0

Rockwell patched a flaw (CVE-2025-9067) in FactoryTalk Linx allowing SYSTEM privilege escalation via MSI repair hijacking. Other flaws risk file deletion and DoS in ICS environments.

Criminal IP to Showcase ASM and CTI Innovations at GovWare 2025 in Singapore govware___1760342660zO1NdzZcwP
  • Press Release

Criminal IP to Showcase ASM and CTI Innovations at GovWare 2025 in Singapore

cybernewswire October 14, 2025 0
Torrance, United States, 14th October 2025, CyberNewsWire
Read More Read more about Criminal IP to Showcase ASM and CTI Innovations at GovWare 2025 in Singapore
Sweet Security Named Cloud Security Leader and CADR Leader in Latio Cloud Security Report Sweet_Final_17604024024setIw1QPt
  • Press Release

Sweet Security Named Cloud Security Leader and CADR Leader in Latio Cloud Security Report

cybernewswire October 14, 2025 0
Tel Aviv, Israel, 14th October 2025, CyberNewsWire
Read More Read more about Sweet Security Named Cloud Security Leader and CADR Leader in Latio Cloud Security Report
SAP Patches Critical 10.0 Flaw in NetWeaver: Unauthenticated RCE Risk SAP Security Patch Day CVE-2025-42944, CVE-2025-42937
  • Vulnerability Report

SAP Patches Critical 10.0 Flaw in NetWeaver: Unauthenticated RCE Risk

Do Son October 14, 2025 0

SAP's October 2025 Security Patch Day addressed 13 new notes, including two critical 10.0 flaws in NetWeaver AS Java and Print Service, posing an RCE threat.

Gcore Mitigates Record-Breaking 6 Tbps DDoS Attack Gcore_Logo_1760369168YMj30ERURV
  • Press Release

Gcore Mitigates Record-Breaking 6 Tbps DDoS Attack

cybernewswire October 14, 2025 0
Luxembourg, Luxembourg, 14th October 2025, CyberNewsWire
Read More Read more about Gcore Mitigates Record-Breaking 6 Tbps DDoS Attack
Google Search Redesign Hides Option to Dismiss Ads, Forcing Users to Scroll Past ‘Sponsored Results’ Blocks Google Search Personal Intelligence, Gemini 3 Search AI Mode Google Ad Redesign, Sponsored Results Visibility
  • Technology

Google Search Redesign Hides Option to Dismiss Ads, Forcing Users to Scroll Past ‘Sponsored Results’ Blocks

Do Son October 14, 2025 0

Google consolidated ads into a "Sponsored Results" section that requires users to scroll over the entire block before they can manually hide the ads, boosting ad visibility globally.

Microsoft Unveils MAI-Image-1: New In-House AI Image Generator to Rival OpenAI and Deepen Self-Reliance Microsoft MAI-Image-1, In-House AI Microsoft Learn, MCP Server Windows Kernel Vulnerability - CVE-2024-38106 PoC exploit
  • Technology

Microsoft Unveils MAI-Image-1: New In-House AI Image Generator to Rival OpenAI and Deepen Self-Reliance

Do Son October 14, 2025 0

Microsoft announced MAI-Image-1, its first in-house AI image generation model, now in testing for Copilot and Bing Image Creator, signaling a major push for technological self-reliance.

Ivanti Endpoint Manager Discloses 13 Flaws: High-Severity RCE and 11 SQL Injection Vulnerabilities Ivanti EPMM security updates Ivanti ITSM vulnerability authenticated privilege escalation Ivanti Xtraction vulnerability CVE-2026-8043 Ivanti EPM RCE, SQL Injection Ivanti EPM, remote code execution CVE-2024-50330 - CVE-2025-0282 and CVE-2025-0283
  • Vulnerability Report

Ivanti Endpoint Manager Discloses 13 Flaws: High-Severity RCE and 11 SQL Injection Vulnerabilities

Do Son October 14, 2025 0

Ivanti disclosed 13 EPM flaws, including a High-severity RCE (CVE-2025-9713) and 11 Medium SQL Injection bugs. Fixes are scheduled for Nov 2025 and Q1 2026.

Apple Hit with Second Lawsuit Alleging AI Training Used Pirated Books from “Shadow Libraries” Apple AI Copyright, Shadow Libraries F1: The Movie, Apple CVE-2023-32434 PoC
  • Technology

Apple Hit with Second Lawsuit Alleging AI Training Used Pirated Books from “Shadow Libraries”

Do Son October 14, 2025 0

Apple faces a second class-action lawsuit claiming its AI models were trained using pirated books from "shadow libraries." The suit cites Anthropic's recent $1.5B copyright settlement.

OneDrive’s AI Facial Recognition Can Only Be Disabled Three Times Per Year for Preview Users OneDrive cloud deletion 2026 OneDrive Facial Recognition, Three-Time Limit OneDrive Suspension, Data Loss
  • Technology

OneDrive’s AI Facial Recognition Can Only Be Disabled Three Times Per Year for Preview Users

Do Son October 14, 2025 0

Early OneDrive testers found Microsoft's new AI facial recognition feature can only be disabled three times per year. The feature is opt-out by default for preview users.

Google Integrates Nano Banana AI Editor into Search, NotebookLM, and Photos to Deepen Ecosystem AI Nano Banana Integration, Google Ecosystem AI
  • Technology

Google Integrates Nano Banana AI Editor into Search, NotebookLM, and Photos to Deepen Ecosystem AI

Do Son October 14, 2025 0

Google is integrating its Nano Banana AI image editor across Search, NotebookLM, and Photos. The feature will enhance video overviews and enable AI image editing via conversational prompts.

Microsoft Patches Edge IE Mode After Hackers Exploited Chakra Zero-Day for Device Takeover Microsoft Edge Google account login interface and synchronization settings Browser Choice Alliance letter Microsoft Edge cleartext credentials memory dump Microsoft Edge auto-startup Microsoft Edge Collections sunset, export Edge Collections CSV Edge IE Mode Zero-Day, Chakra Exploit Windows Search, Microsoft Edge AI video translation, Edge browser Microsoft Editor, Edge Edge Developer tools Windows 10 ESU, Microsoft Edge Microsoft Edge, FCP Optimization CVE-2023-36735 Edge, AI Search
  • Vulnerability Report

Microsoft Patches Edge IE Mode After Hackers Exploited Chakra Zero-Day for Device Takeover

Do Son October 14, 2025 0

Microsoft updated Edge’s IE Mode policy after a Chakra zero-day was exploited via phishing. Users must now manually enable and whitelist domains to prevent remote device compromise.

OpenAI and Broadcom Partner to Develop Custom AI Accelerator Chips for 10 GW of Infrastructure OpenAI Custom Silicon, Broadcom Partnership
  • Technology

OpenAI and Broadcom Partner to Develop Custom AI Accelerator Chips for 10 GW of Infrastructure

Do Son October 14, 2025 0

OpenAI partnered with Broadcom to design and deploy custom AI accelerator chips for 10 gigawatts of infrastructure by 2029, strategically reducing its reliance on external suppliers like NVIDIA.

Chrome Will Now Auto-Revoke Notification Permissions for Inactive Websites to Reduce Spam Chrome Notification Veto, Inactive Sites
  • Technology

Chrome Will Now Auto-Revoke Notification Permissions for Inactive Websites to Reduce Spam

Do Son October 14, 2025 0

Google Chrome will now automatically revoke notification permissions from inactive websites (those with low click-through rates) to significantly reduce user interruptions and spam.

Apple Upgrades Spyware Defense: iOS 26.1 Adds Native Threat Notifications for Pegasus Attacks iOS Native Threat Alerts, Mercenary Spyware
  • Technology

Apple Upgrades Spyware Defense: iOS 26.1 Adds Native Threat Notifications for Pegasus Attacks

Do Son October 14, 2025 0

Apple introduced native threat notifications in iOS 26.1 Beta 3, allowing immediate Lockdown Mode alerts to appear directly in the Notification Center when mercenary spyware attacks are detected.

Critical Supply Chain Flaw: Clevo UEFI Firmware Leaked Intel Boot Guard Private Keys (CVE-2025-11577) Intel Boot Guard Key Leak, Clevo UEFI
  • Vulnerability Report

Critical Supply Chain Flaw: Clevo UEFI Firmware Leaked Intel Boot Guard Private Keys (CVE-2025-11577)

Do Son October 14, 2025 0

CERT/CC warns that Clevo’s UEFI firmware updates accidentally exposed Intel Boot Guard private keys (CVE-2025-11577), risking pre-boot firmware integrity on multiple OEM laptops.

Critical Elastic Cloud Flaw: CVE-2025-37729 (CVSS 9.1) Allows RCE via Jinjava Template Injection ECE Jinjava Injection, CVE-2025-37729
  • Vulnerability Report

Critical Elastic Cloud Flaw: CVE-2025-37729 (CVSS 9.1) Allows RCE via Jinjava Template Injection

Do Son October 14, 2025 0

A Critical (CVSS 9.1) flaw (CVE-2025-37729) in Elastic Cloud Enterprise allows authenticated Admin RCE. Attackers exploit Jinjava template injection to exfiltrate data and execute commands.

RMPocalypse Flaw (CVE-2025-0033) Bypasses AMD SEV-SNP to Fully Compromise Encrypted VMs AMD RMPocalypse, SEV-SNP Bypass
  • Vulnerability Report

RMPocalypse Flaw (CVE-2025-0033) Bypasses AMD SEV-SNP to Fully Compromise Encrypted VMs

Do Son October 14, 2025 0

ETH Zurich exposed RMPocalypse, a deterministic flaw in AMD SEV-SNP that bypasses memory integrity during initialization, allowing a malicious hypervisor to compromise Confidential VMs (Zen 3/4/5) with 100% success.

SVG Smuggling: Fake Colombian Judicial Lure Deploys AsyncRAT via Malicious HTA File SVG Smuggling, AsyncRAT
  • Malware

SVG Smuggling: Fake Colombian Judicial Lure Deploys AsyncRAT via Malicious HTA File

Do Son October 14, 2025 0

Seqrite discovered a campaign using SVG smuggling and a fake Colombian court lure to deploy AsyncRAT. The SVG executes JS to stage a malicious HTA file, evading detection.

Stealth C2: Hackers Abuse Discord Webhooks for Covert Data Exfiltration in npm, PyPI, and RubyGems Supply Chain Attacks SolyxImmortal Malware Python Info-Stealer Discord Webhook C2, Supply Chain Abuse
  • Malware

Stealth C2: Hackers Abuse Discord Webhooks for Covert Data Exfiltration in npm, PyPI, and RubyGems Supply Chain Attacks

Do Son October 14, 2025 0

Malicious packages across npm, PyPI, and RubyGems are exploiting Discord webhooks as stealthy, resilient C2 endpoints to exfiltrate developer config files and sensitive host data.

Hacker Alliance Demands Ransom: Scattered LAPSUS$ Hunters Claim 1 Billion Records Stolen from Salesforce Salesforce Extortion, Scattered LAPSUS$ Hunters
  • Cybercriminals

Hacker Alliance Demands Ransom: Scattered LAPSUS$ Hunters Claim 1 Billion Records Stolen from Salesforce

Do Son October 14, 2025 0

A consortium of LAPSUS$/ShinyHunters hackers launched an EaaS campaign, claiming 1 billion records stolen from 39 Salesforce customers, and demanded a ransom before an October 10 deadline.
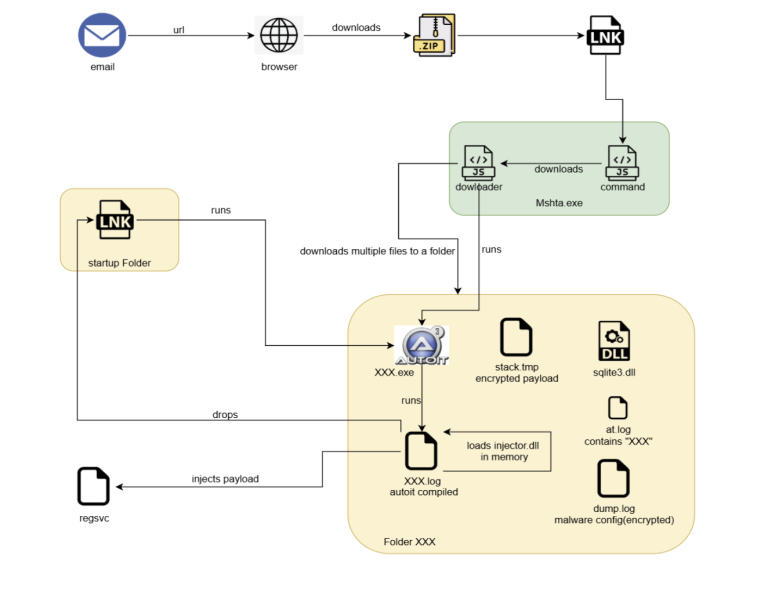
Astaroth Malware Uses Steganography in GitHub Images for Covert C2 Backup and Brazilian Bank Theft Astaroth GitHub C2, Steganography
  • Malware

Astaroth Malware Uses Steganography in GitHub Images for Covert C2 Backup and Brazilian Bank Theft

Do Son October 14, 2025 0

McAfee uncovered the Astaroth banking Trojan using GitHub for C2 backup, hiding encrypted configuration data via steganography in images to target Brazilian financial and crypto users.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59360CVSS 9.8
    The killProcesses mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59361CVSS 9.8
    The cleanIptables mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
  • CVE-2026-119923CVSS 9.3
    A heap-based buffer overflow in the TDS prelogin parser in the Babelfish for PostgreSQL extension versions 1.0-1.5, 2.1-2.15,...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.