Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Google Integrates Nano Banana AI Editor into Search, NotebookLM, and Photos to Deepen Ecosystem AI Nano Banana Integration, Google Ecosystem AI
  • Technology

Google Integrates Nano Banana AI Editor into Search, NotebookLM, and Photos to Deepen Ecosystem AI

Do Son October 14, 2025 0

Google is integrating its Nano Banana AI image editor across Search, NotebookLM, and Photos. The feature will enhance video overviews and enable AI image editing via conversational prompts.

Microsoft Patches Edge IE Mode After Hackers Exploited Chakra Zero-Day for Device Takeover Microsoft Edge Google account login interface and synchronization settings Browser Choice Alliance letter Microsoft Edge cleartext credentials memory dump Microsoft Edge auto-startup Microsoft Edge Collections sunset, export Edge Collections CSV Edge IE Mode Zero-Day, Chakra Exploit Windows Search, Microsoft Edge AI video translation, Edge browser Microsoft Editor, Edge Edge Developer tools Windows 10 ESU, Microsoft Edge Microsoft Edge, FCP Optimization CVE-2023-36735 Edge, AI Search
  • Vulnerability Report

Microsoft Patches Edge IE Mode After Hackers Exploited Chakra Zero-Day for Device Takeover

Do Son October 14, 2025 0

Microsoft updated Edge’s IE Mode policy after a Chakra zero-day was exploited via phishing. Users must now manually enable and whitelist domains to prevent remote device compromise.

OpenAI and Broadcom Partner to Develop Custom AI Accelerator Chips for 10 GW of Infrastructure OpenAI Custom Silicon, Broadcom Partnership
  • Technology

OpenAI and Broadcom Partner to Develop Custom AI Accelerator Chips for 10 GW of Infrastructure

Do Son October 14, 2025 0

OpenAI partnered with Broadcom to design and deploy custom AI accelerator chips for 10 gigawatts of infrastructure by 2029, strategically reducing its reliance on external suppliers like NVIDIA.

Chrome Will Now Auto-Revoke Notification Permissions for Inactive Websites to Reduce Spam Chrome Notification Veto, Inactive Sites
  • Technology

Chrome Will Now Auto-Revoke Notification Permissions for Inactive Websites to Reduce Spam

Do Son October 14, 2025 0

Google Chrome will now automatically revoke notification permissions from inactive websites (those with low click-through rates) to significantly reduce user interruptions and spam.

Apple Upgrades Spyware Defense: iOS 26.1 Adds Native Threat Notifications for Pegasus Attacks iOS Native Threat Alerts, Mercenary Spyware
  • Technology

Apple Upgrades Spyware Defense: iOS 26.1 Adds Native Threat Notifications for Pegasus Attacks

Do Son October 14, 2025 0

Apple introduced native threat notifications in iOS 26.1 Beta 3, allowing immediate Lockdown Mode alerts to appear directly in the Notification Center when mercenary spyware attacks are detected.

Critical Supply Chain Flaw: Clevo UEFI Firmware Leaked Intel Boot Guard Private Keys (CVE-2025-11577) Intel Boot Guard Key Leak, Clevo UEFI
  • Vulnerability Report

Critical Supply Chain Flaw: Clevo UEFI Firmware Leaked Intel Boot Guard Private Keys (CVE-2025-11577)

Do Son October 14, 2025 0

CERT/CC warns that Clevo’s UEFI firmware updates accidentally exposed Intel Boot Guard private keys (CVE-2025-11577), risking pre-boot firmware integrity on multiple OEM laptops.

Critical Elastic Cloud Flaw: CVE-2025-37729 (CVSS 9.1) Allows RCE via Jinjava Template Injection ECE Jinjava Injection, CVE-2025-37729
  • Vulnerability Report

Critical Elastic Cloud Flaw: CVE-2025-37729 (CVSS 9.1) Allows RCE via Jinjava Template Injection

Do Son October 14, 2025 0

A Critical (CVSS 9.1) flaw (CVE-2025-37729) in Elastic Cloud Enterprise allows authenticated Admin RCE. Attackers exploit Jinjava template injection to exfiltrate data and execute commands.

RMPocalypse Flaw (CVE-2025-0033) Bypasses AMD SEV-SNP to Fully Compromise Encrypted VMs AMD RMPocalypse, SEV-SNP Bypass
  • Vulnerability Report

RMPocalypse Flaw (CVE-2025-0033) Bypasses AMD SEV-SNP to Fully Compromise Encrypted VMs

Do Son October 14, 2025 0

ETH Zurich exposed RMPocalypse, a deterministic flaw in AMD SEV-SNP that bypasses memory integrity during initialization, allowing a malicious hypervisor to compromise Confidential VMs (Zen 3/4/5) with 100% success.

SVG Smuggling: Fake Colombian Judicial Lure Deploys AsyncRAT via Malicious HTA File SVG Smuggling, AsyncRAT
  • Malware

SVG Smuggling: Fake Colombian Judicial Lure Deploys AsyncRAT via Malicious HTA File

Do Son October 14, 2025 0

Seqrite discovered a campaign using SVG smuggling and a fake Colombian court lure to deploy AsyncRAT. The SVG executes JS to stage a malicious HTA file, evading detection.

Stealth C2: Hackers Abuse Discord Webhooks for Covert Data Exfiltration in npm, PyPI, and RubyGems Supply Chain Attacks SolyxImmortal Malware Python Info-Stealer Discord Webhook C2, Supply Chain Abuse
  • Malware

Stealth C2: Hackers Abuse Discord Webhooks for Covert Data Exfiltration in npm, PyPI, and RubyGems Supply Chain Attacks

Do Son October 14, 2025 0

Malicious packages across npm, PyPI, and RubyGems are exploiting Discord webhooks as stealthy, resilient C2 endpoints to exfiltrate developer config files and sensitive host data.

Hacker Alliance Demands Ransom: Scattered LAPSUS$ Hunters Claim 1 Billion Records Stolen from Salesforce Salesforce Extortion, Scattered LAPSUS$ Hunters
  • Cybercriminals

Hacker Alliance Demands Ransom: Scattered LAPSUS$ Hunters Claim 1 Billion Records Stolen from Salesforce

Do Son October 14, 2025 0

A consortium of LAPSUS$/ShinyHunters hackers launched an EaaS campaign, claiming 1 billion records stolen from 39 Salesforce customers, and demanded a ransom before an October 10 deadline.
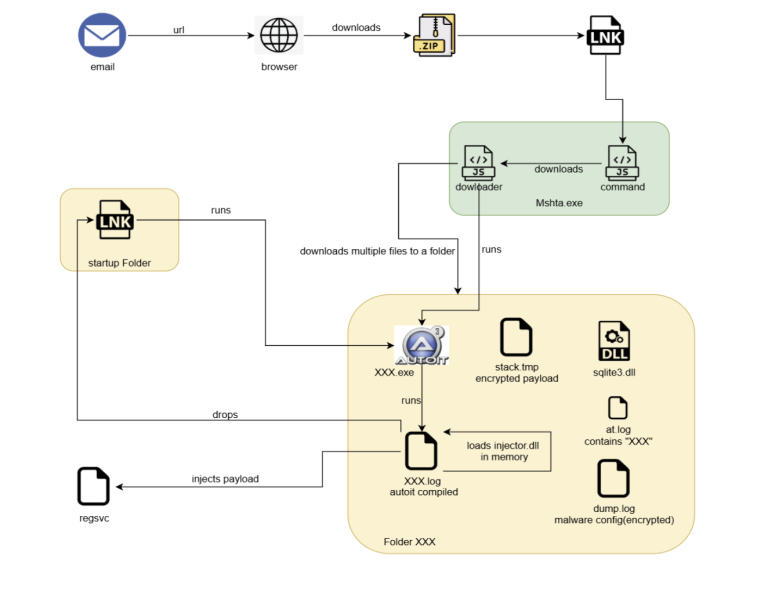
Astaroth Malware Uses Steganography in GitHub Images for Covert C2 Backup and Brazilian Bank Theft Astaroth GitHub C2, Steganography
  • Malware

Astaroth Malware Uses Steganography in GitHub Images for Covert C2 Backup and Brazilian Bank Theft

Do Son October 14, 2025 0

McAfee uncovered the Astaroth banking Trojan using GitHub for C2 backup, hiding encrypted configuration data via steganography in images to target Brazilian financial and crypto users.

iPhone Fold Hinge Costs Drop to $70-$80, Boosting Viability for Mass Production in 2026 iOS 27 Liquid Glass slider iPhone Flip rumors 2026 Setapp Mobile iOS shutdown, Apple DMA political delay tactics Apple AI pin wearable 2027, Siri Campos Gemini integration Apple AI strategy 2026, Liquid Glass interface Apple Intelligence Mac Pro Cancelled Mac Studio Future App Store antitrust, UK lawsuit iPhone Fold Hinge, Cost Optimization MacBook Pro, OLED display Apple supply chain, manufacturing automation Apple home security, smart camera Apple Earnings, AI Investment Apple EU Fine, DMA Appeal CVE-2023-23529
  • Technology

iPhone Fold Hinge Costs Drop to $70-$80, Boosting Viability for Mass Production in 2026

Do Son October 14, 2025 0

Ming-Chi Kuo reports that the iPhone Fold's critical hinge mechanism cost has been reduced to $70-$80 per unit, improving profit margins and accelerating its mass production feasibility.

MIT & Toyota Unveil Steerable Scene Generation: AI Tool Uses MCTS to Create Realistic 3D Training Worlds for Robots Steerable Scene Generation, MCTS Robotics
  • Technology

MIT & Toyota Unveil Steerable Scene Generation: AI Tool Uses MCTS to Create Realistic 3D Training Worlds for Robots

Do Son October 14, 2025 0

MIT & Toyota unveiled Steerable Scene Generation, an AI tool that uses Monte Carlo Tree Search (MCTS) to autonomously create 44M+ realistic 3D virtual scenes for training robots.

Copilot Connector Feature Unlocked: Microsoft AI Can Now Search and Integrate Google and Microsoft Cloud Data Copilot Connectors, Cross-Platform AI
  • Windows

Copilot Connector Feature Unlocked: Microsoft AI Can Now Search and Integrate Google and Microsoft Cloud Data

Do Son October 14, 2025 0

Windows Copilot's new Connector feature allows users to link Google (Gmail, Drive, Calendar) and Microsoft cloud accounts, enabling cross-platform AI search and document generation.

Apple Expected to Unveil M5 iPad Pro, Vision Pro, and MacBook Pro This Week Apple M5 Chip, Product Launch
  • Technology

Apple Expected to Unveil M5 iPad Pro, Vision Pro, and MacBook Pro This Week

Do Son October 13, 2025 0

Apple is expected to unveil the M5 iPad Pro, updated Vision Pro, and 14-inch MacBook Pro this week via press release. Leaks show the M5 chip is up to 36% faster in GPU performance.

Next-Gen AirPods: Apple Developing H3 Chip and Camera-Equipped Pro Model for Vision Pro Integration Apple Spring Event 2026 Apple Intel 14A iPhone 2028, Intel Foundry Apple Silicon iPhone 18 glass cloth shortage, Nittobo T-glass Apple crisis Apple UK App Store lawsuit appeal, Apple tax £1.5bn damages Apple AI Leadership Shakeup Giannandrea Subramanya Touchscreen MacBook Pro Apple 2026 Roadmap Apple Smart Home, Desktop Robot Apple H3 Chip, AirPods Camera Apple chips, on-device AI Apple AI, retail chatbot MacBook, Affordable Foldable iPhone, Apple Strategy Apple COO, Leadership Transition DOJ Lawsuit Apple EU Policy, App Store Fees CVE-2024-23222 Apple French antitrust fine
  • Technology

Next-Gen AirPods: Apple Developing H3 Chip and Camera-Equipped Pro Model for Vision Pro Integration

Do Son October 13, 2025 0

Mark Gurman reveals Apple is developing the H3 chip for future AirPods, including a special camera-equipped Pro edition planned for 2026 to enhance Vision Pro and AI integration.

OpenAI Wins Reprieve: Court Vacates Order Forcing Indefinite Preservation of All ChatGPT Output Data ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

OpenAI Wins Reprieve: Court Vacates Order Forcing Indefinite Preservation of All ChatGPT Output Data

Do Son October 13, 2025 0

A US federal court vacated the controversial order requiring OpenAI to indefinitely preserve all ChatGPT output data in The New York Times copyright infringement lawsuit.

Apple Discontinues Clips Video App, Removing It from App Store After Eight Years Apple vs Epic Supreme Court Apple App Store Guidelines update Apple Clips Discontinued, Video App EOL Apple EU DMA
  • Technology

Apple Discontinues Clips Video App, Removing It from App Store After Eight Years

Do Son October 13, 2025 0

Apple has officially discontinued its Clips short-form video app, removing it from the App Store. Existing users can redownload it but are advised to back up unsaved projects.

Microsoft Offers Windows 10 ESU Free for One Year, Mandating Microsoft Account and OneDrive Backup Windows 10 ESU, OneDrive Mandatory
  • Windows

Microsoft Offers Windows 10 ESU Free for One Year, Mandating Microsoft Account and OneDrive Backup

Do Son October 13, 2025 0

Microsoft offers Windows 10 ESU free for one year, but users must enroll via a Microsoft account and enable OneDrive cloud backup, signaling a push toward cloud integration.

Upgrade to MS Win 11 Pro As Low As $12 Per Key! AI Makes Every Task Easier! More PC Computer Tools On Sale As Well! Antu
  • Technique

Upgrade to MS Win 11 Pro As Low As $12 Per Key! AI Makes Every Task Easier! More PC Computer Tools On Sale As Well!

Do Son October 13, 2025 0
Finding a genuine software key within your budget can be difficult. A high regular price combined with...
Read More Read more about Upgrade to MS Win 11 Pro As Low As $12 Per Key! AI Makes Every Task Easier! More PC Computer Tools On Sale As Well!
Firefox Begins Testing In-Browser VPN Feature to Enhance IP Protection for Paid Users Firefox built-in VPN Firefox VPN data limit, Firefox VPN countries, Mozilla VPN subscription Sanitizer API Firefox 148 Security Firefox WebRTC Vulnerability CVE-2025-14321 PoC Firefox VPN Feature, Browser-Only VPN Firefox Add-ons Rollback Firefox Encryption Firefox MKV support Firefox ESR, Windows 7
  • Technology

Firefox Begins Testing In-Browser VPN Feature to Enhance IP Protection for Paid Users

Do Son October 13, 2025 0

Mozilla is developing a new, browser-only Firefox VPN feature, similar to IP Protection, that will encrypt in-browser traffic and conceal the user's IP address as a premium subscription service.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-119446CVSS 9.4
    Session Fixation vulnerability in the CLI login flow in nerves-hub nerves_hub_web allows an unauthenticated attacker to obtain an...
    📅 Updated: Nov 10, 2026
  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.