Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Kawa4096: A New Ransomware Group with Akira-Style Branding and Qilin-Like Notes CVE-2024-22394
  • Cybercriminals

Kawa4096: A New Ransomware Group with Akira-Style Branding and Qilin-Like Notes

Do Son September 23, 2025 0

AhnLab has uncovered Kawa4096, a Go-based ransomware targeting Windows, Linux, and VMware ESXi. The malware uses advanced crypto and covert backup deletion.

Beyond Trust: A New Campaign Is Using a Legitimate Tool to Deliver RATs ConnectWise ScreenConnect, RMM tool abuse
  • Malware

Beyond Trust: A New Campaign Is Using a Legitimate Tool to Deliver RATs

Do Son September 23, 2025 0

A new report reveals attackers are abusing ScreenConnect to deliver AsyncRAT and custom malware payloads, a serious supply chain risk for enterprises and MSPs.

Subtle Snail: Iran-Linked Espionage Campaign Targets European Telecom, Aerospace, and Defense Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security

Subtle Snail: Iran-Linked Espionage Campaign Targets European Telecom, Aerospace, and Defense

Do Son September 23, 2025 0

A new report reveals Subtle Snail, an Iran-nexus group, is using fake LinkedIn jobs to deliver a custom backdoor for espionage against European telecom and defense firms.

SystemBC Botnet Evolves Into High-Volume VPS Proxy Network, Powering Criminal Ecosystem Vulnerability Digest Zero-Day Exploits Seedworm APT Dindoor Backdoor RedKitten Campaign AI-Generated Malware WSUS RCE ShadowPad CVE-2025-59287
  • Malware

SystemBC Botnet Evolves Into High-Volume VPS Proxy Network, Powering Criminal Ecosystem

Do Son September 23, 2025 0

A new report from Black Lotus Labs reveals SystemBC, a malware-powered proxy network. The botnet compromises VPS systems and fuels global ransomware attacks.
Warning: New Windows 11 Updates Break Video Playback Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

Warning: New Windows 11 Updates Break Video Playback

Do Son September 22, 2025 0
According to Microsoft’s list of known issues updated on September 19, 2025, Windows 11 version 24H2 encounters...
Read More Read more about Warning: New Windows 11 Updates Break Video Playback
Windows 11 Is Getting a Native Video Wallpaper Feature Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Windows 11 Is Getting a Native Video Wallpaper Feature

Do Son September 22, 2025 0

Microsoft is bringing native video wallpaper support to Windows 11. The feature will let you set your favorite video file as a dynamic desktop background.

MediaTek Unveils Dimensity 9500, a New King for Mobile AI and Gaming MediaTek, Dimensity 9500
  • Technology

MediaTek Unveils Dimensity 9500, a New King for Mobile AI and Gaming

Do Son September 22, 2025 0

MediaTek's new Dimensity 9500 chip, built on a 3nm process, features an all-big-core design and dual NPUs to deliver massive gains in AI, gaming, and efficiency.

Apple’s In-House Chips Pave the Way for On-Device AI Revolution Apple Spring Event 2026 Apple Intel 14A iPhone 2028, Intel Foundry Apple Silicon iPhone 18 glass cloth shortage, Nittobo T-glass Apple crisis Apple UK App Store lawsuit appeal, Apple tax £1.5bn damages Apple AI Leadership Shakeup Giannandrea Subramanya Touchscreen MacBook Pro Apple 2026 Roadmap Apple Smart Home, Desktop Robot Apple H3 Chip, AirPods Camera Apple chips, on-device AI Apple AI, retail chatbot MacBook, Affordable Foldable iPhone, Apple Strategy Apple COO, Leadership Transition DOJ Lawsuit Apple EU Policy, App Store Fees CVE-2024-23222 Apple French antitrust fine
  • Technology

Apple’s In-House Chips Pave the Way for On-Device AI Revolution

Do Son September 22, 2025 0

Apple's new C1X and N1 chips in the iPhone Air, along with a powerful A19 Pro, signal its push to control hardware and enable a new era of on-device AI.

EDR-Freeze: How a Researcher Turned Windows Error Reporting Into a Weapon Against Antivirus EDR evasion, Windows Defender
  • Open Source Tool

EDR-Freeze: How a Researcher Turned Windows Error Reporting Into a Weapon Against Antivirus

Do Son September 22, 2025 0

A new technique, "EDR-Freeze," uses a built-in Windows feature to suspend antivirus and EDR processes, giving attackers a critical window to operate undetected.

LastPass Warns of New SEO Poisoning Attack Targeting Mac Users LastPass, macOS infostealer
  • Cybercriminals

LastPass Warns of New SEO Poisoning Attack Targeting Mac Users

Do Son September 22, 2025 0

LastPass warns of a new SEO poisoning campaign that uses fake GitHub repos to trick Mac users into downloading Atomic Stealer, a malware that steals data.
Meta Open-Sources New AI Model for On-Device Reasoning Meta AI usage limits token minimization strategy, Meta AI budget caps, enterprise AI cost control Meta CEO Agent Mark Zuckerberg MobileLLM-R1, on-device AI Meta Midjourney Meta Pika Labs, AI Video Generation EU AI Regulation, Meta AI Stance Meta AI, PlayAI Acquisition Proactive Chatbots Meta AI, Photo Privacy
  • Technology

Meta Open-Sources New AI Model for On-Device Reasoning

Do Son September 22, 2025 0

Meta has open-sourced its MobileLLM-R1 series, a new family of models designed for on-device reasoning in math, coding, and science.

The iPhone Fold: What to Expect from Apple’s Groundbreaking New Device iOS 27 AirDrop speed, AirDrop transfer speed, AirDrop file transfer, AWDL protocol iPhone 17e rumors iPhone Air 2 Roadmap Apple Launch Cadence Shift iPhone Air sales collapse Apple iPhone Fold iPhone Air, thinnest iPhone camera flaw
  • Technology

The iPhone Fold: What to Expect from Apple’s Groundbreaking New Device

Do Son September 22, 2025 0
Although Apple’s new iPhone 17 series and iPhone Air have only just launched this year, market attention...
Read More Read more about The iPhone Fold: What to Expect from Apple’s Groundbreaking New Device
PoC Released for CVE-2025-41243 – A Spring Cloud Gateway Flaw with CVSS 10.0 CVE-2024-22233 Spring Cloud Gateway CVE-2025-41243 PoC
  • Vulnerability

PoC Released for CVE-2025-41243 – A Spring Cloud Gateway Flaw with CVSS 10.0

Do Son September 22, 2025 0

A critical flaw (CVE-2025-41243) in Spring Cloud Gateway with a CVSS 10.0 score allows unauthenticated RCE via SpEL injection. A PoC has been released.

CountLoader: A New Malware Loader Linked to Russian Ransomware Groups Osiris Ransomware Inc Ransomware Connection CountLoader Massive Ransomware Campaign CVE-2025-0289
  • Malware

CountLoader: A New Malware Loader Linked to Russian Ransomware Groups

Do Son September 22, 2025 0

A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.

CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide Microsoft Entra ID vulnerability CVE-2025-55241
  • Vulnerability Report

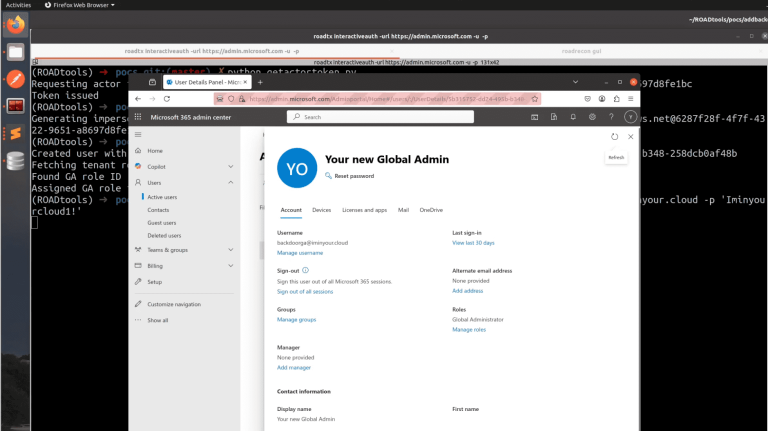
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
Do Son September 22, 2025 0

A critical flaw (CVE-2025-55241) in Microsoft Entra ID could have allowed a compromise of every tenant worldwide by bypassing security with "Actor tokens."
BiDi Swap: A Decade-Old Unicode Flaw Still Enables URL Spoofing BiDi Swap, phishing attacks Cybersecurity Threats
  • Vulnerability Report

BiDi Swap: A Decade-Old Unicode Flaw Still Enables URL Spoofing

Do Son September 22, 2025 0

A decade-old browser flaw, "BiDi Swap," allows attackers to craft deceptive URLs for phishing. The bug, found by Varonis, exploits mixed-text direction.

CopyCop Expands Its Disinformation Network With AI-Generated Content and Global Targets CopyCop Russian disinformation
  • Cyber Security

CopyCop Expands Its Disinformation Network With AI-Generated Content and Global Targets

Do Son September 22, 2025 0

A new report reveals that a Russian influence network, CopyCop, has created over 200 new AI-powered fake media sites to spread propaganda and deepfakes globally.

BlackLock Ransomware: A New Cross-Platform Threat Spreading Rapidly BlackLock
  • Cybercriminals

BlackLock Ransomware: A New Cross-Platform Threat Spreading Rapidly

Do Son September 22, 2025 0

AhnLab has uncovered BlackLock, a Go-based ransomware targeting Windows, Linux, and VMware ESXi. The malware uses advanced crypto and covert backup deletion.

PyPI Under Attack: New Malware ‘SilentSync’ Is Stealing Credentials SonicWall Reconnaissance Akira Ransomware residential proxy malware TraderTraitor BreachForums Honeypot, French Interior Ministry Leak
  • Malware

PyPI Under Attack: New Malware ‘SilentSync’ Is Stealing Credentials

Do Son September 22, 2025 0

A new supply chain attack on PyPI is delivering SilentSync, a Python RAT. The malware steals credentials and files from developers' systems.

The Database Was the Door: A Ransomware Attack Began with an Exposed Oracle Serve Knowledge Deliver RCE vulnerability FortiClient EMS Vulnerability CVE-2026-35616 Cisco SD-WAN Vulnerability CVE-2026-20122 PCPcat, Next.js RCE Salesloft breach, Salesforce CRM WIREFIRE web shell
  • Cybercriminals

The Database Was the Door: A Ransomware Attack Began with an Exposed Oracle Serve

Do Son September 22, 2025 0

A new report reveals that an exposed Oracle Database was the entry point for a ransomware attack. Hackers used a scheduler function to gain access and deploy malware.

GOLD SALEM: A New Ransomware Group Is Exploiting SharePoint Flaws Oracle EBS Zero-Day, GRACEFUL SPIDER Cracked Software, Supply Chain Attack Black Basta - NOVA stealer
  • Malware

GOLD SALEM: A New Ransomware Group Is Exploiting SharePoint Flaws

Do Son September 22, 2025 0

Sophos uncovers GOLD SALEM, a new ransomware group exploiting SharePoint flaws. The group uses EDR evasion and legitimate tools to attack global targets.

CVE-2025-9961: TP-Link Router Flaw Could Be Exploited for RCE, PoC Released TP-Link CWMP CVE-2025-9961
  • Vulnerability Report

CVE-2025-9961: TP-Link Router Flaw Could Be Exploited for RCE, PoC Released

Do Son September 22, 2025 0

A new report reveals a CWMP service flaw in TP-Link routers that can be exploited for RCE. Researchers have published a detailed write-up and a PoC on GitHub.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.