Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
ShinyHunters Syndicate Alleges Major FBI Network Compromise Bling Libra
  • Data Leak

ShinyHunters Syndicate Alleges Major FBI Network Compromise

Do Son September 24, 2026 0

Discover how the ShinyHunters hacking group claims to have orchestrated a massive FBI data breach, stealing employee records via an Oracle zero-day flaw.
Windows 11 Update Breaks Always On VPN Connections Windows 11 Always On VPN connection stuck after the September 2026 update with a port in use error
  • Windows

Windows 11 Update Breaks Always On VPN Connections

Do Son September 24, 2026 0

Windows 11 Always On VPN fails to connect after the September 2026 update. Switch to a fixed IKEv2 or SSTP protocol until Microsoft ships a permanent fix.
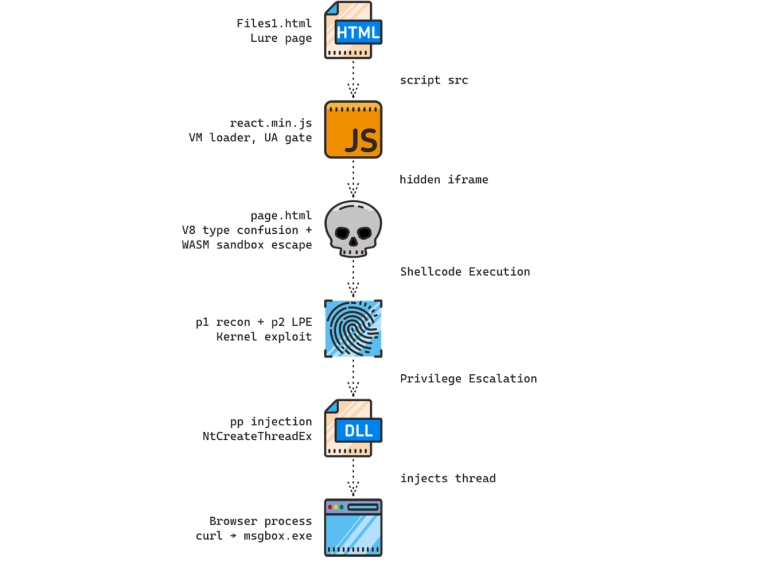
Chinese Hackers Deploy UTA0565 Zero-Day Exploits Diagram of Chinese UTA0565 zero-day exploits showing how UTA0565 zero-day exploits drop CLEANGULP malware
  • Cybercriminals

Chinese Hackers Deploy UTA0565 Zero-Day Exploits

Do Son September 24, 2026 0

Chinese UTA0565 zero-day exploits strike global targets. Learn how the UTA0565 zero-day exploits deploy CLEANGULP malware.
New TASK#STOMP PowerShell Backdoor Targets Windows Diagram showing how prompt injection attacks and prompt injection techniques threaten AI security.
  • Malware

New TASK#STOMP PowerShell Backdoor Targets Windows

Do Son September 24, 2026 0

Learn how the new TASK#STOMP PowerShell backdoor steals data. The TASK#STOMP PowerShell backdoor abuses native Windows tools for persistence.
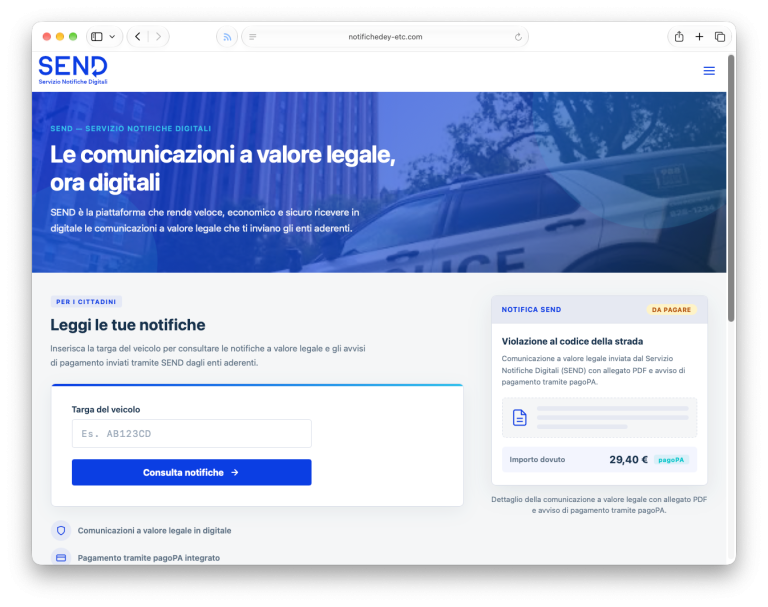
Italian Phishing Campaign Delivering an iOS Exploit Chain Italian phishing campaign delivering an iOS exploit chain and Coruna Pro V2 exploit kit details
  • Cybercriminals

Italian Phishing Campaign Delivering an iOS Exploit Chain

Do Son September 24, 2026 0

Learn about the new Italian phishing campaign delivering an iOS exploit chain. This Italian phishing campaign targets outdated iPhones using fake SEND portals.
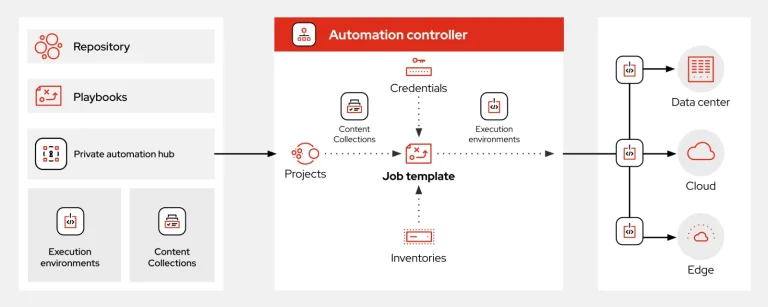
Ansible Automation Platform Vulnerabilities Allow Exploits Diagram of Ansible Automation Platform vulnerabilities and critical Ansible Automation Platform vulnerabilities
  • Vulnerability Report

Ansible Automation Platform Vulnerabilities Allow Exploits

Do Son September 24, 2026 0

Patch these critical Ansible Automation Platform vulnerabilities to prevent privilege escalation. Ansible Automation Platform vulnerabilities expose secrets.
CVE-2026-48842: Roundcube Webmail Vulnerability Exploited in the Wild Diagram of the exploited Roundcube Webmail vulnerability and SQL injection attack chain
  • Vulnerability Report

CVE-2026-48842: Roundcube Webmail Vulnerability Exploited in the Wild

Do Son September 24, 2026 0

An exploited Roundcube Webmail vulnerability allows SQL injection attacks. Learn how CVE-2026-48842 impacts servers and apply the latest patches immediately.
Critical Rancher XSS Vulnerability Exposes Admin Credentials Diagram explaining the Rancher XSS vulnerability and CVE-2026-88804 attack chain
  • Vulnerability Report

Critical Rancher XSS Vulnerability Exposes Admin Credentials

Do Son September 24, 2026 0

A critical Rancher XSS vulnerability tracked as CVE-2026-88804 exposes admin sessions. Update your clusters immediately to prevent system compromise.
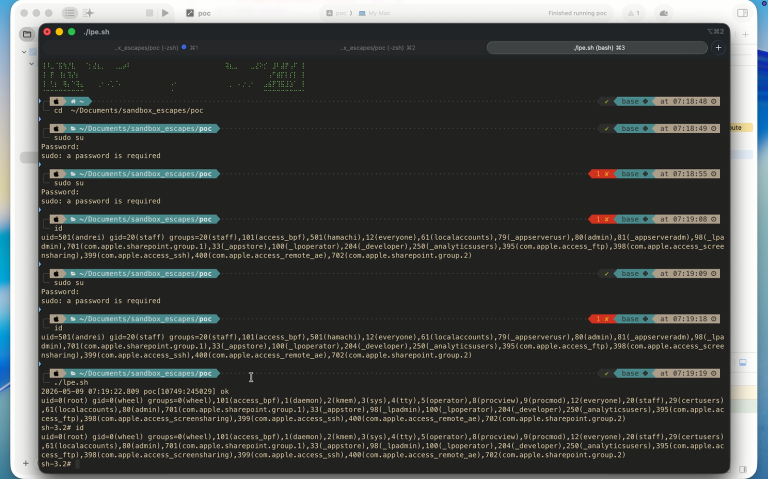
macOS DesktopServicesHelper LPE Vulnerability Details and PoC Disclosed Diagram explaining the critical macOS DesktopServicesHelper vulnerability and root escalation chain
  • Vulnerability Report

macOS DesktopServicesHelper LPE Vulnerability Details and PoC Disclosed

Do Son September 24, 2026 0

Details and PoC for the critical macOS DesktopServicesHelper vulnerability are public. Learn how CVE-2026-43783 enables root access.
Critical cPanel Security Vulnerabilities Allow Root Escalation Diagram illustrating cPanel security vulnerabilities and critical cPanel security vulnerabilities affecting WHM
  • Vulnerability Report

Critical cPanel Security Vulnerabilities Allow Root Escalation

Do Son September 24, 2026 0

cPanel patched critical cPanel security vulnerabilities including CVE-2026-87899. Update cPanel and WP Toolkit now to prevent privilege escalation.
Fluent Bit Vulnerability Details and PoC Disclosed Diagram of the critical Fluent Bit vulnerability CVE-2026-61674 buffer overflow
  • Vulnerability Report

Fluent Bit Vulnerability Details and PoC Disclosed

Do Son September 24, 2026 0

Technical details and a PoC for a critical Fluent Bit vulnerability (CVE-2026-61674) are public. Patch this Fluent Bit vulnerability to prevent RCE attacks.
Critical GitHub Enterprise Server Vulnerabilities Addressed Diagram showing the attack chain of critical GitHub Enterprise Server vulnerabilities
  • Vulnerability Report

Critical GitHub Enterprise Server Vulnerabilities Addressed

Do Son September 24, 2026 0

Critical GitHub Enterprise Server vulnerabilities allow remote code execution. Update your instances now to mitigate these high-severity security flaws.
GitLab Critical Patch Release Fixes Severe RCE Flaws Diagram illustrating the GitLab critical patch release mitigating the GitLab RCE vulnerability
  • Vulnerability Report

GitLab Critical Patch Release Fixes Severe RCE Flaws

Do Son September 23, 2026 0

A GitLab critical patch release addresses two CVEs enabling a GitLab RCE vulnerability. Update your CI/CD pipelines to prevent arbitrary code execution.
Apache Tomcat Vulnerabilities Fixed in 11.0.26 Update Diagram illustrating Apache Tomcat vulnerabilities including CVE-2026-87022
  • Vulnerability Report

Apache Tomcat Vulnerabilities Fixed in 11.0.26 Update

Do Son September 23, 2026 0

Apache patched 15 Apache Tomcat vulnerabilities in version 11.0.26. Update to secure your servers against HTTP/2, AJP, and WebSocket DoS flaws today.
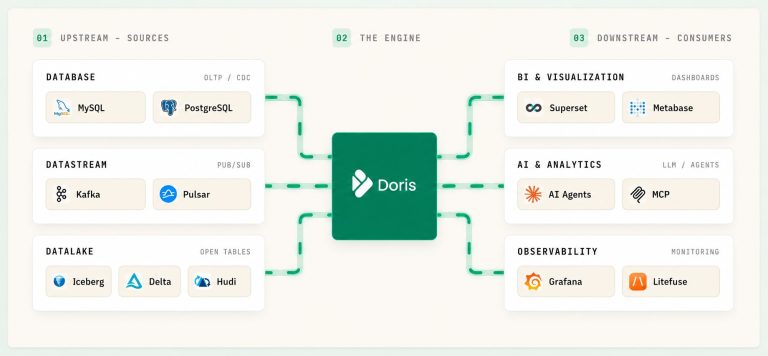
Apache Doris Vulnerabilities Patched in New Updates Diagram of patched Apache Doris vulnerabilities and attack paths
  • Vulnerability Report

Apache Doris Vulnerabilities Patched in New Updates

Do Son September 23, 2026 0

The team patched Apache Doris vulnerabilities in new updates. Learn how these Apache Doris vulnerabilities impact clusters and update now.
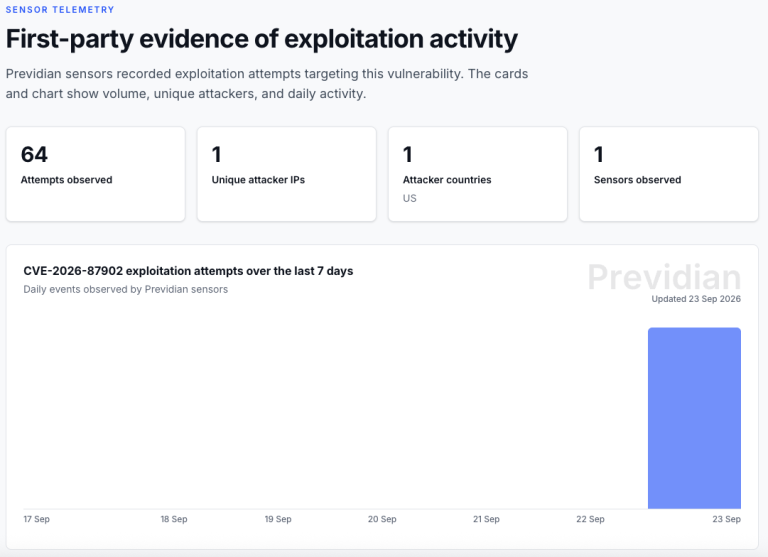
Exploited WordPress RCE Vulnerability Details and PoC Disclosed Diagram showing the exploited WordPress RCE vulnerability and attack chain
  • Vulnerability Report

Exploited WordPress RCE Vulnerability Details and PoC Disclosed

Do Son September 23, 2026 0

An exploited WordPress RCE vulnerability (CVE-2026-87902) is under attack. Details and PoC exploit code are public. Patch your sites now.
Critical ManageEngine Security Vulnerabilities Require Immediate Patching ManageEngine security vulnerabilities and OpManager vulnerabilities overview
  • Vulnerability Report

Critical ManageEngine Security Vulnerabilities Require Immediate Patching

Do Son September 23, 2026 0

ManageEngine security vulnerabilities expose servers to remote code execution. Patch these OpManager vulnerabilities and CVE-2026-19599 to secure your network.
Vidar Information Stealer Upgrades Evasion Tactics AutoIt-Delivering-Vidar-Stealer
  • Malware

Vidar Information Stealer Upgrades Evasion Tactics

Do Son September 23, 2026 0

Discover the latest Vidar information stealer obfuscation tactics. ThreatLabz reveals how the malware uses a virtual machine and custom stream ciphers.

WordPress Stored XSS Details and PoC Publicly Disclosed CVE-2024-11972 - Hunk Companion
  • Vulnerability Report

WordPress Stored XSS Details and PoC Publicly Disclosed

Do Son September 23, 2026 0

Details and PoC exploit code for a critical WordPress stored XSS are public. Learn how CVE-2026-93485 enables RCE and patch WordPress today.
Leaked GitHub App Private Keys Expose Critical Infrastructure Diagram showing leaked GitHub App private keys and how GitHub App private keys compromise repositories
  • Data Leak

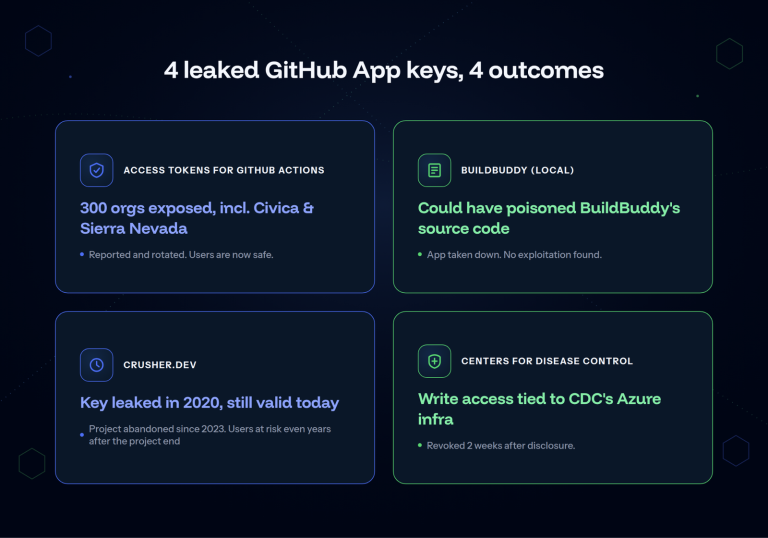
Leaked GitHub App Private Keys Expose Critical Infrastructure

Do Son September 23, 2026 0

GitGuardian discovered 474 leaked GitHub App private keys still active. Learn how exposed GitHub App private keys threaten organizations like the CDC.
Apple Introduces the iOS 27 Auto Lock Feature iOS 27 Auto Lock feature securing a snatched iPhone and protecting user data
  • Technology

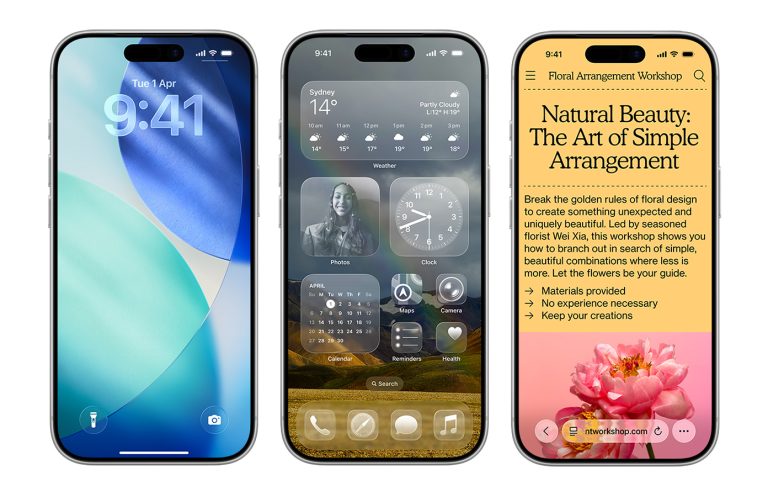
Apple Introduces the iOS 27 Auto Lock Feature

Do Son September 23, 2026 0

Discover how the new iOS 27 Auto Lock feature protects your iPhone. This advanced anti-theft security automatically locks snatched devices to secure data.
Trump Mandates Super Intelligence to Replace AI Terminology Donald Trump announcing super intelligence mandate at a press conference
  • Technology

Trump Mandates Super Intelligence to Replace AI Terminology

Do Son September 23, 2026 0

Discover the new Trump super intelligence mandate. The US government will replace the term artificial intelligence, sparking debate across the tech industry.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-118333CVSS 9.3
    Missing authorization in Video in Google Chrome prior to 156.0.8078.73 allowed a remote attacker to bypass web origin...
    📅 Updated: Oct 30, 2026
  • CVE-2026-118337CVSS 9.3
    Improper access control in Forms in Google Chrome prior to 156.0.8078.73 allowed a remote attacker to bypass web...
    📅 Updated: Oct 30, 2026
  • CVE-2026-104339CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.3 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107327CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107328CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107329CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-110186CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.