Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
MemTensor MemOS Compromise Exposes AI Developer Secrets Diagram showing the MemTensor MemOS compromise details and how the MemTensor MemOS compromise affects developers
  • Malware

MemTensor MemOS Compromise Exposes AI Developer Secrets

Do Son September 23, 2026 0

Discover the critical MemTensor MemOS compromise details. This MemTensor MemOS compromise targets AI developers via malicious npm and PyPI packages.
Chrome Extension Popups Freeze for macOS Users Chrome extension popup freeze bug on macOS delaying 1Password and other extension windows
  • Technology

Chrome Extension Popups Freeze for macOS Users

Do Son September 23, 2026 0

A Chrome extension popup freeze bug on macOS delays 1Password and other extensions by minutes. Google has flagged it high priority but has no fix yet.
How Contractors Can Choose AI Estimating Software Without Getting Distracted By Hype d
  • Technique

How Contractors Can Choose AI Estimating Software Without Getting Distracted By Hype

Do Son September 23, 2026 0

Learn how contractors can compare AI estimating software based on workflow fit, scope clarity, pricing control, proposal quality, and real ROI.
Android May Let You Unlock a Forgotten PIN With Google Android 17 Unlock with Google Account feature recovering a forgotten PIN without a factory reset
  • Android

Android May Let You Unlock a Forgotten PIN With Google

Do Son September 23, 2026 0

Android 17 QPR2 Beta 5 code hints at an Unlock with Google Account feature to recover a forgotten PIN without a factory reset. Here is how it may work.
iPhone 18 Pro Face ID Failures Trigger System Restarts iPhone 18 Pro Max Face ID error screen and system crash illustration
  • Technology

iPhone 18 Pro Face ID Failures Trigger System Restarts

Do Son September 23, 2026 0

Discover why the iPhone 18 Pro Face ID fails and causes system restarts. Learn how to avoid this iOS 27 bug when accessing password-protected apps.
SideCopy APT Campaign Targets Academic Institutions CoreRAT malware decoy PDF used in Core Werewolf phishing attack on Russian defense targets
  • Cybercriminals

SideCopy APT Campaign Targets Academic Institutions

Do Son September 23, 2026 0

The SideCopy APT campaign deploys custom RATs. Learn how the SideCopy APT campaign malware exploits mshta to target academic and government networks.
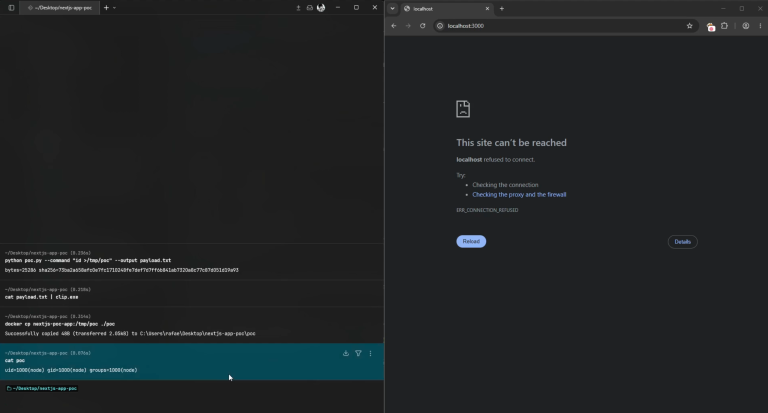
Critical Next.js RCE Vulnerability Fixed in Version 16.3.6 Diagram illustrating the critical Next.js RCE vulnerability in image generation
  • Vulnerability Report

Critical Next.js RCE Vulnerability Fixed in Version 16.3.6

Do Son September 23, 2026 0

Vercel fixed a critical Next.js RCE vulnerability in image generation. Update to patch this Next.js RCE vulnerability and secure your apps.
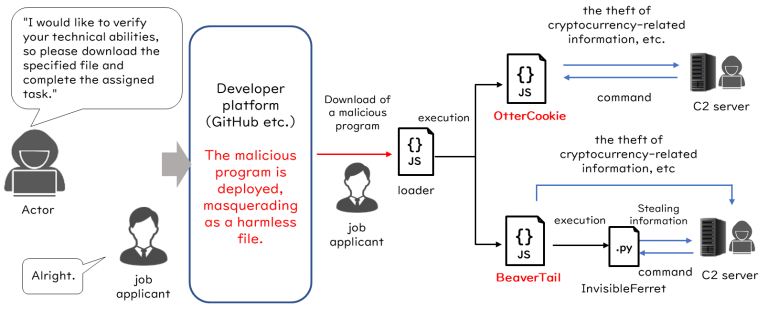
The WaterPlum Cyber Actor Group Targets Global IT Professionals A diagram detailing the North Korean WaterPlum cyber actor group infection chain
  • Cybercriminals

The WaterPlum Cyber Actor Group Targets Global IT Professionals

Do Son September 23, 2026 0

Discover how the North Korean WaterPlum cyber actor group uses fake job interviews to steal crypto and infiltrate networks globally.
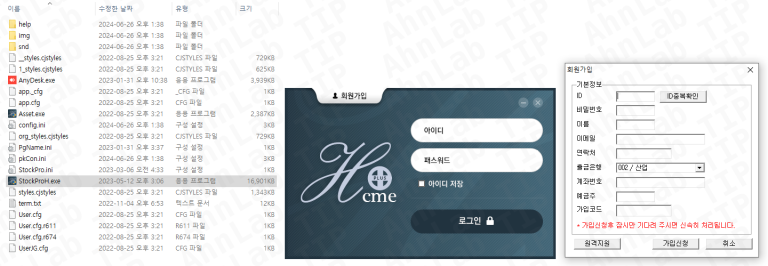
KRSID Ransomware Targets Private HTS Investment Platforms KRSID ransomware targeting private HTS malware victims
  • Malware

KRSID Ransomware Targets Private HTS Investment Platforms

Do Son September 23, 2026 0

Fraudulent investment groups are using the UBP Asset private HTS malware to distribute KRSID ransomware. Learn how to protect your trading accounts today.
Critical IBM FTM Vulnerabilities Expose Financial Systems to Attack Diagram showing critical IBM FTM vulnerabilities and authentication bypass risks
  • Vulnerability Report

Critical IBM FTM Vulnerabilities Expose Financial Systems to Attack

Do Son September 23, 2026 0

IBM patched critical IBM FTM vulnerabilities in Financial Transaction Manager. Learn how these IBM FTM vulnerabilities impact systems and update immediately.
Critical HPE ALE Vulnerabilities Allow Complete Server Takeover Diagram illustrating critical HPE ALE vulnerabilities and system takeover risks
  • Vulnerability Report

Critical HPE ALE Vulnerabilities Allow Complete Server Takeover

Do Son September 23, 2026 0

Critical HPE ALE vulnerabilities threaten enterprise networks. Update HPE ALE vulnerabilities now to prevent unauthorized access and remote code execution.
Critical IBM DataStage Vulnerabilities Threaten Cloud Environments Diagram illustrating the impact of IBM DataStage vulnerabilities
  • Vulnerability Report

Critical IBM DataStage Vulnerabilities Threaten Cloud Environments

Do Son September 23, 2026 0

IBM DataStage vulnerabilities expose cloud environments to RCE and DoS. Upgrade Cloud Pak for Data to version 5.4 patch 7 immediately.
Chrome 154 Release Patches 108 Security Vulnerabilities Graphic highlighting the Chrome 154 security fixes and 108 security vulnerabilities patched
  • Vulnerability Report

Chrome 154 Release Patches 108 Security Vulnerabilities

Do Son September 23, 2026 0

Google Chrome 154 patches 108 security vulnerabilities, including critical memory corruption flaws. Update your browser immediately to stay secure.
SolarWinds Observability Vulnerabilities Enable Remote Code Execution Diagram detailing SolarWinds Observability vulnerabilities and CVE-2026-28324 execution flow
  • Vulnerability Report

SolarWinds Observability Vulnerabilities Enable Remote Code Execution

Do Son September 23, 2026 0

SolarWinds Observability vulnerabilities allow RCE via CVE-2026-28324. Update to version 2026.2.3 to secure your monitoring infrastructure today.
D-Link DAP-1360 Vulnerability Details and PoC Disclosed Diagram of the D-Link DAP-1360 vulnerability CVE-2026-95675 execution flow
  • Vulnerability Report

D-Link DAP-1360 Vulnerability Details and PoC Disclosed

Do Son September 23, 2026 0

Technical details and a PoC for the D-Link DAP-1360 vulnerability (CVE-2026-95675) are public. Learn how this unauthenticated flaw impacts legacy routers.
NVIDIA Patches Critical Vulnerabilities in Infrastructure Controller Diagram showing critical NVIDIA Infrastructure Controller vulnerabilities and CVE-2026-65113
  • Vulnerability Report

NVIDIA Patches Critical Vulnerabilities in Infrastructure Controller

Do Son September 22, 2026 0

NVIDIA patched critical NVIDIA Infrastructure Controller vulnerabilities across Linux builds. Learn how CVE-2026-65113 impacts systems and update now.
Microsoft Disrupts EvilTokens Cybercrime Platform Disrupting EvilTokens cybercrime platform infrastructure and the EvilTokens cybercrime platform portal
  • Cybercriminals

Microsoft Disrupts EvilTokens Cybercrime Platform

Do Son September 22, 2026 0

Microsoft led a coalition disrupting EvilTokens cybercrime platform. Learn how the EvilTokens cybercrime platform used AI and device code phishing.
Exploited BIG-IP APM Vulnerability Allows Remote Code Execution Diagram detailing the exploited BIG-IP APM vulnerability and CVE-2026-94127 flow
  • Vulnerability Report

Exploited BIG-IP APM Vulnerability Allows Remote Code Execution

Do Son September 22, 2026 0

An exploited BIG-IP APM vulnerability tracked as CVE-2026-94127 allows RCE attacks. Secure your BIG-IP APM vulnerability deployments with new F5 hotfixes.
Critical ManageEngine ADSelfService Plus Vulnerability Fixed Diagram of the ManageEngine ADSelfService Plus vulnerability affecting the GINA client
  • Vulnerability Report

Critical ManageEngine ADSelfService Plus Vulnerability Fixed

Do Son September 22, 2026 0

A critical ManageEngine ADSelfService Plus vulnerability (CVE-2026-74849) allows system compromise. Update to build 7001 to secure your endpoints.
Exploited Check Point VPN Vulnerability Hit in the Wild Diagram of the exploited Check Point VPN vulnerability affecting gateways
  • Vulnerability Report

Exploited Check Point VPN Vulnerability Hit in the Wild

Do Son September 22, 2026 0

An exploited Check Point VPN vulnerability allows remote code execution. Patch this Check Point VPN vulnerability now to block active in-the-wild attacks.
CVE-2026-87902: Critical WordPress RCE Flaw Fixed in Version 7.1.2 Diagram detailing the critical WordPress RCE vulnerability tracked as CVE-2026-87902
  • Vulnerability Report

CVE-2026-87902: Critical WordPress RCE Flaw Fixed in Version 7.1.2

Do Son September 22, 2026 0

WordPress 7.1.2 patches a critical WordPress RCE vulnerability (CVE-2026-87902). Update your site to prevent conditional remote code execution.
Wild Exploitation Of CVE-2026-93616 Check Point Management Server Lets Attackers Execute Arbitrary Scripts hacked-2
  • Vulnerability Report

Wild Exploitation Of CVE-2026-93616 Check Point Management Server Lets Attackers Execute Arbitrary Scripts

Do Son September 22, 2026 0

A critical exploited Check Point Management vulnerability (CVE-2026-93616) allows attackers to execute arbitrary scripts. Secure your servers now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-118333CVSS 9.3
    Missing authorization in Video in Google Chrome prior to 156.0.8078.73 allowed a remote attacker to bypass web origin...
    📅 Updated: Oct 30, 2026
  • CVE-2026-118337CVSS 9.3
    Improper access control in Forms in Google Chrome prior to 156.0.8078.73 allowed a remote attacker to bypass web...
    📅 Updated: Oct 30, 2026
  • CVE-2026-104339CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.3 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107327CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107328CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-107329CVSS 9.9
    IBM Langflow OSS 1.0.0 through 1.12.4 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-110186CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.