
 cybernewswire
Menlo Park, United States, 26th August 2025, CyberNewsWire

Silver Spring, USA / Maryland, 26th August 2025, CyberNewsWire

 Do Son
A new Google report reveals that its AI agent, Big Sleep, discovered and foiled a critical SQLite flaw (CVE-2025-6965) before attackers could exploit it.

A new APK teardown reveals Google is actively working on bringing its Quick Share feature to iOS, a move that could finally bridge the gap in file sharing between Android and Apple.

Perplexity AI is launching a new subscription model that will pay publishers for content used in its AI-powered search, a major shift in how AI platforms interact with the web.

The Langflow project has issued an important security advisory regarding a newly discovered vulnerability that poses a...

A new report reveals a critical SSRF vulnerability in the PhpSpreadsheet library. The flaw could allow attackers to access internal networks and sensitive data.
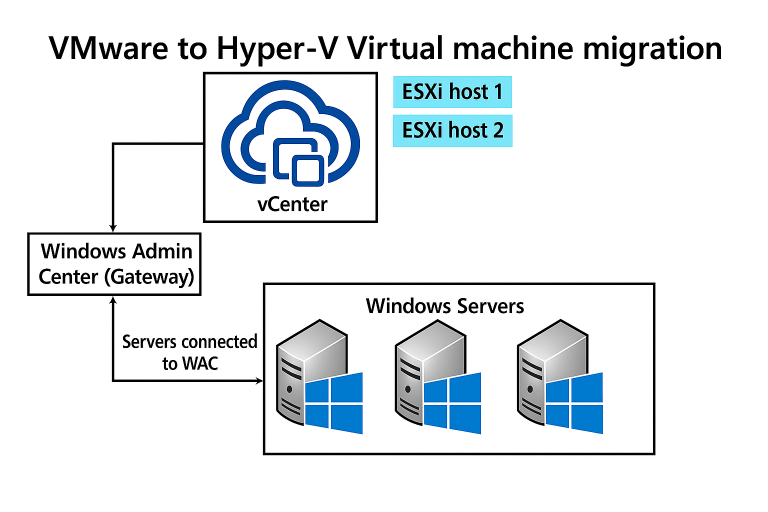
Microsoft has released a new VM Conversion utility in Windows Admin Center, allowing enterprises to seamlessly migrate their VMs from VMware to Hyper-V.

Google is overhauling its smart home line with new Nest cameras and a smart speaker integrated with Gemini AI, promising a more secure and convenient home experience.

Reports have long suggested that Apple may introduce 7.5W wireless reverse charging in the upcoming iPhone 17...

Elon Musk's xAI has sued Apple and OpenAI, alleging the two companies colluded to create a monopoly that unfairly stifles competition in the AI market.

A new study reveals X/Twitter is the most aggressive social media app for location tracking, while YouTube collects the least.

Apple is reportedly planning to launch its first foldable iPhone in 2026, which may reintroduce Touch ID, and is considering a radical all-glass iPhone for its 20th anniversary in 2027.

YouTube has admitted to secretly using AI to "enhance" Shorts videos without creators' consent, a move that has sparked backlash over transparency and trust.

NVIDIA has launched NVLink Fusion, a new initiative that allows third-party chipmakers to integrate their custom processors with NVIDIA's GPUs to create massive AI superfactories.

Two critical flaws in the open-source BI tool DataEase allow attackers to achieve remote code execution and arbitrary file writes, exposing unpatched systems to compromise.
CISA has added two Citrix and one critical Git vulnerability to its KEV Catalog, warning that all three flaws are being actively exploited by malicious actors.

GreyNoise reports a massive, coordinated scanning campaign targeting Microsoft RDP services. Attackers are probing tens of thousands of IPs to prepare for future attacks.

A new report reveals a rapidly growing global phishing campaign using fake voicemails and purchase orders to distribute UpCrypter, a sophisticated malware loader.

TP-Link has patched a high-severity flaw (CVE-2025-8627) in its KP303 Smart Plug. The vulnerability allows remote attackers to issue unauthenticated commands.

A new Rapid7 report reveals four critical flaws in Securden's Privileged Access Manager, including authentication bypass and RCE, that could expose passwords and secrets.
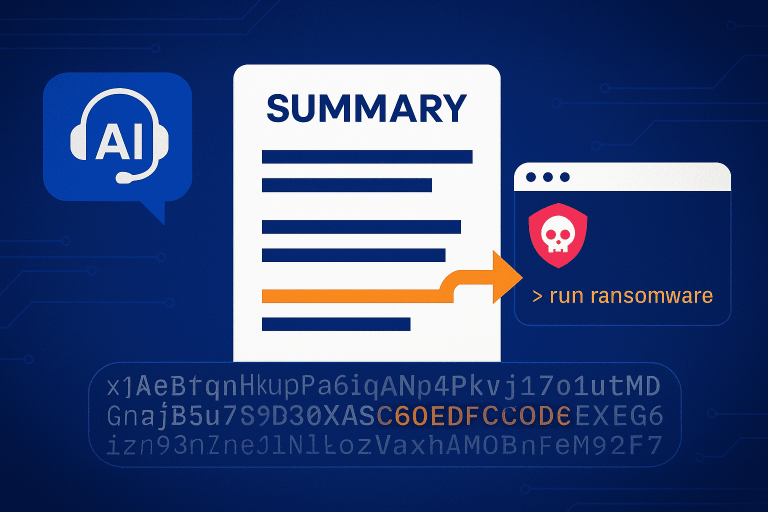
A new report reveals how attackers are using invisible text and "prompt overdose" to trick AI summarizers into delivering ransomware instructions to users.