
 Do Son
The IETF has proposed a new HTTP header to label AI-generated content. The voluntary "AI-Disclosure" header would help bots and archives filter out low-quality material.

A critical command injection flaw (CVE-2025-57105) has been found in D-Link's end-of-life DI-7400G+ router series. Because the devices are unsupported, no patch is coming.

A supply chain attack on the Nx build system is stealing crypto wallets and SSH keys from developers. The malware also abuses AI tools for data exfiltration.

Apple is reportedly weighing acquisitions of AI startups Perplexity AI and Mistral AI, a move that highlights a major internal rift over the company's AI strategy.

Microsoft has released a new preview update, KB5063842, for Windows 10 version 22H2 to address several known...

Walmart has selected Broadcom's VMware Cloud Foundation to modernize its tech stack. The partnership will enable the retail giant to scale its private cloud and edge computing infrastructure.
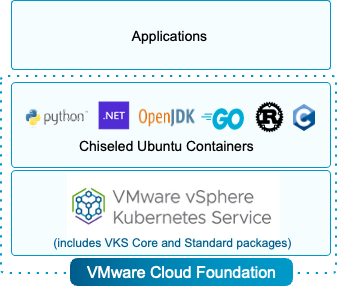
Broadcom and Canonical have partnered to integrate Ubuntu into VMware Cloud Foundation, providing streamlined, secure, and efficient AI and cloud-native application deployment.

Google's new Gemini model brings major upgrades to AI image editing, focusing on character consistency, multi-stage edits, and digital watermarks for transparency.

Google will soon require all sideloaded Android apps to come from a verified developer. The move aims to combat malware, which is 50x more common in unverified apps.

Broadcom has unveiled new security services for VMware Cloud Foundation, focusing on compliance, Zero Trust, and post-quantum cryptography to secure AI workloads.

Anthropic's new Claude AI extension for Chrome allows it to read websites, but the tool also introduces a risk of prompt injection attacks that could lead to data theft.

Apple has confirmed its "Awe dropping" event for September 9, where it's expected to unveil a new iPhone 17 Air, Apple Watch 11, and AirPods Pro 3.

A new report reveals that Google's AI agent, Big Sleep, discovered and fixed a critical use-after-free vulnerability (CVE-2025-9478) in Chrome's ANGLE engine.

A new report reveals the Hook Android trojan has evolved into a hybrid threat with ransomware-style overlays, lockscreen bypasses, and stealthy screen-streaming.

A critical flaw (CVE-2025-41702) in Welotec egOS allows unauthenticated attackers to impersonate administrators, gain full control, and disrupt industrial systems.

A new Google report reveals a Chinese APT group is hijacking captive portals and disguised plugins to deliver malware for espionage against diplomats in Southeast Asia.

A new report reveals a SpyNote Android RAT campaign using fake Google Play Store clones to steal data, with the malware abusing Accessibility Services for control.

A new ransomware strain called Cephalus is using compromised RDP, DLL sideloading, and abused security tools to bypass defenses and intimidate victims.

A new report from AhnLab reveals the Underground ransomware gang is back with a global campaign that uses sophisticated multi-layered encryption and customized malware.
Microsoft has now opened registration for the Extended Security Updates (ESU) program to Windows 10 Home users....

A new report reveals that a phishing attack on a Salesforce vendor has led to a data breach at Farmers Insurance, exposing the data of over 1.1 million customers.

The Cloud Software Group has released urgent updates for NetScaler ADC and Gateway to patch a zero-day (CVE-2025-7775) being actively exploited in the wild.