Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Android Malware Strikes: Fake Facebook & TikTok Apps Impersonate Brands for Traffic Monetization BadBox 2.0, Android Botnet Alien spyware - CVE-2024-43093
  • Malware

Android Malware Strikes: Fake Facebook & TikTok Apps Impersonate Brands for Traffic Monetization

Do Son July 22, 2025 0

Trustwave uncovers an Android malware cluster using fake Facebook & TikTok apps to lure victims via brand impersonation, abusing permissions for data collection and traffic monetization.
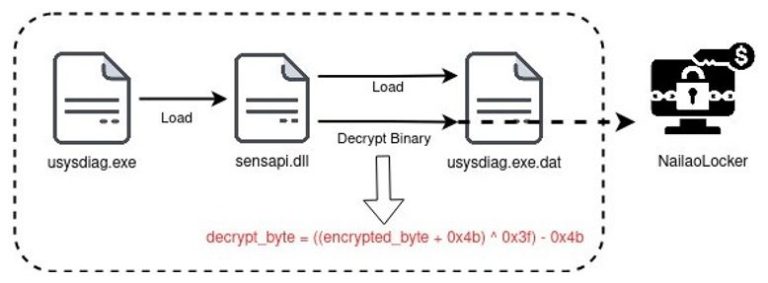
NailaoLocker Ransomware: Chinese SM2 Crypto and Built-in Decryptor Raise Questions NailaoLocker, SM2 Ransomware
  • Malware

NailaoLocker Ransomware: Chinese SM2 Crypto and Built-in Decryptor Raise Questions

Do Son July 22, 2025 0

FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

Important wolfSSL Update: Critical Apple Trust Store Bypass & Predictable Randomness Flaws Patched wolfSSL Vulnerabilities, TLS/SSL Security
  • Vulnerability Report

Important wolfSSL Update: Critical Apple Trust Store Bypass & Predictable Randomness Flaws Patched

Do Son July 22, 2025 0

wolfSSL 5.8.2 patches four vulnerabilities, including a critical Apple trust store bypass (CVE-2025-7395) and predictable randomness after fork(), impacting secure communications.

From MDifyLoader to Fscan: JPCERT Uncovers Deep Exploitation of Ivanti VPN Flaws in Advanced Malware Campaign Ivanti Exploitation, Multi-Malware Campaign
  • Vulnerability Report

From MDifyLoader to Fscan: JPCERT Uncovers Deep Exploitation of Ivanti VPN Flaws in Advanced Malware Campaign

Do Son July 22, 2025 0

JPCERT/CC details a sophisticated, ongoing malware campaign exploiting Ivanti Connect Secure (CVE-2025-0282, -22457) using MDifyLoader, Cobalt Strike, vshell, and Fscan for stealthy persistent access.

SVF Botnet: New Python DDoS Threat Leverages Discord for Stealthy C&C on Linux Servers Linux Botnet Discord C2
  • Malware

SVF Botnet: New Python DDoS Threat Leverages Discord for Stealthy C&C on Linux Servers

Do Son July 22, 2025 0

AhnLab uncovers SVF Bot, a Python-based DDoS botnet abusing Discord as its C&C channel to target misconfigured Linux servers and launch HTTP/UDP floods.

DeedRAT Backdoor: Chinese APT Targets Southeast Asian Governments via Vulnerable AV Software DeedRAT, Chinese Cyberattack
  • Malware

DeedRAT Backdoor: Chinese APT Targets Southeast Asian Governments via Vulnerable AV Software

Do Son July 22, 2025 0

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.

Ghost Crypt & PureRAT: New Stealthy Malware Targets Accounting Firm via “Process Hypnosis” Ghost Crypt, PureRAT
  • Malware

Ghost Crypt & PureRAT: New Stealthy Malware Targets Accounting Firm via “Process Hypnosis”

Do Son July 22, 2025 0

eSentire uncovered a sophisticated attack on a US accounting firm, deploying PureRAT via the new Ghost Crypt crypter and a stealthy "Process Hypnosis" injection technique.

Apache Jena Flaws (CVE-2025-49656 and CVE-2025-50151) Expose Semantic Web Apps to File System Compromise Apache Jena, File System Vulnerabilities
  • Vulnerability Report

Apache Jena Flaws (CVE-2025-49656 and CVE-2025-50151) Expose Semantic Web Apps to File System Compromise

Do Son July 22, 2025 0

Apache Jena versions up to 5.4.0 are vulnerable (CVE-2025-49656, -50151), allowing admin users to compromise the server file system and manipulate configurations.

APT41 Unleashes Full Arsenal in Rare African Cyberespionage Campaign Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cyber Security

APT41 Unleashes Full Arsenal in Rare African Cyberespionage Campaign

Do Son July 22, 2025 0

Kaspersky uncovers a sophisticated APT41 cyberespionage campaign targeting African government IT, showcasing the Chinese group's full TTPs, including Impacket and Cobalt Strike.

LARVA-208: New Web3 Phishing Campaign Leverages Fake AI Platforms & Job Lures to Steal Crypto jobs
  • Cybercriminals

LARVA-208: New Web3 Phishing Campaign Leverages Fake AI Platforms & Job Lures to Steal Crypto

Do Son July 22, 2025 0

LARVA-208 is targeting Web3 developers with fake AI platforms (like Norlax AI) and job lures to deploy Fickle Stealer malware, aiming to steal crypto and sensitive data.

Apple’s Foldable iPhone Coming 2026: “Not the First, But the Best” Strategy Aims for China Reboot Apple Spring Event 2026 Apple Intel 14A iPhone 2028, Intel Foundry Apple Silicon iPhone 18 glass cloth shortage, Nittobo T-glass Apple crisis Apple UK App Store lawsuit appeal, Apple tax £1.5bn damages Apple AI Leadership Shakeup Giannandrea Subramanya Touchscreen MacBook Pro Apple 2026 Roadmap Apple Smart Home, Desktop Robot Apple H3 Chip, AirPods Camera Apple chips, on-device AI Apple AI, retail chatbot MacBook, Affordable Foldable iPhone, Apple Strategy Apple COO, Leadership Transition DOJ Lawsuit Apple EU Policy, App Store Fees CVE-2024-23222 Apple French antitrust fine
  • Technology

Apple’s Foldable iPhone Coming 2026: “Not the First, But the Best” Strategy Aims for China Reboot

Do Son July 21, 2025 0

Mark Gurman reports Apple's first foldable iPhone is set for 2026, leveraging its "not the first, but the best" strategy to potentially boost growth in China.

Microsoft Extends Exchange Server 2016/2019 Support with Paid ESU Program (6-Month Lifeline) Exchange Server EOL, ESU Program Cumulative Update for Exchange Server 2019
  • Technology

Microsoft Extends Exchange Server 2016/2019 Support with Paid ESU Program (6-Month Lifeline)

Do Son July 21, 2025 0

Microsoft announces a paid 6-month ESU program for Exchange Server 2016/2019, offering critical security updates beyond October 2025 EOL to aid migrations.

Intel Discontinues Clear Linux: End of an Era for High-Performance OS Amid Cost Cuts Clear Linux EOL, Intel Open Source
  • Linux

Intel Discontinues Clear Linux: End of an Era for High-Performance OS Amid Cost Cuts

Do Son July 21, 2025 0

Intel has officially discontinued Clear Linux OS, its high-performance distribution. This move, part of broader cost-cutting, ends a decade of innovation and requires users to migrate immediately.

WhatsApp on Windows 11 Ditches Native UWP for WebView2: Performance Takes a Hit WhatsApp antitrust API probe India SIM-Binding Mandate Messaging App KYC WhatsApp DMA Interoperability BirdyChat Haiket Denmark Social Media Ban CVE-2025-55177 WhatsApp vulnerability, zero-click flaw npm Malware, System Wipe WhatsApp Windows App, WebView2 Downgrade WhatsApp Ban, US House NSO WhatsApp, Pegasus Spyware WhatsApp iPad iPadOS app
  • Technology

WhatsApp on Windows 11 Ditches Native UWP for WebView2: Performance Takes a Hit

Do Son July 21, 2025 0

WhatsApp's Windows 11 app beta has reverted from native UWP to a WebView2 web wrapper, leading to noticeable performance degradation and increased resource consumption.

Windows 11 Gets “Shared Audio”: Play Sound Through Multiple Devices Simultaneously Windows 11 Audio, Shared Audio
  • Windows

Windows 11 Gets “Shared Audio”: Play Sound Through Multiple Devices Simultaneously

Do Son July 21, 2025 0

Windows 11 is testing a new "shared audio" feature in Insider builds, allowing users to play sound through multiple connected audio output devices simultaneously.

Debian 13 “Trixie” Nears Release with Official RISC-V Architecture Support Year 2038 Problem, Debian Linux Debian 11.2 Debian 13, RISC-V Support
  • Linux

Debian 13 “Trixie” Nears Release with Official RISC-V Architecture Support

Do Son July 21, 2025 0

Debian 13 "Trixie" is entering full freeze on July 27 and launching August 9, marking the first official release with RISC-V architecture support.

New iPad Pro Rumored to Feature Dual Front Cameras & M5 Chip for Enhanced User Experience iPad Pro Camera, M5 Chip iPadOS 18 iPad Repair, Self-Service
  • Technology

New iPad Pro Rumored to Feature Dual Front Cameras & M5 Chip for Enhanced User Experience

Do Son July 21, 2025 0

New iPad Pro models are rumored to feature a dual front-facing camera setup for improved Face ID and video calls, alongside the powerful M5 chip, debuting later this year.

Windows 11 Adds OOBE Cloud Restore: Easier PC Setup, But Win32 Apps Still a Manual Chore Windows 11 Backup, PC Migration
  • Windows

Windows 11 Adds OOBE Cloud Restore: Easier PC Setup, But Win32 Apps Still a Manual Chore

Do Son July 21, 2025 0

Windows 11 is testing new OOBE features to restore data from the cloud to new PCs, but manual backup/migration for Win32 applications and their data remains a limitation.

Elon Musk Unveils “Baby Grok”: xAI’s New Child-Friendly AI App on the Horizon AI coding, grok-code-fast-1 xAI Grok 3 Grok 4, AI Model Baby Grok, xAI for Kids
  • Technology

Elon Musk Unveils “Baby Grok”: xAI’s New Child-Friendly AI App on the Horizon

Do Son July 21, 2025 0

Elon Musk announces "Baby Grok," a forthcoming xAI app dedicated to child-friendly AI content, aiming to offer safe, educational, and interactive experiences for children.

Three High-Severity Privilege Escalation Flaws Patched in Sophos Intercept X for Windows Sophos Intercept X, Privilege Escalation
  • Vulnerability Report

Three High-Severity Privilege Escalation Flaws Patched in Sophos Intercept X for Windows

Do Son July 21, 2025 0

Sophos has patched three high-severity LPE vulnerabilities in Intercept X for Windows (CVE-2024-13972, CVE-2025-7433, CVE-2025-7472), allowing local users to gain SYSTEM privileges.

Critical Livewire RCE (CVE-2025-54068) Threatens Millions of Laravel Apps – Patch Immediately! Livewire RCE, Laravel Vulnerability
  • Vulnerability Report

Critical Livewire RCE (CVE-2025-54068) Threatens Millions of Laravel Apps – Patch Immediately!

Do Son July 21, 2025 0

A critical RCE (CVE-2025-54068) in Livewire v3.6.3 and earlier allows unauthenticated attackers to execute arbitrary code on millions of Laravel applications. Update now!

Scanception: Global QR Code Phishing Campaign Bypasses Enterprise Security, Steals Credentials at Scale QR Code Phishing, Credential Harvesting
  • Cybercriminals

Scanception: Global QR Code Phishing Campaign Bypasses Enterprise Security, Steals Credentials at Scale

Do Son July 21, 2025 0

Scanception campaign uses QR code-based phishing in PDFs to bypass traditional security, targeting high-value industries globally for credential and 2FA theft.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.