
 Do Son
Apple revised EU App Store policies, allowing external purchases and new fees (initial acquisition, service, CTC) after a €500M fine. Developers can now direct users to outside payment channels.

MongoDB discloses CVE-2025-6710 (CVSS 7.5), a pre-authentication DoS flaw. Crafted JSON inputs can crash servers via stack overflow.

IBM warns of a critical RCE flaw (CVE-2025-36038) in WebSphere Application Server 8.5/9.0, allowing unauthenticated attackers to execute arbitrary code via serialization.

Following the 2024 CrowdStrike BSOD incident, Microsoft's Windows Resiliency Initiative is moving security drivers out of the kernel into user mode to boost system stability.

Let’s Encrypt is now testing IP-only digital certificates, offering a free alternative for securing IP addresses without domains, valid for six days with automated renewal.

Notorious hacker "IntelBroker" (Kai West) has been arrested, traced by the FBI through his crypto transactions. He's charged with stealing and selling data, causing $25M in damages.

Microsoft confirms any activated Windows 10 PC can receive ESU updates, regardless of Windows 11 hardware compatibility. Get one year of security updates via payment or free options.

HDMI 2.2 is finalized, doubling bandwidth to 96Gbps for 4K@240Hz, 8K@60Hz, and 16K@60Hz (via DSC). Requires Ultra96 cables, with devices expected Q4 2025.

PNG 3.0 is now a W3C Recommendation, introducing HDR imaging, native APNG, and EXIF metadata support, significantly enhancing the visual quality and functionality of web images.

The US Senate reintroduced the Open App Markets Act, aiming to curb Apple & Google's app store dominance by mandating sideloading, third-party payments, and preventing self-preferencing.

Google Cloud launches Gemini CLI, a free, open-source terminal tool bringing Gemini 2.5 Pro to developers for code generation, debugging, and file manipulation.
Amazon is investing $4B to expand same-day/next-day delivery to over 4,000 smaller US communities by 2026, leveraging AI and new hubs to boost e-commerce dominance.

Microsoft is replacing Windows' iconic Blue Screen of Death with a new black-and-white interface this summer, removing the QR code and emoticon for faster IT diagnosis.

A critical flaw (CVE-2025-3699) in Mitsubishi Electric AC systems allows remote authentication bypass, risking illegal control and firmware tampering.

Arctic Wolf Labs reveals UAC-0226 is using evolving GIFTEDCROOK malware in cyber-espionage against Ukrainian military and government, exfiltrating sensitive documents

China-aligned Hive0154 is using phishing lures themed around Tibetan issues to deploy the Pubload backdoor. Campaigns target the Tibetan community, US military
A critical flaw (CVE-2025-6561, CVSS 9.8) in Hunt Electronic DVRs allows unauthenticated remote attackers to access configuration files and obtain plaintext admin credentials.
A sophisticated campaign is exploiting AI tool popularity via Black Hat SEO to poison search results, delivering Vidar, Lumma, and Legion Stealers to unsuspecting users.

Iranian APT "Educated Manticore" (APT42) uses AI-assisted spear-phishing via email/WhatsApp to target critics with React-based phishing kits, bypassing MFA and stealing credentials.
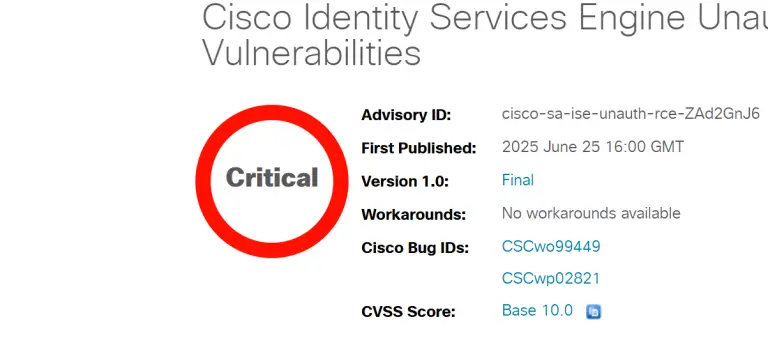
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
Citrix warns of a critical memory overflow flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway, actively exploited for DoS. Update to patched versions immediately!

Two critical flaws (CVE-2025-46415, CVE-2025-46416) in guix-daemon allow local attackers to gain root access via socket exploitation and race conditions.