Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Apple Overhauls EU App Store Policy: New Fees & Open External Purchases After €500M Fine Apple Spring Event 2026 Apple Intel 14A iPhone 2028, Intel Foundry Apple Silicon iPhone 18 glass cloth shortage, Nittobo T-glass Apple crisis Apple UK App Store lawsuit appeal, Apple tax £1.5bn damages Apple AI Leadership Shakeup Giannandrea Subramanya Touchscreen MacBook Pro Apple 2026 Roadmap Apple Smart Home, Desktop Robot Apple H3 Chip, AirPods Camera Apple chips, on-device AI Apple AI, retail chatbot MacBook, Affordable Foldable iPhone, Apple Strategy Apple COO, Leadership Transition DOJ Lawsuit Apple EU Policy, App Store Fees CVE-2024-23222 Apple French antitrust fine
  • Technology

Apple Overhauls EU App Store Policy: New Fees & Open External Purchases After €500M Fine

Do Son June 27, 2025 0

Apple revised EU App Store policies, allowing external purchases and new fees (initial acquisition, service, CTC) after a €500M fine. Developers can now direct users to outside payment channels.

MongoDB Hit by Pre-Auth Denial of Service Vulnerability MongoDB Server vulnerability use-after-free vulnerability, CVE-2026-11933, CVE-2026-9740, CVE-2026-9750 MongoDB DoS, Pre-Authentication Vulnerability CVE-2024-7553 - MongoDB Server CVE-2025-3083, CVE-2025-3084, and CVE-2025-3085
  • Vulnerability

MongoDB Hit by Pre-Auth Denial of Service Vulnerability

Do Son June 27, 2025 0

MongoDB discloses CVE-2025-6710 (CVSS 7.5), a pre-authentication DoS flaw. Crafted JSON inputs can crash servers via stack overflow.

CVE-2025-36038: Critical RCE Vulnerability Discovered in IBM WebSphere Application Server IBM WebSphere, Remote Code Execution
  • Vulnerability Report

CVE-2025-36038: Critical RCE Vulnerability Discovered in IBM WebSphere Application Server

Do Son June 27, 2025 0

IBM warns of a critical RCE flaw (CVE-2025-36038) in WebSphere Application Server 8.5/9.0, allowing unauthenticated attackers to execute arbitrary code via serialization.

Microsoft’s Major Shift: Moving Security Drivers Out of Windows Kernel to Prevent Future BSOD Disasters Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Microsoft’s Major Shift: Moving Security Drivers Out of Windows Kernel to Prevent Future BSOD Disasters

Do Son June 27, 2025 0

Following the 2024 CrowdStrike BSOD incident, Microsoft's Windows Resiliency Initiative is moving security drivers out of the kernel into user mode to boost system stability.

Good News! Let’s Encrypt Begins Testing IP-Only Certificates — No Domain Needed Merkle Tree Certificates Let's Encrypt 45-Day Certificates ACME Profile Updates 2026 Let’s Encrypt Generation Y, 45-Day TLS Certificates Let's Encrypt, IP Certificates Certificate Revocation Lists
  • Technology

Good News! Let’s Encrypt Begins Testing IP-Only Certificates — No Domain Needed

Do Son June 27, 2025 0

Let’s Encrypt is now testing IP-only digital certificates, offering a free alternative for securing IP addresses without domains, valid for six days with automated renewal.

Notorious Hacker “IntelBroker” (Kai West) Arrested: Exposed by Crypto Transactions, Caused $25M in Damages IntelBroker Arrest, Cybercriminal
  • Cybercriminals

Notorious Hacker “IntelBroker” (Kai West) Arrested: Exposed by Crypto Transactions, Caused $25M in Damages

Do Son June 27, 2025 0

Notorious hacker "IntelBroker" (Kai West) has been arrested, traced by the FBI through his crypto transactions. He's charged with stealing and selling data, causing $25M in damages.

Windows 10 ESU: Any Activated PC Can Get Extended Security Updates, No Windows 11 Hardware Needed Windows VSM shutdown bug Windows 10 ESU, EEA Free Update Windows 10 ESU, Hardware Eligibility
  • Windows

Windows 10 ESU: Any Activated PC Can Get Extended Security Updates, No Windows 11 Hardware Needed

Do Son June 27, 2025 0

Microsoft confirms any activated Windows 10 PC can receive ESU updates, regardless of Windows 11 hardware compatibility. Get one year of security updates via payment or free options.

HDMI 2.2 Officially Finalized: Doubles Bandwidth to 96Gbps for Next-Gen 4K/240Hz, 8K/60Hz, and 16K HDMI 2.2, Bandwidth Doubling
  • Technology

HDMI 2.2 Officially Finalized: Doubles Bandwidth to 96Gbps for Next-Gen 4K/240Hz, 8K/60Hz, and 16K

Do Son June 27, 2025 0

HDMI 2.2 is finalized, doubling bandwidth to 96Gbps for 4K@240Hz, 8K@60Hz, and 16K@60Hz (via DSC). Requires Ultra96 cables, with devices expected Q4 2025.

PNG 3.0 Becomes W3C Standard: Brings HDR, Native APNG & EXIF Support to the Web PNG 3.0, Web Standard
  • Technology

PNG 3.0 Becomes W3C Standard: Brings HDR, Native APNG & EXIF Support to the Web

Do Son June 27, 2025 0

PNG 3.0 is now a W3C Recommendation, introducing HDR imaging, native APNG, and EXIF metadata support, significantly enhancing the visual quality and functionality of web images.

US Senate Reintroduces Open App Markets Act: Aims to Break Apple & Google’s App Store Monopoly Open App Markets Act, App Store Regulation
  • Technology

US Senate Reintroduces Open App Markets Act: Aims to Break Apple & Google’s App Store Monopoly

Do Son June 27, 2025 0

The US Senate reintroduced the Open App Markets Act, aiming to curb Apple & Google's app store dominance by mandating sideloading, third-party payments, and preventing self-preferencing.

Google Cloud Unveils Gemini CLI: Free AI Assistant Brings Gemini 2.5 Pro to Your Terminal Google Gemini CLI, AI Command Line
  • Technology

Google Cloud Unveils Gemini CLI: Free AI Assistant Brings Gemini 2.5 Pro to Your Terminal

Do Son June 27, 2025 0

Google Cloud launches Gemini CLI, a free, open-source terminal tool bringing Gemini 2.5 Pro to developers for code generation, debugging, and file manipulation.
Amazon Expands Same-Day Delivery: 4,000 New US Cities & Towns by 2026 Amazon Delivery, E-commerce Expansion
  • Technology

Amazon Expands Same-Day Delivery: 4,000 New US Cities & Towns by 2026

Do Son June 27, 2025 0

Amazon is investing $4B to expand same-day/next-day delivery to over 4,000 smaller US communities by 2026, leveraging AI and new hubs to boost e-commerce dominance.

Windows 11 Retires Blue Screen of Death: New Black Crash Screen Focuses on Faster Diagnostics Windows Public Display Crash BSOD Hiding Windows 11 BSOD, Black Screen of Death
  • Windows

Windows 11 Retires Blue Screen of Death: New Black Crash Screen Focuses on Faster Diagnostics

Do Son June 27, 2025 0

Microsoft is replacing Windows' iconic Blue Screen of Death with a new black-and-white interface this summer, removing the QR code and emoticon for faster IT diagnosis.

Mitsubishi Electric Air Conditioning Systems Vulnerable to Remote Authentication Bypass (CVSS 9.8) Mitsubishi Electric, Critical Vulnerability
  • Vulnerability Report

Mitsubishi Electric Air Conditioning Systems Vulnerable to Remote Authentication Bypass (CVSS 9.8)

Do Son June 27, 2025 0

A critical flaw (CVE-2025-3699) in Mitsubishi Electric AC systems allows remote authentication bypass, risking illegal control and firmware tampering.

GIFTEDCROOK Evolves: Arctic Wolf Labs Exposes Threat Group UAC-0226’s Espionage on Ukraine tg
  • Cybercriminals

GIFTEDCROOK Evolves: Arctic Wolf Labs Exposes Threat Group UAC-0226’s Espionage on Ukraine

Do Son June 27, 2025 0

Arctic Wolf Labs reveals UAC-0226 is using evolving GIFTEDCROOK malware in cyber-espionage against Ukrainian military and government, exfiltrating sensitive documents

China-Aligned Hive0154 APT Strikes Tibetan Community: Pubload Backdoor Delivered via Phishing Lures Artivion cybersecurity - Zero-Day Attacks
  • Cyber Security

China-Aligned Hive0154 APT Strikes Tibetan Community: Pubload Backdoor Delivered via Phishing Lures

Do Son June 27, 2025 0

China-aligned Hive0154 is using phishing lures themed around Tibetan issues to deploy the Pubload backdoor. Campaigns target the Tibetan community, US military
CVE-2025-6561 (CVSS 9.8): Hunt Electronic DVR Vulnerability Exposes Admin Credentials in Plaintext F5 BIG-IP Hunt Electronic DVR, Critical Vulnerability
  • Vulnerability Report

CVE-2025-6561 (CVSS 9.8): Hunt Electronic DVR Vulnerability Exposes Admin Credentials in Plaintext

Do Son June 27, 2025 0

A critical flaw (CVE-2025-6561, CVSS 9.8) in Hunt Electronic DVRs allows unauthenticated remote attackers to access configuration files and obtain plaintext admin credentials.
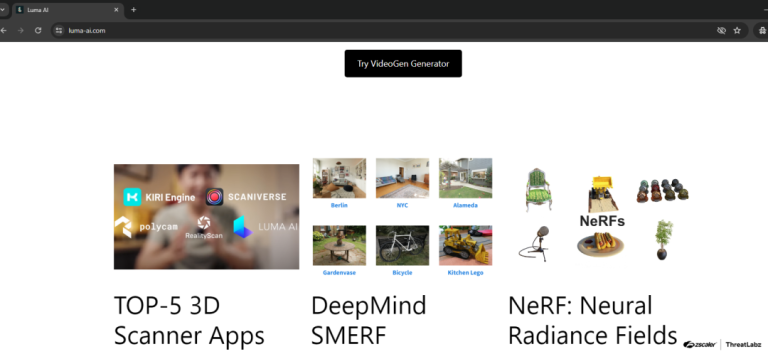
AI Hype Exploited: Black Hat SEO Campaign Poisons Search Results to Deliver Vidar, Lumma & Legion Stealers Example AI-themed website designed to lure victims into installing malware
  • Cybercriminals

AI Hype Exploited: Black Hat SEO Campaign Poisons Search Results to Deliver Vidar, Lumma & Legion Stealers

Do Son June 27, 2025 0

A sophisticated campaign is exploiting AI tool popularity via Black Hat SEO to poison search results, delivering Vidar, Lumma, and Legion Stealers to unsuspecting users.

Iranian APT “Educated Manticore” Unleashes AI-Powered Phishing & Keylogging Against Critics g-pass
  • Cybercriminals

Iranian APT “Educated Manticore” Unleashes AI-Powered Phishing & Keylogging Against Critics

Do Son June 27, 2025 0

Iranian APT "Educated Manticore" (APT42) uses AI-assisted spear-phishing via email/WhatsApp to target critics with React-based phishing kits, bypassing MFA and stealing credentials.
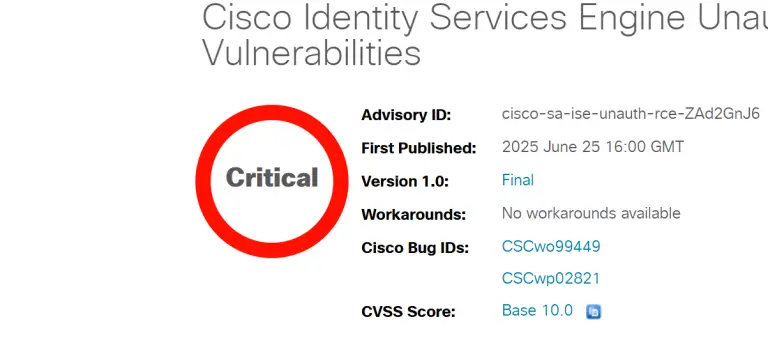
Cisco ISE/ISE-PIC Alert: Two Critical RCE Flaws (CVSS 10.0) Allow Unauthenticated Root Access Cisco ISE, Critical RCE
  • Vulnerability Report

Cisco ISE/ISE-PIC Alert: Two Critical RCE Flaws (CVSS 10.0) Allow Unauthenticated Root Access

Do Son June 27, 2025 0

Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
Urgent Citrix NetScaler Alert: Critical Memory Overflow Flaw (CVE-2025-6543, CVSS 9.2) Actively Exploited Citrix NetScaler, Critical Vulnerability
  • Vulnerability Report

Urgent Citrix NetScaler Alert: Critical Memory Overflow Flaw (CVE-2025-6543, CVSS 9.2) Actively Exploited

Do Son June 27, 2025 0

Citrix warns of a critical memory overflow flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway, actively exploited for DoS. Update to patched versions immediately!

Privilege Escalation in guix-daemon: Critical Vulnerabilities Threaten Multi-User Systems Guix Daemon, Privilege Escalation
  • Vulnerability

Privilege Escalation in guix-daemon: Critical Vulnerabilities Threaten Multi-User Systems

Do Son June 26, 2025 0

Two critical flaws (CVE-2025-46415, CVE-2025-46416) in guix-daemon allow local attackers to gain root access via socket exploitation and race conditions.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.