Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
From Bypass to Root: Mandiant Red Team Exploits CVE-2025-2171 and CVE-2025-2172 in Aviatrix Cloud Controller bypass
  • Vulnerability Report

From Bypass to Root: Mandiant Red Team Exploits CVE-2025-2171 and CVE-2025-2172 in Aviatrix Cloud Controller

Do Son June 24, 2025 0

Mandiant Red Team breached Aviatrix Controller via auth bypass & RCE flaws CVE-2025-2171/2172—reached root, gained AWS keys. Full chain, no guesswork.

No Patch, Full Exploit: CVSS 9.9 RCE & IDOR Flaws in InnoShop eCommerce Platform InnoShop vulnerabilities
  • Vulnerability Report

No Patch, Full Exploit: CVSS 9.9 RCE & IDOR Flaws in InnoShop eCommerce Platform

Do Son June 24, 2025 0

Critical CVSS 9.9 RCE, IDOR, and path traversal flaws in InnoShop with full PoC exploit. No patch available—eCommerce sites at serious risk.

EvilConwi: Hackers Abuse Signed ConnectWise Installers to Launch Stealth Remote Access Attacks abuse
  • Cybercriminals

EvilConwi: Hackers Abuse Signed ConnectWise Installers to Launch Stealth Remote Access Attacks

Do Son June 24, 2025 0

Hackers are weaponizing legitimately signed ConnectWise ScreenConnect installers by using Authenticode stuffing to deploy malware and fake updates, leveraging social engineering.

SHOE RACK Malware: NCSC Uncovers Stealthy Reverse SSH & DoH Post-Exploitation Tool Targeting FortiGate Firewalls SHOE RACK Malware, Reverse SSH
  • Malware

SHOE RACK Malware: NCSC Uncovers Stealthy Reverse SSH & DoH Post-Exploitation Tool Targeting FortiGate Firewalls

Do Son June 24, 2025 0

NCSC reveals SHOE RACK, a stealthy post-exploitation malware using reverse SSH tunneling, DoH, and protocol abuse to maintain remote access on FortiGate 100D firewalls.

Cyber Fattah Breach: Pro-Iranian Hackers Leak Saudi Games Athlete Data in Targeted Info Op Saudi Games, Cyber Fattah
  • Data Leak

Cyber Fattah Breach: Pro-Iranian Hackers Leak Saudi Games Athlete Data in Targeted Info Op

Do Son June 24, 2025 0

Pro-Iranian group Cyber Fattah leaked thousands of sensitive Saudi Games participant records, including PII and bank data, in a political information operation targeting Saudi Arabia.

Spyware Reloaded: SparkKitty Stalks Crypto Wallets via TikTok Mods and Fake Apps Mobile Spyware, SparkKitty
  • Malware

Spyware Reloaded: SparkKitty Stalks Crypto Wallets via TikTok Mods and Fake Apps

Do Son June 24, 2025 0

Kaspersky uncovers SparkKitty mobile spyware, which infiltrates Android/iOS via TikTok mods and crypto apps, using image recognition to steal sensitive photos like crypto seed phrases.
North Korean Hackers Exploit GitHub and Dropbox in Targeted Spearphishing Attacks CVE-2024-3393 - Zservers sanctions
  • Cybercriminals

North Korean Hackers Exploit GitHub and Dropbox in Targeted Spearphishing Attacks

Do Son June 24, 2025 0

North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.

Wedding Invitation Scam: SpyMax RAT Targets Indian WhatsApp Users, Stealing OTPs & Banking Credentials Android Spyware, SpyMax RAT CVE-2024-0039 Android Auto-Reboot Google Play Services
  • Malware

Wedding Invitation Scam: SpyMax RAT Targets Indian WhatsApp Users, Stealing OTPs & Banking Credentials

Do Son June 24, 2025 0

A new Android spyware campaign uses a "Wedding Invitation" APK via WhatsApp to install SpyMax RAT, stealing OTPs, contacts, and banking credentials from Indian users.

Speaker Proposal Deadline Approaches for OpenSSL Conference 2025 in Prague PR_Speakers_Conf_02_1750689274PuXbB6t4ud
  • Press Release

Speaker Proposal Deadline Approaches for OpenSSL Conference 2025 in Prague

cybernewswire June 23, 2025 0
Newark, United States, 23rd June 2025, CyberNewsWire
Read More Read more about Speaker Proposal Deadline Approaches for OpenSSL Conference 2025 in Prague
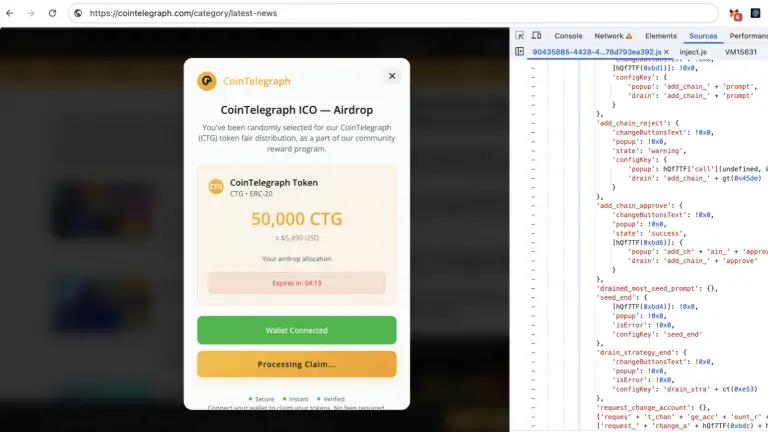
CoinTelegraph Hacked: Fake CTG Airdrop Scam Steals Crypto Via Malicious Pop-Ups CoinTelegraph Hack, Crypto Scam
  • Cybercriminals

CoinTelegraph Hacked: Fake CTG Airdrop Scam Steals Crypto Via Malicious Pop-Ups

Do Son June 23, 2025 0

CoinTelegraph was hacked on June 22, 2025, with attackers injecting malicious JavaScript to display fake CTG airdrop pop-ups, stealing crypto by draining connected wallets.

CoinMarketCap Hacked: “Doodle” Graphic Delivers Malware, Stealing $43K+ from User Wallets CoinMarketCap Hack, Inferno Drainer CVE-2024-53677 PoC Exploit
  • Cybercriminals

CoinMarketCap Hacked: “Doodle” Graphic Delivers Malware, Stealing $43K+ from User Wallets

Do Son June 23, 2025 0

CoinMarketCap suffered a client-side attack on June 20, 2025, using a fake "doodle" graphic to deliver Inferno Drainer, stealing over $43,000 from user wallets.

YouTube’s New Anti-Ad Blocker Tactic: “Fake Buffering” Delays Videos by 10+ Seconds YouTube deepfake YouTube AI YouTube Premium YouTube Ad Blockers, Fake Buffering Google Lens, YouTube Shorts
  • Technology

YouTube’s New Anti-Ad Blocker Tactic: “Fake Buffering” Delays Videos by 10+ Seconds

Do Son June 23, 2025 0

YouTube is experimenting with "fake buffering" via A/B testing, intentionally delaying video loading by ~10 seconds for ad-blocking users to encourage Premium subscriptions.

Microsoft Tightens Windows Restore: 60-Day Limit for Windows 11 24H2 Restore Points Windows Restore, Microsoft Policy
  • Windows

Microsoft Tightens Windows Restore: 60-Day Limit for Windows 11 24H2 Restore Points

Do Son June 23, 2025 0

Microsoft shortens Windows 11 24H2 System Restore point retention to 60 days, purging older points. This follows a previous reduction in Windows 10's rollback window.

CapCut’s New Terms: ByteDance Gains Perpetual Rights to User Content, Likeness, & Voice Globally CapCut Terms, Data Rights
  • Technology

CapCut’s New Terms: ByteDance Gains Perpetual Rights to User Content, Likeness, & Voice Globally

Do Son June 23, 2025 0

CapCut's updated TOS (June 12, 2025) grants ByteDance a perpetual, worldwide license to use user content, including likeness and voice, for any purpose without compensation or approval.
iOS 26 Unveils “Captive Assist”: Seamless Public Wi-Fi Login Across All Your Apple Devices AirDrop PIN Pairing 30-Day AirDrop Trust iOS 26 downgrade iOS 26 battery drain 5G MacBook, Cellular Mac iOS 26, Communication Safety iOS 26, Wi-Fi Synchronization iOS 26, Wi-Fi Synchronization Apple Redesign Apple Public Betas, AirPods Firmware
  • Technology

iOS 26 Unveils “Captive Assist”: Seamless Public Wi-Fi Login Across All Your Apple Devices

Do Son June 23, 2025 0

iOS 26 is testing "Captive Assist," a new feature to synchronize public Wi-Fi logins across all your Apple devices, streamlining access to captive networks.

Apple Eyes Perplexity AI Acquisition: Bolstering Search & Siri with Generative AI Mac Pro discontinued 2026 iOS 27 Snow Leopard update iOS 27 Maintenance Apple Stability Focus M5 MacBook, Studio Display macOS update, Mac Studio M3 Ultra Perplexity Apple, Perplexity AI Acquisition Mac Mini M2, Power Issue macOS, Intel Macs
  • Technology

Apple Eyes Perplexity AI Acquisition: Bolstering Search & Siri with Generative AI

Do Son June 23, 2025 0

Apple is reportedly in talks to acquire Perplexity AI, aiming to accelerate its AI search engine development and integrate generative AI into the next generation of Siri.

Cloudflare Mitigates Record 7.3 Tbps DDoS Attack: 37.4 TB in 45 Seconds Cloudflare DDoS, Record Attack
  • Cybercriminals

Cloudflare Mitigates Record 7.3 Tbps DDoS Attack: 37.4 TB in 45 Seconds

Do Son June 23, 2025 0

Cloudflare successfully mitigated a record-breaking 7.3 Tbps DDoS attack in May 2025, delivering 37.4 TB in 45 seconds with no service disruption.

Microsoft Family Safety Blocks Google Chrome in Windows 11: Workarounds Revealed Chrome 148 lazy loading Chrome for Linux ARM64 Chrome 145 Update Chrome Security Fixes Chrome Security Update CVE-2026-1220 Chrome 144 Security Update CVE-2026-0899 Chrome Memory Safety, WebGPU UAF Chrome V8 Type Confusion, Google Updater Flaw Chrome V8 Flaw, CVE-2025-13042 Chrome V8, Type Confusion, Chrome 142 Update Chrome V8 Flaw, CVE-2025-12036 Chrome 141, WebGPU Overflow Google Chrome preloading Chrome, V8 vulnerability CVE-2025-9132 Chrome Security Update, Use-After-Free Chrome V8, Type Confusion Chrome Telemetry, Windows 10 EOL Microsoft Family Safety, Chrome Blocking Chrome Security Update, High-Severity Google Chrome, Antitrust CVE-2024-10487 and CVE-2024-10488 Google Chrome Root Program Chrome Update, CVE-2025-3619 Chrome Acquisition, Perplexity.ai
  • Technology

Microsoft Family Safety Blocks Google Chrome in Windows 11: Workarounds Revealed

Do Son June 23, 2025 0

Microsoft Family Safety is automatically blocking Google Chrome (v137.0.7151.68/69) in Windows 11. Learn why and how to manually unblock the browser.

Windows Update’s Driver Purge: Smoother Updates, or Hidden Headaches? Driver Cleanup CVE-2024-49138 - December Patch Tuesday Windows update errors, Windows update troubleshooting
  • Windows

Windows Update’s Driver Purge: Smoother Updates, or Hidden Headaches?

Do Son June 23, 2025 0

Microsoft is purging old drivers from Windows Update, offering a cleaner experience. But will this new OEM-focused policy lead to unexpected compatibility issues?

Critical Python Tarfile Flaw (CVE-2025-4517, CVSS 9.4): Arbitrary File Write, PoC Available Python Tarfile, Path Traversal
  • Vulnerability

Critical Python Tarfile Flaw (CVE-2025-4517, CVSS 9.4): Arbitrary File Write, PoC Available

Do Son June 23, 2025 0

A critical flaw (CVE-2025-4517, CVSS 9.4) in Python's tarfile module allows arbitrary file reads/writes outside the extraction directory. PoC is public; update immediately

Confucius Group Evolves: Researcher Uncovers New Modular Backdoor “Anondoor” in Latest Espionage Campaign Confucius APT, Anondoor Backdoor
  • Malware

Confucius Group Evolves: Researcher Uncovers New Modular Backdoor “Anondoor” in Latest Espionage Campaign

Do Son June 23, 2025 0

Confucius APT has a new modular backdoor, "Anondoor," delivering espionage payloads and evading sandboxes in targeted attacks on South and East Asian governments.

Prometei Botnet Evolves: Linux Variant Returns With Stealthier Payloads and Monero Mining Focus Prometei Botnet, Linux Malware
  • Malware

Prometei Botnet Evolves: Linux Variant Returns With Stealthier Payloads and Monero Mining Focus

Do Son June 23, 2025 0

The Prometei botnet is back with a stealthy Linux variant, actively mining Monero and stealing credentials. It uses DGA, custom UPX packing, and sophisticated anti-analysis techniques.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.