Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
ChatGPT Supercharged: New Enterprise Features for Business Productivity! AI Empire, Sam Altman OpenAI Government, AI Procurement ChatGPT Usage, AI Growth ChatGPT Enterprise, AI Business Tools ChatGPT Free ChatGPT Memory AI Personalization
  • Technology

ChatGPT Supercharged: New Enterprise Features for Business Productivity!

Do Son June 5, 2025 0

ChatGPT Enterprise gains powerful new features: cloud integrations (OneDrive, Google Drive), meeting transcription, Deep Research connectors & MCP for advanced analysis.

OpenAI vs. Court Order: The Battle to Protect Your ChatGPT Privacy ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

OpenAI vs. Court Order: The Battle to Protect Your ChatGPT Privacy

Do Son June 5, 2025 0

OpenAI is fighting a court order to retain all ChatGPT user logs, including deleted conversations, due to copyright infringement claims. This could impact global user privacy.
Amazon’s $10 Billion AI Boost: North Carolina Lands Major Tech Expansion! AWS Middle East drone strikes AWS Frontier Agents Autonomous Software Engineering AWS AI Factories Data Sovereignty AI Agentic AI Nova Sonic AWS Google Cloud Interconnect AWS Free Tier, Cloud Credits Freevee, ad-supported streaming Amazon AI, North Carolina Investment CVE-2022-2385
  • Technology

Amazon’s $10 Billion AI Boost: North Carolina Lands Major Tech Expansion!

Do Son June 5, 2025 0

Amazon is investing $10B in North Carolina for AI infrastructure, creating 500+ high-skilled jobs and boosting the local economy and STEM education.

Microsoft 365 Update Channels – Major Changes Ahead for IT Admins! student discount Microsoft 365, Intelligent Services Microsoft 365 UWP, App Deprecation Microsoft 365, Startup Boost Windows 10 EOL, Microsoft 365 Support Protocol Deprecation Microsoft 365 Updates, IT Admin Alert Microsoft 365 VPN shut down Microsoft Authenticator, password manager Windows 10 Microsoft 365 Microsoft nonprofit policy, software donations
  • Technology

Microsoft 365 Update Channels – Major Changes Ahead for IT Admins!

Do Son June 5, 2025 0

Microsoft 365 update channels are changing! Semi-Annual Enterprise Channel support is reduced, and Preview is deprecated. IT admins must review & adjust immediately for smooth deployment.

CVE-2025-49113: Roundcube RCE Exploit Unveiled—The Swiss Army Knife of Webmail Just Got a Weaponized Blade Roundcube Vulnerability CVE-2025-49113 exploit
  • Vulnerability Report

CVE-2025-49113: Roundcube RCE Exploit Unveiled—The Swiss Army Knife of Webmail Just Got a Weaponized Blade

Do Son June 5, 2025 0

A critical RCE flaw (CVE-2025-49113) in Roundcube is under active exploitation with PoC sold on forums. Patch immediately to v1.5.10 or v1.6.11!

Cisco Patches Two Vulnerabilities in CCP and ISE: Proof-of-Concept Exploits Publicly Available Cisco Vulnerabilities, PoC Exploit
  • Vulnerability Report

Cisco Patches Two Vulnerabilities in CCP and ISE: Proof-of-Concept Exploits Publicly Available

Do Son June 5, 2025 0

Cisco addresses CVE-2025-20129 and CVE-2025-20130 in CCP and ISE platforms. PoC exploits are public. Admins urged to migrate to fixed versions.

12.2TB of User Data Exposed in Passion.io Breach: Over 3.6 Million Records Left Unprotected Data Breach, Passion.io
  • Data Leak

12.2TB of User Data Exposed in Passion.io Breach: Over 3.6 Million Records Left Unprotected

Do Son June 5, 2025 0

12TB of unencrypted user data, including PII and financial records, allegedly from Passion.io, was exposed online. A critical security reminder for all!

Critical Dell Bug (CVSS 9.8) Lets Unauthenticated Attackers Fully Compromise the System Dell AI PC marketing pivot, XPS 2026 brand revival, NPU, Tech Industry News CVE-2023-32484 PowerScale OneFS, CVE-2024-53298
  • Vulnerability

Critical Dell Bug (CVSS 9.8) Lets Unauthenticated Attackers Fully Compromise the System

Do Son June 5, 2025 0

Unauthenticated attackers can fully compromise Dell PowerScale OneFS. Patch now to stop critical NFS access flaws.

CVE-2025-48951: Critical Deserialization Flaw in Auth0 PHP SDK Threatens Millions of Applications Auth0 PHP SDK, Critical Vulnerability
  • Vulnerability Report

CVE-2025-48951: Critical Deserialization Flaw in Auth0 PHP SDK Threatens Millions of Applications

Do Son June 5, 2025 0

A critical Auth0 PHP SDK deserialization flaw (CVE-2025-48951, CVSS 9.3) allows unauthenticated RCE in web apps. Patch to v8.14.0+ immediately!

Cisco Warns of High-Severity SSH Security Flaws in UCS IMC and NDFC Systems Cisco Vulnerabilities, Privilege Escalation
  • Vulnerability Report

Cisco Warns of High-Severity SSH Security Flaws in UCS IMC and NDFC Systems

Do Son June 5, 2025 0

Cisco issues advisories for high-severity flaws (CVSS 8.8, 8.7) in IMC and NDFC, risking privilege escalation and device impersonation. Patch immediately!

Sophos Unmasks Sakura RAT: Hackers Hacking Hackers with Backdoored Malware! Sakura RAT, Hacker Malware
  • Cybercriminals

Sophos Unmasks Sakura RAT: Hackers Hacking Hackers with Backdoored Malware!

Do Son June 5, 2025 0

Sophos X-Ops found a backdoored Sakura RAT targeting hackers and cheaters, spreading info-stealers via hidden scripts in open-source projects.
Alert: Fake DocuSign & Gitcodes Pages Install NetSupport RAT Malware! NetSupport RAT, Phishing Campaign
  • Malware

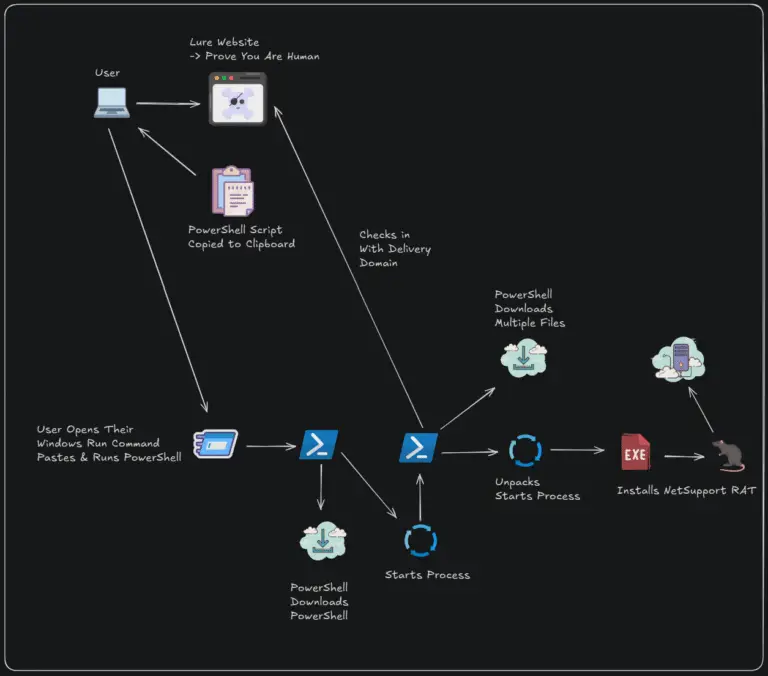
Alert: Fake DocuSign & Gitcodes Pages Install NetSupport RAT Malware!

Do Son June 5, 2025 0

A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

CVE-2025-48947: Session Cookies at Risk in Auth0 Next.js SDK Auth0, Next.js SDK
  • Vulnerability Report

CVE-2025-48947: Session Cookies at Risk in Auth0 Next.js SDK

Do Son June 5, 2025 0

Auth0 Next.js SDK flaw (CVE-2025-48947, CVSS 7.7) could expose session cookies via CDNs. Patch to v4.6.1 immediately to secure your app!

IBM X-Force Uncovers Hive0131’s Sophisticated DCRat Campaign Targeting Colombian Users ph
  • Cybercriminals

IBM X-Force Uncovers Hive0131’s Sophisticated DCRat Campaign Targeting Colombian Users

Do Son June 5, 2025 0

IBM X-Force warns of a new phishing campaign by Hive0131 targeting Colombian users with DCRat malware via fake legal notices.

Kaspersky Exposes Hidden Dangers: Are Your Containers Truly Secure? Container Security
  • Vulnerability Report

Kaspersky Exposes Hidden Dangers: Are Your Containers Truly Secure?

Do Son June 5, 2025 0

Kaspersky warns organizations are overestimating container isolation. New analysis reveals hidden attack surfaces and crucial detection blind spots.

ViperSoftX Evolves: New PowerShell Malware Boasts Stealth & Persistence PowerShell Malware, ViperSoftX
  • Malware

ViperSoftX Evolves: New PowerShell Malware Boasts Stealth & Persistence

Do Son June 5, 2025 0

K7 Labs details an evolved PowerShell malware, ViperSoftX 2025, featuring enhanced modularity, stealth, and persistence for advanced attacks.
Critical Cisco ISE Cloud Vulnerability (CVSS 9.9) with PoC Exploit Threatens AWS, Azure, OCI Cisco ISE, CVE-2025-20286
  • Vulnerability Report

Critical Cisco ISE Cloud Vulnerability (CVSS 9.9) with PoC Exploit Threatens AWS, Azure, OCI

Do Son June 5, 2025 0

CVSS 9.9 flaw in Cisco ISE cloud deployments with public PoC exploit enables remote attacks on AWS, Azure, and OCI. Patch now.

Critical ABB EIBPORT Flaw: Update Now to Prevent Building Automation Hijacks! ABB Security, EIBPORT Vulnerability
  • Vulnerability Report

Critical ABB EIBPORT Flaw: Update Now to Prevent Building Automation Hijacks!

Do Son June 5, 2025 0

ABB warns of a critical session fixation vulnerability (CVE-2024-13967) in EIBPORT V3, allowing unauthorized access. Update to firmware 3.9.9 immediately.

Multiple Stored XSS Vulnerabilities Discovered in VMware NSX — Patch Now VMware NSX, XSS Vulnerabilities
  • Vulnerability Report

Multiple Stored XSS Vulnerabilities Discovered in VMware NSX — Patch Now

Do Son June 4, 2025 0

Broadcom releases critical patches for three Stored XSS vulnerabilities (CVE-2025-22243, CVE-22244, CVE-22245) in VMware NSX, Cloud Foundation & Telco Cloud. Update immediately!

Making $9,756 a day? Teach you how to use Robinhood to start your RIMining crypto cloud mining journey Exploit Jupyter Notebooks
  • Technique

Making $9,756 a day? Teach you how to use Robinhood to start your RIMining crypto cloud mining journey

Do Son June 4, 2025 0
In May 2025, US President Trump announced that he would raise $2.5 billion to establish a national...
Read More Read more about Making $9,756 a day? Teach you how to use Robinhood to start your RIMining crypto cloud mining journey
Coinbase Data Breach: 69,000 Customers’ Info Leaked Via Third-Party Coinbase Breach, Data Leak
  • Data Leak

Coinbase Data Breach: 69,000 Customers’ Info Leaked Via Third-Party

Do Son June 4, 2025 0

Coinbase suffered a data breach impacting 69,000 customers, linked to a third-party contractor. Personal info was leaked, raising security concerns.

Samsung Joins Google: Inactive Accounts & Data to Be Deleted! Samsung zero-day Samsung Galaxy S25 Edge, Sales Performance Samsung Account, Inactive Accounts One UI 7 Samsung Update
  • Technology

Samsung Joins Google: Inactive Accounts & Data to Be Deleted!

Do Son June 4, 2025 0

Samsung will delete inactive accounts and all associated data after 24 months, starting July 31, 2025. Log in to avoid loss!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.