 Do Son
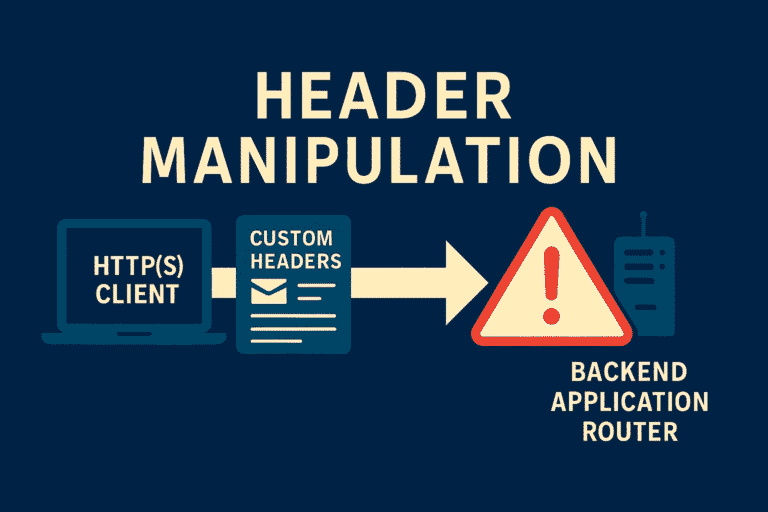
A critical flaw in Fabio load balancer allows malicious clients to manipulate or strip HTTP headers, leading to potential access control bypass. Upgrade to 1.6.6.

Over 50,000 Microsoft Azure AD user records from the aviation industry were exposed due to a misconfigured, unauthenticated API, revealing sensitive data and posing major risks.
CISA warns of critical flaws (CVE-2025-41438, CVE-2025-46352) in Consilium Safety CS5000 Fire Panels, allowing remote access & disruption. Vendor won't patch.

Veritas DLO has critical vulnerabilities (CVE-2024-38475, CVE-2025-24813) in bundled Apache components, leading to RCE. Upgrade immediately to prevent exploitation.

Rapid7 found critical RCE flaws in MICI NetFax (versions < 3.0.1.0) via default credentials & command injection. Vendor refuses to patch, advising no internet exposure.

A sophisticated PyPI supply chain attack, "cappership," steals Solana private keys by monkey-patching, leveraging transitive dependencies and blockchain exfiltration.
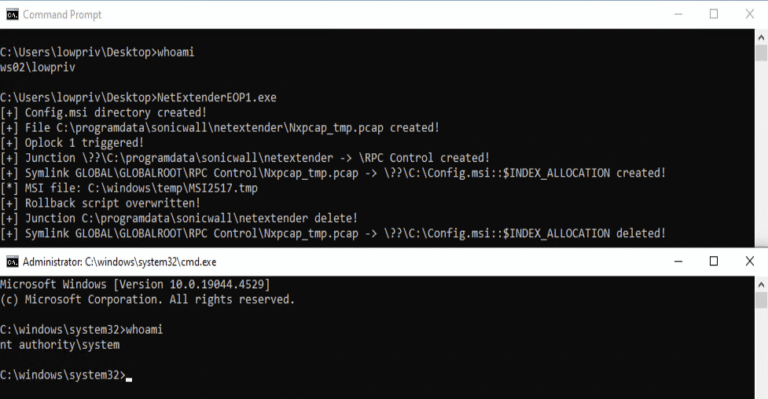
High-risk LPE vulnerabilities in SonicWall NetExtender for Windows (CVE-2025-23009, CVE-2025-23010) allow SYSTEM access or DoS. Patch immediately to version 10.3.2.

A study reveals widespread path traversal (CWE-22) in open-source projects, exacerbated by LLMs generating insecure code. Automated detection and patching are critical.

Darktrace uncovers PumaBot, a stealthy Linux botnet using Go binaries, SSH brute-force, and rootkits to compromise IoT devices, aiming for persistent, undetected access.

Hitachi Energy's Asset Suite, used in power gen, faces severe vulnerabilities including XSS, plaintext passwords, & RCE. Immediate action advised to secure systems.
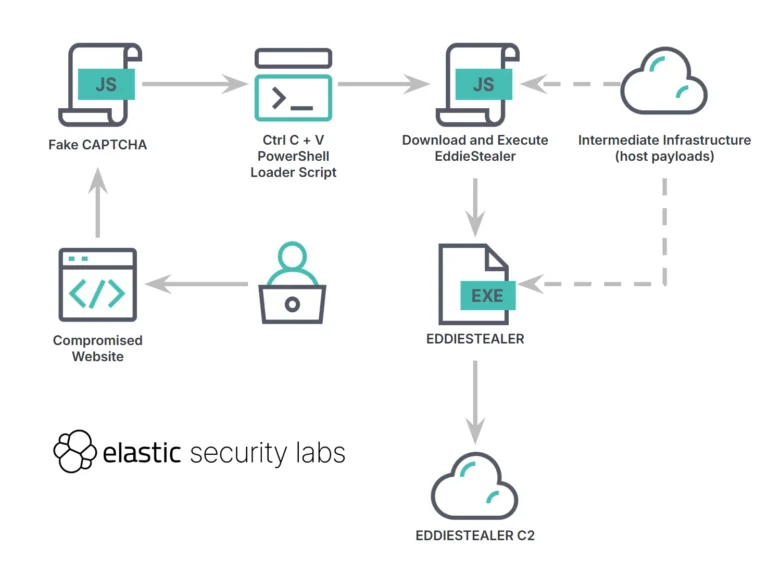
EDDIESTEALER, a new Rust-based infostealer, targets Windows systems via fake CAPTCHAs, stealing crypto wallets, browser data, and credentials with advanced stealth.

AyySSHush is a new stealthy botnet backdooring ASUS routers via SSH keys, abusing legitimate features to persist across firmware updates and targeting residential networks globally.

Microsoft's Russian subsidiary, "Microsoft Rus," is filing for bankruptcy after lawsuits over undelivered services following its 2022 market withdrawal.

A new race condition vulnerability in Perl's threading mechanism exposes systems to local attackers. Upgrade to Perl 5.41.13 or apply the patch immediately.

A SQL injection vulnerability (CVE-2025-48912) in Apache Superset allows authenticated attackers to bypass row-level security, exposing sensitive data.

Google Chrome will distrust TLS certs from Chunghwa Telecom & NetLock starting Aug 1, 2025, due to compliance issues, impacting website access.
Learn how AI protects emails, PDFs, and chat logs while boosting compliance for enterprises. Secure unstructured data intelligently.

Netwrix warns of critical 10.0 CVSS flaws in Directory Manager v11, including a hard-coded password. Patch immediately to prevent unauthorized access and data breaches.
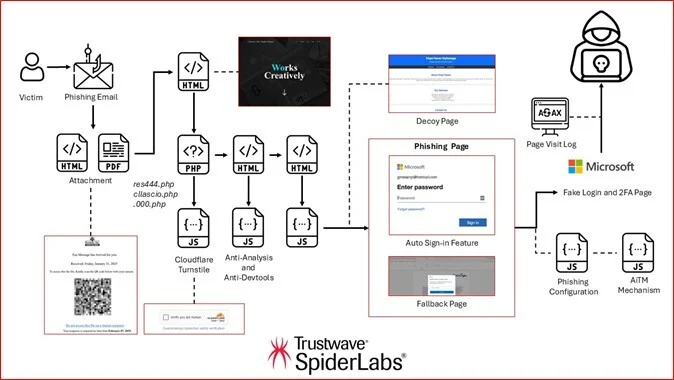
Trustwave uncovers Dadsec and Tycoon2FA, new Phishing-as-a-Service kits bypassing MFA to target Microsoft 365 users with advanced AiTM tactics.

Amidst India-Pakistan tensions, Bitter APT launched a spear phishing campaign against Pakistan Telecommunication Company, using WmRAT for espionage.

Firefox 139.0.1 fixes flickering and graphical glitches on Nvidia GPUs caused by a recent update. Update now for a smooth Browse experience!

Microsoft Authenticator's password manager is being deprecated. Save new passwords until June 2025; migrate to Edge or export your data now!