 cybernewswire
Miami, Florida, 22nd May 2025, CyberNewsWire

 Do Son
Google is placing sponsored ads seamlessly within its AI-generated search summaries, appearing at the bottom of the AI overview on desktop and mobile.

A China-linked APT, UAT-6382, is actively exploiting a zero-day (CVE-2025-0994) in Cityworks to gain RCE and persistent access to government and utility systems.

Global operation neutralizes Lumma Stealer, infecting hundreds of thousands of PCs. Europol & Microsoft seized over 1,300 malicious domains.


Cisco patches two privilege escalation flaws in Unified Intelligence Center that could expose sensitive data. Users urged to upgrade immediately.

A high-severity flaw (CVE-2025-48026) in Mitel OpenScape Xpressions allows unauthenticated attackers to read sensitive local files, including voicemail.

Google Chrome released an update with 8 security fixes, including a high-severity use-after-free vulnerability (CVE-2025-5063). Update your browser now!

ProjectDiscovery revealed critical zero-days (CVSS 10) in Versa Concerto, enabling full RCE and host compromise via auth bypass and Docker escape.

Unauthenticated remote attackers can crash Cisco ISE via RADIUS, enabled by default. CVE-2025-20152 fix released—patch now to prevent DoS.

Grafana rushed an emergency patch for CVE-2025-4123, a high-severity XSS flaw that was made public. Upgrade now to prevent unauthorized access.

GitLab released urgent updates (18.0.1+) fixing high-severity flaws, including a DoS vulnerability (CVE-2025-0993) and a 2FA bypass (CVE-2024-12093).
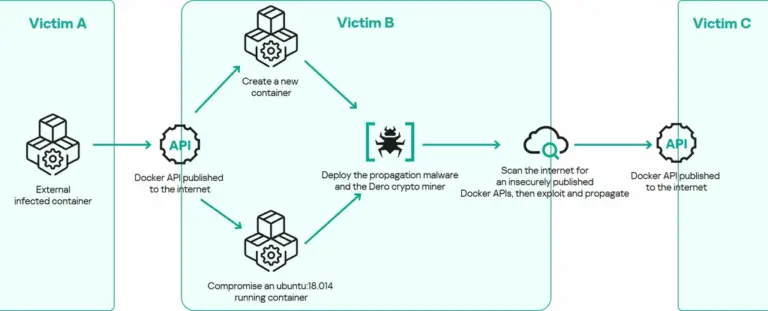
A new self-replicating Dero cryptominer is infecting exposed Docker containers, spreading as a worm without needing a C2 server.
NIST introduces the Likely Exploited Vulnerability (LEV) metric, a new way to estimate which CVEs have likely been exploited in the wild.

Critical vulnerabilities (CVSS 9.8) in the Langroid Python framework allow remote code execution in LLM applications. Update to version 0.53.15 now!


Learn about critical vulnerabilities in LLM-powered Browse agents like Browser Use, allowing domain bypass and prompt injection for data theft.

AutomationDirect's MB-Gateway has a critical (CVSS 10) flaw allowing unauthenticated remote access and RCE. Hardware limits prevent a software fix; replacement is recommended.
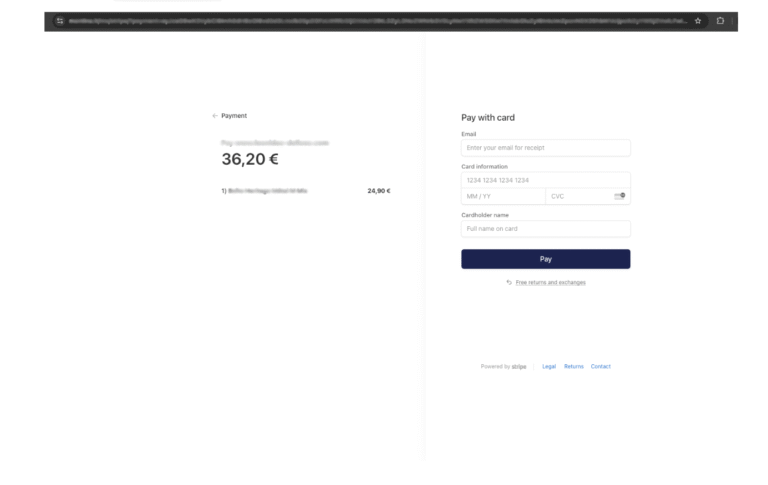
Attackers exploit JSONP flaws in Google APIs to inject malicious scripts into e-commerce sites, silently redirecting users to fake payment pages.

A joint advisory warns that Russia's APT28 (Fancy Bear) is actively targeting logistics and tech companies supporting Ukraine with espionage and data exfiltration.

A high-severity path traversal flaw in setuptools can allow RCE, exposing millions of Python users. Update to 78.1.1 now.