Skip to content
October 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Zero-Day Attacks & Stolen Keys: Silk Typhoon Breaches Networks Artivion cybersecurity - Zero-Day Attacks
  • Cyber Security

Zero-Day Attacks & Stolen Keys: Silk Typhoon Breaches Networks

Do Son March 6, 2025 0
Read More Read more about Zero-Day Attacks & Stolen Keys: Silk Typhoon Breaches Networks
Fake Copyright Claims: YouTubers Tricked into Pushing Malware Youtube malware
  • Malware

Fake Copyright Claims: YouTubers Tricked into Pushing Malware

Do Son March 6, 2025 0
Read More Read more about Fake Copyright Claims: YouTubers Tricked into Pushing Malware
UNK_CraftyCamel: New Threat Group Using Polyglot Malware in UAE UNK_CraftyCamel - Sosano backdoor
  • Cyber Security
  • Malware

UNK_CraftyCamel: New Threat Group Using Polyglot Malware in UAE

Do Son March 6, 2025 0
Read More Read more about UNK_CraftyCamel: New Threat Group Using Polyglot Malware in UAE
CVE-2025-20206: Cisco Secure Client Flaw Allows Code Execution with SYSTEM Privileges Cisco Phone DoS, CVE-2025-20350 Cisco SNMP Flaw CVE-2025-20352 CVE-2024-20398 & CVE-2024-20381 CVE-2025-20206
  • Vulnerability

CVE-2025-20206: Cisco Secure Client Flaw Allows Code Execution with SYSTEM Privileges

Do Son March 6, 2025 0
Read More Read more about CVE-2025-20206: Cisco Secure Client Flaw Allows Code Execution with SYSTEM Privileges
Massive Cyber Campaign Exploits 4,000 ISP IPs in the U.S. and China for Credential Theft and Cryptojacking ISP Infostealer Campaign
  • Malware

Massive Cyber Campaign Exploits 4,000 ISP IPs in the U.S. and China for Credential Theft and Cryptojacking

Do Son March 6, 2025 0
Read More Read more about Massive Cyber Campaign Exploits 4,000 ISP IPs in the U.S. and China for Credential Theft and Cryptojacking
PrintSteal: Unmasking a Large-Scale KYC Document Fraud Operation PrintSteal
  • Cyber Security

PrintSteal: Unmasking a Large-Scale KYC Document Fraud Operation

Do Son March 6, 2025 0
Read More Read more about PrintSteal: Unmasking a Large-Scale KYC Document Fraud Operation
Beyond Keywords: Google’s AI Mode Redefines Search with Chat Google AI Mode
  • Technology

Beyond Keywords: Google’s AI Mode Redefines Search with Chat

Do Son March 6, 2025 0
Read More Read more about Beyond Keywords: Google’s AI Mode Redefines Search with Chat
CSRF and Open Redirect: Jenkins Patches Major Vulnerabilities Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability

CSRF and Open Redirect: Jenkins Patches Major Vulnerabilities

Do Son March 6, 2025 0
Read More Read more about CSRF and Open Redirect: Jenkins Patches Major Vulnerabilities
CVE-2025-25015 (CVSS 9.9): Critical Code Execution Vulnerability Patched in Elastic Kibana
  • Vulnerability

CVE-2025-25015 (CVSS 9.9): Critical Code Execution Vulnerability Patched in Elastic Kibana

Do Son March 5, 2025 0
Read More Read more about CVE-2025-25015 (CVSS 9.9): Critical Code Execution Vulnerability Patched in Elastic Kibana
CVE-2025-26776 (CVSS 10) in Chaty Pro Plugin Exposes Thousands of WordPress Sites to Takeover CVE-2025-26776
  • Vulnerability

CVE-2025-26776 (CVSS 10) in Chaty Pro Plugin Exposes Thousands of WordPress Sites to Takeover

Do Son March 5, 2025 0
Read More Read more about CVE-2025-26776 (CVSS 10) in Chaty Pro Plugin Exposes Thousands of WordPress Sites to Takeover
North Korean IT Workers Pose as Developers on GitHub to Infiltrate Global Companies North Korean IT Workers
  • Cyber Security

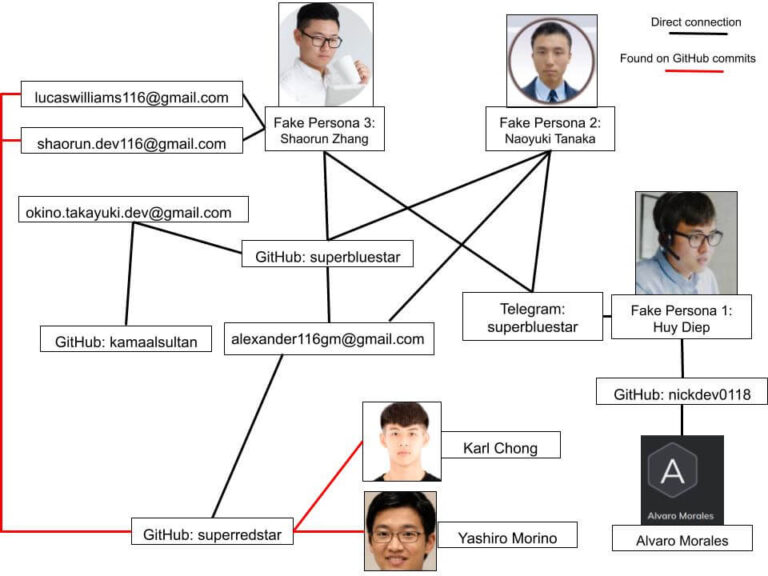
North Korean IT Workers Pose as Developers on GitHub to Infiltrate Global Companies

Do Son March 5, 2025 0
Read More Read more about North Korean IT Workers Pose as Developers on GitHub to Infiltrate Global Companies
B2B Business Email Compromise: A Sophisticated Scheme Exploiting Trusted Relationships B2B Business Email Compromise
  • Cyber Security

B2B Business Email Compromise: A Sophisticated Scheme Exploiting Trusted Relationships

Do Son March 5, 2025 0
Read More Read more about B2B Business Email Compromise: A Sophisticated Scheme Exploiting Trusted Relationships
Russian Cybercriminals Impersonate EFF in Targeted Attack on Albion Online Players DPRK IT Workers, APT38 Crypto Forfeiture
  • Malware

Russian Cybercriminals Impersonate EFF in Targeted Attack on Albion Online Players

Do Son March 5, 2025 0
Read More Read more about Russian Cybercriminals Impersonate EFF in Targeted Attack on Albion Online Players
Cisco Webex for BroadWorks Vulnerability Exposes User Credentials CVE-2024-20419 - Cisco Webex Vulnerability Cisco ISE DoS, CVE-2025-20152
  • Vulnerability

Cisco Webex for BroadWorks Vulnerability Exposes User Credentials

Do Son March 5, 2025 0
Read More Read more about Cisco Webex for BroadWorks Vulnerability Exposes User Credentials
CVE-2025-27507 (CVSS 9.0): ZITADEL Users at Risk of Account Takeover ZITADEL Vulnerability CVE-2026-29191 CVE-2025-27507 ZITADEL SSRF, Login UI Hijack
  • Vulnerability

CVE-2025-27507 (CVSS 9.0): ZITADEL Users at Risk of Account Takeover

Do Son March 5, 2025 0
Read More Read more about CVE-2025-27507 (CVSS 9.0): ZITADEL Users at Risk of Account Takeover
Privacy First: Google’s AI Detects Fraud, No Cloud Storage Google Phone Fraud Detection
  • Android
  • Technology

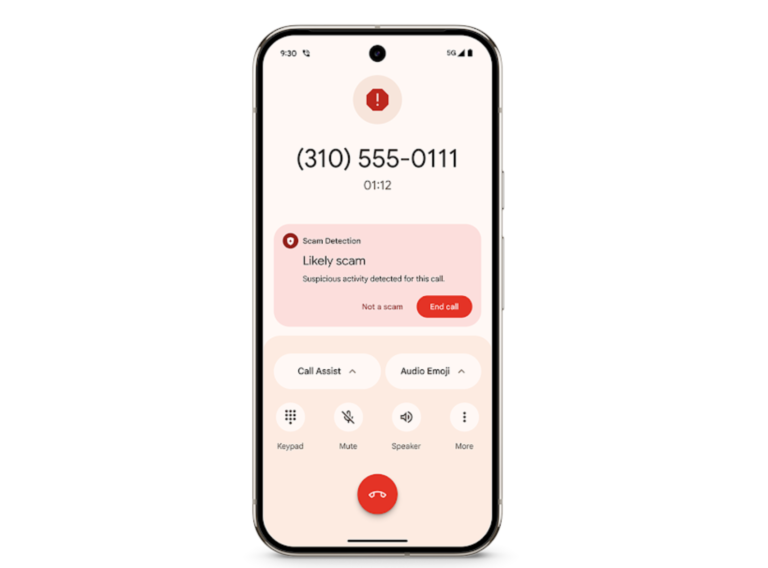
Privacy First: Google’s AI Detects Fraud, No Cloud Storage

Do Son March 5, 2025 0
Read More Read more about Privacy First: Google’s AI Detects Fraud, No Cloud Storage
CVE-2025-1080: LibreOffice Patches Security Flaw Allowing Arbitrary Script Execution CVE-2024-7788 LibreOffice CVE-2025-1080
  • Vulnerability

CVE-2025-1080: LibreOffice Patches Security Flaw Allowing Arbitrary Script Execution

Do Son March 5, 2025 0
Read More Read more about CVE-2025-1080: LibreOffice Patches Security Flaw Allowing Arbitrary Script Execution
Bybit Hack: Lazarus Group Launders $1.4 Billion in Ethereum Through THORChain Cryptocurrency Exchange Security Bybit Hack
  • Cyber Security

Bybit Hack: Lazarus Group Launders $1.4 Billion in Ethereum Through THORChain

Do Son March 5, 2025 0
Read More Read more about Bybit Hack: Lazarus Group Launders $1.4 Billion in Ethereum Through THORChain
Google Fights Back: Breakup Threatens National Security, Company Claims Google Arkansas Investment, AI Data Center Google, privacy fine Ecosia Google Chrome Alphabet Earnings, AI Growth Google Hydropower, AI Data Centers Google Breakup Antitrust Workspace Flows Google Workspace Google remote work, return to office
  • Technology

Google Fights Back: Breakup Threatens National Security, Company Claims

Do Son March 5, 2025 0
Read More Read more about Google Fights Back: Breakup Threatens National Security, Company Claims
CVE-2025-1393 (CVSS 9.8): Hard-Coded Credentials in Weidmüller PROCON-WIN Expose Industrial Systems to Attack Energy Meter RCE CVE-2025-41709 ICS Exposure, Power Grid Security CVE-2025-1393 & CVE-2024-23943
  • Vulnerability

CVE-2025-1393 (CVSS 9.8): Hard-Coded Credentials in Weidmüller PROCON-WIN Expose Industrial Systems to Attack

Do Son March 5, 2025 0
Read More Read more about CVE-2025-1393 (CVSS 9.8): Hard-Coded Credentials in Weidmüller PROCON-WIN Expose Industrial Systems to Attack
Opera Browser Operator: AI Handles Web Tasks, No Cloud Needed Opera Browser Operator
  • Technology

Opera Browser Operator: AI Handles Web Tasks, No Cloud Needed

Do Son March 4, 2025 0
Read More Read more about Opera Browser Operator: AI Handles Web Tasks, No Cloud Needed
Data Privacy Row: Apple Takes UK Government to Court Apple Background Security CVE-2026-20643 Apple Background Security Improvement Apple Backdoor Apple Lawsuit, Data Exfiltration CVE-2024-44131 - CVE-2025-24118 PoC
  • Technology

Data Privacy Row: Apple Takes UK Government to Court

Do Son March 4, 2025 0
Read More Read more about Data Privacy Row: Apple Takes UK Government to Court
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
  • CVE-2026-104286CVSS 9.8
    An improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiMail 8.0.0 through...
    CISA KEV📅 Added to KEV: Oct 1, 2026
  • CVE-2026-76504CVSS 9.8
    A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 30, 2026📅 Updated: Sep 30, 2026
  • CVE-2026-86950CVSS 8.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in iOS 26.7.1 and...
    Admin intelCISA KEV📅 Added to KEV: Sep 29, 2026📅 Updated: Sep 29, 2026
  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-91107CVSS 9.3
    openSIS Classic 9.3 allows an authenticated user with the built-in teacher role can select an arbitrary staff record...
    📅 Updated: Oct 6, 2026
  • CVE-2026-21589CVSS 9.3
    h3. Summary This is a vulnerability in Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center,...
    📅 Updated: Oct 6, 2026
  • CVE-2026-86246CVSS 9.1
    Initialization of a resource with an insecure default vulnerability in Apache Tomcat Native enabled insecure options by default including...
    📅 Updated: Oct 6, 2026
  • CVE-2026-91140CVSS 9.6
    An OS command injection vulnerability in the shell-based temporary-file cleanup instructions in Progress Software Autonomous REST Connector GenAI...
    📅 Updated: Oct 6, 2026
  • CVE-2026-105484CVSS 10.0
    A security vulnerability has been detected in TOTOLINK X6000R 9.4.0cu.652_B20230116. The impacted element is the function firmware_check of...
    📅 Updated: Oct 6, 2026
  • CVE-2026-105835CVSS 9.1
    PLANKA 2.2.0 through 2.2.1 fails to limit incorrect TOTP codes submitted to POST /api/access-tokens/verify-totp, allowing attackers to brute...
    📅 Updated: Oct 6, 2026
  • CVE-2026-82531CVSS 9.2
    Smarty before 4.5.8 and 5.x before 5.8.5 contains a code injection vulnerability where the top-level nocache_hash is never...
    📅 Updated: Oct 6, 2026
  • CVE-2025-12543CVSS 9.6
    A flaw was found in the Undertow HTTP server core, which is used in WildFly, JBoss EAP, and...
    📅 Updated: Oct 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.