Skip to content
October 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2024-12284 in NetScaler Console Exposes Systems to Unauthorized Command Execution CVE-2023-6548 vulnerability CVE-2024-12284
  • Vulnerability

CVE-2024-12284 in NetScaler Console Exposes Systems to Unauthorized Command Execution

Do Son February 19, 2025 0
Read More Read more about CVE-2024-12284 in NetScaler Console Exposes Systems to Unauthorized Command Execution
How Dark Web Monitoring Can Help Financial Services Respond to Emerging Threats How Dark Web Monitoring Can Help Financial Services Respond to Emerging Threats
  • Technique

How Dark Web Monitoring Can Help Financial Services Respond to Emerging Threats

Do Son February 19, 2025 0
Read More Read more about How Dark Web Monitoring Can Help Financial Services Respond to Emerging Threats
Meta Announces LlamaCon Developer Conference Meta AI Investment, Scale AI LlamaCon developer conference
  • Technology

Meta Announces LlamaCon Developer Conference

Do Son February 19, 2025 0
Read More Read more about Meta Announces LlamaCon Developer Conference
Windows 11 Migration: Will Win32 Apps Make the Cut? Windows Migration app
  • Windows

Windows 11 Migration: Will Win32 Apps Make the Cut?

Do Son February 19, 2025 0
Read More Read more about Windows 11 Migration: Will Win32 Apps Make the Cut?
CVE-2024-52577 (CVSS 9.5): Apache Ignite Vulnerability Could Allow Remote Code Execution CVE-2024-52577
  • Vulnerability

CVE-2024-52577 (CVSS 9.5): Apache Ignite Vulnerability Could Allow Remote Code Execution

Do Son February 18, 2025 0
Read More Read more about CVE-2024-52577 (CVSS 9.5): Apache Ignite Vulnerability Could Allow Remote Code Execution
CVE-2025-26519 Exposes Applications Using musl libc to Remote Code Execution CVE-2025-26519
  • Vulnerability

CVE-2025-26519 Exposes Applications Using musl libc to Remote Code Execution

Do Son February 18, 2025 0
Read More Read more about CVE-2025-26519 Exposes Applications Using musl libc to Remote Code Execution
US Threatens UK Over iCloud Backdoor Demand iCloud Backdoor, UK Surveillance iCloud Backdoor
  • Data Leak
  • Technology

US Threatens UK Over iCloud Backdoor Demand

Do Son February 18, 2025 0
Read More Read more about US Threatens UK Over iCloud Backdoor Demand
Anonymous VPS Provider BitLaunch Under Fire for Facilitating Ransomware Attacks BitLaunch hosting provider
  • Cyber Security

Anonymous VPS Provider BitLaunch Under Fire for Facilitating Ransomware Attacks

Do Son February 18, 2025 0
Read More Read more about Anonymous VPS Provider BitLaunch Under Fire for Facilitating Ransomware Attacks
Xerox Versalink Printers Vulnerable to Pass-Back Attacks, Credentials at Risk CVE-2024-12510 and CVE-2024-12511
  • Vulnerability

Xerox Versalink Printers Vulnerable to Pass-Back Attacks, Credentials at Risk

Do Son February 18, 2025 0
Read More Read more about Xerox Versalink Printers Vulnerable to Pass-Back Attacks, Credentials at Risk
New XELERA Ransomware Campaign Spreading Through Malicious Documents XELERA Ransomware Campaign
  • Malware

New XELERA Ransomware Campaign Spreading Through Malicious Documents

Do Son February 18, 2025 0
Read More Read more about New XELERA Ransomware Campaign Spreading Through Malicious Documents
Exploit Code Published for Critical GatesAir Transmitter Vulnerabilities, No Patches Available Yet GatesAir Maxiva UAXT
  • Vulnerability

Exploit Code Published for Critical GatesAir Transmitter Vulnerabilities, No Patches Available Yet

Do Son February 18, 2025 0
Read More Read more about Exploit Code Published for Critical GatesAir Transmitter Vulnerabilities, No Patches Available Yet
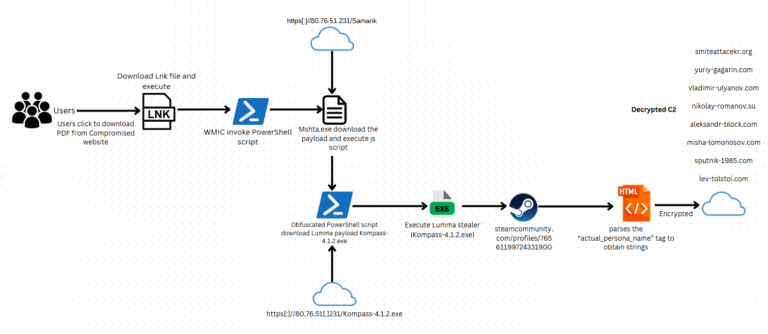
Lumma Stealer Malware Campaign Targets Educational Institutions with Deceptive PDF Lures Lumma Stealer stealer
  • Malware

Lumma Stealer Malware Campaign Targets Educational Institutions with Deceptive PDF Lures

Do Son February 18, 2025 0
Read More Read more about Lumma Stealer Malware Campaign Targets Educational Institutions with Deceptive PDF Lures
CVE-2025-0999 & CVE-2025-1426: Chrome’s Latest Update Patches Major Security Risks Chrome 148 lazy loading Chrome for Linux ARM64 Chrome 145 Update Chrome Security Fixes Chrome Security Update CVE-2026-1220 Chrome 144 Security Update CVE-2026-0899 Chrome Memory Safety, WebGPU UAF Chrome V8 Type Confusion, Google Updater Flaw Chrome V8 Flaw, CVE-2025-13042 Chrome V8, Type Confusion, Chrome 142 Update Chrome V8 Flaw, CVE-2025-12036 Chrome 141, WebGPU Overflow Google Chrome preloading Chrome, V8 vulnerability CVE-2025-9132 Chrome Security Update, Use-After-Free Chrome V8, Type Confusion Chrome Telemetry, Windows 10 EOL Microsoft Family Safety, Chrome Blocking Chrome Security Update, High-Severity Google Chrome, Antitrust CVE-2024-10487 and CVE-2024-10488 Google Chrome Root Program Chrome Update, CVE-2025-3619 Chrome Acquisition, Perplexity.ai
  • Vulnerability

CVE-2025-0999 & CVE-2025-1426: Chrome’s Latest Update Patches Major Security Risks

Do Son February 18, 2025 0
Read More Read more about CVE-2025-0999 & CVE-2025-1426: Chrome’s Latest Update Patches Major Security Risks
90,000 Sites at Risk: Jupiter X Core RCE Vulnerability (CVE-2025-0366) CVE-2023-0291 CVE-2025-0366
  • Vulnerability

90,000 Sites at Risk: Jupiter X Core RCE Vulnerability (CVE-2025-0366)

Do Son February 18, 2025 0
Read More Read more about 90,000 Sites at Risk: Jupiter X Core RCE Vulnerability (CVE-2025-0366)
TRIPLESTRENGTH Threat Actor Group : Ransomware, Mining, and Server Hacks TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Cyber Security

TRIPLESTRENGTH Threat Actor Group : Ransomware, Mining, and Server Hacks

Do Son February 18, 2025 0
Read More Read more about TRIPLESTRENGTH Threat Actor Group : Ransomware, Mining, and Server Hacks
OpenSSH Flaws CVE-2025-26465 & CVE-2025-26466 Expose Clients and Servers to Attacks CVE-2024-6409 - CVE-2025-26466 - CVE-2025-26465
  • Vulnerability

OpenSSH Flaws CVE-2025-26465 & CVE-2025-26466 Expose Clients and Servers to Attacks

Do Son February 18, 2025 0
Read More Read more about OpenSSH Flaws CVE-2025-26465 & CVE-2025-26466 Expose Clients and Servers to Attacks
PirateFi Removed: Malware Found in Steam Game Steam Store Redesign, Valve Update macOS Steam Game malware Chromebooks Steam
  • Malware

PirateFi Removed: Malware Found in Steam Game

Do Son February 18, 2025 0
Read More Read more about PirateFi Removed: Malware Found in Steam Game
ZServers/XHost Bulletproof Hosting Down: 127 Servers Seized Davis Lu, Kill Switch
  • Cyber Security

ZServers/XHost Bulletproof Hosting Down: 127 Servers Seized

Do Son February 18, 2025 0
Read More Read more about ZServers/XHost Bulletproof Hosting Down: 127 Servers Seized
Chinese Hackers Emperor Dragonfly Use Espionage Tools for Ransomware AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Cyber Security

Chinese Hackers Emperor Dragonfly Use Espionage Tools for Ransomware

Do Son February 18, 2025 0
Read More Read more about Chinese Hackers Emperor Dragonfly Use Espionage Tools for Ransomware
LibreOffice Vulnerabilities (CVE-2024-12425 & CVE-2024-12426): PoCs Released, Patch ASAP LibreOffice Vulnerabilities
  • Vulnerability

LibreOffice Vulnerabilities (CVE-2024-12425 & CVE-2024-12426): PoCs Released, Patch ASAP

Do Son February 17, 2025 0
Read More Read more about LibreOffice Vulnerabilities (CVE-2024-12425 & CVE-2024-12426): PoCs Released, Patch ASAP
CVE-2023-20198 & CVE-2023-20273: RedMike Attacks 1,000+ Cisco Devices in Global Espionage Campaign RedMine
  • Cyber Security
  • Vulnerability

CVE-2023-20198 & CVE-2023-20273: RedMike Attacks 1,000+ Cisco Devices in Global Espionage Campaign

Do Son February 17, 2025 0
Read More Read more about CVE-2023-20198 & CVE-2023-20273: RedMike Attacks 1,000+ Cisco Devices in Global Espionage Campaign
Stealth Attack: EarthKapre Leverages Cloud and DLL Sideloading for Data Exfiltration RedCurl APT EarthKapre
  • Cyber Security
  • Malware

Stealth Attack: EarthKapre Leverages Cloud and DLL Sideloading for Data Exfiltration

Do Son February 17, 2025 0
Read More Read more about Stealth Attack: EarthKapre Leverages Cloud and DLL Sideloading for Data Exfiltration
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
  • CVE-2026-104286CVSS 9.8
    An improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiMail 8.0.0 through...
    CISA KEV📅 Added to KEV: Oct 1, 2026
  • CVE-2026-76504CVSS 9.8
    A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 30, 2026📅 Updated: Sep 30, 2026
  • CVE-2026-86950CVSS 8.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in iOS 26.7.1 and...
    Admin intelCISA KEV📅 Added to KEV: Sep 29, 2026📅 Updated: Sep 29, 2026
  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-105135CVSS 10.0
    A vulnerability has been found in InternLM MindSearch 0.1.0. This issue affects the function ExecutionAction.run of the file...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106501CVSS 9.6
    Backstage is an open framework for building developer portals. Prior to 3.3.1, 3.4.1, 4.0.3 and 4.1.0, the @backstage/plugin-scaffolder-backend...
    📅 Updated: Oct 6, 2026
  • CVE-2026-55330CVSS 9.8
    In BluetoothCccHandlerCallbackImpl of bluetooth_ccc.cc, there is a possible use-after-free due to a logic error in the code. This...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106417CVSS 9.6
    Integer overflow in Media in Google Chrome prior to 155.0.8059.39 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106375CVSS 9.6
    Incomplete cleanup in Dawn in Google Chrome prior to 155.0.8059.39 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106401CVSS 9.6
    Out of bounds write in Media in Google Chrome prior to 155.0.8059.39 allowed a remote attacker to potentially...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106372CVSS 9.6
    Incorrect authorization in UI in Google Chrome prior to 155.0.8059.39 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106323CVSS 9.6
    Missing authorization in Chrome for iOS in Google Chrome on on iOS prior to 155.0.8059.39 allowed a remote...
    📅 Updated: Oct 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.