Skip to content
October 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Palo Alto Firewall Flaw (CVE-2025-0108): Active Exploits in the Wild, PoC Released Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability

Palo Alto Firewall Flaw (CVE-2025-0108): Active Exploits in the Wild, PoC Released

Do Son February 13, 2025 0
Read More Read more about Palo Alto Firewall Flaw (CVE-2025-0108): Active Exploits in the Wild, PoC Released
CVE-2025-1126: Critical Lexmark Print Management Client Bug Puts Systems at Risk CVE-2025-1126 Lexmark, Remote Code Execution
  • Vulnerability

CVE-2025-1126: Critical Lexmark Print Management Client Bug Puts Systems at Risk

Do Son February 13, 2025 0
Read More Read more about CVE-2025-1126: Critical Lexmark Print Management Client Bug Puts Systems at Risk
New I2PRAT Malware: Advanced, Undetectable? Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

New I2PRAT Malware: Advanced, Undetectable?

Do Son February 13, 2025 0
Read More Read more about New I2PRAT Malware: Advanced, Undetectable?
CVE-2024-32838 (CVSS 9.4): Critical SQL Injection Flaw Threatens Apache Fineract Users CVE-2024-32838 Apache Fineract IDOR, Core Banking Bypass
  • Vulnerability

CVE-2024-32838 (CVSS 9.4): Critical SQL Injection Flaw Threatens Apache Fineract Users

Do Son February 13, 2025 0
Read More Read more about CVE-2024-32838 (CVSS 9.4): Critical SQL Injection Flaw Threatens Apache Fineract Users
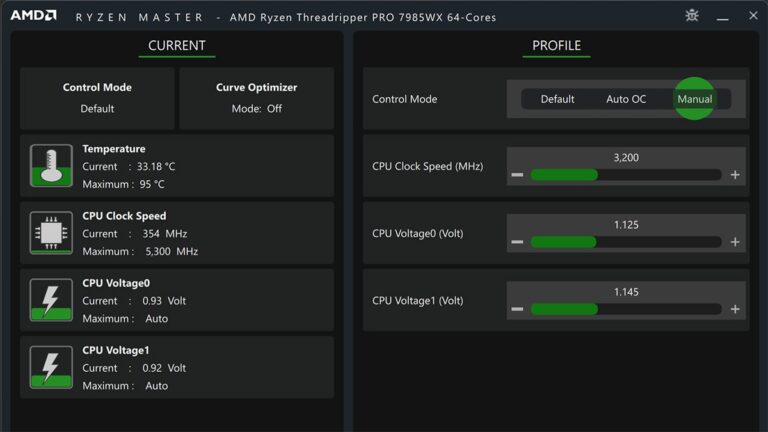
AMD Ryzen Master Utility Vulnerable to DLL Hijacking (CVE-2024-21966) CVE-2024-21966
  • Vulnerability

AMD Ryzen Master Utility Vulnerable to DLL Hijacking (CVE-2024-21966)

Do Son February 13, 2025 0
Read More Read more about AMD Ryzen Master Utility Vulnerable to DLL Hijacking (CVE-2024-21966)
Hackers Can Take Over 30,000 WordPress Sites Due to Critical CleanTalk Security Flaw (CVE-2024-13365) CVE-2024-13365
  • Vulnerability

Hackers Can Take Over 30,000 WordPress Sites Due to Critical CleanTalk Security Flaw (CVE-2024-13365)

Do Son February 13, 2025 0
Read More Read more about Hackers Can Take Over 30,000 WordPress Sites Due to Critical CleanTalk Security Flaw (CVE-2024-13365)
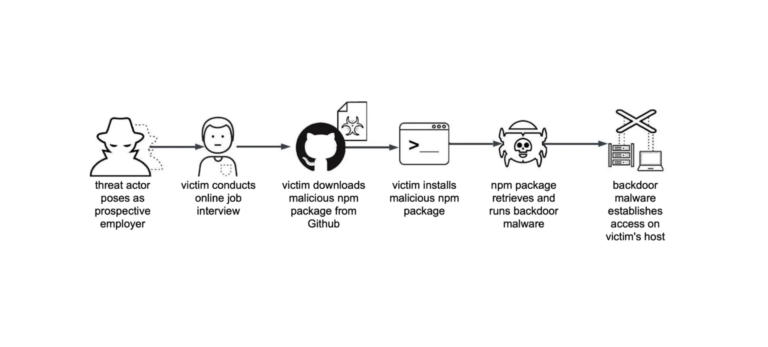
Lazarus Group’s Infostealer Malware Targets Developers in New Espionage Campaigns Lazarus Group’s Infostealer Malware
  • Malware

Lazarus Group’s Infostealer Malware Targets Developers in New Espionage Campaigns

Do Son February 13, 2025 0
Read More Read more about Lazarus Group’s Infostealer Malware Targets Developers in New Espionage Campaigns
CVE-2025-23359: NVIDIA Container Toolkit Flaw Could Lead to Code Execution and Denial of Service CVE-2025-23359
  • Vulnerability

CVE-2025-23359: NVIDIA Container Toolkit Flaw Could Lead to Code Execution and Denial of Service

Do Son February 13, 2025 0
Read More Read more about CVE-2025-23359: NVIDIA Container Toolkit Flaw Could Lead to Code Execution and Denial of Service
Russian Influence Operations Target German Elections Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security

Russian Influence Operations Target German Elections

Do Son February 13, 2025 0
Read More Read more about Russian Influence Operations Target German Elections
XSS Flaw in Apache Atlas (CVE-2024-46910) Puts Data Governance at Risk CVE-2024-46910 Apache Atlas Vulnerability Gremlin Code Injection
  • Vulnerability

XSS Flaw in Apache Atlas (CVE-2024-46910) Puts Data Governance at Risk

Do Son February 13, 2025 0
Read More Read more about XSS Flaw in Apache Atlas (CVE-2024-46910) Puts Data Governance at Risk
South Korean CSOs Under Cyberattack: 3-Year Study South Korean Cyberattack
  • Cyber Security

South Korean CSOs Under Cyberattack: 3-Year Study

Do Son February 13, 2025 0
Read More Read more about South Korean CSOs Under Cyberattack: 3-Year Study
How Satellite IoT Companies Are Solving Global Connectivity Challenges Open Sesame attack - CVE-2024-52324
  • Technique

How Satellite IoT Companies Are Solving Global Connectivity Challenges

Do Son February 13, 2025 0
Read More Read more about How Satellite IoT Companies Are Solving Global Connectivity Challenges
The Role of Laser Beam Shapers in Beam Shaping a
  • Technique

The Role of Laser Beam Shapers in Beam Shaping

Do Son February 13, 2025 0
Read More Read more about The Role of Laser Beam Shapers in Beam Shaping
5 Ways Micro Coils and Sensors Are Revolutionizing the Field of Medicine Medicine
  • Technique

5 Ways Micro Coils and Sensors Are Revolutionizing the Field of Medicine

Do Son February 13, 2025 0
Read More Read more about 5 Ways Micro Coils and Sensors Are Revolutionizing the Field of Medicine
macOS Security Breach: CVE-2024-54531 PoC Published, Attackers Can Bypass KASLR CVE-2024-54531 PoC
  • Vulnerability

macOS Security Breach: CVE-2024-54531 PoC Published, Attackers Can Bypass KASLR

Do Son February 12, 2025 0
Read More Read more about macOS Security Breach: CVE-2024-54531 PoC Published, Attackers Can Bypass KASLR
OpenAI to Integrate o3 Model into GPT-5, Offering Free Access to All Users o3-Pro model AI Model, OpenAI ChatGPT malware - GPT-5 Model
  • Technology

OpenAI to Integrate o3 Model into GPT-5, Offering Free Access to All Users

Do Son February 12, 2025 0
Read More Read more about OpenAI to Integrate o3 Model into GPT-5, Offering Free Access to All Users
zkLend Hacked: $9.5 Million in Bitcoin Stolen TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Cyber Security

zkLend Hacked: $9.5 Million in Bitcoin Stolen

Do Son February 12, 2025 0
Read More Read more about zkLend Hacked: $9.5 Million in Bitcoin Stolen
How to Read Other’s Instagram Messages Without Them Knowing | 3 Methods Instagram 3 Billion, Reels Focus
  • Technique

How to Read Other’s Instagram Messages Without Them Knowing | 3 Methods

Do Son February 12, 2025 0
Read More Read more about How to Read Other’s Instagram Messages Without Them Knowing | 3 Methods
CVE-2025-0108 & CVE-2025-0110: Palo Alto Networks Fixes High-Severity PAN-OS Vulnerabilities PAN-OS IKEv2 Buffer Overflow CVE-2026-0263 Palo Alto Cortex XDR Privilege Escalation Palo Alto Networks Vulnerability CVE-2026-0229 PAN-OS Vulnerability CVE-2026-0227 CVE-2024-5914 - Palo Alto Networks - CVE-2025-0108 & CVE-2025-0110
  • Vulnerability

CVE-2025-0108 & CVE-2025-0110: Palo Alto Networks Fixes High-Severity PAN-OS Vulnerabilities

Do Son February 12, 2025 0
Read More Read more about CVE-2025-0108 & CVE-2025-0110: Palo Alto Networks Fixes High-Severity PAN-OS Vulnerabilities
CrowdStrike Addresses High-Severity TLS Vulnerability in Falcon Sensor for Linux (CVE-2025-1146) LogScale Vulnerability Path Traversal Falcon Sensor File Deletion, CVE-2025-42701 CrowdStrike update crashes - CVE 2025-1146
  • Vulnerability

CrowdStrike Addresses High-Severity TLS Vulnerability in Falcon Sensor for Linux (CVE-2025-1146)

Do Son February 12, 2025 0
Read More Read more about CrowdStrike Addresses High-Severity TLS Vulnerability in Falcon Sensor for Linux (CVE-2025-1146)
InvestAI: EU Invests €200 Billion in AI to Rival US and China Apple Google EU alliance DMA European Commission Breach Trivy Supply Chain Attack Europa.eu Breach EU Cloud Infrastructure EU Cyber Sanctions State-Sponsored Hacking EU 2040 Emissions Target, Europe Climate Leadership AWS Azure DMA Cloud Gatekeeper DSA violation, illegal content Apple DMA Delay, iPhone Mirroring EU EU Age Verification, Google Play Integrity Corning Antitrust, EU Competition Apple EU Digital Markets Act App Store commission European Union cyberattacks - InvestAI EU Targets Musk’s X Digital Markets Act, EU fines
  • Technology

InvestAI: EU Invests €200 Billion in AI to Rival US and China

Do Son February 12, 2025 0
Read More Read more about InvestAI: EU Invests €200 Billion in AI to Rival US and China
Attackers Ramp Up Exploitation of CVE-2022-47945 and CVE-2023-49103 Vulnerabilities Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Vulnerability

Attackers Ramp Up Exploitation of CVE-2022-47945 and CVE-2023-49103 Vulnerabilities

Do Son February 12, 2025 0
Read More Read more about Attackers Ramp Up Exploitation of CVE-2022-47945 and CVE-2023-49103 Vulnerabilities
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
  • CVE-2026-104286CVSS 9.8
    An improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiMail 8.0.0 through...
    CISA KEV📅 Added to KEV: Oct 1, 2026
  • CVE-2026-76504CVSS 9.8
    A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 30, 2026📅 Updated: Sep 30, 2026
  • CVE-2026-86950CVSS 8.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in iOS 26.7.1 and...
    Admin intelCISA KEV📅 Added to KEV: Sep 29, 2026📅 Updated: Sep 29, 2026
  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-93674CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.2 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 7, 2026
  • CVE-2026-104334CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.2 could allow a remote attacker to execute arbitrary code due to improper...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106501CVSS 9.6
    Backstage is an open framework for building developer portals. Prior to 3.3.1, 3.4.1, 4.0.3 and 4.1.0, the @backstage/plugin-scaffolder-backend...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106414CVSS 9.6
    Improper input validation in Mobile in Google Chrome on on iOS prior to 155.0.8059.39 allowed a remote attacker...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106329CVSS 9.6
    Incorrect authorization in FileSystem in Google Chrome prior to 155.0.8059.39 allowed a remote attacker leveraging social engineering to...
    📅 Updated: Oct 6, 2026
  • CVE-2026-106239CVSS 9.6
    Integer overflow in WebGL in Google Chrome on on Android prior to 155.0.8059.39 allowed a remote attacker to...
    📅 Updated: Oct 6, 2026
  • CVE-2026-102322CVSS 9.6
    Incorrect Authorization in SiteIsolation in Google Chrome prior to 155.0.8059.39 allowed a remote attacker to execute arbitrary code...
    📅 Updated: Oct 6, 2026
  • CVE-2024-46484CVSS 9.8
    TRENDnet TV-IP410 vA1.0R was discovered to contain an OS command injection vulnerability via the /server/cgi-bin/testserv.cgi component.
    📅 Updated: Oct 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.