Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2025-2704: Critical Bug in OpenVPN Can Trigger Server Crashes CVE-2025-2704
  • Vulnerability

CVE-2025-2704: Critical Bug in OpenVPN Can Trigger Server Crashes

Do Son April 4, 2025 0

OpenVPN 2.6.14 addresses CVE-2025-2704 to prevent denial of service. Ensure your VPN is secure against this vulnerability.

Apache Traffic Server Hit by Request Smuggling Vulnerability (CVE-2024-53868) CVE-2024-53868
  • Vulnerability

Apache Traffic Server Hit by Request Smuggling Vulnerability (CVE-2024-53868)

Do Son April 4, 2025 0

Understand CVE-2024-53868: a vulnerability in Apache Traffic Server that affects how chunked messages are processed.
RolandSkimmer: New Wave of Credit Card Skimming Attacks RolandSkimmer
  • Malware

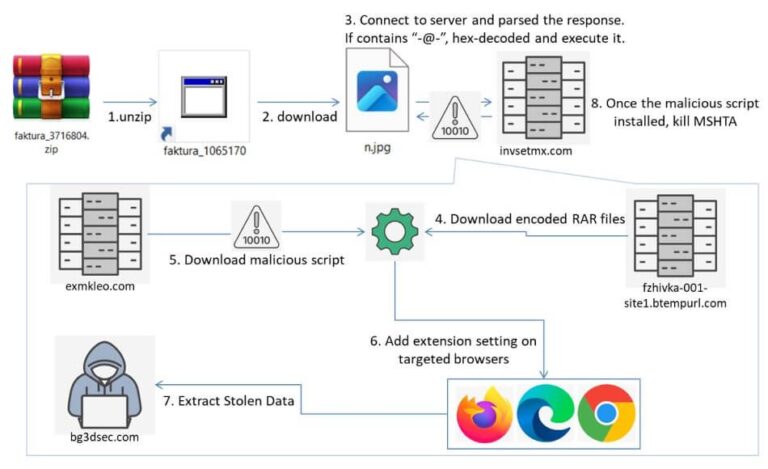
RolandSkimmer: New Wave of Credit Card Skimming Attacks

Do Son April 4, 2025 0

Discover the dangers of RolandSkimmer and how it exploits browser vulnerabilities through deceptive ZIP files and extensions.

Operation HollowQuill Unveiled: Weaponized Documents Infiltrate Russia’s Defense Sector Operation HollowQuill
  • Cyber Security

Operation HollowQuill Unveiled: Weaponized Documents Infiltrate Russia’s Defense Sector

Do Son April 4, 2025 0

Uncover the details of Operation HollowQuill, which targets defense institutions using weaponized documents for infiltration.

Carding Automation: Malicious PyPI Package Threatens Stores Carding attacks
  • Malware

Carding Automation: Malicious PyPI Package Threatens Stores

Do Son April 4, 2025 0

Discover the rise of carding attacks with the malicious Python package disgrasya targeting WooCommerce stores with automated scripts.

Beware the Bait: BeaverTail and Tropidoor Malware Lurk in Recruitment Emails WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Malware

Beware the Bait: BeaverTail and Tropidoor Malware Lurk in Recruitment Emails

Do Son April 4, 2025 0

Explore the dangers of Tropidoor malware and how deceptive emails can lead to cyber threats. Stay informed and protected.
Cisco Addresses High Severity Vulnerabilities in Enterprise Chat and Email, and Meraki MX/Z Series Devices Cisco Secure FMC CVE-2026-20079 Cisco RCE, Firewall Vulnerability Cisco Nexus, vulnerability CVE-2024-20412 - Cisco data breach
  • Vulnerability

Cisco Addresses High Severity Vulnerabilities in Enterprise Chat and Email, and Meraki MX/Z Series Devices

Do Son April 4, 2025 0

Learn about CVE-2025-20139 and its impact on Cisco's Enterprise Chat and Email security. Stay informed and protect your systems.

CVE-2025-22457: UNC5221 Exploits Ivanti Zero-Day Flaw to Deploy TRAILBLAZE and BRUSHFIRE Malware CVE-2025-22457
  • Vulnerability

CVE-2025-22457: UNC5221 Exploits Ivanti Zero-Day Flaw to Deploy TRAILBLAZE and BRUSHFIRE Malware

Do Son April 3, 2025 0

Learn about CVE-2025-22457, a critical vulnerability in Ivanti products that allows remote code execution by attackers.

CVE-2025-31334: WinRAR Flaw Enables Mark-of-the-Web Bypass and Arbitrary Code Execution CVE-2025-31334
  • Vulnerability

CVE-2025-31334: WinRAR Flaw Enables Mark-of-the-Web Bypass and Arbitrary Code Execution

Do Son April 3, 2025 0

Learn about CVE-2025-31334, a new vulnerability in WinRAR that can bypass Windows security and execute malicious code.

AI Crawlers Deluge Wikimedia Commons, Consuming Over 65% of High-Cost Bandwidth ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

AI Crawlers Deluge Wikimedia Commons, Consuming Over 65% of High-Cost Bandwidth

Do Son April 3, 2025 0

Explore the issue of AI crawlers and their impact on bandwidth and resources in the Wikimedia Commons project.

Google Password Manager Adds Passkeys, Future Export Teased Google Password Manager passkey export
  • Technology

Google Password Manager Adds Passkeys, Future Export Teased

Do Son April 3, 2025 0

Learn about Google Password Manager passkey export to enhance security and streamline multi-factor authentication.
Amazon Eyes TikTok: Acquisition Race Heats Up TikTok USDS Joint Venture LLC, TikTok U.S. divestment 2026 TikTok Deal, ByteDance Divestment U.S. ban TikTok TikTok Sale, Trump Announcement TikTok lawsuit Trump Amazon Acquisition
  • Technology

Amazon Eyes TikTok: Acquisition Race Heats Up

Do Son April 3, 2025 0

Amazon has entered the fray, expressing interest in purchasing TikTok's American division and engaging in discussions with U.S. Vice President JD Vance

Verizon Call Filter App Vulnerability Exposed Call Records of Millions Verizon
  • Data Leak
  • Vulnerability

Verizon Call Filter App Vulnerability Exposed Call Records of Millions

Do Son April 3, 2025 0

Learn about the Verizon Call Filter app vulnerability that exposed call history logs of customers and raised privacy concerns.

Multiple Jenkins Plugin and Core Vulnerabilities Expose Sensitive Data and Execution Paths CVE-2025-31720
  • Vulnerability

Multiple Jenkins Plugin and Core Vulnerabilities Expose Sensitive Data and Execution Paths

Do Son April 3, 2025 0

Learn about CVE-2025-31720, a security vulnerability in Jenkins that allows unauthorized access to agent configurations.

CVE-2025-31137: React Router Vulnerability Exposes Web Apps to Cache Poisoning and WAF Bypass Attacks CVE-2025-31137
  • Vulnerability

CVE-2025-31137: React Router Vulnerability Exposes Web Apps to Cache Poisoning and WAF Bypass Attacks

Do Son April 3, 2025 0

Explore CVE-2025-31137, a React Router vulnerability that can exploit URL manipulations through specific headers.

CVE-2025-0415 (CVSSv4 9.2): Critical Vulnerability Discovered in Moxa Network Devices Moxa Hard-Coded Credentials, Critical JWT Bypass CVE-2024-9137 and CVE-2024-9139 - CVE-2024-12297 CVE-2024-7695 CVE-2024-9404 CVE-2024-12297 CVE-2025-0415
  • Vulnerability

CVE-2025-0415 (CVSSv4 9.2): Critical Vulnerability Discovered in Moxa Network Devices

Do Son April 3, 2025 0

Learn about CVE-2025-0415 and its critical impact on Moxa secure routers. Protect your devices from potential exploitation.

Multiple Vulnerabilities in Zabbix Open the Door to XSS, DoS, and SQL Injection CVE-2024-36465
  • Vulnerability

Multiple Vulnerabilities in Zabbix Open the Door to XSS, DoS, and SQL Injection

Do Son April 3, 2025 0

Learn about CVE-2024-36465, a critical SQL injection vulnerability in Zabbix API that can be exploited by low-privilege users.

Outlaw Linux Malware: Persistent Threat Leveraging Simplicity Outlaw Linux malware
  • Malware

Outlaw Linux Malware: Persistent Threat Leveraging Simplicity

Do Son April 3, 2025 0

Explore the dangers of Outlaw Linux malware, a persistent coinminer that combines automated execution with manual oversight.

DLL Sideloading Exposed: TookPS Hides with TeamViewer TookPS downloader
  • Malware

DLL Sideloading Exposed: TookPS Hides with TeamViewer

Do Son April 3, 2025 0

Uncover the threat posed by the TookPS downloader, a malware strain exploiting popular software and fraudulent websites.

Rancher Users: Update Now to Fix Admin Takeover Bug (CVE-2025-23391) CVE-2025-23391
  • Vulnerability

Rancher Users: Update Now to Fix Admin Takeover Bug (CVE-2025-23391)

Do Son April 3, 2025 0

Learn about CVE-2025-23391, a critical vulnerability in Rancher that allows Restricted Administrators to compromise accounts.

DPRK IT Workers: A Global Threat Expanding in Scope and Scale DPRK IT worker
  • Cyber Security

DPRK IT Workers: A Global Threat Expanding in Scope and Scale

Do Son April 3, 2025 0

Learn how DPRK IT workers are expanding their reach beyond the United States, posing serious cybersecurity threats worldwide.

High-Severity Vulnerabilities in Bruno API Client Expose Users to Potential RCE CVE-2025-30354 & CVE-2025-30210
  • Vulnerability

High-Severity Vulnerabilities in Bruno API Client Expose Users to Potential RCE

Do Son April 3, 2025 0

Explore CVE-2025-30354 & CVE-2025-30210 and their implications for the Bruno API client. Discover the risks of Safe-Mode bypass vulnerabilities

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-123218CVSS 9.8
    IBM Aspera Faspex 5.0.0 through 5.0.19 could allow an authorized user to craft a specific message to bypass...
    CISA KEV📅 Added to KEV: Nov 9, 2026📅 Updated: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-89126CVSS 10.0
    SAP Web Dispatcher does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89119CVSS 9.6
    SAP Web Dispatcher and SAP NetWeaver Application Server ABAP (Internet Communication Manager) do not perform sufficient request validation...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89103CVSS 10.0
    SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attacker as internal...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76964CVSS 10.0
    SAP NetWeaver Application Server ABAP does not sufficiently validate certain network input processed by an internal component. An...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76965CVSS 9.9
    SAP NetWeaver Application Server ABAP and ABAP Platform does not perform necessary authorization checks for certain internal functionality....
    📅 Updated: Nov 10, 2026
  • CVE-2026-120017CVSS 10.0
    SAP NetWeaver AS ABAP and ABAP Platform does not perform sufficient verification of incoming authentication assertions under certain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.