Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Telegram’s EvilLoader: Hackers Exploit Video Flaw Again EvilLoader
  • Vulnerability

Telegram’s EvilLoader: Hackers Exploit Video Flaw Again

Do Son March 7, 2025 0

Learn about EvilLoader and its impact on Telegram for Android. Discover how it enables the distribution of malware.

Secret Service-Led Operation Seizes Garantex Cryptocurrency Exchange Garantex Seize
  • Cyber Security

Secret Service-Led Operation Seizes Garantex Cryptocurrency Exchange

Do Son March 7, 2025 0

Explore the Garantex Seize operation led by the U.S. Secret Service against a major ransomware laundering hub.

Android 16: June Release Confirmed by Google at MWC Android 16 adoption rate Android 16KB Page, .NET MAUI 9 Android Security, Fast Charging Android Canary, Developer Program Android Updates, EU Regulation Android 16 Google Android Terminal Cloud Compilation Android, Google I/O
  • Android

Android 16: June Release Confirmed by Google at MWC

Do Son March 7, 2025 0

Android 16 is coming in June with a stable release. Learn about the new updates and speedier security patches now.

Apple AI: Summarizing App Reviews, No More Scrolling App Store, Developer Revenue AI-Generated Review Summaries
  • Technology

Apple AI: Summarizing App Reviews, No More Scrolling

Do Son March 7, 2025 0

Explore AI-generated review summaries from Apple for apps and games, offering insights into user sentiments effortlessly.

Critical Flaws Uncovered in DrayTek Routers: Backdoors, RCE, and Weak Authentication Exposed CVE-2024-41339 & CVE-2024-41334
  • Vulnerability

Critical Flaws Uncovered in DrayTek Routers: Backdoors, RCE, and Weak Authentication Exposed

Do Son March 6, 2025 0

Learn about CVE-2024-41339 & CVE-2024-41334 and the critical vulnerabilities discovered in DrayTek Vigor routers by the Faraday Team.

CISA Warns of Critical Edimax IP Camera Flaw (CVE-2025-1316) with Public Exploits and No Vendor Fix shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability

CISA Warns of Critical Edimax IP Camera Flaw (CVE-2025-1316) with Public Exploits and No Vendor Fix

Do Son March 6, 2025 0

CISA warns about CVE-2025-1316 vulnerability in Edimax IC-7100 IP cameras. This flaw permits remote code execution by attackers.

Zero-Day Attacks & Stolen Keys: Silk Typhoon Breaches Networks Artivion cybersecurity - Zero-Day Attacks
  • Cyber Security

Zero-Day Attacks & Stolen Keys: Silk Typhoon Breaches Networks

Do Son March 6, 2025 0

Learn how Silk Typhoon utilizes Zero-Day Attacks to target remote management tools and access cloud environments effectively.

Fake Copyright Claims: YouTubers Tricked into Pushing Malware Youtube malware
  • Malware

Fake Copyright Claims: YouTubers Tricked into Pushing Malware

Do Son March 6, 2025 0

Learn how YouTube is being exploited to spread malware through deceptive links shared by YouTubers and hackers.

UNK_CraftyCamel: New Threat Group Using Polyglot Malware in UAE UNK_CraftyCamel - Sosano backdoor
  • Cyber Security
  • Malware

UNK_CraftyCamel: New Threat Group Using Polyglot Malware in UAE

Do Son March 6, 2025 0

Explore the UNK_CraftyCamel campaign, a sophisticated cyber-espionage threat targeting UAE aviation and transportation.

CVE-2025-20206: Cisco Secure Client Flaw Allows Code Execution with SYSTEM Privileges Cisco Phone DoS, CVE-2025-20350 Cisco SNMP Flaw CVE-2025-20352 CVE-2024-20398 & CVE-2024-20381 CVE-2025-20206
  • Vulnerability

CVE-2025-20206: Cisco Secure Client Flaw Allows Code Execution with SYSTEM Privileges

Do Son March 6, 2025 0

CVE-2025-20206 affects Cisco Secure Client for Windows, potentially allowing attackers to execute arbitrary code seamlessly.

Massive Cyber Campaign Exploits 4,000 ISP IPs in the U.S. and China for Credential Theft and Cryptojacking ISP Infostealer Campaign
  • Malware

Massive Cyber Campaign Exploits 4,000 ISP IPs in the U.S. and China for Credential Theft and Cryptojacking

Do Son March 6, 2025 0

Learn about the ISP Infostealer Campaign and its severe impacts on ISP infrastructure through brute force and data exfiltration.

PrintSteal: Unmasking a Large-Scale KYC Document Fraud Operation PrintSteal
  • Cyber Security

PrintSteal: Unmasking a Large-Scale KYC Document Fraud Operation

Do Son March 6, 2025 0

Uncover the PrintSteal operation that produces counterfeit KYC documents in India. Learn about its scope and security risks.

Beyond Keywords: Google’s AI Mode Redefines Search with Chat Google AI Mode
  • Technology

Beyond Keywords: Google’s AI Mode Redefines Search with Chat

Do Son March 6, 2025 0

Explore the new Google AI Mode. Engage in interactive searches and refine results with a conversational AI experience.

CSRF and Open Redirect: Jenkins Patches Major Vulnerabilities Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability

CSRF and Open Redirect: Jenkins Patches Major Vulnerabilities

Do Son March 6, 2025 0

Find out how the latest Jenkins vulnerability advisory affects versions 2.499 and earlier. Learn the details of the security issues.

CVE-2025-25015 (CVSS 9.9): Critical Code Execution Vulnerability Patched in Elastic Kibana
  • Vulnerability

CVE-2025-25015 (CVSS 9.9): Critical Code Execution Vulnerability Patched in Elastic Kibana

Do Son March 5, 2025 0

Learn about CVE-2025-25015: a serious vulnerability in Kibana that poses risks of arbitrary code execution on systems.
CVE-2025-26776 (CVSS 10) in Chaty Pro Plugin Exposes Thousands of WordPress Sites to Takeover CVE-2025-26776
  • Vulnerability

CVE-2025-26776 (CVSS 10) in Chaty Pro Plugin Exposes Thousands of WordPress Sites to Takeover

Do Son March 5, 2025 0

Learn about CVE-2025-26776, a critical vulnerability in Chaty Pro that can lead to website takeover for over 18,000 users.
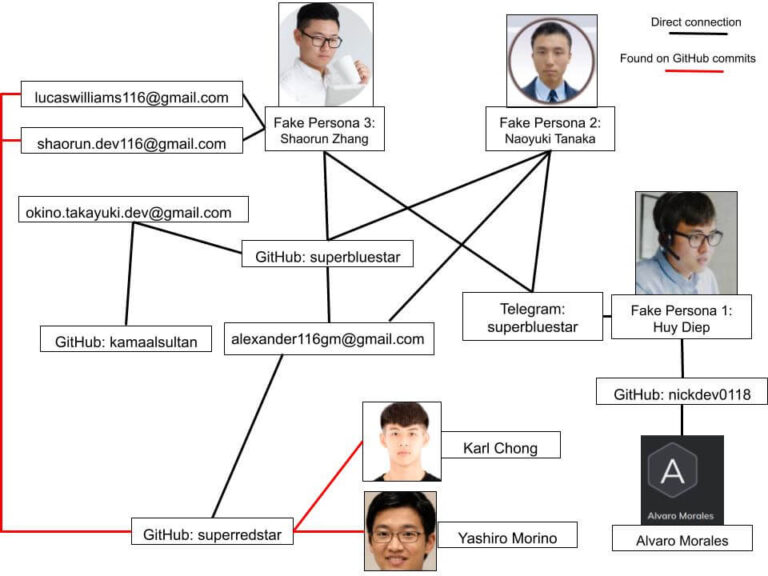
North Korean IT Workers Pose as Developers on GitHub to Infiltrate Global Companies North Korean IT Workers
  • Cyber Security

North Korean IT Workers Pose as Developers on GitHub to Infiltrate Global Companies

Do Son March 5, 2025 0

Learn about the fraud network of North Korean IT workers exploiting fake profiles to infiltrate U.S. and Japanese tech companies.

B2B Business Email Compromise: A Sophisticated Scheme Exploiting Trusted Relationships B2B Business Email Compromise
  • Cyber Security

B2B Business Email Compromise: A Sophisticated Scheme Exploiting Trusted Relationships

Do Son March 5, 2025 0

Uncover the risks of B2B Business Email Compromise. Learn how sophisticated scams target trusted business relationships.

Russian Cybercriminals Impersonate EFF in Targeted Attack on Albion Online Players DPRK IT Workers, APT38 Crypto Forfeiture
  • Malware

Russian Cybercriminals Impersonate EFF in Targeted Attack on Albion Online Players

Do Son March 5, 2025 0

Uncover how Pyramid C2 is being used in a cybercriminal campaign targeting Albion Online players. Stay informed on cybersecurity.

Cisco Webex for BroadWorks Vulnerability Exposes User Credentials CVE-2024-20419 - Cisco Webex Vulnerability Cisco ISE DoS, CVE-2025-20152
  • Vulnerability

Cisco Webex for BroadWorks Vulnerability Exposes User Credentials

Do Son March 5, 2025 0

Discover the Cisco Webex vulnerability impacting user credentials in Release 45.2 and how to protect your data effectively.

CVE-2025-27507 (CVSS 9.0): ZITADEL Users at Risk of Account Takeover ZITADEL Vulnerability CVE-2026-29191 CVE-2025-27507 ZITADEL SSRF, Login UI Hijack
  • Vulnerability

CVE-2025-27507 (CVSS 9.0): ZITADEL Users at Risk of Account Takeover

Do Son March 5, 2025 0

Learn about CVE-2025-27507 vulnerabilities in ZITADEL's Admin API that could compromise user accounts and settings.
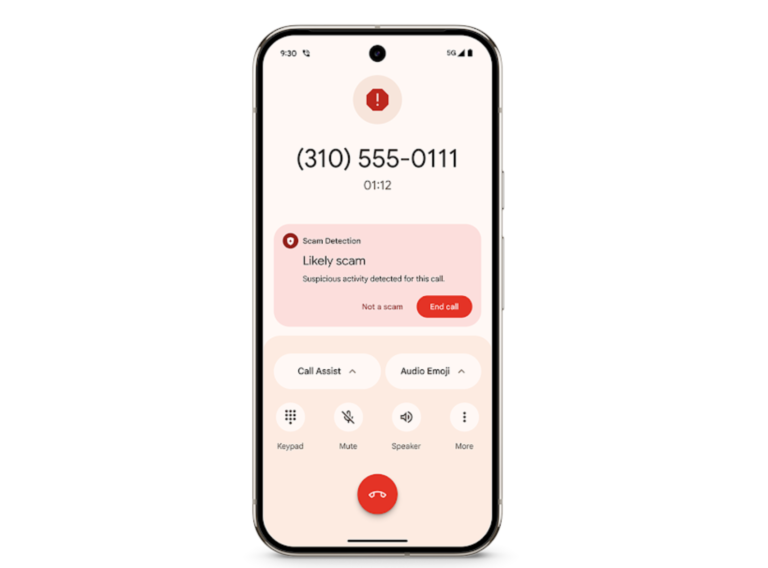
Privacy First: Google’s AI Detects Fraud, No Cloud Storage Google Phone Fraud Detection
  • Android
  • Technology

Privacy First: Google’s AI Detects Fraud, No Cloud Storage

Do Son March 5, 2025 0

Understand the innovations behind Fraud Detection on Google Phone. This AI feature protects users by analyzing calls locally.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17158CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.