Skip to content
September 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
HPE Insight Remote Support Hit with Critical Vulnerabilities, Urgent Patch Released CVE-2024-53676
  • Vulnerability

HPE Insight Remote Support Hit with Critical Vulnerabilities, Urgent Patch Released

Do Son November 27, 2024 0
Read More Read more about HPE Insight Remote Support Hit with Critical Vulnerabilities, Urgent Patch Released
Cybercrime as an Industry: A Deep Dive into the Organizational Structure of Chinese Cybercrime Chinese cybercrime
  • Cyber Security

Cybercrime as an Industry: A Deep Dive into the Organizational Structure of Chinese Cybercrime

Do Son November 27, 2024 0
Read More Read more about Cybercrime as an Industry: A Deep Dive into the Organizational Structure of Chinese Cybercrime
Jenkins Users Beware: Multiple Security Vulnerabilities Discovered Jenkins RCE vulnerabilities Jenkins plugin security flaws CVE-2024-47855
  • Vulnerability

Jenkins Users Beware: Multiple Security Vulnerabilities Discovered

Do Son November 27, 2024 0
Read More Read more about Jenkins Users Beware: Multiple Security Vulnerabilities Discovered
XorBot Botnet Resurfaces with Advanced Evasion and Exploits, Threatens IoT Devices XorBot botnet
  • Malware
  • Vulnerability

XorBot Botnet Resurfaces with Advanced Evasion and Exploits, Threatens IoT Devices

Do Son November 27, 2024 0
Read More Read more about XorBot Botnet Resurfaces with Advanced Evasion and Exploits, Threatens IoT Devices
Year-Long Supply Chain Attack: Malicious NPM Package Compromises Cryptocurrency Wallets NPM Supply Chain
  • Malware

Year-Long Supply Chain Attack: Malicious NPM Package Compromises Cryptocurrency Wallets

Do Son November 27, 2024 0
Read More Read more about Year-Long Supply Chain Attack: Malicious NPM Package Compromises Cryptocurrency Wallets
SMOKEDHAM Backdoor: UNC2465’s Stealth Weapon for Extortion and Ransomware Campaigns SMOKEDHAM backdoor
  • Cyber Security
  • Malware

SMOKEDHAM Backdoor: UNC2465’s Stealth Weapon for Extortion and Ransomware Campaigns

Do Son November 27, 2024 0
Read More Read more about SMOKEDHAM Backdoor: UNC2465’s Stealth Weapon for Extortion and Ransomware Campaigns
CVE-2024-11680 (CVSS 9.8): Critical ProjectSend Vulnerability Actively Exploited, PoC Published CVE-2024-11680
  • Vulnerability

CVE-2024-11680 (CVSS 9.8): Critical ProjectSend Vulnerability Actively Exploited, PoC Published

Do Son November 27, 2024 0
Read More Read more about CVE-2024-11680 (CVSS 9.8): Critical ProjectSend Vulnerability Actively Exploited, PoC Published
Cloudflare Logs Suffer Critical Failure, Losing 55% of User Data Cloudflare Containers Regional Placement Cloudflare Logs Lost
  • Technology

Cloudflare Logs Suffer Critical Failure, Losing 55% of User Data

Do Son November 27, 2024 0
Read More Read more about Cloudflare Logs Suffer Critical Failure, Losing 55% of User Data
ESET Unveils “Bootkitty”: The First UEFI Bootkit Targeting Linux Systems vulnerable UEFI shim bootloaders, Secure Boot bypass UEFI Secure Boot, Critical Vulnerability CVE-2025-3052
  • Linux
  • Malware

ESET Unveils “Bootkitty”: The First UEFI Bootkit Targeting Linux Systems

Do Son November 27, 2024 0
Read More Read more about ESET Unveils “Bootkitty”: The First UEFI Bootkit Targeting Linux Systems
Microsoft Clarifies: Your Word and Excel Data Isn’t Training Our AI Microsoft Word Training AI
  • Technology

Microsoft Clarifies: Your Word and Excel Data Isn’t Training Our AI

Do Son November 27, 2024 0
Read More Read more about Microsoft Clarifies: Your Word and Excel Data Isn’t Training Our AI
Intel Secures Nearly $8 Billion in CHIPS Act Funding to Boost US Semiconductor Production Intel Eric Demers GPU Chief Architect Intel, CHIPS Act Trump Intel, semiconductor investment Intel CHIPS Act
  • Technology

Intel Secures Nearly $8 Billion in CHIPS Act Funding to Boost US Semiconductor Production

Do Son November 27, 2024 0
Read More Read more about Intel Secures Nearly $8 Billion in CHIPS Act Funding to Boost US Semiconductor Production
Blue Yonder Grapples with Ransomware Attack, Disrupting Global Supply Chains Blue Yonder ransomware attack
  • Cyber Security

Blue Yonder Grapples with Ransomware Attack, Disrupting Global Supply Chains

Do Son November 26, 2024 0
Read More Read more about Blue Yonder Grapples with Ransomware Attack, Disrupting Global Supply Chains
19,000 Banned: Call of Duty: Black Ops 6’s AI Anti-Cheat in Action Call of Duty: Black Ops 6
  • Technology

19,000 Banned: Call of Duty: Black Ops 6’s AI Anti-Cheat in Action

Do Son November 26, 2024 0
Read More Read more about 19,000 Banned: Call of Duty: Black Ops 6’s AI Anti-Cheat in Action
CVE-2024-0130: NVIDIA Patches High-Severity Vulnerability in UFM Products NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability

CVE-2024-0130: NVIDIA Patches High-Severity Vulnerability in UFM Products

Do Son November 26, 2024 0
Read More Read more about CVE-2024-0130: NVIDIA Patches High-Severity Vulnerability in UFM Products
Operation Serengeti: Major Cybercrime Sweep Across Africa Nets 1,006 Suspects Operation Serengeti
  • Cyber Security

Operation Serengeti: Major Cybercrime Sweep Across Africa Nets 1,006 Suspects

Do Son November 26, 2024 0
Read More Read more about Operation Serengeti: Major Cybercrime Sweep Across Africa Nets 1,006 Suspects
macOS Vulnerability (CVE-2023-32428) Grants Root Access, PoC Published CVE-2023-32428 exploit
  • Vulnerability

macOS Vulnerability (CVE-2023-32428) Grants Root Access, PoC Published

Do Son November 26, 2024 0
Read More Read more about macOS Vulnerability (CVE-2023-32428) Grants Root Access, PoC Published
Unpatched NTLM Flaws Leave Microsoft Systems Vulnerable NTLM Privilege Escalation
  • Vulnerability

Unpatched NTLM Flaws Leave Microsoft Systems Vulnerable

Do Son November 26, 2024 0
Read More Read more about Unpatched NTLM Flaws Leave Microsoft Systems Vulnerable
CVE-2024-8114: GitLab Vulnerability Allows Privilege Escalation GitLab Security Update CVE-2025-7659 CVE-2024-5655 GitLab Vulnerabilities, XSS & Data Exposure
  • Vulnerability

CVE-2024-8114: GitLab Vulnerability Allows Privilege Escalation

Do Son November 26, 2024 0
Read More Read more about CVE-2024-8114: GitLab Vulnerability Allows Privilege Escalation
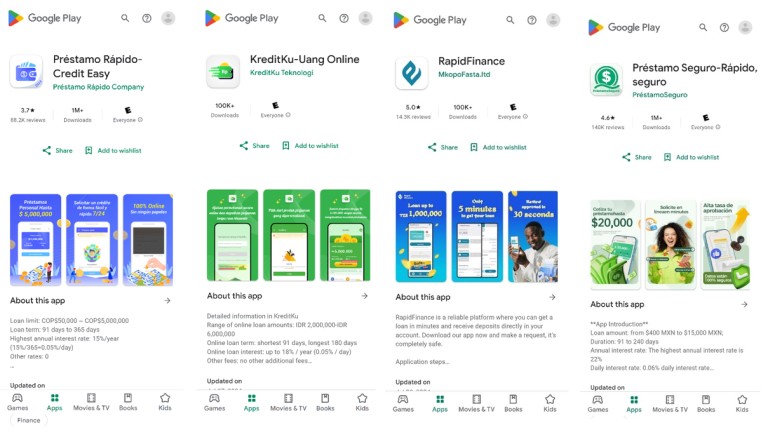
Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications SpyLoan
  • Android
  • Data Leak
  • Malware

Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications

Do Son November 26, 2024 0
Read More Read more about Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications
VMware Aria Operations Hit By Multiple Vulnerabilities CVE-2022-31702 - VMware Aria Operations
  • Vulnerability

VMware Aria Operations Hit By Multiple Vulnerabilities

Do Son November 26, 2024 0
Read More Read more about VMware Aria Operations Hit By Multiple Vulnerabilities
CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers Earth Estries APT group
  • Cyber Security
  • Malware
  • Vulnerability

CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers

Do Son November 26, 2024 0
Read More Read more about CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers
CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics CyberVolk Stealer
  • Cyber Security
  • Malware

CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics

Do Son November 26, 2024 0
Read More Read more about CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-85102CVSS 9.8
    Improper certificate trust validation during VPN negotiation in Check Point Quantum Security Gateway may allow an unauthenticated remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93616CVSS 9.8
    A directory traversal and file upload vulnerability allows an unauthenticated attacker to upload and execute arbitrary scripts on...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-100741CVSS 9.8
    Eval injection in the JScript event-script dispatcher in Progressive Robot Ltd's hMailServer, versions 6.0.0 through 6.3.3 on Windows,...
    📅 Updated: Sep 27, 2026
  • CVE-2026-94130CVSS 9.3
    Joomla Extension - joomlaboat.com - Unauthenticated SQL injection in YouTube Gallery extension < 5.7.3 - An SQL injection...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97161CVSS 9.2
    Joomla Extension - lomart.fr - Various path traversal / file access vectors in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-97163CVSS 10.0
    Joomla Extension - lomart.fr - Unauthenticated remote code installation in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-94132CVSS 9.5
    Joomla Extension - acymailing.com - Remote Code Execution vulnerability in mailbox action feature in AcyMailing Enterprise extension <...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97160CVSS 9.4
    Joomla Extension - lomart.fr - Authenticated, privileged PHP command injection in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-100835CVSS 9.1
    Contrast before 1.16.0 is susceptible to remote attestation relay attacks. Contrast accepted any TEE attestation report that verified...
    📅 Updated: Sep 27, 2026
  • CVE-2026-100721CVSS 9.5
    vm2 before 3.12.2 contains an authorization bypass in the NodeVM external-module resolver. When an embedder configures `require.external` with...
    📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.