Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Gemini Advanced Remembers: Google’s AI Gets a Memory Boost Gemini Advanced Remembers
  • Technology

Gemini Advanced Remembers: Google’s AI Gets a Memory Boost

Do Son February 14, 2025 0

Discover how Gemini Advanced remembers previous conversations for improved user experience and interaction with AI assistance.

“Country of Geniuses” by 2030? Anthropic CEO Amodei’s AI Warning AI pre-release vetting AI copyright law US UK FoundationMotion, AI Motion Understanding AI Deregulation, DOGE AI Self-Preservation, GPT-4o Country of Geniuses
  • Technology

“Country of Geniuses” by 2030? Anthropic CEO Amodei’s AI Warning

Do Son February 14, 2025 0

Explore the concept of a Country of Geniuses. AI advancements could reshape society by 2030, raising important security concerns.

AI Humanizers for SEO: Can They Improve Rankings? Yoshua Bengio AI sycophancy, reverse deception AI feedback AI chatbots, FTC investigation AI-generated content Trump AI Policy, AI Deregulation Military AI, DoD Funding Stargate Project AI Art Restoration
  • Technique

AI Humanizers for SEO: Can They Improve Rankings?

Do Son February 13, 2025 0
In this age of ever-changing technology in SEO, the rise of AI tools has changed the game...
Read More Read more about AI Humanizers for SEO: Can They Improve Rankings?
OBS Studio vs. Fedora: Open Source Legal Battle OBS Studio Fedora
  • Linux
  • Technology

OBS Studio vs. Fedora: Open Source Legal Battle

Do Son February 13, 2025 0

Explore the legal disputes surrounding OBS Studio Fedora and the implications of intellectual property in open-source projects.

Reddit Cashes In on AI: Google and OpenAI Pay $130M for User Data OpenAI Reddit data
  • Technology

Reddit Cashes In on AI: Google and OpenAI Pay $130M for User Data

Do Son February 13, 2025 0

Learn how Reddit's vast user-generated data, including OpenAI Reddit data, became essential for AI model training and monetization.

CVE-2025-1240: WinZip Vulnerability Opens Door to Remote Code Execution CVE-2024-8811 - CVE-2025-1240
  • Vulnerability

CVE-2025-1240: WinZip Vulnerability Opens Door to Remote Code Execution

Do Son February 13, 2025 0

Learn about CVE-2025-1240, a WinZip vulnerability that allows remote code execution through 7Z file parsing.

Palo Alto Firewall Flaw (CVE-2025-0108): Active Exploits in the Wild, PoC Released Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability

Palo Alto Firewall Flaw (CVE-2025-0108): Active Exploits in the Wild, PoC Released

Do Son February 13, 2025 0

A proof-of-concept (PoC) exploit for CVE-2025-0108 has been publicly released, making it easier for threat actors to target unpatched systems.

CVE-2025-1126: Critical Lexmark Print Management Client Bug Puts Systems at Risk CVE-2025-1126 Lexmark, Remote Code Execution
  • Vulnerability

CVE-2025-1126: Critical Lexmark Print Management Client Bug Puts Systems at Risk

Do Son February 13, 2025 0

Learn about CVE-2025-1126, a critical vulnerability in Lexmark Print Management Client that allows unauthorized access to systems.

New I2PRAT Malware: Advanced, Undetectable? Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

New I2PRAT Malware: Advanced, Undetectable?

Do Son February 13, 2025 0

Uncover the threat of I2PRAT malware, a sophisticated Remote Access Trojan targeting data security through I2P anonymity.

CVE-2024-32838 (CVSS 9.4): Critical SQL Injection Flaw Threatens Apache Fineract Users CVE-2024-32838 Apache Fineract IDOR, Core Banking Bypass
  • Vulnerability

CVE-2024-32838 (CVSS 9.4): Critical SQL Injection Flaw Threatens Apache Fineract Users

Do Son February 13, 2025 0

Learn about CVE-2024-32838, a critical vulnerability in Apache Fineract affecting financial institutions. Stay informed.
AMD Ryzen Master Utility Vulnerable to DLL Hijacking (CVE-2024-21966) CVE-2024-21966
  • Vulnerability

AMD Ryzen Master Utility Vulnerable to DLL Hijacking (CVE-2024-21966)

Do Son February 13, 2025 0

Understand CVE-2024-21966, a high-risk vulnerability in the AMD Ryzen Master Utility that allows potential code execution.

Hackers Can Take Over 30,000 WordPress Sites Due to Critical CleanTalk Security Flaw (CVE-2024-13365) CVE-2024-13365
  • Vulnerability

Hackers Can Take Over 30,000 WordPress Sites Due to Critical CleanTalk Security Flaw (CVE-2024-13365)

Do Son February 13, 2025 0

Learn about CVE-2024-13365, a critical vulnerability affecting WordPress that could compromise over 30,000 websites.
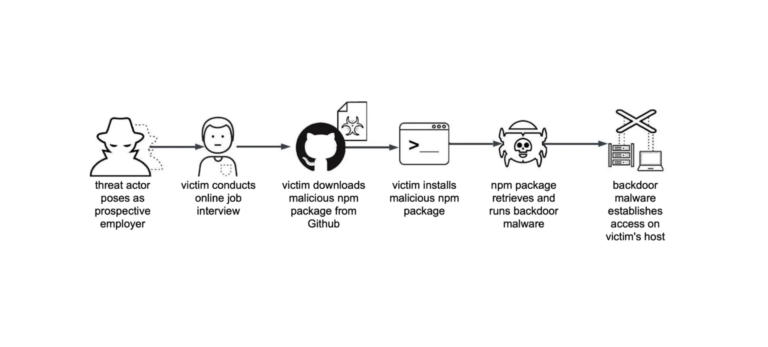
Lazarus Group’s Infostealer Malware Targets Developers in New Espionage Campaigns Lazarus Group’s Infostealer Malware
  • Malware

Lazarus Group’s Infostealer Malware Targets Developers in New Espionage Campaigns

Do Son February 13, 2025 0

Uncover the dangers of Lazarus Group’s Infostealer Malware targeting software developers and IT professionals with malicious scripts.

CVE-2025-23359: NVIDIA Container Toolkit Flaw Could Lead to Code Execution and Denial of Service CVE-2025-23359
  • Vulnerability

CVE-2025-23359: NVIDIA Container Toolkit Flaw Could Lead to Code Execution and Denial of Service

Do Son February 13, 2025 0

NVIDIA’s CVE-2025-23359 vulnerability poses serious threats. Discover the impact and security measures to protect your systems.

Russian Influence Operations Target German Elections Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security

Russian Influence Operations Target German Elections

Do Son February 13, 2025 0

Explore the Russian influence operations targeting the 2025 German elections. Discover their tactics and impact on democracy.

XSS Flaw in Apache Atlas (CVE-2024-46910) Puts Data Governance at Risk CVE-2024-46910 Apache Atlas Vulnerability Gremlin Code Injection
  • Vulnerability

XSS Flaw in Apache Atlas (CVE-2024-46910) Puts Data Governance at Risk

Do Son February 13, 2025 0

CVE-2024-46910 exposes a security flaw in Apache Atlas. Understand the implications for data governance and protection.

South Korean CSOs Under Cyberattack: 3-Year Study South Korean Cyberattack
  • Cyber Security

South Korean CSOs Under Cyberattack: 3-Year Study

Do Son February 13, 2025 0

Explore the impact of South Korean cyberattack threats on civil society organizations and their defenders in a detailed study.

How Satellite IoT Companies Are Solving Global Connectivity Challenges Open Sesame attack - CVE-2024-52324
  • Technique

How Satellite IoT Companies Are Solving Global Connectivity Challenges

Do Son February 13, 2025 0
With the advancements of smart homes and health wearables, many industries are going to change their  relationship...
Read More Read more about How Satellite IoT Companies Are Solving Global Connectivity Challenges
The Role of Laser Beam Shapers in Beam Shaping a
  • Technique

The Role of Laser Beam Shapers in Beam Shaping

Do Son February 13, 2025 0
Laser beam shaping is the critical process for various laser applications which involve shaping or transforming the...
Read More Read more about The Role of Laser Beam Shapers in Beam Shaping
5 Ways Micro Coils and Sensors Are Revolutionizing the Field of Medicine Medicine
  • Technique

5 Ways Micro Coils and Sensors Are Revolutionizing the Field of Medicine

Do Son February 13, 2025 0
Miniaturization has changed the fast-developing field of medical technology. Among the most significant developments are micro coils...
Read More Read more about 5 Ways Micro Coils and Sensors Are Revolutionizing the Field of Medicine
macOS Security Breach: CVE-2024-54531 PoC Published, Attackers Can Bypass KASLR CVE-2024-54531 PoC
  • Vulnerability

macOS Security Breach: CVE-2024-54531 PoC Published, Attackers Can Bypass KASLR

Do Son February 12, 2025 0

Researchers published a PoC exploit on GitHub, raising concerns about potential real-world attacks leveraging the CVE-2024-54531 flaw

OpenAI to Integrate o3 Model into GPT-5, Offering Free Access to All Users o3-Pro model AI Model, OpenAI ChatGPT malware - GPT-5 Model
  • Technology

OpenAI to Integrate o3 Model into GPT-5, Offering Free Access to All Users

Do Son February 12, 2025 0

Explore the advancements of the GPT-5 model, incorporating the o3 AI for efficient, context-driven responses across queries.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.