Analysis & PoC Exploits Released for Palo Alto Zero-Days – CVE-2024-0012 and CVE-2024-9474 Vulnerability Analysis & PoC Exploits Released for Palo Alto Zero-Days – CVE-2024-0012 and CVE-2024-9474 Do Son November 19, 2024 0 Read More Read more about Analysis & PoC Exploits Released for Palo Alto Zero-Days – CVE-2024-0012 and CVE-2024-9474
CVE-2024-21697: High Severity Flaw in Sourcetree Enables Remote Code Execution Vulnerability CVE-2024-21697: High Severity Flaw in Sourcetree Enables Remote Code Execution Do Son November 19, 2024 0 Read More Read more about CVE-2024-21697: High Severity Flaw in Sourcetree Enables Remote Code Execution
Google Chrome Patches High-Severity Flaw CVE-2024-11395 in Latest Stable Release Vulnerability Google Chrome Patches High-Severity Flaw CVE-2024-11395 in Latest Stable Release Do Son November 19, 2024 0 Read More Read more about Google Chrome Patches High-Severity Flaw CVE-2024-11395 in Latest Stable Release
CVE-2024-21287: Critical Zero-Day Exploited in Oracle Agile PLM Vulnerability CVE-2024-21287: Critical Zero-Day Exploited in Oracle Agile PLM Do Son November 19, 2024 0 Read More Read more about CVE-2024-21287: Critical Zero-Day Exploited in Oracle Agile PLM
Gabagool: A Sophisticated Phishing Kit Exploiting Cloudflare R2 Cyber Security Gabagool: A Sophisticated Phishing Kit Exploiting Cloudflare R2 Do Son November 19, 2024 0 Read More Read more about Gabagool: A Sophisticated Phishing Kit Exploiting Cloudflare R2
CVE-2024-47533 (CVSS 9.8): Cobbler Vulnerability Exposes Linux Servers to Compromise Vulnerability CVE-2024-47533 (CVSS 9.8): Cobbler Vulnerability Exposes Linux Servers to Compromise Do Son November 19, 2024 0 Read More Read more about CVE-2024-47533 (CVSS 9.8): Cobbler Vulnerability Exposes Linux Servers to Compromise
CVE-2024-42057: Exploited by Helldown Ransomware to Target Linux Malware Vulnerability CVE-2024-42057: Exploited by Helldown Ransomware to Target Linux Do Son November 19, 2024 0 Read More Read more about CVE-2024-42057: Exploited by Helldown Ransomware to Target Linux
Bitwarden Users Targeted in Malicious Facebook Ad Campaign Malware Bitwarden Users Targeted in Malicious Facebook Ad Campaign Do Son November 19, 2024 0 Read More Read more about Bitwarden Users Targeted in Malicious Facebook Ad Campaign
Wget Vulnerability (CVE-2024-10524) Opens Door to SSRF Attacks Vulnerability Wget Vulnerability (CVE-2024-10524) Opens Door to SSRF Attacks Do Son November 19, 2024 0 Read More Read more about Wget Vulnerability (CVE-2024-10524) Opens Door to SSRF Attacks
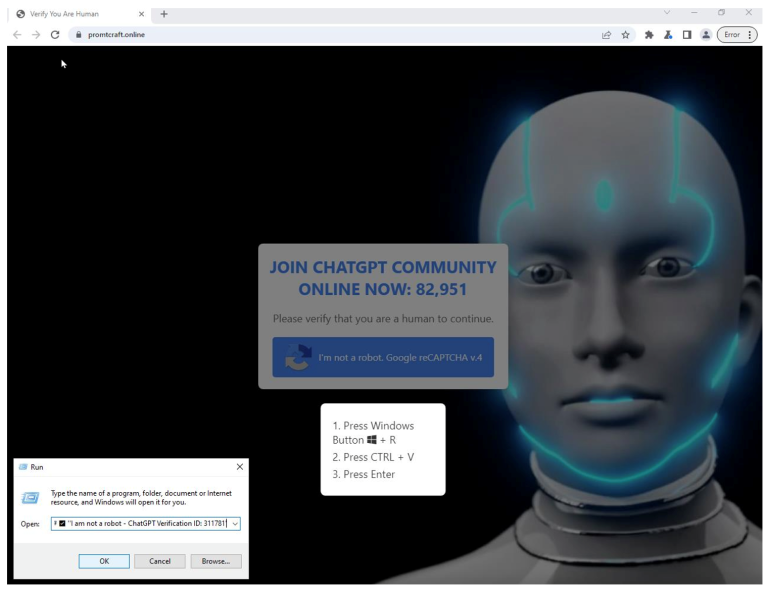
ClickFix: The Rising Threat of Clipboard-Based Social Engineering Malware ClickFix: The Rising Threat of Clipboard-Based Social Engineering Do Son November 19, 2024 0 Read More Read more about ClickFix: The Rising Threat of Clipboard-Based Social Engineering
CVE-2024-47208 & CVE-2024-48962: Apache OFBiz Exposed to Remote Code Execution Vulnerability CVE-2024-47208 & CVE-2024-48962: Apache OFBiz Exposed to Remote Code Execution Do Son November 19, 2024 0 Read More Read more about CVE-2024-47208 & CVE-2024-48962: Apache OFBiz Exposed to Remote Code Execution
DONOT APT Group Targets Pakistan’s Maritime and Defense Sectors in New Campaign Cyber Security DONOT APT Group Targets Pakistan’s Maritime and Defense Sectors in New Campaign Do Son November 19, 2024 0 Read More Read more about DONOT APT Group Targets Pakistan’s Maritime and Defense Sectors in New Campaign
CVE-2024-44308 and CVE-2024-44309: Apple Addresses Zero-Day Vulnerabilities Vulnerability CVE-2024-44308 and CVE-2024-44309: Apple Addresses Zero-Day Vulnerabilities Do Son November 19, 2024 0 Read More Read more about CVE-2024-44308 and CVE-2024-44309: Apple Addresses Zero-Day Vulnerabilities
CISA Warns of Actively Exploited Vulnerabilities in Kemp LoadMaster and Palo Alto Networks PAN-OS Vulnerability CISA Warns of Actively Exploited Vulnerabilities in Kemp LoadMaster and Palo Alto Networks PAN-OS Do Son November 19, 2024 0 Read More Read more about CISA Warns of Actively Exploited Vulnerabilities in Kemp LoadMaster and Palo Alto Networks PAN-OS
Phobos Ransomware Administrator Extradited to US to Face Charges Cyber Security Malware Phobos Ransomware Administrator Extradited to US to Face Charges Do Son November 19, 2024 0 Read More Read more about Phobos Ransomware Administrator Extradited to US to Face Charges
Phishing Alert: Government Impersonation Attacks Surge via DocuSign Cyber Security Phishing Alert: Government Impersonation Attacks Surge via DocuSign Do Son November 19, 2024 0 Read More Read more about Phishing Alert: Government Impersonation Attacks Surge via DocuSign
From CVE to PoC: A Collection Maps Windows Privilege Escalation Landscape Vulnerability From CVE to PoC: A Collection Maps Windows Privilege Escalation Landscape Do Son November 18, 2024 0 Read More Read more about From CVE to PoC: A Collection Maps Windows Privilege Escalation Landscape
CVE-2024-52308: GitHub CLI Vulnerability Could Allow Remote Code Execution Vulnerability CVE-2024-52308: GitHub CLI Vulnerability Could Allow Remote Code Execution Do Son November 18, 2024 0 Read More Read more about CVE-2024-52308: GitHub CLI Vulnerability Could Allow Remote Code Execution
LibreNMS Vulnerability (CVE-2024-51092): Mitigating the Risk of Server Compromise Vulnerability LibreNMS Vulnerability (CVE-2024-51092): Mitigating the Risk of Server Compromise Do Son November 18, 2024 0 Read More Read more about LibreNMS Vulnerability (CVE-2024-51092): Mitigating the Risk of Server Compromise
Actively Exploited VMware Vulnerabilities (CVE-2024-38812 & CVE-2024-38813) Threaten Virtualized Infrastructure Vulnerability Actively Exploited VMware Vulnerabilities (CVE-2024-38812 & CVE-2024-38813) Threaten Virtualized Infrastructure Do Son November 18, 2024 0 Read More Read more about Actively Exploited VMware Vulnerabilities (CVE-2024-38812 & CVE-2024-38813) Threaten Virtualized Infrastructure
North Korean Hackers Target Job Seekers with Malware-Laced Video Apps Cyber Security North Korean Hackers Target Job Seekers with Malware-Laced Video Apps Do Son November 18, 2024 0 Read More Read more about North Korean Hackers Target Job Seekers with Malware-Laced Video Apps
Trio of Apache Tomcat Flaws Disclosed: Authentication Bypass, HTTP/2 Request Mix-Up, and XSS Flaw Vulnerability Trio of Apache Tomcat Flaws Disclosed: Authentication Bypass, HTTP/2 Request Mix-Up, and XSS Flaw Do Son November 18, 2024 0 Read More Read more about Trio of Apache Tomcat Flaws Disclosed: Authentication Bypass, HTTP/2 Request Mix-Up, and XSS Flaw

 Do Son