Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2024-56404 (CVSS 9.9): Critical Vulnerability Discovered in One Identity Manager Ollama Heap Leak CVE-2026-5757 Anritsu Vulnerability Authentication Bypass Gootloader Malware Malformed ZIP Evasion Blender Malware, StealC V2 Lectora, XSS CVE-2025-9125 HFS RCE, Template Injection Arch Linux Malware, CHAOS RAT CVE-2024-56404 - CVE-2024-39327 CVE-2025-2538
  • Vulnerability

CVE-2024-56404 (CVSS 9.9): Critical Vulnerability Discovered in One Identity Manager

Do Son January 27, 2025 0

Learn about the newly discovered security vulnerability (CVE-2024-56404) in One Identity Manager and how it puts organizations at risk.

Akira Ransomware Adapts to Target Linux and VMware ESXi Servers Akira RaaS
  • Malware

Akira Ransomware Adapts to Target Linux and VMware ESXi Servers

Do Son January 27, 2025 0

Discover the rise of Akira, a highly active Ransomware-as-a-Service (RaaS) group targeting organizations worldwide.
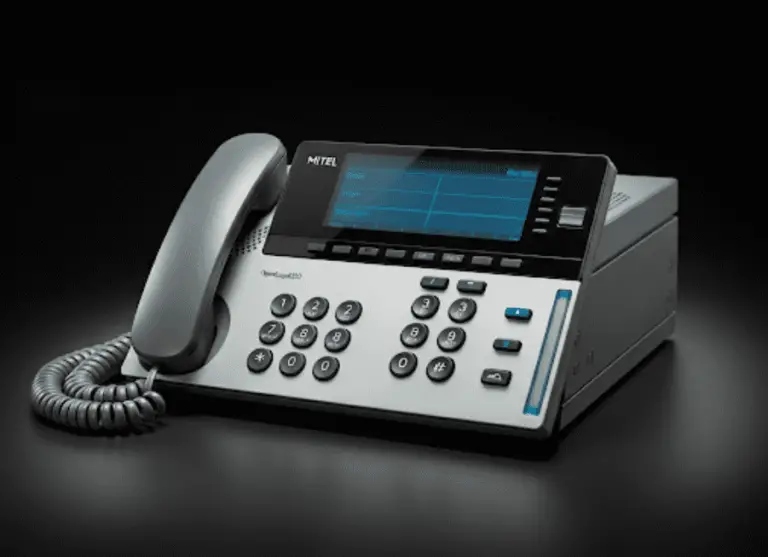
CVE-2025-23093 & CVE-2025-23094: Mitel OpenScape Users Urged to Update Now CVE-2025-23093 & CVE-2025-23094
  • Vulnerability

CVE-2025-23093 & CVE-2025-23094: Mitel OpenScape Users Urged to Update Now

Do Son January 27, 2025 0

Mitel's urgent security advisory warns of high-severity vulnerabilities affecting their OpenScape 4000 platforms. Learn about CVE-2025-23093 and CVE-2025-23094.

Silent Lynx APT Group: A New Espionage Threat Targeting Central Asia injection
  • Cyber Security

Silent Lynx APT Group: A New Espionage Threat Targeting Central Asia

Do Son January 27, 2025 0

Get insights into Silent Lynx: Discover the tactics and targets of this newly identified threat group operating in Central Asia.

North Korea’s Andariel Group Deploys New RID Hijacking Technique for Stealthy Attacks RID Hijacking Technique
  • Cyber Security

North Korea’s Andariel Group Deploys New RID Hijacking Technique for Stealthy Attacks

Do Son January 27, 2025 0

Uncover the sophisticated RID Hijacking technique used by the Andariel threat group. Learn how this technique allows attackers to escalate privileges during breaches.

CVE-2024-55573 & CVE-2024-53923: Centreon Hit by Critical SQL Injection Flaws CVE-2024-55573 & CVE-2024-53923 Centreon AWIE Vulnerabilities CVE-2025-15029
  • Vulnerability

CVE-2024-55573 & CVE-2024-53923: Centreon Hit by Critical SQL Injection Flaws

Do Son January 27, 2025 0

Protect your Centreon Web installation from critical SQL injection vulnerabilities. Learn how to apply urgent security updates to fix CVE-2024-53923 and CVE-2024-55573.

Cellular Security Compromised: 119 Vulnerabilities Discovered Across LTE and 5G 5G Vulnerabilities
  • Vulnerability

Cellular Security Compromised: 119 Vulnerabilities Discovered Across LTE and 5G

Do Son January 27, 2025 0

Discover the alarming findings of a research study on LTE and 5G vulnerabilities. Uncover the security flaws that put cellular networks at risk.

New Phishing Trend: Generic Pages Impersonate Any Brand Generic Phishing Pages
  • Cyber Security

New Phishing Trend: Generic Pages Impersonate Any Brand

Do Son January 27, 2025 0

Beware of generic phishing pages that adapt to target victims. Learn how these pages impersonate brands and trick users into surrendering sensitive credentials.

5 Common Reasons Email Bounces (and How to Resolve Them) Img_2025_01_28_08_23_40
  • Technique

5 Common Reasons Email Bounces (and How to Resolve Them)

Do Son January 27, 2025 0
When an email bounces, it means the recipient’s server rejects it. It generally indicates delivery issues. Have...
Read More Read more about 5 Common Reasons Email Bounces (and How to Resolve Them)
CVE-2025-24085: Apple Patches Actively Exploited Zero-Day Vulnerability Apple Background Security CVE-2026-20643 Apple Background Security Improvement Apple Backdoor Apple Lawsuit, Data Exfiltration CVE-2024-44131 - CVE-2025-24118 PoC
  • Vulnerability

CVE-2025-24085: Apple Patches Actively Exploited Zero-Day Vulnerability

Do Son January 27, 2025 0

Apple addresses a critical zero-day vulnerability (CVE-2025-24085) that allows malicious apps to exploit iPhones. Get the details on the emergency security updates from Apple.

How to Choose the Best Home Security System for Your Airbnb woman-8656655_1280
  • Technique

How to Choose the Best Home Security System for Your Airbnb

Do Son January 27, 2025 0
Running an Airbnb comes with plenty of responsibilities, and ensuring the safety of both your property and...
Read More Read more about How to Choose the Best Home Security System for Your Airbnb
Apache Solr Vulnerabilities CVE-2024-52012 and CVE-2025-24814 Expose Systems to File Write and Code Execution Risks Apache Solr default credentials CVE-2026-44825 workaround CVE-2025-24814 & CVE-2025-24814
  • Vulnerability

Apache Solr Vulnerabilities CVE-2024-52012 and CVE-2025-24814 Expose Systems to File Write and Code Execution Risks

Do Son January 27, 2025 0

Discover the security update for Apache Solr addressing the vulnerabilities CVE-2024-52012 and CVE-2025-24814. Ensure the safety of your search platform.

PoC for 7-Zip CVE-2025-0411 Lets Attackers Bypass MotW and Run Malicious Code CVE-2025-0411 PoC exploit - Homoglyph Attacks
  • Vulnerability

PoC for 7-Zip CVE-2025-0411 Lets Attackers Bypass MotW and Run Malicious Code

Do Son January 26, 2025 0

Security researcher Dhmos Funk released a PoC exploit for CVE-2025-0411 (CVSS 7.0), a high-severity vulnerability in the 7-Zip file archiver

Lumma Stealer MaaS: Clipboard Hijacking and LOLBins Used in Latest Campaign Lumma Stealer model
  • Malware

Lumma Stealer MaaS: Clipboard Hijacking and LOLBins Used in Latest Campaign

Do Son January 26, 2025 0

Stay informed about the latest malware campaign leveraging the Lumma Stealer model. Learn how social engineering techniques are used to bypass traditional security defenses.

Lazarus Group Deploys Electron-Based Malware to Target Cryptocurrency Enthusiasts Lazarus Group Electron Malware
  • Cyber Security
  • Malware

Lazarus Group Deploys Electron-Based Malware to Target Cryptocurrency Enthusiasts

Do Son January 26, 2025 0

Learn about Lazarus Group's latest attack targeting cryptocurrency professionals. Discover how they weaponized a legitimate open-source project to steal sensitive information.

Podman and Buildah Vulnerable to Container Breakout – CVE-2024-11218 CVE-2024-11218
  • Vulnerability

Podman and Buildah Vulnerable to Container Breakout – CVE-2024-11218

Do Son January 26, 2025 0

Discover the high-severity vulnerability CVE-2024-11218 in Podman and Buildah. Learn how attackers can break out of containers and access sensitive information on the host system.

CVE-2024-52975 (CVSS 9.0): Fleet Server Update Patches Critical Information Exposure Vulnerability CVE-2024-52975
  • Vulnerability

CVE-2024-52975 (CVSS 9.0): Fleet Server Update Patches Critical Information Exposure Vulnerability

Do Son January 26, 2025 0

Critical security update for Elastic Fleet Server - CVE-2024-52975. Protect your sensitive information and prevent data breaches.

Zyxel Vulnerability Exploited by Helldown Ransomware Group Helldown ransomware group
  • Malware
  • Vulnerability

Zyxel Vulnerability Exploited by Helldown Ransomware Group

Do Son January 26, 2025 0

Learn about the recent campaign by Helldown ransomware group targeting Zyxel devices and the vulnerabilities exploited.

Researchers Expose Critical Isolation Vulnerability in Intel Trust Domain Extensions (TDX) Intel Trust Domain Extensions Vulnerability
  • Vulnerability

Researchers Expose Critical Isolation Vulnerability in Intel Trust Domain Extensions (TDX)

Do Son January 26, 2025 0

Uncover the vulnerability in Intel's Trust Domain Extensions (TDX) and its impact on secure virtualized environments. Learn how side-channel attacks compromise core isolation and expose sensitive information.

Sophisticated J-Magic Backdoor Evades Detection on Juniper Routers J-Magic backdoor campaign
  • Malware

Sophisticated J-Magic Backdoor Evades Detection on Juniper Routers

Do Son January 26, 2025 0

Learn about the J-Magic backdoor campaign targeting Juniper routers. Discover how attackers exploit vulnerabilities to gain long-term access and control.

Palo Alto Networks Firewalls Exposed: BootHole and Other Critical Flaws Uncovered BootHole Vulnerability
  • Vulnerability

Palo Alto Networks Firewalls Exposed: BootHole and Other Critical Flaws Uncovered

Do Son January 26, 2025 0

Eclypsium researchers expose critical vulnerabilities in Palo Alto Networks firewalls, including the BootHole vulnerability. Stay informed and protect your systems.

Subaru’s STARLINK Vulnerability: How Hackers Could Track and Control Vehicles Subaru STARLINK Vulnerability
  • Vulnerability

Subaru’s STARLINK Vulnerability: How Hackers Could Track and Control Vehicles

Do Son January 26, 2025 0

Discover the critical vulnerability in Subaru STARLINK connected vehicle service that allows remote tracking and control of vehicles.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61949CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Bookly Bookly bookly-responsive-appointment-booking-tool allows...
    📅 Updated: Nov 10, 2026
  • CVE-2026-13312CVSS 9.9
    A vulnerability that could allow an attacker to compromise a system.
    📅 Updated: Nov 10, 2026
  • CVE-2026-72868CVSS 9.9
    Dokploy is a free, self-hostable Platform as a Service (PaaS). Prior to 0.29.13, apps/dokploy/server/api/routers/destination.ts interpolates the accessKey, secretAccessKey,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-6715CVSS 9.8
    IBM Concert 1.0 through 3.0.1.1 allows an attacker can supply crafted input that is incorporated into an operating...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17403CVSS 9.0
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to gain full...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17402CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 10, 2026
  • CVE-2026-17392CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to gain...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.