Skip to content
October 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2024-11680 (CVSS 9.8): Critical ProjectSend Vulnerability Actively Exploited, PoC Published CVE-2024-11680
  • Vulnerability

CVE-2024-11680 (CVSS 9.8): Critical ProjectSend Vulnerability Actively Exploited, PoC Published

Do Son November 27, 2024 0
Read More Read more about CVE-2024-11680 (CVSS 9.8): Critical ProjectSend Vulnerability Actively Exploited, PoC Published
Cloudflare Logs Suffer Critical Failure, Losing 55% of User Data Cloudflare Containers Regional Placement Cloudflare Logs Lost
  • Technology

Cloudflare Logs Suffer Critical Failure, Losing 55% of User Data

Do Son November 27, 2024 0
Read More Read more about Cloudflare Logs Suffer Critical Failure, Losing 55% of User Data
ESET Unveils “Bootkitty”: The First UEFI Bootkit Targeting Linux Systems vulnerable UEFI shim bootloaders, Secure Boot bypass UEFI Secure Boot, Critical Vulnerability CVE-2025-3052
  • Linux
  • Malware

ESET Unveils “Bootkitty”: The First UEFI Bootkit Targeting Linux Systems

Do Son November 27, 2024 0
Read More Read more about ESET Unveils “Bootkitty”: The First UEFI Bootkit Targeting Linux Systems
Microsoft Clarifies: Your Word and Excel Data Isn’t Training Our AI Microsoft Word Training AI
  • Technology

Microsoft Clarifies: Your Word and Excel Data Isn’t Training Our AI

Do Son November 27, 2024 0
Read More Read more about Microsoft Clarifies: Your Word and Excel Data Isn’t Training Our AI
Intel Secures Nearly $8 Billion in CHIPS Act Funding to Boost US Semiconductor Production Intel Eric Demers GPU Chief Architect Intel, CHIPS Act Trump Intel, semiconductor investment Intel CHIPS Act
  • Technology

Intel Secures Nearly $8 Billion in CHIPS Act Funding to Boost US Semiconductor Production

Do Son November 27, 2024 0
Read More Read more about Intel Secures Nearly $8 Billion in CHIPS Act Funding to Boost US Semiconductor Production
Blue Yonder Grapples with Ransomware Attack, Disrupting Global Supply Chains Blue Yonder ransomware attack
  • Cyber Security

Blue Yonder Grapples with Ransomware Attack, Disrupting Global Supply Chains

Do Son November 26, 2024 0
Read More Read more about Blue Yonder Grapples with Ransomware Attack, Disrupting Global Supply Chains
19,000 Banned: Call of Duty: Black Ops 6’s AI Anti-Cheat in Action Call of Duty: Black Ops 6
  • Technology

19,000 Banned: Call of Duty: Black Ops 6’s AI Anti-Cheat in Action

Do Son November 26, 2024 0
Read More Read more about 19,000 Banned: Call of Duty: Black Ops 6’s AI Anti-Cheat in Action
CVE-2024-0130: NVIDIA Patches High-Severity Vulnerability in UFM Products NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability

CVE-2024-0130: NVIDIA Patches High-Severity Vulnerability in UFM Products

Do Son November 26, 2024 0
Read More Read more about CVE-2024-0130: NVIDIA Patches High-Severity Vulnerability in UFM Products
Operation Serengeti: Major Cybercrime Sweep Across Africa Nets 1,006 Suspects Operation Serengeti
  • Cyber Security

Operation Serengeti: Major Cybercrime Sweep Across Africa Nets 1,006 Suspects

Do Son November 26, 2024 0
Read More Read more about Operation Serengeti: Major Cybercrime Sweep Across Africa Nets 1,006 Suspects
macOS Vulnerability (CVE-2023-32428) Grants Root Access, PoC Published CVE-2023-32428 exploit
  • Vulnerability

macOS Vulnerability (CVE-2023-32428) Grants Root Access, PoC Published

Do Son November 26, 2024 0
Read More Read more about macOS Vulnerability (CVE-2023-32428) Grants Root Access, PoC Published
Unpatched NTLM Flaws Leave Microsoft Systems Vulnerable NTLM Privilege Escalation
  • Vulnerability

Unpatched NTLM Flaws Leave Microsoft Systems Vulnerable

Do Son November 26, 2024 0
Read More Read more about Unpatched NTLM Flaws Leave Microsoft Systems Vulnerable
CVE-2024-8114: GitLab Vulnerability Allows Privilege Escalation GitLab Security Update CVE-2025-7659 CVE-2024-5655 GitLab Vulnerabilities, XSS & Data Exposure
  • Vulnerability

CVE-2024-8114: GitLab Vulnerability Allows Privilege Escalation

Do Son November 26, 2024 0
Read More Read more about CVE-2024-8114: GitLab Vulnerability Allows Privilege Escalation
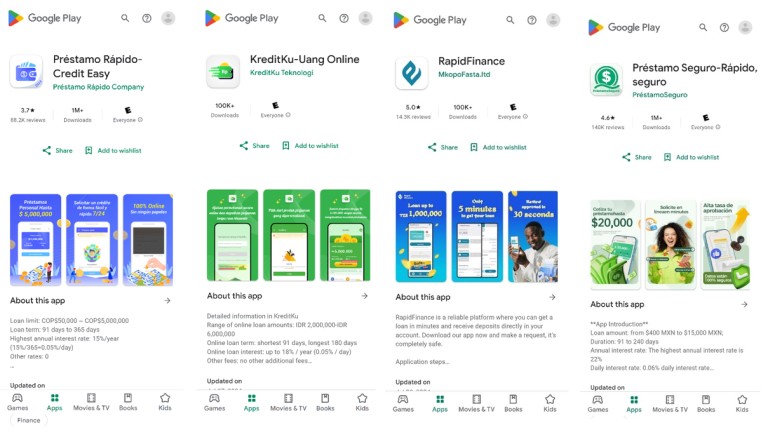
Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications SpyLoan
  • Android
  • Data Leak
  • Malware

Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications

Do Son November 26, 2024 0
Read More Read more about Privacy and Financial Security at Risk: McAfee Labs Warns of SpyLoan Applications
VMware Aria Operations Hit By Multiple Vulnerabilities CVE-2022-31702 - VMware Aria Operations
  • Vulnerability

VMware Aria Operations Hit By Multiple Vulnerabilities

Do Son November 26, 2024 0
Read More Read more about VMware Aria Operations Hit By Multiple Vulnerabilities
CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers Earth Estries APT group
  • Cyber Security
  • Malware
  • Vulnerability

CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers

Do Son November 26, 2024 0
Read More Read more about CVE-2024-21887 and More: How Earth Estries APT Group Exploits VPNs & Servers
CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics CyberVolk Stealer
  • Cyber Security
  • Malware

CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics

Do Son November 26, 2024 0
Read More Read more about CyberVolk: The Hacktivist Collective Blurring Lines Between Activism, Ransomware, and Geopolitics
CVE-2024-41779 (CVSS 9.8): IBM Rhapsody Model Manager Vulnerability Puts Systems at Risk CVE-2024-41779 - CVE-2025-0159 IBM HashiCorp Acquisition
  • Vulnerability

CVE-2024-41779 (CVSS 9.8): IBM Rhapsody Model Manager Vulnerability Puts Systems at Risk

Do Son November 26, 2024 0
Read More Read more about CVE-2024-41779 (CVSS 9.8): IBM Rhapsody Model Manager Vulnerability Puts Systems at Risk
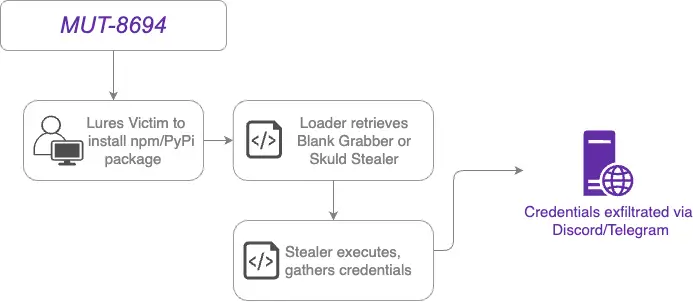
Cybersecurity Alert: MUT-8694 Supply Chain Attack Targets npm and PyPI Ecosystems MUT-8694 threat actor
  • Cyber Security
  • Malware

Cybersecurity Alert: MUT-8694 Supply Chain Attack Targets npm and PyPI Ecosystems

Do Son November 26, 2024 0
Read More Read more about Cybersecurity Alert: MUT-8694 Supply Chain Attack Targets npm and PyPI Ecosystems
Keycloak Patches Multiple Vulnerabilities in Latest Update Keycloak vulnerabilities Keycloak Security MFA Bypass
  • Vulnerability

Keycloak Patches Multiple Vulnerabilities in Latest Update

Do Son November 26, 2024 0
Read More Read more about Keycloak Patches Multiple Vulnerabilities in Latest Update
Kansas City Man Indicted for Hacking into Nonprofit and Health Club NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cyber Security

Kansas City Man Indicted for Hacking into Nonprofit and Health Club

Do Son November 26, 2024 0
Read More Read more about Kansas City Man Indicted for Hacking into Nonprofit and Health Club
Palo Alto Networks Warns of GlobalProtect App Flaw with Public Exploit Code (CVE-2024-5921) CVE-2024-5921 - CVE-2025-0103 CVE-2025-0110 PoC
  • Vulnerability

Palo Alto Networks Warns of GlobalProtect App Flaw with Public Exploit Code (CVE-2024-5921)

Do Son November 25, 2024 0
Read More Read more about Palo Alto Networks Warns of GlobalProtect App Flaw with Public Exploit Code (CVE-2024-5921)
PHP Patches Multi Flaws, Including CVE-2024-8932 (CVSS 9.8), Urges Immediate Update PHP Vulnerabilities, SQLi DoS CVE-2024-8932 & CVE-2024-8929
  • Vulnerability

PHP Patches Multi Flaws, Including CVE-2024-8932 (CVSS 9.8), Urges Immediate Update

Do Son November 25, 2024 0
Read More Read more about PHP Patches Multi Flaws, Including CVE-2024-8932 (CVSS 9.8), Urges Immediate Update
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-93836CVSS 7.2
    The WPC Product Bundles for WooCommerce plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the \'qty\'...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-21589CVSS 9.3
    This is a vulnerability in Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-61500CVSS 9.3
    Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-107459CVSS 9.3
    The SecuShare Pro developed by Openfind has an OS Command Injection vulnerability. Unauthenticated remote attackers can inject arbitrary...
    📅 Updated: Oct 8, 2026
  • CVE-2026-14990CVSS 9.3
    IBM DataPower Gateway 10.6.0.0 through 10.6.0.10 is vulnerable to cross-site scripting. This vulnerability allows an unauthenticated user to embed...
    📅 Updated: Oct 8, 2026
  • CVE-2026-14991CVSS 9.8
    IBM DataPower Gateway 10.5.0.0 through 10.5.0.22, 10.6.1 through 10.6.6, 10.6.0.0 through 10.6.0.10, and 11.0.0.0 through 11.0.0.2 is vulnerable...
    📅 Updated: Oct 8, 2026
  • CVE-2026-17635CVSS 9.1
    IBM Financial Transaction Manager (FTM) for RedHat OpenShift could allow a remote attacker to perform unauthorized actions due...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102106CVSS 9.1
    Improper authentication in a Kiteworks Email Protection Gateway administrative service. An administrative service in Kiteworks Email Protection Gateway...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102105CVSS 9.1
    Kiteworks Email Protection Gateway before version 9.5.0 is vulnerable to Server-Side Request Forgery (SSRF). A server-side request forgery...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102104CVSS 9.1
    Kiteworks Email Protection Gateway before version 9.5.0 is vulnerable to Server-Side Request Forgery (SSRF). A server-side request forgery...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102103CVSS 9.1
    Kiteworks Email Protection Gateway before version 9.5.0 is vulnerable to Server-Side Request Forgery (SSRF). A server-side request forgery...
    📅 Updated: Oct 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.