Critical Vulnerabilities in QNAP Notes Station 3: Update Now to Protect Your Data Vulnerability Critical Vulnerabilities in QNAP Notes Station 3: Update Now to Protect Your Data Do Son November 25, 2024 0 Read More Read more about Critical Vulnerabilities in QNAP Notes Station 3: Update Now to Protect Your Data
CVE-2024-10542 & CVE-2024-10781: Critical WordPress Plugin Flaw Exposes 200,000 Sites Vulnerability CVE-2024-10542 & CVE-2024-10781: Critical WordPress Plugin Flaw Exposes 200,000 Sites Do Son November 25, 2024 0 Read More Read more about CVE-2024-10542 & CVE-2024-10781: Critical WordPress Plugin Flaw Exposes 200,000 Sites
Infostealers VietCredCare and DuckTail Fuel Facebook Business Account Exploitation Cyber Security Infostealers VietCredCare and DuckTail Fuel Facebook Business Account Exploitation Do Son November 25, 2024 0 Read More Read more about Infostealers VietCredCare and DuckTail Fuel Facebook Business Account Exploitation
North Korean and Chinese Threat Actors Target Crypto, Aerospace, and Government Agencies Cyber Security North Korean and Chinese Threat Actors Target Crypto, Aerospace, and Government Agencies Do Son November 25, 2024 0 Read More Read more about North Korean and Chinese Threat Actors Target Crypto, Aerospace, and Government Agencies
CVE-2023-28461 (CVSS 9.8): Critical Array Networks Vulnerability Added to KEV Catalog Vulnerability CVE-2023-28461 (CVSS 9.8): Critical Array Networks Vulnerability Added to KEV Catalog Do Son November 25, 2024 0 Read More Read more about CVE-2023-28461 (CVSS 9.8): Critical Array Networks Vulnerability Added to KEV Catalog
Lazarus Group Exploits xattr with “RustyAttr” to Evade Detection Malware Lazarus Group Exploits xattr with “RustyAttr” to Evade Detection Do Son November 25, 2024 0 Read More Read more about Lazarus Group Exploits xattr with “RustyAttr” to Evade Detection
7 Android & Pixel Vulnerabilities Exposed: Researcher Publishes PoC Exploits Vulnerability 7 Android & Pixel Vulnerabilities Exposed: Researcher Publishes PoC Exploits Do Son November 25, 2024 0 Read More Read more about 7 Android & Pixel Vulnerabilities Exposed: Researcher Publishes PoC Exploits
Malicious npm Packages Exploiting Typosquatting to Inject SSH Backdoors Malware Malicious npm Packages Exploiting Typosquatting to Inject SSH Backdoors Do Son November 25, 2024 0 Read More Read more about Malicious npm Packages Exploiting Typosquatting to Inject SSH Backdoors
Unveiling the “Nearest Neighbor Attack”: A Russian APT’s Covert Tactic to Weaponize Wi-Fi Cyber Security Unveiling the “Nearest Neighbor Attack”: A Russian APT’s Covert Tactic to Weaponize Wi-Fi Do Son November 25, 2024 0 Read More Read more about Unveiling the “Nearest Neighbor Attack”: A Russian APT’s Covert Tactic to Weaponize Wi-Fi
CVE-2024-48860 (CVSS 9.5): Critical Flaw in QNAP QuRouter, Immediate Update Recommended Vulnerability CVE-2024-48860 (CVSS 9.5): Critical Flaw in QNAP QuRouter, Immediate Update Recommended Do Son November 25, 2024 0 Read More Read more about CVE-2024-48860 (CVSS 9.5): Critical Flaw in QNAP QuRouter, Immediate Update Recommended
CVE-2024-11477: 7-Zip Vulnerability Allows Remote Code Execution, Update Now! Vulnerability CVE-2024-11477: 7-Zip Vulnerability Allows Remote Code Execution, Update Now! Do Son November 24, 2024 0 Read More Read more about CVE-2024-11477: 7-Zip Vulnerability Allows Remote Code Execution, Update Now!
Google Docs and Weebly Weaponized in New Phishing Scheme Cyber Security Google Docs and Weebly Weaponized in New Phishing Scheme Do Son November 24, 2024 0 Read More Read more about Google Docs and Weebly Weaponized in New Phishing Scheme
Russia-Linked TAG-110 Launches Cyberespionage Campaign Across Asia and Europe Cyber Security Malware Russia-Linked TAG-110 Launches Cyberespionage Campaign Across Asia and Europe Do Son November 24, 2024 0 Read More Read more about Russia-Linked TAG-110 Launches Cyberespionage Campaign Across Asia and Europe
WolfsBane: Gelsemium APT Group’s Linux Backdoor Debut Cyber Security Malware WolfsBane: Gelsemium APT Group’s Linux Backdoor Debut Do Son November 24, 2024 0 Read More Read more about WolfsBane: Gelsemium APT Group’s Linux Backdoor Debut
Asyncshell: The Evolution of APT-K-47’s Cyber Arsenal Cyber Security Malware Asyncshell: The Evolution of APT-K-47’s Cyber Arsenal Do Son November 24, 2024 0 Read More Read more about Asyncshell: The Evolution of APT-K-47’s Cyber Arsenal
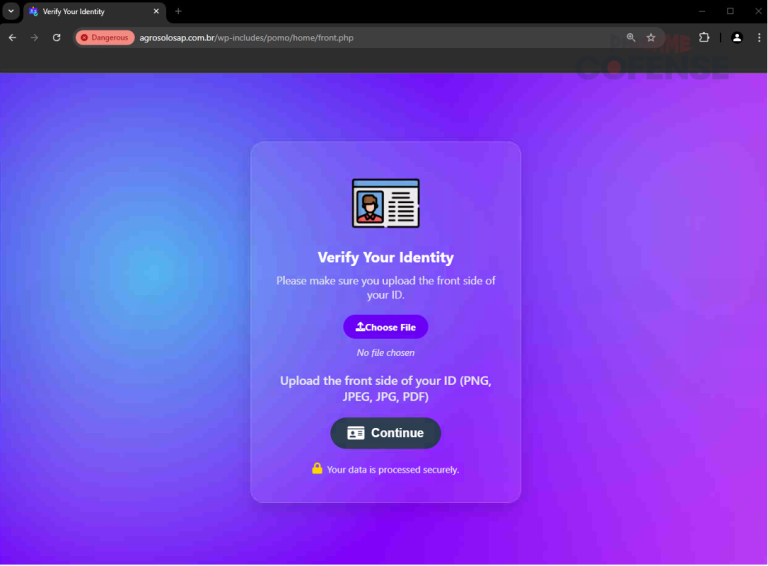
Government IDs and Facial Recognition: A New Phishing Threat Cyber Security Data Leak Government IDs and Facial Recognition: A New Phishing Threat Do Son November 24, 2024 0 Read More Read more about Government IDs and Facial Recognition: A New Phishing Threat
PROSPERO & Proton66: Unmasking the Bulletproof Hosting Connection Cyber Security Malware PROSPERO & Proton66: Unmasking the Bulletproof Hosting Connection Do Son November 24, 2024 0 Read More Read more about PROSPERO & Proton66: Unmasking the Bulletproof Hosting Connection
Fake Identities, Real Profits: Exposing North Korea’s IT Front Companies Cyber Security Fake Identities, Real Profits: Exposing North Korea’s IT Front Companies Do Son November 24, 2024 0 Read More Read more about Fake Identities, Real Profits: Exposing North Korea’s IT Front Companies
Fortune 1000’s Hidden Threat: 30,000 Exposed APIs and 100,000 API Vulnerabilities Unveiled Data Leak Vulnerability Fortune 1000’s Hidden Threat: 30,000 Exposed APIs and 100,000 API Vulnerabilities Unveiled Do Son November 24, 2024 0 Read More Read more about Fortune 1000’s Hidden Threat: 30,000 Exposed APIs and 100,000 API Vulnerabilities Unveiled
Kling AI Announces Black Friday Mega Deals with Upgraded Features for Content Creators Technique Kling AI Announces Black Friday Mega Deals with Upgraded Features for Content Creators Do Son November 24, 2024 0 Read More Read more about Kling AI Announces Black Friday Mega Deals with Upgraded Features for Content Creators
CVE-2024-9511 (CVSS 9.8): Critical Flaw in FluentSMTP Plugin Exposes Over 300,000 WordPress Sites to Potential Takeover Vulnerability CVE-2024-9511 (CVSS 9.8): Critical Flaw in FluentSMTP Plugin Exposes Over 300,000 WordPress Sites to Potential Takeover Do Son November 23, 2024 0 Read More Read more about CVE-2024-9511 (CVSS 9.8): Critical Flaw in FluentSMTP Plugin Exposes Over 300,000 WordPress Sites to Potential Takeover
Python NodeStealer Evolution: Targeting Facebook Ads Manager and Credit Cards Malware Python NodeStealer Evolution: Targeting Facebook Ads Manager and Credit Cards Do Son November 23, 2024 0 Read More Read more about Python NodeStealer Evolution: Targeting Facebook Ads Manager and Credit Cards

 Do Son