Skip to content
October 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Malicious Update in Python Crypto Library Targets Private Keys via Telegram Everon OCPP Vulnerability CVE-2026-26288 ASUSTOR ADM Vulnerability CVE-2026-24936 PrismX MX100 Vulnerability Hard-Coded Credentials Advantech Vulnerability CVE-2025-52694 Eaton UPS Companion, CVE-2025-59887 ASUS Router, Authentication Bypass ASUSTOR DLL Hijacking, Privilege Escalation OpenShift AI, Privilege Escalation GoAnywhere vulnerability CVE-2025-10035 LangChainGo, template injection DeepDiff, class pollution ToolShell Sunshine, CSRF Vulnerability KACE SMA, Critical Vulnerabilities Oracle Zero-Days - PDQ Deploy vulnerability
  • Malware

Malicious Update in Python Crypto Library Targets Private Keys via Telegram

Do Son November 23, 2024 0
Read More Read more about Malicious Update in Python Crypto Library Targets Private Keys via Telegram
CVE-2024-8811: WinZip Flaw Allows Malicious Code Execution CVE-2024-8811 - CVE-2025-1240
  • Vulnerability

CVE-2024-8811: WinZip Flaw Allows Malicious Code Execution

Do Son November 22, 2024 0
Read More Read more about CVE-2024-8811: WinZip Flaw Allows Malicious Code Execution
Ignoble Scorpius Strikes Again: The Rise of BlackSuit Ransomware Ignoble Scorpius
  • Cyber Security
  • Malware

Ignoble Scorpius Strikes Again: The Rise of BlackSuit Ransomware

Do Son November 22, 2024 0
Read More Read more about Ignoble Scorpius Strikes Again: The Rise of BlackSuit Ransomware
Wowza Streaming Engine Vulnerabilities Expose Thousands of Servers to Attack Wowza Streaming Engine - CVE-2024-52052
  • Vulnerability

Wowza Streaming Engine Vulnerabilities Expose Thousands of Servers to Attack

Do Son November 22, 2024 0
Read More Read more about Wowza Streaming Engine Vulnerabilities Expose Thousands of Servers to Attack
Microsoft Takes Down “ONNX” Phishing-as-a-Service Operation Fraudulent ONNX Store Telegram Channels
  • Cyber Security

Microsoft Takes Down “ONNX” Phishing-as-a-Service Operation

Do Son November 22, 2024 0
Read More Read more about Microsoft Takes Down “ONNX” Phishing-as-a-Service Operation
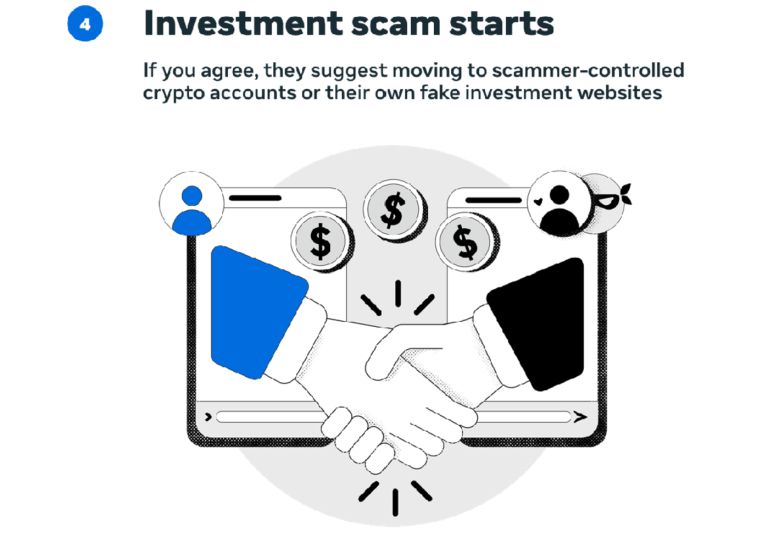
300,000 Forced to Scam: Meta’s Report Reveals Staggering Scale of “Pig Butchering” Pig Butchering
  • Cyber Security

300,000 Forced to Scam: Meta’s Report Reveals Staggering Scale of “Pig Butchering”

Do Son November 22, 2024 0
Read More Read more about 300,000 Forced to Scam: Meta’s Report Reveals Staggering Scale of “Pig Butchering”
USDA Pioneers Phishing-Resistant MFA with Fast IDentity Online (FIDO) Fast IDentity Online
  • Cyber Security

USDA Pioneers Phishing-Resistant MFA with Fast IDentity Online (FIDO)

Do Son November 22, 2024 0
Read More Read more about USDA Pioneers Phishing-Resistant MFA with Fast IDentity Online (FIDO)
CISA Sounds the Alarm on Actively Exploited Apple and Oracle Zero-Days Everon OCPP Vulnerability CVE-2026-26288 ASUSTOR ADM Vulnerability CVE-2026-24936 PrismX MX100 Vulnerability Hard-Coded Credentials Advantech Vulnerability CVE-2025-52694 Eaton UPS Companion, CVE-2025-59887 ASUS Router, Authentication Bypass ASUSTOR DLL Hijacking, Privilege Escalation OpenShift AI, Privilege Escalation GoAnywhere vulnerability CVE-2025-10035 LangChainGo, template injection DeepDiff, class pollution ToolShell Sunshine, CSRF Vulnerability KACE SMA, Critical Vulnerabilities Oracle Zero-Days - PDQ Deploy vulnerability
  • Vulnerability

CISA Sounds the Alarm on Actively Exploited Apple and Oracle Zero-Days

Do Son November 22, 2024 0
Read More Read more about CISA Sounds the Alarm on Actively Exploited Apple and Oracle Zero-Days
“PopeyeTools” Dismantled: Justice Department Seizes Cybercrime Marketplace and Charges Administrators PopeyeTools
  • Cyber Security

“PopeyeTools” Dismantled: Justice Department Seizes Cybercrime Marketplace and Charges Administrators

Do Son November 22, 2024 0
Read More Read more about “PopeyeTools” Dismantled: Justice Department Seizes Cybercrime Marketplace and Charges Administrators
Why Should Businesses Use Residential Proxies? CVE-2023-49606
  • Technique

Why Should Businesses Use Residential Proxies?

Do Son November 22, 2024 0
Read More Read more about Why Should Businesses Use Residential Proxies?
Red Hat Enterprise Linux Lands on Windows Subsystem for Linux Red Hat Enterprise Linux WSL WSL open source, Windows Linux
  • Linux
  • Technology
  • Windows

Red Hat Enterprise Linux Lands on Windows Subsystem for Linux

Do Son November 21, 2024 0
Read More Read more about Red Hat Enterprise Linux Lands on Windows Subsystem for Linux
DOJ’s Radical Proposal: Could Google Be Forced to Sell Chrome and Android? Chrome Vulnerability CVE-2024-4761 - Google Sell Chrome CVE-2025-1920 Chrome Crash, Browser Issue
  • Technology

DOJ’s Radical Proposal: Could Google Be Forced to Sell Chrome and Android?

Do Son November 21, 2024 0
Read More Read more about DOJ’s Radical Proposal: Could Google Be Forced to Sell Chrome and Android?
Qualities of the Best Security Guard Company: Ensuring Safety and Peace of Mind cybersecurity Advertise
  • Technique

Qualities of the Best Security Guard Company: Ensuring Safety and Peace of Mind

Do Son November 21, 2024 0
Read More Read more about Qualities of the Best Security Guard Company: Ensuring Safety and Peace of Mind
NVIDIA Base Command Manager Update Patches CVE-2024-0138 (CVSS 9.8) NVIDIA GPU Security CUDA-Q Vulnerability NVIDIA Apex Vulnerability AI Infrastructure Security NVIDIA Cumulus Linux CVE-2025-33179 NVIDIA Arm divestment NVIDIA DGX Spark, CVE-2025-33187 NVIDIA Isaac-GROOT, Code Injection Megatron-LM Vulnerability, AI Code Injection NVIDIA China NVIDIA GPUs, Hardware Kill Switches NVIDIA Megatron-LM, LLM Vulnerabilities NVIDIA Base Command Manager - CVE-2024-0138
  • Vulnerability

NVIDIA Base Command Manager Update Patches CVE-2024-0138 (CVSS 9.8)

Do Son November 21, 2024 0
Read More Read more about NVIDIA Base Command Manager Update Patches CVE-2024-0138 (CVSS 9.8)
Weaponized Defenses: Malicious Campaign Hijacks Legitimate Security Drivers Hijack Security Drivers
  • Malware

Weaponized Defenses: Malicious Campaign Hijacks Legitimate Security Drivers

Do Son November 21, 2024 0
Read More Read more about Weaponized Defenses: Malicious Campaign Hijacks Legitimate Security Drivers
CVE-2024-10126 & CVE-2024-10127: M-Files Addresses File Inclusion and Authentication Bypass Flaws M-Files Security, Session Token Disclosure CVE-2024-10126 and CVE-2024-10127
  • Vulnerability

CVE-2024-10126 & CVE-2024-10127: M-Files Addresses File Inclusion and Authentication Bypass Flaws

Do Son November 21, 2024 0
Read More Read more about CVE-2024-10126 & CVE-2024-10127: M-Files Addresses File Inclusion and Authentication Bypass Flaws
Chinese APTs Shift Tactics to Evade Detection and Maintain Stealth Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security

Chinese APTs Shift Tactics to Evade Detection and Maintain Stealth

Do Son November 21, 2024 0
Read More Read more about Chinese APTs Shift Tactics to Evade Detection and Maintain Stealth
Raspberry Robin’s Stealth Tactics: USB Infections, Exploits, and Advanced Obfuscation Unveiled GuLoader Malware CloudEye Obfuscation npm, malware Ethereum, npm supply chain OAST techniques StilachiRAT macOS Malware PasivRobber
  • Cyber Security
  • Vulnerability

Raspberry Robin’s Stealth Tactics: USB Infections, Exploits, and Advanced Obfuscation Unveiled

Do Son November 21, 2024 0
Read More Read more about Raspberry Robin’s Stealth Tactics: USB Infections, Exploits, and Advanced Obfuscation Unveiled
CVE-2024-9478 & CVE-2024-9479: upKeeper IPA Flaws Rated CVSSv4 10 Now Resolved WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Vulnerability

CVE-2024-9478 & CVE-2024-9479: upKeeper IPA Flaws Rated CVSSv4 10 Now Resolved

Do Son November 21, 2024 0
Read More Read more about CVE-2024-9478 & CVE-2024-9479: upKeeper IPA Flaws Rated CVSSv4 10 Now Resolved
Cybersecurity Concerns Loom Over Drinking Water Systems, Says EPA Inspector General Report Iranian Hacktivists Operation Epic Fury Cyber New Generation Warfare Russian Hybrid Escalation Plex data breach Water Systems Cybersecurity - Threat Actor Naming Standard
  • Cyber Security

Cybersecurity Concerns Loom Over Drinking Water Systems, Says EPA Inspector General Report

Do Son November 21, 2024 0
Read More Read more about Cybersecurity Concerns Loom Over Drinking Water Systems, Says EPA Inspector General Report
Volt Typhoon: Chinese State-Sponsored APT Targets U.S. Critical Infrastructure Volt Typhoon APT group
  • Cyber Security
  • Vulnerability

Volt Typhoon: Chinese State-Sponsored APT Targets U.S. Critical Infrastructure

Do Son November 21, 2024 0
Read More Read more about Volt Typhoon: Chinese State-Sponsored APT Targets U.S. Critical Infrastructure
CVE-2024-52067: Sensitive Data Exposed in Apache NiFi Debug Logs Apache NiFi RCE CVE-2026-39816 Apache NiFi Vulnerability CVE-2026-25903 Apache NiFi Deserialization, GetAsanaObject Vulnerability CVE-2024-52067 - CVE-2024-56512 CVE-2025-27017
  • Vulnerability

CVE-2024-52067: Sensitive Data Exposed in Apache NiFi Debug Logs

Do Son November 21, 2024 0
Read More Read more about CVE-2024-52067: Sensitive Data Exposed in Apache NiFi Debug Logs
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-93836CVSS 7.2
    The WPC Product Bundles for WooCommerce plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the \'qty\'...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-21589CVSS 9.3
    This is a vulnerability in Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-61500CVSS 9.3
    Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-107459CVSS 9.3
    The SecuShare Pro developed by Openfind has an OS Command Injection vulnerability. Unauthenticated remote attackers can inject arbitrary...
    📅 Updated: Oct 8, 2026
  • CVE-2026-14990CVSS 9.3
    IBM DataPower Gateway 10.6.0.0 through 10.6.0.10 is vulnerable to cross-site scripting. This vulnerability allows an unauthenticated user to embed...
    📅 Updated: Oct 8, 2026
  • CVE-2026-14991CVSS 9.8
    IBM DataPower Gateway 10.5.0.0 through 10.5.0.22, 10.6.1 through 10.6.6, 10.6.0.0 through 10.6.0.10, and 11.0.0.0 through 11.0.0.2 is vulnerable...
    📅 Updated: Oct 8, 2026
  • CVE-2026-17635CVSS 9.1
    IBM Financial Transaction Manager (FTM) for RedHat OpenShift could allow a remote attacker to perform unauthorized actions due...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102106CVSS 9.1
    Improper authentication in a Kiteworks Email Protection Gateway administrative service. An administrative service in Kiteworks Email Protection Gateway...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102105CVSS 9.1
    Kiteworks Email Protection Gateway before version 9.5.0 is vulnerable to Server-Side Request Forgery (SSRF). A server-side request forgery...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102104CVSS 9.1
    Kiteworks Email Protection Gateway before version 9.5.0 is vulnerable to Server-Side Request Forgery (SSRF). A server-side request forgery...
    📅 Updated: Oct 8, 2026
  • CVE-2026-102103CVSS 9.1
    Kiteworks Email Protection Gateway before version 9.5.0 is vulnerable to Server-Side Request Forgery (SSRF). A server-side request forgery...
    📅 Updated: Oct 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.