Skip to content
October 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Sync-Scheduler Malware: Unveiling a Sophisticated Espionage Attack APT Bitter - Sync-Scheduler
  • Cyber Security

Sync-Scheduler Malware: Unveiling a Sophisticated Espionage Attack

Do Son November 21, 2024 0
Read More Read more about Sync-Scheduler Malware: Unveiling a Sophisticated Espionage Attack
MisakaNetwork: Blockchain Botnet Threatens npm Ecosystem C2 interaction with an infected system
  • Malware

MisakaNetwork: Blockchain Botnet Threatens npm Ecosystem

Do Son November 21, 2024 0
Read More Read more about MisakaNetwork: Blockchain Botnet Threatens npm Ecosystem
Researchers Uncover XenoRAT’s New Tactics Leveraging Excel XLL Files and Advanced Obfuscation ahost.exe DLL Sideloading Signed Application Abuse PS1Bot, malware ransomware attacks bill
  • Malware

Researchers Uncover XenoRAT’s New Tactics Leveraging Excel XLL Files and Advanced Obfuscation

Do Son November 21, 2024 0
Read More Read more about Researchers Uncover XenoRAT’s New Tactics Leveraging Excel XLL Files and Advanced Obfuscation
Critical VMware vCenter Server Flaws Under Active Attack: CISA Issues Urgent Warning GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability

Critical VMware vCenter Server Flaws Under Active Attack: CISA Issues Urgent Warning

Do Son November 21, 2024 0
Read More Read more about Critical VMware vCenter Server Flaws Under Active Attack: CISA Issues Urgent Warning
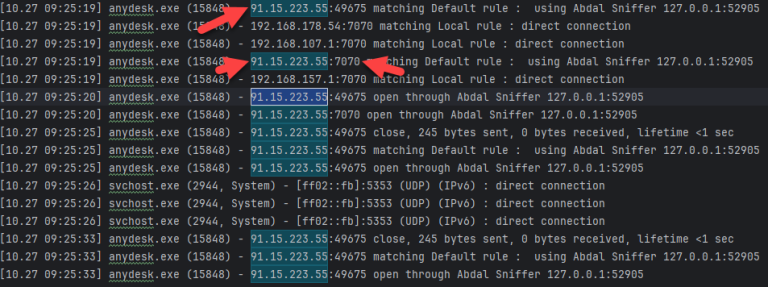
CVE-2024-52940: AnyDesk Vulnerability Exposes User IP Addresses, PoC Published CVE-2024-52940
  • Vulnerability

CVE-2024-52940: AnyDesk Vulnerability Exposes User IP Addresses, PoC Published

Do Son November 21, 2024 0
Read More Read more about CVE-2024-52940: AnyDesk Vulnerability Exposes User IP Addresses, PoC Published
PDFFlex: Analyzing PUA Persistence and Evasion Techniques PUA Persistence
  • Malware

PDFFlex: Analyzing PUA Persistence and Evasion Techniques

Do Son November 21, 2024 0
Read More Read more about PDFFlex: Analyzing PUA Persistence and Evasion Techniques
CVE-2024-10220: Kubernetes Vulnerability Allows Arbitrary Command Execution Ingress-Nginx Vulnerability Kubernetes RCE Vulnerability CVE-2025-9708 Kubernetes Security, Image Builder Vulnerability CVE-2024-10220 - OPA Gatekeeper Bypass
  • Vulnerability

CVE-2024-10220: Kubernetes Vulnerability Allows Arbitrary Command Execution

Do Son November 20, 2024 0
Read More Read more about CVE-2024-10220: Kubernetes Vulnerability Allows Arbitrary Command Execution
Phishing Scheme Nets Millions in Cryptocurrency, Five Charged StrelaStealer malware attacks - Phishing Scheme
  • Cyber Security

Phishing Scheme Nets Millions in Cryptocurrency, Five Charged

Do Son November 20, 2024 0
Read More Read more about Phishing Scheme Nets Millions in Cryptocurrency, Five Charged
CVE-2024-42450 (CVSS 10): Versa Networks Addresses Critical Vulnerability in Versa Director CVE-2024-42450 - Versa Director
  • Vulnerability

CVE-2024-42450 (CVSS 10): Versa Networks Addresses Critical Vulnerability in Versa Director

Do Son November 20, 2024 0
Read More Read more about CVE-2024-42450 (CVSS 10): Versa Networks Addresses Critical Vulnerability in Versa Director
Earth Kasha Expands Operations: New LODEINFO Malware Hits Government and High-Tech Earth Kasha - LODEINFO
  • Cyber Security
  • Malware

Earth Kasha Expands Operations: New LODEINFO Malware Hits Government and High-Tech

Do Son November 20, 2024 0
Read More Read more about Earth Kasha Expands Operations: New LODEINFO Malware Hits Government and High-Tech
2024 CWE Top 25: Critical Software Weaknesses Revealed 2024 CWE Top 25
  • Vulnerability

2024 CWE Top 25: Critical Software Weaknesses Revealed

Do Son November 20, 2024 0
Read More Read more about 2024 CWE Top 25: Critical Software Weaknesses Revealed
WorkflowKit Race Vulnerability (CVE-2024-27821): Researcher Reveals Exploit that Let Malicious Apps Hijack Shortcuts Apple Foldable, iPhone Fold WorkflowKit, CVE-2024-27821 Zero-Days
  • Vulnerability

WorkflowKit Race Vulnerability (CVE-2024-27821): Researcher Reveals Exploit that Let Malicious Apps Hijack Shortcuts

Do Son November 20, 2024 0
Read More Read more about WorkflowKit Race Vulnerability (CVE-2024-27821): Researcher Reveals Exploit that Let Malicious Apps Hijack Shortcuts
FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Malware

FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol

Do Son November 20, 2024 0
Read More Read more about FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol
LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms PromptMink Campaign AI Agent Deception LIMINAL PANDA UNC1549 DLL Hijacking, VDI Breakout
  • Cyber Security

LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms

Do Son November 20, 2024 0
Read More Read more about LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms
Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution Veritas Enterprise Vault server CVE-2025-27816
  • Vulnerability

Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution

Do Son November 20, 2024 0
Read More Read more about Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution
New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming Exploited VMware
  • Cyber Security

New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming

Do Son November 20, 2024 0
Read More Read more about New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming
Ruckus Networks Issues Security Advisory for Critical RCE Vulnerability in Access Points libheif Vulnerability CVE-2025-65586 Trend Micro RCE CVE-2025-69258 SessionReaper CVE-2025-54236 VS Code Marketplace, supply chain attack npm Supply Chain, Toptal Compromise Ruckus AP Vulnerability
  • Vulnerability

Ruckus Networks Issues Security Advisory for Critical RCE Vulnerability in Access Points

Do Son November 20, 2024 0
Read More Read more about Ruckus Networks Issues Security Advisory for Critical RCE Vulnerability in Access Points
35,000 Bots, 180 Countries: Inside the Criminal Network of the NSOCKS Botnet NSOCKS botnet
  • Malware

35,000 Bots, 180 Countries: Inside the Criminal Network of the NSOCKS Botnet

Do Son November 20, 2024 0
Read More Read more about 35,000 Bots, 180 Countries: Inside the Criminal Network of the NSOCKS Botnet
Critical Vulnerability in D-Link EOL Routers Allows Remote Code Execution D-Link Vulnerability - End-of-Life Routers
  • Vulnerability

Critical Vulnerability in D-Link EOL Routers Allows Remote Code Execution

Do Son November 20, 2024 0
Read More Read more about Critical Vulnerability in D-Link EOL Routers Allows Remote Code Execution
“Ghost Tap” Emerges: Cybercriminals Exploit NFC Relay for Contactless Cash-Outs Ghost Tap
  • Cyber Security

“Ghost Tap” Emerges: Cybercriminals Exploit NFC Relay for Contactless Cash-Outs

Do Son November 20, 2024 0
Read More Read more about “Ghost Tap” Emerges: Cybercriminals Exploit NFC Relay for Contactless Cash-Outs
Kaspersky Lab’s Report Reveals Surge in Black Friday Shopping Threats BiDi Swap, phishing attacks Cybersecurity Threats
  • Cyber Security

Kaspersky Lab’s Report Reveals Surge in Black Friday Shopping Threats

Do Son November 20, 2024 0
Read More Read more about Kaspersky Lab’s Report Reveals Surge in Black Friday Shopping Threats
Five Critical Privilege Escalation Vulnerabilities Found in Ubuntu’s Default Utility, needrestart CVE-2024-48990 and CVE-2024-48922
  • Linux
  • Vulnerability

Five Critical Privilege Escalation Vulnerabilities Found in Ubuntu’s Default Utility, needrestart

Do Son November 20, 2024 0
Read More Read more about Five Critical Privilege Escalation Vulnerabilities Found in Ubuntu’s Default Utility, needrestart
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-93836CVSS 7.2
    The WPC Product Bundles for WooCommerce plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the \'qty\'...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-21589CVSS 9.3
    This is a vulnerability in Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-61500CVSS 9.3
    Rejetto HFS 3.0.0 through 3.2.0 derives its session-cookie signing key from the non-cryptographic Math.random() generator and discloses outputs...
    Admin intel📅 Updated: Oct 7, 2026
  • CVE-2026-88779CVSS 8.7
    Vulnerability in NetScaler ADC and NetScaler Gateway. This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS,...
    Admin intelCISA KEV📅 Added to KEV: Oct 4, 2026📅 Updated: Oct 4, 2026
  • CVE-2026-102490CVSS 8.5
    All versions of Zammad including the latest alpha enable the local zammad user to escalate privileges to root.
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-102489CVSS 8.7
    Zammad versions 6.3.0 to 6.5.4 are vulnerable a session hijack vulnerability that leads to remote code execution as...
    Admin intelCISA KEV📅 Added to KEV: Oct 2, 2026📅 Updated: Oct 2, 2026
  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-9209CVSS 9.3
    mJobTime through build 15.7.3.32 contains an unauthenticated SQL execution vulnerability in the Login.aspx admin panel handlers, where the...
    📅 Updated: Oct 8, 2026
  • CVE-2026-95606CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Liquid Web / StellarWP The Events Calendar allows Object Injection. This issue...
    📅 Updated: Oct 8, 2026
  • CVE-2026-95605CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Passionate Programmer Peter WP...
    📅 Updated: Oct 8, 2026
  • CVE-2026-85097CVSS 9.8
    The Bricksforge plugin for WordPress is vulnerable to unauthenticated arbitrary file upload in versions up to, and including,...
    📅 Updated: Oct 8, 2026
  • CVE-2026-17609CVSS 9.1
    The Super Forms – Drag & Drop Form Builder plugin for WordPress is vulnerable to Arbitrary Directory Deletion...
    📅 Updated: Oct 8, 2026
  • CVE-2022-37897CVSS 9.8
    There is a command injection vulnerability that could lead to unauthenticated remote code execution by sending specially crafted...
    📅 Updated: Oct 8, 2026
  • CVE-2026-105110CVSS 9.3
    OS Command Injection in the login.xgi CGI endpoint in Iskratel Innbox GPON ONT devices allows an unauthenticated remote...
    📅 Updated: Oct 8, 2026
  • CVE-2026-61447CVSS 10.0
    ### Summary `CodeAgent._execute_python()` executes LLM-generated Python code in a subprocess with the complete parent-process environment (`os.environ.copy()`), zero AST...
    📅 Updated: Oct 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.