 Do Son
Five actively exploited software vulnerabilities threaten critical systems. Update your servers now to prevent critical remote code execution attacks.
Latest Security News
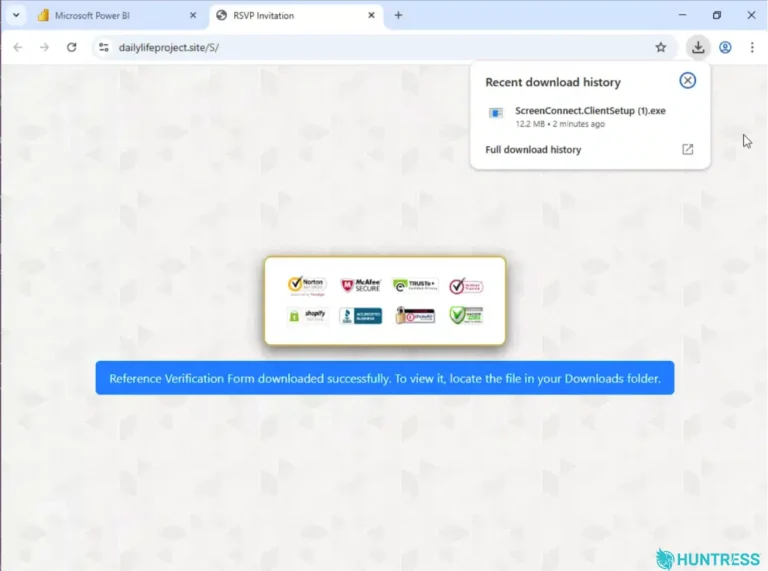
A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
Multiple IBM Verify Access vulnerabilities expose systems to remote attacks. Update your software now to block these critical security flaws.
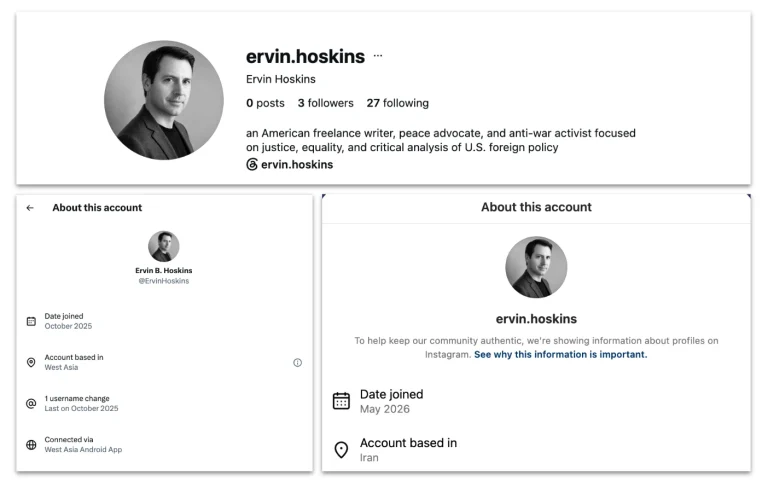
OpenAI disrupted state-backed AI false front operations. Threat actors ran covert false front operations using fake personas to manipulate global media.

Chinese state hackers allegedly use Integrity Technology Group tools for botnet data theft. Protect your networks from this massive cyberespionage campaign.
Discover the new critical Tapo C325WB vulnerabilities exposing TP-Link cameras. Learn how to patch these Tapo C325WB vulnerabilities and secure your video.
Threat actors are actively abusing critical AhsayCBS vulnerabilities in the wild to deploy cryptominers. Patch unpatched AhsayCBS vulnerabilities now.
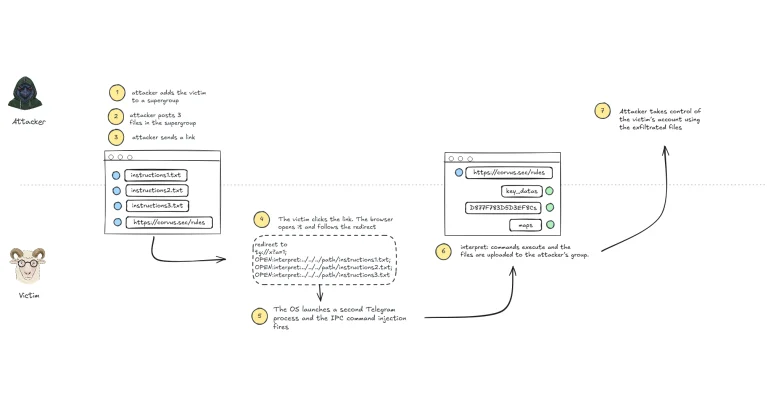
A critical Telegram Desktop account takeover vulnerability (CVE-2026-107181) exposes users to session hijacking. Exploit details and PoC are now public.
HPE fixes a critical HPE iLO 7 vulnerability, CVE-2026-79820, and iMC authentication bypass CVE-2026-79842. Update iLO to 1.25.01 now.
Critical Citrix NetScaler vulnerability CVE-2026-107406 (CVSS 9.5) can lead to RCE on SAML-configured ADC and Gateway. Upgrade now.
IBM fixes 23 IBM DataPower Gateway vulnerabilities, including critical RCE flaws CVE-2026-15762 and CVE-2026-16340. Upgrade to 11.0.0.3 now.
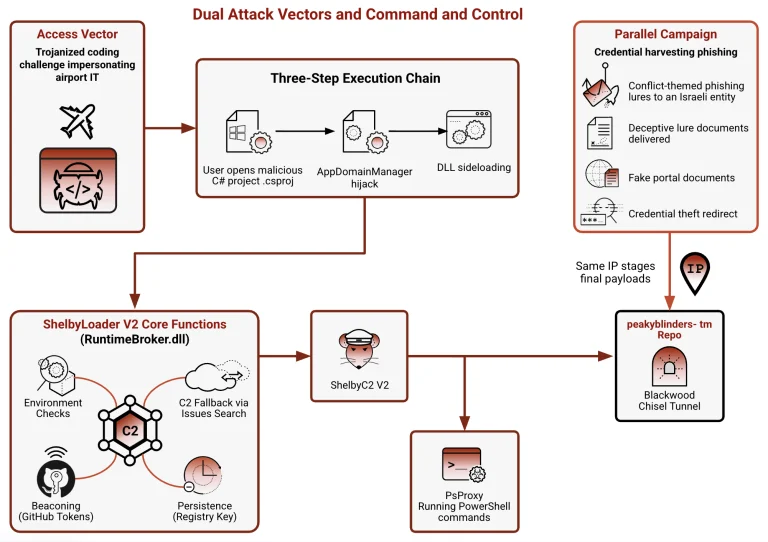
The Blinder Tunnel campaign used a fake Dubai Airports coding test to drop ShelbyLoader V2 on an Iraqi target. See how it works and how to defend.
Latest Technology News
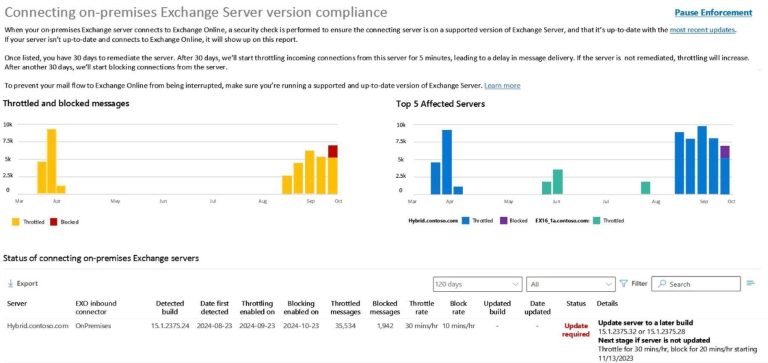
Exchange Online blocking of outdated Exchange 2016 and 2019 servers begins in September 2026, requiring the October 2025 update baseline.
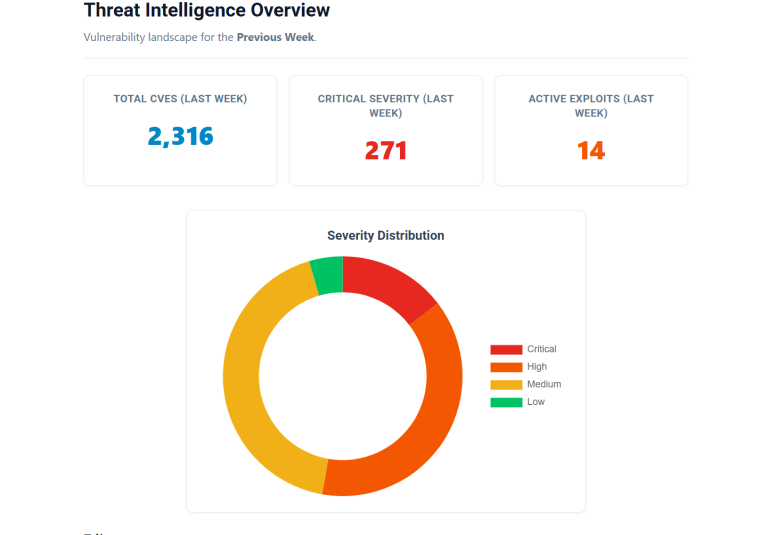
This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.
Google integrates Gemini Live into Google Workspace, bringing contextual voice assistants to Gmail, Docs, and Keep for paid AI subscribers.
Most AI security tools ship with one approve button. You click it and the action runs. You...
A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.
Discover the new GPT-6 Astra Codex pricing policy. OpenAI now removes multiplier penalties for contexts exceeding 272K, offering flat rates up to 1M tokens.
CERN's Debian migration moves 2,200+ accelerator control machines off Red Hat, driven by RHEL's raised x86-64 CPU baseline.
 cybernewswire
Frankfurt am Main, Deutschland, 3rd September 2026, CyberNewswire
Microsoft will require a Windows driver SBOM and VEX statement for signing from March 2027, aligning WHCP with the EU CRA.
The General Court dismisses the Opera lawsuit. The EU exempts Microsoft Edge from strict Digital Markets Act gatekeeper rules based on low user engagement.
Latest Security News
A VMware VMXNET3 vulnerability, CVE-2026-59346 (CVSS 9.3), allows VM escape. Full details and PoC exploit code are now public. Patch to 26H1u1.
Splunk fixes 22 Splunk Enterprise vulnerabilities, including critical Patroni API flaw CVE-2026-76268 and CVE-2026-76281. Upgrade to 10.4.3 now.
An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
Cisco License On-Prem vulnerabilities include CVSS 10 flaw CVE-2026-76482 and password reset bug CVE-2026-20328. APIC and Meraki also patched.
Cisco NX-OS vulnerabilities fixed, including critical NX-API RCE flaw CVE-2026-76471 and CVE-2026-76455, across Nexus, MDS and UCS gear. Patch now.
Four critical Cisco Nexus vulnerabilities, including CVE-2026-76485 and CVE-2026-76465 (CVSS 9.8), allow root RCE on NX-OS switches. Patch now.
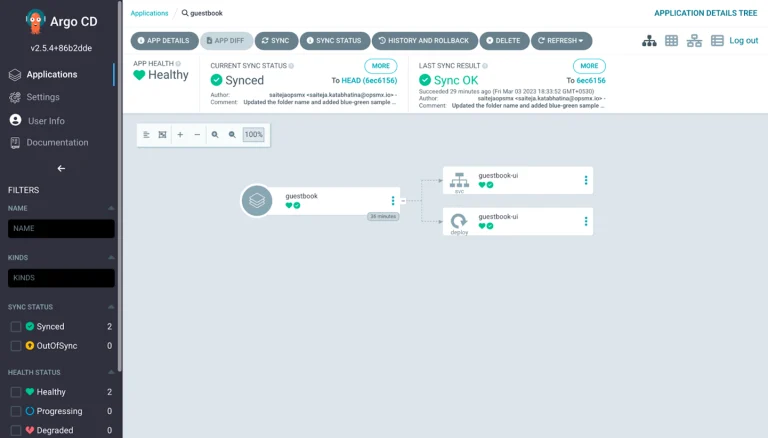
Four critical Argo CD vulnerabilities, including AppProject bypass CVE-2026-77459, threaten the repo-server and clusters. Upgrade to v3.5.4 now.
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
eSentire tracks four clusters behind CVE-2026-88771 exploitation, planting NetScaler web shells and backdoor accounts. Learn how to detect them.
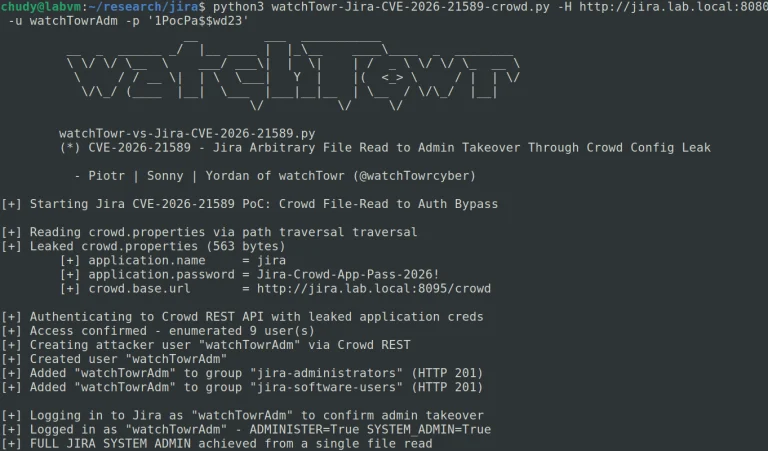
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Elastic fixes 14 Elastic Stack vulnerabilities, including Kibana flaw CVE-2026-102406 and Elasticsearch bug CVE-2026-103007. Upgrade now.
Latest Technology News
This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.
Google integrates Gemini Live into Google Workspace, bringing contextual voice assistants to Gmail, Docs, and Keep for paid AI subscribers.
Most AI security tools ship with one approve button. You click it and the action runs. You...
A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.
Discover the new GPT-6 Astra Codex pricing policy. OpenAI now removes multiplier penalties for contexts exceeding 272K, offering flat rates up to 1M tokens.
CERN's Debian migration moves 2,200+ accelerator control machines off Red Hat, driven by RHEL's raised x86-64 CPU baseline.
Frankfurt am Main, Deutschland, 3rd September 2026, CyberNewswire
Microsoft will require a Windows driver SBOM and VEX statement for signing from March 2027, aligning WHCP with the EU CRA.
The General Court dismisses the Opera lawsuit. The EU exempts Microsoft Edge from strict Digital Markets Act gatekeeper rules based on low user engagement.
Microsoft Defender for Office 365 incorrectly flags Google search links as malicious, causing false alarms. Microsoft is fixing the classification error.