Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
US Offers $10M for IRGC Cyber Leader US Rewards for Justice poster offering $10 million for information on Iranian IRGC cyber commander Amir Yaryab
  • Cybercriminals

US Offers $10M for IRGC Cyber Leader

Do Son September 5, 2026 0

The US offers a $10 million reward for Amir Yaryab, an IRGC cyber commander linked to CyberAv3ngers attacks on critical water infrastructure.
Coder Registry Attack: Hijacked Cloudflare Pool Served Malicious Terraform Modules Coder registry attack serving malicious Terraform modules from a hijacked Cloudflare pool
  • Cybercriminals

Coder Registry Attack: Hijacked Cloudflare Pool Served Malicious Terraform Modules

Do Son September 5, 2026 0

The Coder registry attack hijacked Cloudflare IPs to serve malicious Terraform modules from registry.coder.com, stealing developer secrets.
Google Workspace Integrates Gemini Live Features Google Workspace interface displaying Gemini Live integration across Gmail, Docs, and Keep applications
  • Technology

Google Workspace Integrates Gemini Live Features

Do Son September 5, 2026 0

Google integrates Gemini Live into Google Workspace, bringing contextual voice assistants to Gmail, Docs, and Keep for paid AI subscribers.
CVE-2026-75754 (CVSS 10): ASUS Control Center Root RCE ASUS Control Center vulnerability CVE-2026-75754 allowing unauthenticated attackers to gain a root shell and full remote control
  • Vulnerability Report

CVE-2026-75754 (CVSS 10): ASUS Control Center Root RCE

Do Son September 4, 2026 0

An ASUS Control Center vulnerability, CVE-2026-75754 (CVSS 10), gives unauthenticated attackers a root shell. Update to v3.1.0.9 now.
Your AI Security Tool Has One Approval Button. It Needs Four Diagram illustrating Langflow OSS vulnerabilities and CVE-2026-10134 execution paths
  • Technique

Your AI Security Tool Has One Approval Button. It Needs Four

Do Son September 4, 2026 0
Most AI security tools ship with one approve button. You click it and the action runs. You...
Read More Read more about Your AI Security Tool Has One Approval Button. It Needs Four
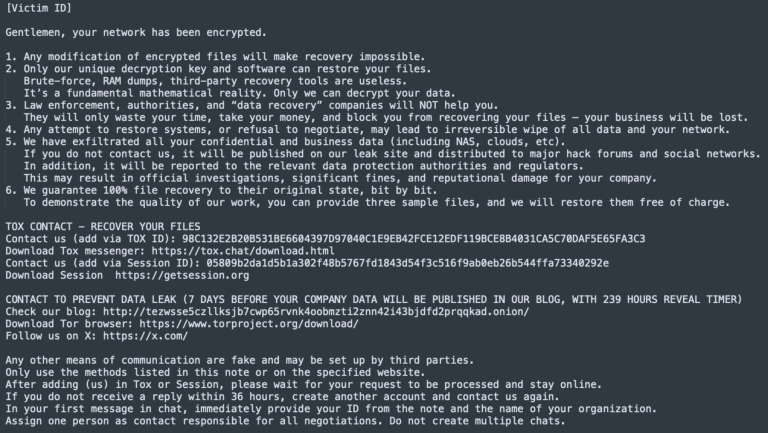
The Gentlemen Ransomware Deploys in Under 24 Hours The Gentlemen ransomware attack chain showing GOLD SHERWOOD affiliates using GentleKiller EDR killer and Rclone data exfiltration
  • Malware

The Gentlemen Ransomware Deploys in Under 24 Hours

Do Son September 4, 2026 0

The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.
Trezor Data Breach at ShipMonk Grows to 80,000 Customers Trezor data breach notice showing customer order data exposed through shipping provider ShipMonk in a third-party vendor breach
  • Data Leak

Trezor Data Breach at ShipMonk Grows to 80,000 Customers

Do Son September 4, 2026 0

The Trezor data breach at shipping partner ShipMonk exposed about 80,000 customers' order data. Wallets are safe, but phishing risk is high.
FreeSWITCH api-chat RCE Exploited in the Wild, Patch Now FreeSWITCH api-chat vulnerability exploited in the wild for remote code execution via SIP MESSAGE on FusionPBX servers
  • Vulnerability

FreeSWITCH api-chat RCE Exploited in the Wild, Patch Now

Do Son September 4, 2026 0

A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.
Toy Ghouls Backdoor Uses HiveMQ and Element for C2 Rust supply chain attack on arrayref crate with proc-macro1 typosquat and DPRK infrastructure overlap
  • Cybercriminals

Toy Ghouls Backdoor Uses HiveMQ and Element for C2

Do Son September 4, 2026 0

The Toy Ghouls backdoor hides C2 traffic in HiveMQ MQTT and Element messenger. See how the Bearlyfy group's custom malware works.
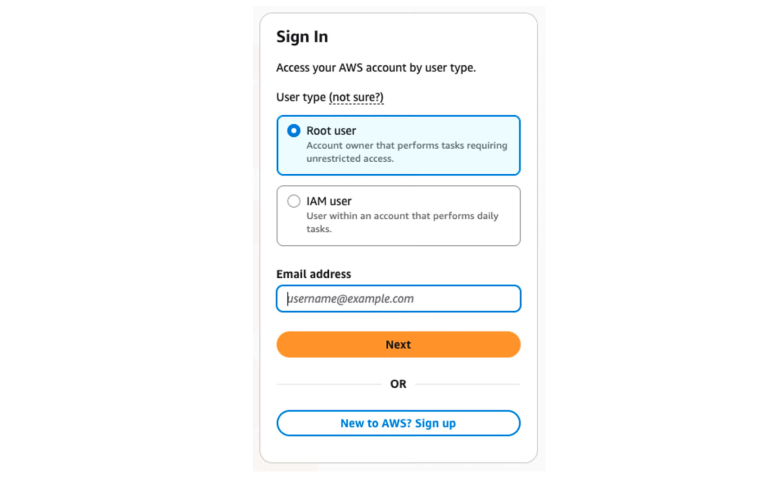
AWS Password Spraying Campaign Targets Root Accounts Chart showing an AWS password spraying campaign targeting root logins with AWS password spraying
  • Cybercriminals

AWS Password Spraying Campaign Targets Root Accounts

Do Son September 4, 2026 0

Datadog uncovered an AWS password spraying campaign targeting cloud environments. Protect your accounts against this AWS password spraying activity now.
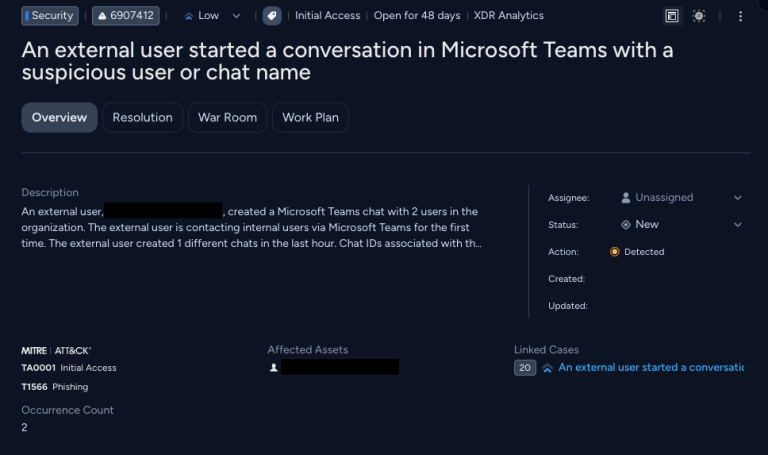
Spring Ring Vishing Campaign Targets Microsoft Teams Anatomy of the Spring Ring vishing campaign and Microsoft Teams phishing attacks
  • Cybercriminals

Spring Ring Vishing Campaign Targets Microsoft Teams

Do Son September 4, 2026 0

Discover how the Spring Ring vishing campaign uses Microsoft Teams phishing tactics to trick employees into installing malware and giving up remote access.

AiTM Phishing Campaign Targets Healthcare via Account Takeovers Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
  • Cybercriminals

AiTM Phishing Campaign Targets Healthcare via Account Takeovers

Do Son September 4, 2026 0

A new AiTM phishing campaign targets healthcare. Learn how this healthcare AiTM phishing campaign chains compromised accounts to bypass MFA.
Apache Allura Security Vulnerabilities Patched in v1.21.0 Apache Allura security vulnerabilities update
  • Vulnerability Report

Apache Allura Security Vulnerabilities Patched in v1.21.0

Do Son September 4, 2026 0

Apache released version 1.21.0 to patch critical Apache Allura security vulnerabilities. Update now to protect against XSS, SSRF, and data exposure flaws.
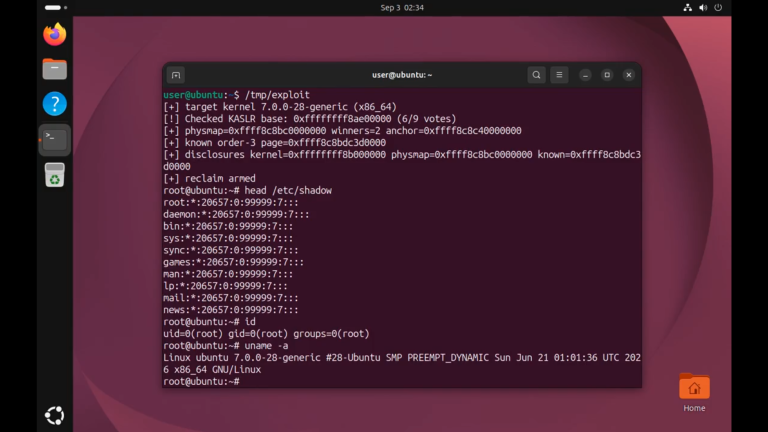
CVE-2026-52924 PoC Exploit Disclosed: 9.8 CVSS Linux Root Privilege Escalation Linux CVE-2026-52924 details and Linux CVE-2026-52924 PoC exploit release
  • Vulnerability Report

CVE-2026-52924 PoC Exploit Disclosed: 9.8 CVSS Linux Root Privilege Escalation

Do Son September 4, 2026 0

Security researchers released a Linux CVE-2026-52924 PoC exploit. Check flaw details and patch instructions to secure your systems against root takeovers.
GPT-6 Astra Updates Codex Pricing GPT-6 Astra Codex pricing token cost chart
  • Technology

GPT-6 Astra Updates Codex Pricing

Do Son September 4, 2026 0

Discover the new GPT-6 Astra Codex pricing policy. OpenAI now removes multiplier penalties for contexts exceeding 272K, offering flat rates up to 1M tokens.
TP-Link Archer AX55 Flaws Expose Routers to Code Execution TP-Link Archer AX55 vulnerability advisory showing EasyMesh buffer overflow and hardcoded RSA key flaws CVE-2026-18167 CVE-2026-18330
  • Vulnerability Report

TP-Link Archer AX55 Flaws Expose Routers to Code Execution

Do Son September 4, 2026 0

A TP-Link Archer AX55 vulnerability (CVE-2026-18167) risks remote code execution via EasyMesh buffer overflow. Update to build 20260527 now.
Plex Issues Urgent Security Update for Media Server and Desktop Plex security update notice for Media Server 1.43.3 and Plex Desktop 1.115.0
  • Vulnerability Report

Plex Issues Urgent Security Update for Media Server and Desktop

Do Son September 4, 2026 0

Plex urges an urgent security update to Media Server 1.43.3 and Desktop 1.115.0. NAS and Docker users may need to patch manually.
CERN to Move 2,200 Accelerator Control Machines to Debian 13 CERN Debian migration of accelerator control computers from Red Hat to Debian 13
  • Linux

CERN to Move 2,200 Accelerator Control Machines to Debian 13

Do Son September 4, 2026 0

CERN's Debian migration moves 2,200+ accelerator control machines off Red Hat, driven by RHEL's raised x86-64 CPU baseline.
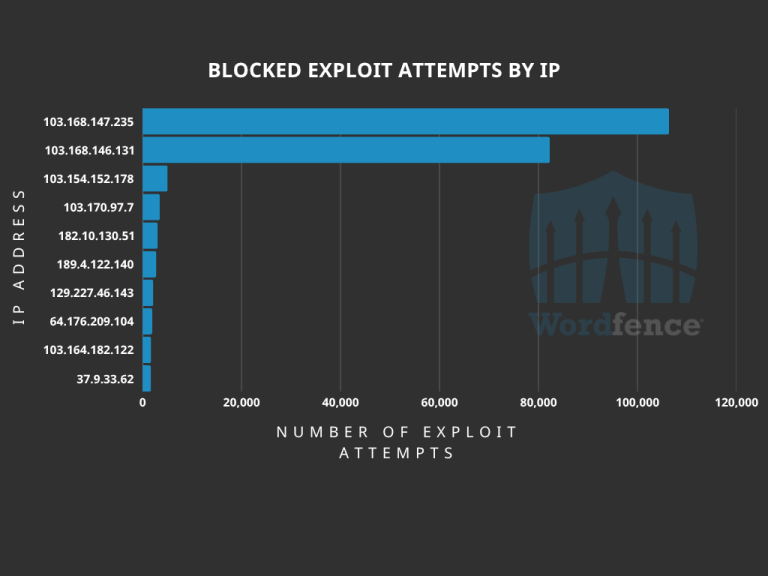
Super Forms Vulnerability Exploited in the Wild: 13,000 Sites Face 9.8 CVSS Remote Code Execution Super Forms vulnerability CVE-2026-14894 arbitrary file upload remote code execution exploited in the wild WordPress plugin diagram
  • Vulnerability Report

Super Forms Vulnerability Exploited in the Wild: 13,000 Sites Face 9.8 CVSS Remote Code Execution

Do Son September 4, 2026 0

CVE-2026-14894, a critical Super Forms vulnerability, is exploited in the wild. The 9.8 CVSS file upload flaw enables unauthenticated remote code execution.
Critical WHMCS Security Update Patches RCE Flaws WHMCS security update for CVE-2026-67399 remote code execution and CVE-2026-67398
  • Vulnerability Report

Critical WHMCS Security Update Patches RCE Flaws

Do Son September 4, 2026 0

A critical WHMCS security update fixes CVE-2026-67399 and CVE-2026-67398. Apply the patch now to prevent remote code execution and data leaks.
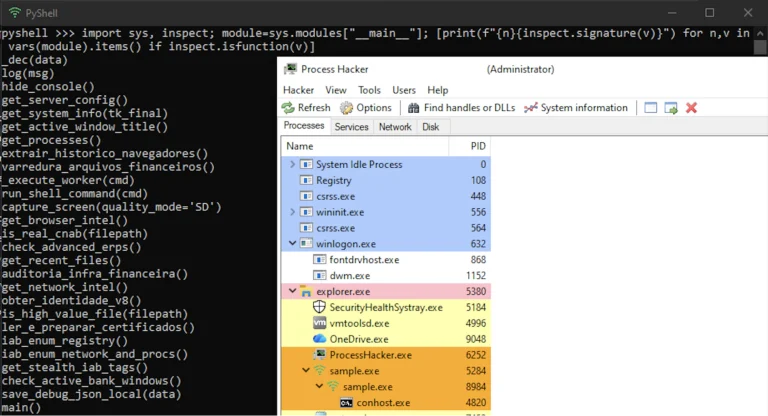
BraZetsu Malware Framework Powers Initial Access Sales BraZetsu malware framework and BraZetsu malware framework operations diagram
  • Cybercriminals

BraZetsu Malware Framework Powers Initial Access Sales

Do Son September 4, 2026 0

Group-IB uncovered the BraZetsu malware framework operations targeting financial systems. Learn how this tool powers initial access broker sales.
Critical SonicWall NSM Vulnerabilities Patched Critical SonicWall NSM vulnerabilities security update overview
  • Vulnerability Report

Critical SonicWall NSM Vulnerabilities Patched

Do Son September 3, 2026 0

SonicWall patched critical SonicWall NSM vulnerabilities in on-prem software. Update now to protect your network against remote code execution.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118697CVSS 9.0
    In JetBrains Toolbox App before 3.9.1 and 3.8.2; IntelliJ IDEA before 2026.3 and 2026.2.4, the jetbrainsd daemon trusted...
    📅 Updated: Oct 31, 2026
  • CVE-2026-112816CVSS 10.0
    Improper certificate validation in the HTTPS listener in Canonical LXD 4.0.14, 5.0.10, 5.21.8, 6.9 before 4.0.15, 5.0.11, 5.21.9, 6.10.1...
    📅 Updated: Oct 31, 2026
  • CVE-2026-78845CVSS 9.8
    Aidot products Linkind Matter Smart Plug 1.01.32, OREiN Matter Smart Light Bulb 3.15.21, and Linkind Wi-Fi Smart Light...
    📅 Updated: Oct 31, 2026
  • CVE-2026-102649CVSS 9.9
    Burrito is a Terraform Automation Collaboration Software (TACoS) Kubernetes operator. Prior to 0.13.0, `POST /api/webhook` accepts unsigned GitHub...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116508CVSS 10.0
    A security flaw has been discovered in TOTOLINK A950RG 4.1.2cu.5268_B20221104. Affected by this issue is the function sub_402340...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116505CVSS 9.4
    A vulnerability was found in TOTOLINK A950RG 4.1.2cu.5268_B20221104. This impacts the function getDeviceInfo of the file /var/lib/misc/udhcpd.leases of...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.