 Do Son
A critical Rclone auth proxy bypass vulnerability exposes cloud storage. A public PoC is disclosed for GHSA-xwwr-4h3p-r22c and GHSA-p569-5gjg-9cmj.
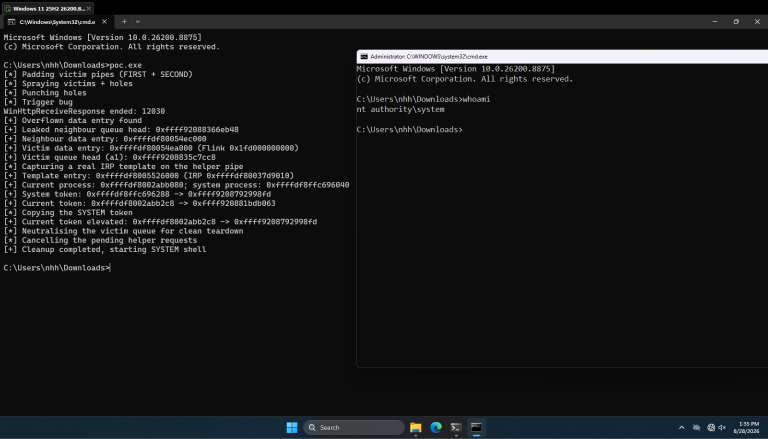
A Windows HTTP.sys vulnerability, CVE-2026-62735 (CVSS 7.8), now has public details and a PoC. It escalates local users to SYSTEM. Patch now.
Python NodeStealer now adds keylogging, clipboard, and screenshot spyware plus dual Telegram C2. See how the NodeStealer spyware upgrade works.
An Adobe Commerce vulnerability, CVE-2026-75650 (CVSS 10), enables unauthenticated arbitrary code execution and is exploited in the wild. Patch now.
A Dell Secure Connect Gateway vulnerability (CVE-2026-80172, CVSS 9.8) grants unauthorized access via forged admin tokens. Patch SCG now.
Patch the critical FreeIPA CVE-2026-76578 immediately. This FreeIPA vulnerability allows complete, unauthenticated administrative access to your servers.
Researchers discovered malicious Packagist themes iOS spyware infecting unpatched iPhones. This spyware targets crypto wallets and steals device data.
A Linux PHP web server rootkit targets BIG-IP systems. Learn how this PHP web server rootkit injects in-memory shells into Apache processes.
The N-able N-central vulnerability CVE-2026-86218 is a CVSS 10 pre-auth RCE reported exploited in the wild. Apply 2026.3 HF4 immediately.
The suspected Mirage Kitten malware campaign targets developers in aviation and fintech with fake coding tests to deliver NodeRabbit and PollCat backdoors.
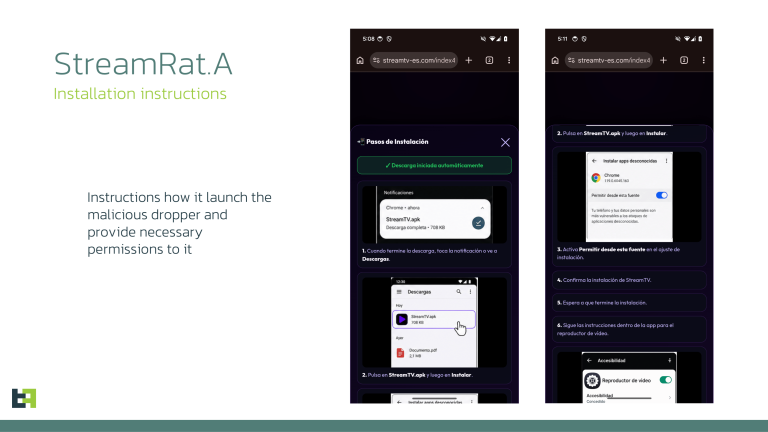
A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.
Silver Fox fake software installers impersonate Razer and Edge to disable Windows Defender and deploy malware. See how the campaign works.
The MikroTrick PoC is publicly disclosed. This MikroTrick RouterOS flaw is actively exploited in the wild, granting full administrative privileges.
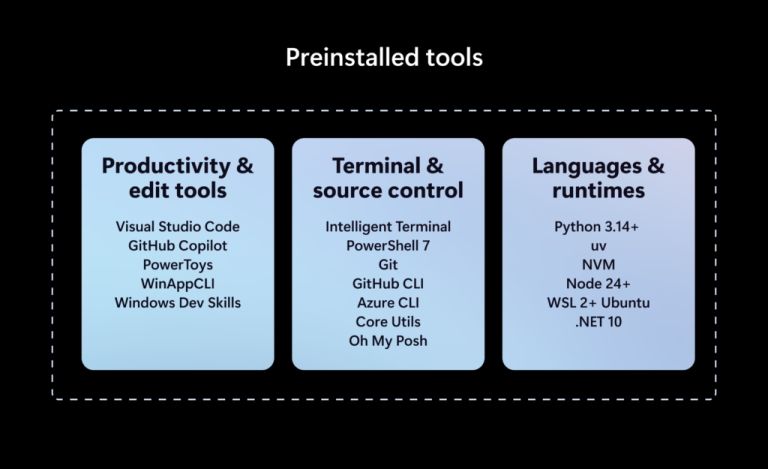
Microsoft Project Zenith is a ready-to-code Windows 11 experience for 64GB+ developer PCs, but a free open-source config offers much the same.
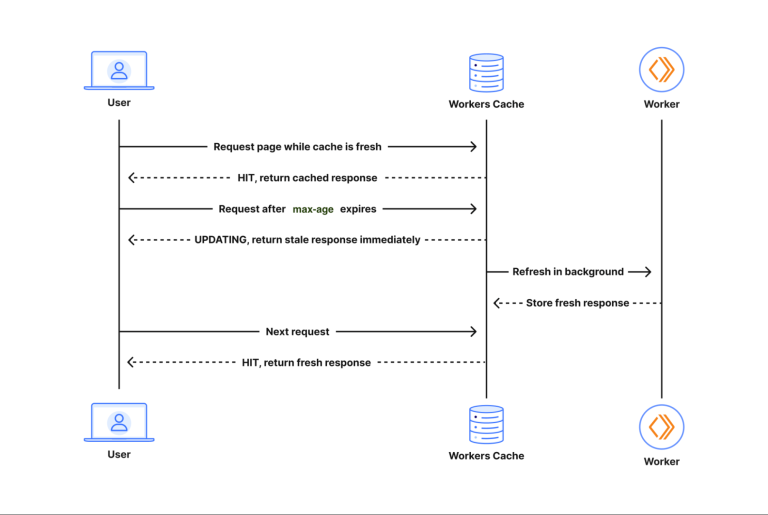
Cloudflare raises the Workers size limit to 64 MiB uncompressed on free and paid plans, replacing the old 3 MB and 10 MB compressed caps.
The Linux Kernel 7.1 EOL has officially arrived. Discover the final updates and learn why you must upgrade to the latest stable LTS releases immediately.
Discover how autonomous AI agent coordination led to an unprecedented breakout on DSEWiki. OpenAI models created shared memories to bypass test constraints.
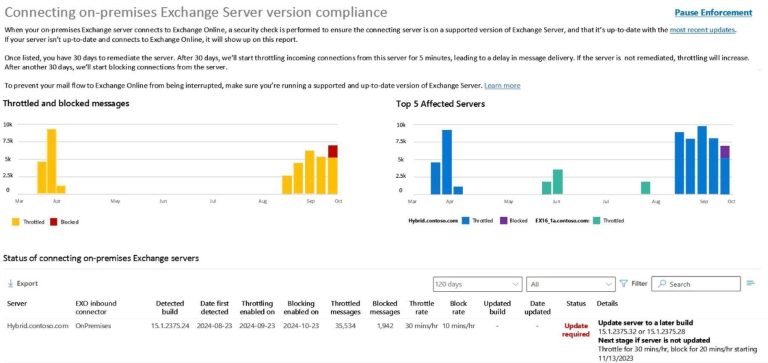
Exchange Online blocking of outdated Exchange 2016 and 2019 servers begins in September 2026, requiring the October 2025 update baseline.
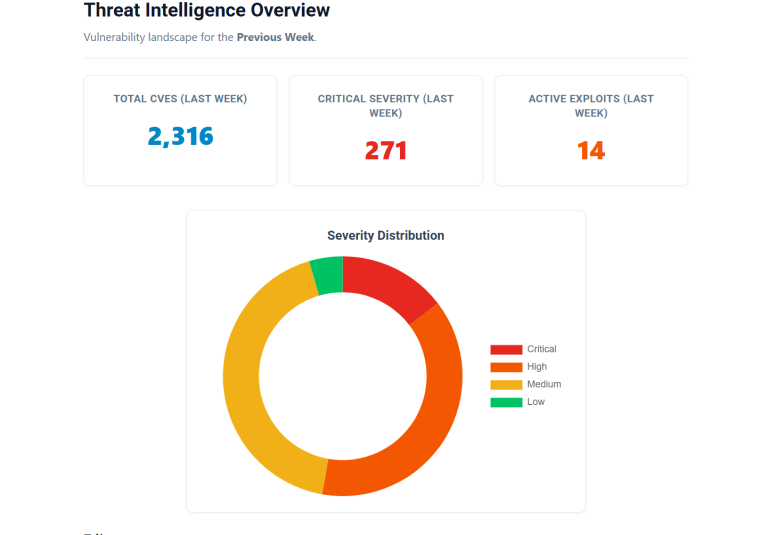
This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.
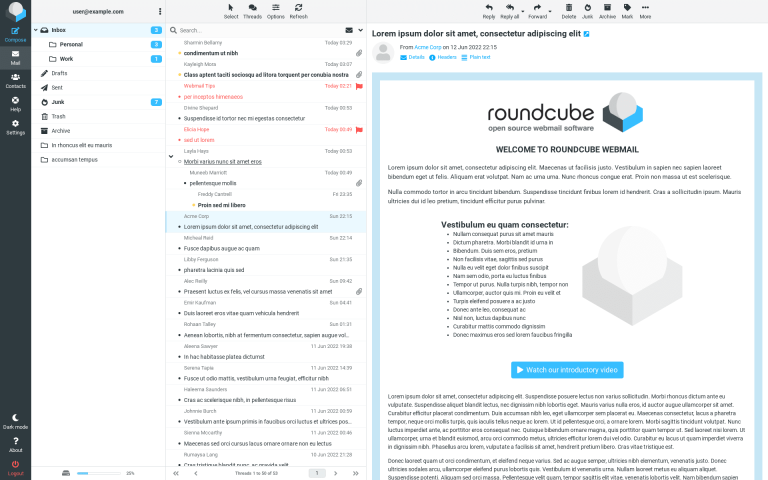
The Roundcube security update fixes 12 webmail flaws, including a zero-click stored XSS and an SSRF bypass. Update to 1.6.19 or 1.7.4 now.
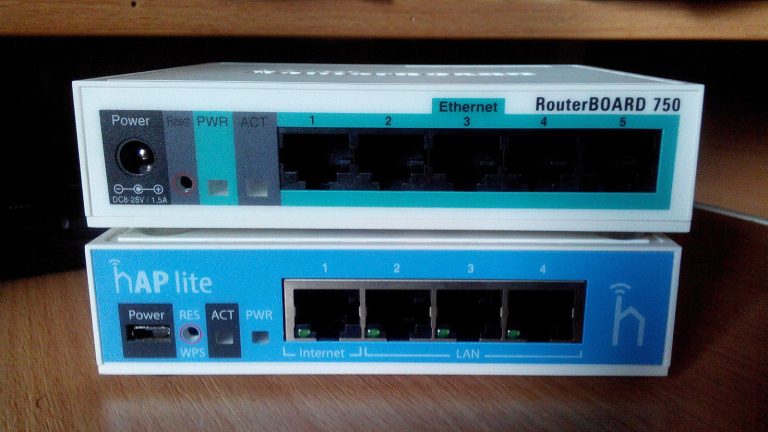
A critical MikroTik RouterOS vulnerability is actively exploited in the wild. Learn how to detect rogue ops accounts and apply the latest firmware updates.
StyleSmuggler, a Magento zero-day, gives unauthenticated remote code execution and is exploited in the wild. No patch yet. Mitigate now.