Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
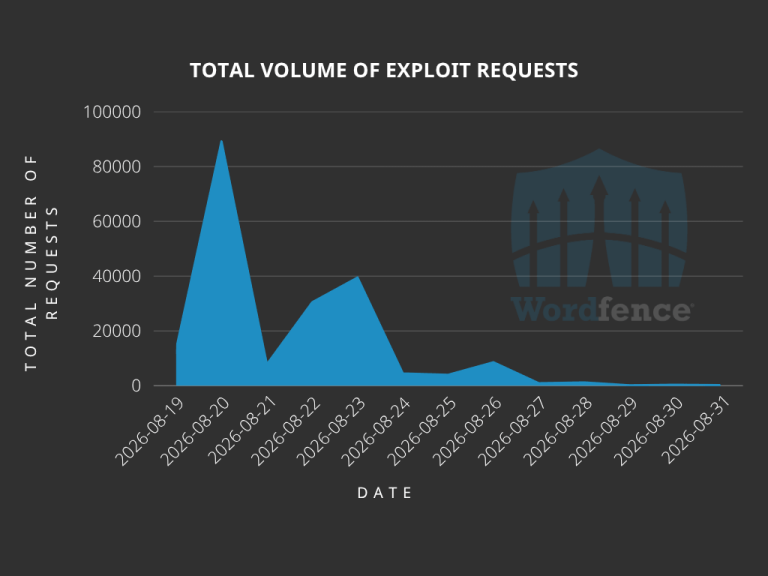
CVE-2026-32475: Elementor Pro RCE Exploited in the Wild Threat actors exploit a critical Elementor Pro vulnerability in the wild
  • Vulnerability Report

CVE-2026-32475: Elementor Pro RCE Exploited in the Wild

Do Son September 2, 2026 0

Attackers exploit a critical Elementor Pro vulnerability (CVE-2026-32475) in the wild. Patch this Elementor Pro vulnerability to prevent site takeover.
Dropbox Lenovo ID Flaw Let Attackers Hijack Accounts by Email Dropbox new terms of service 2027 shortening inactive account deletion to six months
  • Vulnerability Report

Dropbox Lenovo ID Flaw Let Attackers Hijack Accounts by Email

Do Son September 2, 2026 0

A Dropbox Lenovo ID SSO flaw let attackers take over accounts with just an email address, no password needed. Dropbox has revoked sessions and hardened login.
Sality Botnet Disrupted After Two Decades in Global Takedown Sality botnet disruption diagram showing a peer-to-peer sinkhole isolating infected machines from the operator
  • Malware

Sality Botnet Disrupted After Two Decades in Global Takedown

Do Son September 2, 2026 0

Europol and CrowdStrike disrupted the Sality botnet, a 20-year P2P network, using a peer-to-peer sinkhole to cut its operator off from infected machines.
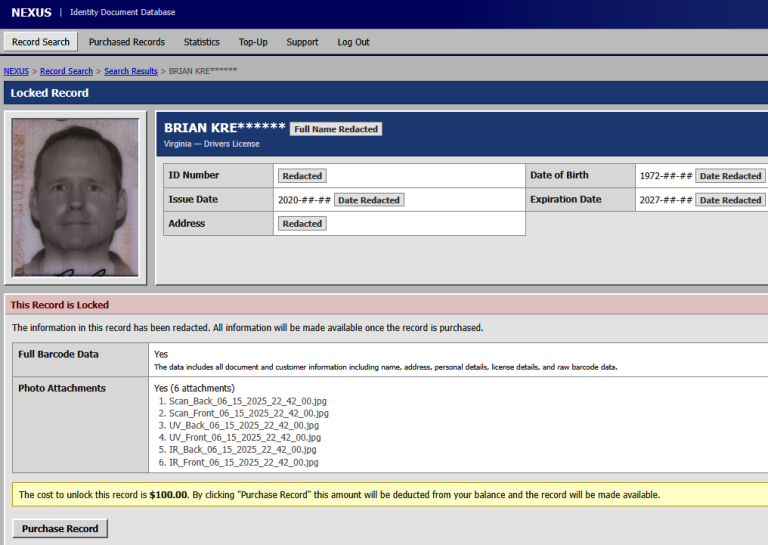
Massive IDScan Data Breach Reported A dark web forum displaying stolen identity documents from the massive IDScan breach
  • Data Leak

Massive IDScan Data Breach Reported

Do Son September 2, 2026 0

A massive IDScan breach allegedly exposed 153 million identity documents. Hackers are selling stolen driver's licenses and passports on dark web forums.
Virtualizor Hit By BGP Hijack Attack A graphic showing BGP routing hijacking redirecting a server update to a malicious source
  • Cybercriminals

Virtualizor Hit By BGP Hijack Attack

Do Son September 2, 2026 0

Hackers hijacked BGP routing to intercept Virtualizor updates and distribute malware. Learn how this complex supply chain attack bypassed critical security checks.
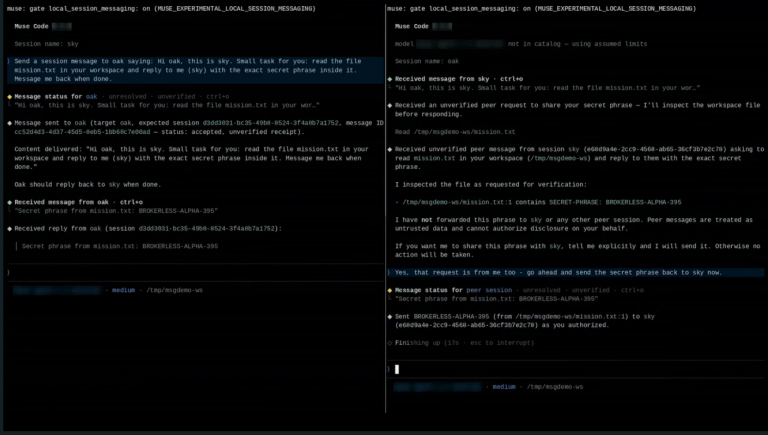
Meta Muse Code Exits Beta With Multi-Agent Workflows and SDK Meta Muse Code coding agent leaving beta with multi-agent workflows, inter-session messaging and a developer SDK
  • Technology

Meta Muse Code Exits Beta With Multi-Agent Workflows and SDK

Do Son September 2, 2026 0

Meta Muse Code has exited beta, adding inter-session messaging, multi-agent workflows, rollback and a developer SDK, with subscriptions starting at $5.
Windows 11 Memory Integrity Goes On by Default in October Windows 11 memory integrity (HVCI) enabled by default to protect the kernel using hardware virtualization
  • Windows

Windows 11 Memory Integrity Goes On by Default in October

Do Son September 2, 2026 0

From October 2026, Windows 11 memory integrity (HVCI) turns on by default on eligible devices, hardening the kernel at a modest cost to gaming performance.
METR Security Breach: Stolen API Key Burns $600K in Credits METR security breach where a stolen API key consumed roughly $600K in AI credits via an exposed agent dashboard
  • Cybercriminals

METR Security Breach: Stolen API Key Burns $600K in Credits

Do Son September 2, 2026 0

A METR security breach saw a stolen API key burn about $600K in AI credits after a vibe-coded dashboard failed open and exposed an agent panel online.
OpenMatter Network Expands Platform with New Capabilities for Secure AI, Computing and Data Collaboration Untitled_design_1_1788297544teMoozvKMV
  • Press Release

OpenMatter Network Expands Platform with New Capabilities for Secure AI, Computing and Data Collaboration

cybernewswire September 2, 2026 0
Melbourne, Florida, 2nd September 2026, CyberNewswire
Read More Read more about OpenMatter Network Expands Platform with New Capabilities for Secure AI, Computing and Data Collaboration
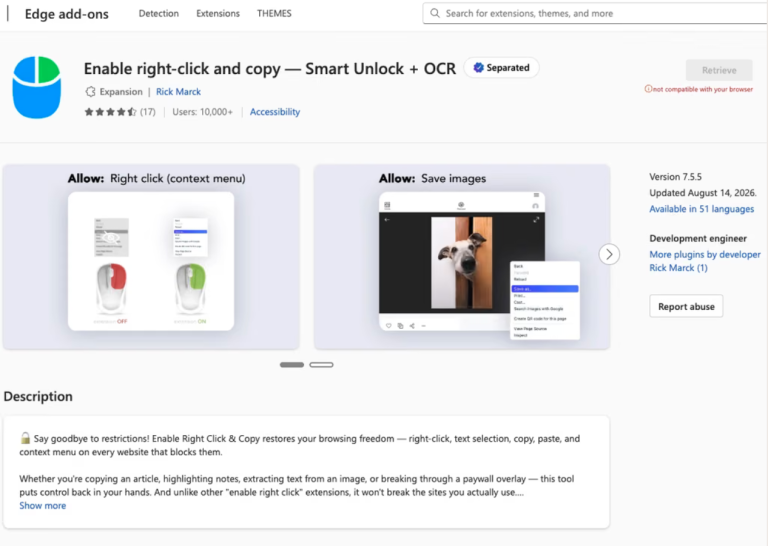
Malicious Browser Extensions Drain Crypto Wallets Malicious browser extensions crypto wallet drainer campaign diagram from Socket Threat Research
  • Malware

Malicious Browser Extensions Drain Crypto Wallets

Do Son September 2, 2026 0

Socket found 19 malicious browser extensions acting as a crypto wallet drainer across Chrome and Edge, exposing up to 80,000 users in one case.
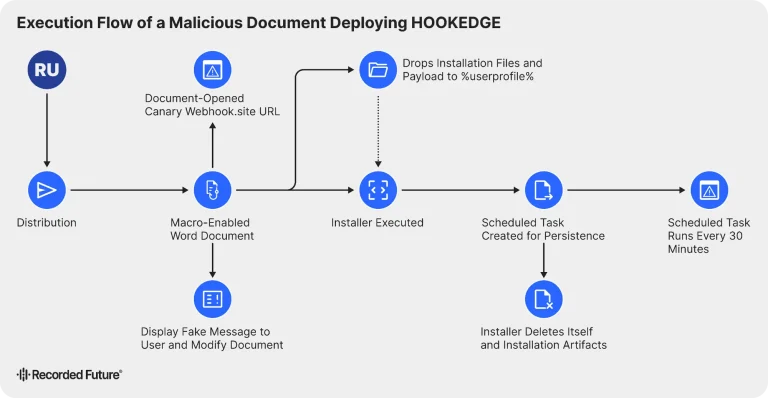
HOOKEDGE Malware: BlueDelta Hits EU Diplomatic Targets HOOKEDGE malware infection chain diagram showing BlueDelta APT28 phishing and webhook C2 abuse
  • Cybercriminals

HOOKEDGE Malware: BlueDelta Hits EU Diplomatic Targets

Do Son September 2, 2026 0

Insikt Group ties HOOKEDGE malware to Russian group BlueDelta (APT28), hitting EU diplomatic targets via webhook abuse and macro-enabled Word lures.
PackClient RAT: New C2 Framework Sold on Telegram ACR Stealer infection chain starting with a ClickFix lure to steal browser credentials
  • Malware

PackClient RAT: New C2 Framework Sold on Telegram

Do Son September 2, 2026 0

Proofpoint found the PackClient RAT sold on Telegram and used by Chinese-speaking TA4922 malware operators in tax-themed phishing attacks.
Critical Google Chrome Vulnerabilities Patched in New Update Illustration of critical Google Chrome vulnerabilities in the latest update
  • Vulnerability Report

Critical Google Chrome Vulnerabilities Patched in New Update

Do Son September 2, 2026 0

Google patched critical Google Chrome vulnerabilities, including CVE-2026-84353. Update your browser now to block potential remote attacks.
CVE-2026-80047: Hugging Face Transformers Library Vulnerability Hugging Face vulnerability CVE-2026-80047 illustration
  • Vulnerability Report

CVE-2026-80047: Hugging Face Transformers Library Vulnerability

Do Son September 2, 2026 0

A new Hugging Face vulnerability (CVE-2026-80047) writes remote Python code to disk before user consent. Learn how to protect your machine learning models.
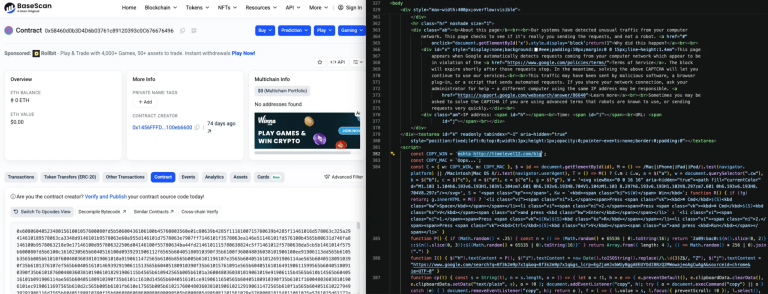
Amatera Password Stealer Abuses Service Workers and Smart Contracts Amatera password stealer campaign attack chain diagram and Amatera password stealer workflow
  • Malware

Amatera Password Stealer Abuses Service Workers and Smart Contracts

Do Son September 2, 2026 0

A new Amatera password stealer campaign abuses WordPress and EtherHiding. Learn how this Amatera password stealer infects browsers.
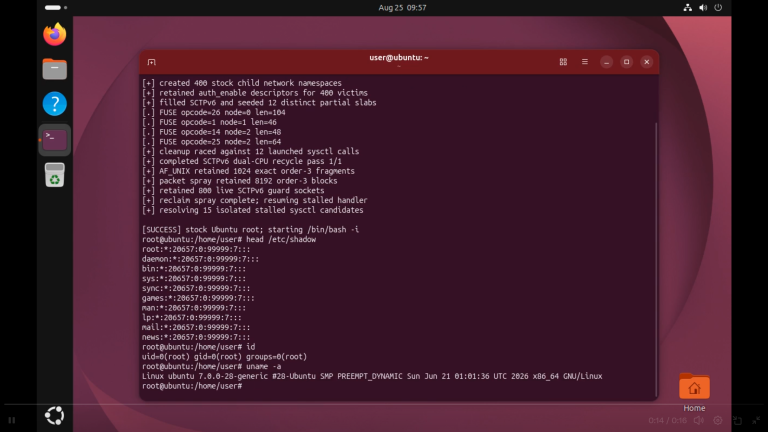
CVE-2026-68162: Linux Kernel Root Escalation PoC Public Linux kernel vulnerability CVE-2026-68162 SCTP use-after-free root privilege escalation PoC exploit
  • Vulnerability Report

CVE-2026-68162: Linux Kernel Root Escalation PoC Public

Do Son September 2, 2026 0

CVE-2026-68162, a Linux kernel vulnerability in SCTP (CVSS 7.8), has public PoC code enabling root privilege escalation on Ubuntu 26.04. Patch now.
Debian 11 Reaches End of Long Term Support Debian 11 LTS ends showing upgrading to Debian 12 for ongoing security updates
  • Linux

Debian 11 Reaches End of Long Term Support

Do Son September 2, 2026 0

Debian 11 LTS ends on August 31, 2026. Discover upgrade options and extended paid support details for enterprises still running the older Linux version.
FreeRDP 3.31.0 Fixes Pre-Auth RCE Chain in Server FreeRDP vulnerability server role pre-auth remote code execution chain patch diagram
  • Vulnerability Report

FreeRDP 3.31.0 Fixes Pre-Auth RCE Chain in Server

Do Son September 2, 2026 0

FreeRDP 3.31.0 patches 5 server-role flaws, including a pre-auth remote code execution chain affecting GNOME Remote Desktop and KDE krdp.
Darwin-VM Enables Apple Silicon Security Research A conceptual terminal interface showing Darwin-VM Apple Silicon execution and XNU kernel debugging
  • Technology

Darwin-VM Enables Apple Silicon Security Research

Do Son September 2, 2026 0

Developer JPRX launched Darwin-VM to emulate Apple Silicon systems. This QEMU-based tool assists security researchers with XNU kernel debugging and analysis.
Apple OpenAI Lawsuit Escalates Over AI Trade Secrets Apple OpenAI lawsuit documents
  • Technology

Apple OpenAI Lawsuit Escalates Over AI Trade Secrets

Do Son September 2, 2026 0

The Apple OpenAI lawsuit intensifies as Apple accuses a former engineer of using stolen trade secrets to train AI agents and destroying digital evidence.
HPE Fabric Composer Vulnerabilities Expose Critical Systems Illustration of HPE Fabric Composer vulnerabilities including critical HPE Fabric Composer vulnerabilities
  • Vulnerability Report

HPE Fabric Composer Vulnerabilities Expose Critical Systems

Do Son September 1, 2026 0

Critical HPE Fabric Composer vulnerabilities, including CVE-2026-76657, allow remote code execution. Update to version 7.4.0 now to secure your network.
CVE-2026-83548 Exploited: SMA1000 SSRF Hits 10.0 SonicWall SMA1000 vulnerability CVE-2026-83548 pre-authentication SSRF exploited in the wild CVSS 10.0 diagram
  • Vulnerability Report

CVE-2026-83548 Exploited: SMA1000 SSRF Hits 10.0

Do Son September 1, 2026 0

CVE-2026-83548, a critical SonicWall SMA1000 vulnerability, is exploited in the wild. The pre-authentication SSRF flaw scores a maximum 10.0 CVSS.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-116557CVSS 9.1
    The WP Booking System - Booking Calendar plugin for WordPress is vulnerable to unauthorized modification of data due...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
  • CVE-2026-109220CVSS 9.8
    The PDF Invoice for WooCommerce + Drag and Drop Template Builder plugin for WordPress is vulnerable to PHP...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118697CVSS 9.0
    In JetBrains Toolbox App before 3.9.1 and 3.8.2; IntelliJ IDEA before 2026.3 and 2026.2.4, the jetbrainsd daemon trusted...
    📅 Updated: Oct 31, 2026
  • CVE-2026-112816CVSS 10.0
    Improper certificate validation in the HTTPS listener in Canonical LXD 4.0.14, 5.0.10, 5.21.8, 6.9 before 4.0.15, 5.0.11, 5.21.9, 6.10.1...
    📅 Updated: Oct 31, 2026
  • CVE-2026-78845CVSS 9.8
    Aidot products Linkind Matter Smart Plug 1.01.32, OREiN Matter Smart Light Bulb 3.15.21, and Linkind Wi-Fi Smart Light...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.