Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Browser Isolation Bypassed: QR Codes Used in Novel C2 Attacks QR-Code
  • Cyber Security
  • Vulnerability

Browser Isolation Bypassed: QR Codes Used in Novel C2 Attacks

Do Son December 5, 2024 0

Explore the vulnerabilities of browser isolation technology and learn about an innovative method for attackers to bypass it using QR codes.

Phishing, Fraud, and Stolen Data: Europol Takes Down Cybercrime Network Fraudulent shopping sites
  • Cyber Security

Phishing, Fraud, and Stolen Data: Europol Takes Down Cybercrime Network

Do Son December 5, 2024 0

Europol announces successful dismantling of a major online fraud network. Learn how they disrupted the trade of stolen data and arrested key suspects.

CVE-2024-43222 (CVSS 9.8): Critical Flaw in Sweet Date WordPress Theme Exposes Thousands of Sites to Potential Takeovers CVE-2024-43222
  • Vulnerability

CVE-2024-43222 (CVSS 9.8): Critical Flaw in Sweet Date WordPress Theme Exposes Thousands of Sites to Potential Takeovers

Do Son December 5, 2024 0

Stay informed about the flaw (CVE-2024-43222) in the Sweet Date WordPress theme. Learn how to secure your website and prevent unauthorized access

iVerify Unveils Disturbing Prevalence of Pegasus Spyware on Mobile Devices Pegasus spyware sample
  • Malware

iVerify Unveils Disturbing Prevalence of Pegasus Spyware on Mobile Devices

Do Son December 5, 2024 0

Discover the shocking prevalence of the notorious Pegasus spyware in mobile devices. iVerify's investigation reveals seven infections in a sample of 2,500 devices.

Multiple Vulnerabilities in SonicWall SMA 100 Could Lead to Remote Code Execution SonicWall ES RCE, Code Integrity Bypass SonicWall SMA, Arbitrary File Upload SonicWall SMA100 - CVE-2024-40764
  • Vulnerability

Multiple Vulnerabilities in SonicWall SMA 100 Could Lead to Remote Code Execution

Do Son December 5, 2024 0

Discover the vulnerabilities impacting SonicWall SMA 100 series SSL-VPN products. Find out how these flaws can lead to remote code execution and data breaches.

Russian Hacker Secret Blizzard Hijack C2 Infrastructure in New Espionage Campaign Secret Blizzard
  • Cyber Security
  • Malware

Russian Hacker Secret Blizzard Hijack C2 Infrastructure in New Espionage Campaign

Do Son December 5, 2024 0

Uncover the secrets of Secret Blizzard, a Russian threat actor known for hijacking other groups' infrastructure for intelligence gathering.

CVE-2024-53990 (CVSS 9.2): AsyncHttpClient Vulnerability Puts Java Applications at Risk CVE-2024-53990
  • Vulnerability

CVE-2024-53990 (CVSS 9.2): AsyncHttpClient Vulnerability Puts Java Applications at Risk

Do Son December 5, 2024 0

Learn about CVE-2024-53990, a critical vulnerability in AsyncHttpClient. Discover how attackers could exploit user sessions and gain unauthorized access to sensitive data.
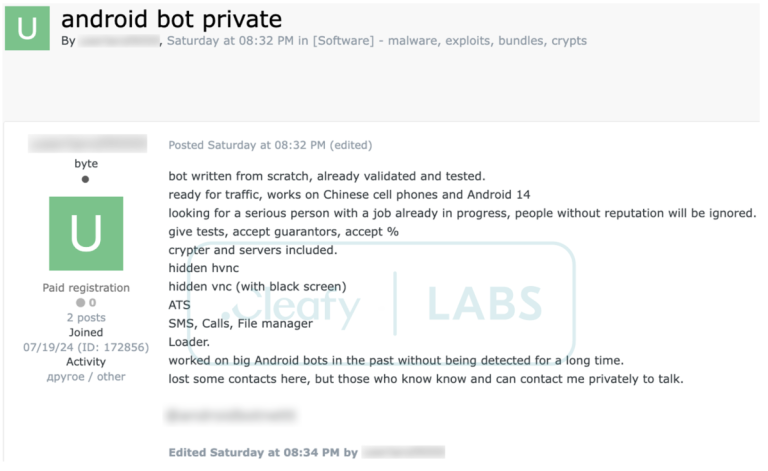
DroidBot: A New Android Threat Exposes Global Financial Institutions Forum post advertising a new Android bot
  • Malware

DroidBot: A New Android Threat Exposes Global Financial Institutions

Do Son December 5, 2024 0

Dive into the world of mobile malware with DroidBot, a powerful Android RAT that combines hidden VNC, overlay attacks, and keylogging capabilities.

Black Basta Resurgence: Social Engineering Campaign Delivers Zbot, DarkGate, and Custom Malware Screenshot 2024-12-05 145929
  • Malware

Black Basta Resurgence: Social Engineering Campaign Delivers Zbot, DarkGate, and Custom Malware

Do Son December 5, 2024 0

The threat actors have refined their techniques, introducing novel methods for gaining access and delivering malware, including Zbot, DarkGate
Fake DocuSign Emails: Don’t Get Hooked by Phishing Scams BiDi Swap, phishing attacks Cybersecurity Threats
  • Cyber Security

Fake DocuSign Emails: Don’t Get Hooked by Phishing Scams

Do Son December 5, 2024 0

Stay informed about the latest DocuSign phishing attacks. Learn how cybercriminals are targeting users and stealing sensitive credentials.

How an Intranet Can Enhance Business Security cybersecurity Advertise
  • Technique

How an Intranet Can Enhance Business Security

Do Son December 5, 2024 0
Security is a paramount concern that impacts all facets of business operations. An intranet, as a restricted...
Read More Read more about How an Intranet Can Enhance Business Security
Veeam Backup & Replication Vulnerabilities Exposed: High-Severity Flaws Put Data at Risk Veeam Backup vulnerability remote code execution Veeam Backup vulnerability Veeam Vulnerabilities CVE-2024-42448 & CVE-2024-42449
  • Vulnerability

Veeam Backup & Replication Vulnerabilities Exposed: High-Severity Flaws Put Data at Risk

Do Son December 4, 2024 0

Stay up to date with the latest Veeam Backup & Replication vulnerabilities. Learn how these security issues can compromise your systems and what steps you can take to mitigate the risks.

Five Flaws in Lorex 2K Security Cameras Enable Hackers to Take Full Control, PoC Published Lorex 2K Indoor Wi-Fi Security Camera - CVE-2024-52544
  • Vulnerability

Five Flaws in Lorex 2K Security Cameras Enable Hackers to Take Full Control, PoC Published

Do Son December 4, 2024 0

Critical vulnerabilities in the Lorex 2K Indoor Wi-Fi Security Camera uncovered! Learn how attackers can compromise the devices and execute remote code.

CVE-2024-10905 (CVSS 10): Critical Vulnerability in SailPoint IdentityIQ Exposes Sensitive Data CVE-2024-10905
  • Vulnerability

CVE-2024-10905 (CVSS 10): Critical Vulnerability in SailPoint IdentityIQ Exposes Sensitive Data

Do Son December 4, 2024 0

Learn about the critical vulnerability in SailPoint IdentityIQ (CVE-2024-10905) and its potential impact on organizations.

Fuji Electric Indonesia Suffers Ransomware Attack: Business Partner Data Potentially Leaked critical server patch Pygmy Goat malware - Fuji Electric Ransomware Attack
  • Cyber Security
  • Data Leak

Fuji Electric Indonesia Suffers Ransomware Attack: Business Partner Data Potentially Leaked

Do Son December 4, 2024 0

Fuji Electric's subsidiary, Fuji Electric Indonesia, suffers ransomware attack leading to system shutdown and potential data leaks.

CVE-2024-51378 (CVSS 10): Critical CyberPanel Flaw Under Active Attack, CISA Warns CVE-2024-51378 vulnerability
  • Vulnerability

CVE-2024-51378 (CVSS 10): Critical CyberPanel Flaw Under Active Attack, CISA Warns

Do Son December 4, 2024 0

Stay informed about the latest cyber threat: CVE-2024-51378 vulnerability in CyberPanel exploited by attackers to deploy ransomware and compromise systems.

Exploit Code Available: Critical Flaw Found in WhatsUp Gold- CVE-2024-8785 (CVSS 9.8) Sitefinity critical vulnerabilities Sitefinity security update CVE-2024-7763 - CVE-2024-8785 exploit CVE-2025-1758
  • Vulnerability

Exploit Code Available: Critical Flaw Found in WhatsUp Gold- CVE-2024-8785 (CVSS 9.8)

Do Son December 4, 2024 0

Uncover the details of the CVE-2024-8785 exploit in WhatsUp Gold. Find out how an unauthenticated remote attacker can gain control through registry modifications and what you can do to mitigate the risk.

FBI Warns of Generative AI’s Role in Amplifying Fraud Schemes AI Fraud Schemes TAMECAT Malware APT42 Espionage
  • Cyber Security

FBI Warns of Generative AI’s Role in Amplifying Fraud Schemes

Do Son December 4, 2024 0

Stay informed about the latest AI fraud schemes and how criminals are leveraging generative AI technology to deceive victims.

Payroll Pirates: Unveiling the Sophisticated Payroll Redirection Phishing Campaign Payroll Pirates
  • Cyber Security

Payroll Pirates: Unveiling the Sophisticated Payroll Redirection Phishing Campaign

Do Son December 4, 2024 0

Uncover the alarming 'Payroll Pirates' phishing campaign targeting HR portals. Learn how threat actors are redirecting payroll funds and exploiting employee information.

NCA’s Operation Destabilise: Dismantling a Global Money Laundering Network Operation Destabilise
  • Cyber Security

NCA’s Operation Destabilise: Dismantling a Global Money Laundering Network

Do Son December 4, 2024 0

The NCA disrupts a large-scale money laundering network in Operation Destabilise. Discover the interconnected threat landscape created by Russian elites, cybercriminals, and organized crime groups.

New Andromeda/Gamarue Command-and-Control Cluster Targets APAC Industries Andromeda malware
  • Malware

New Andromeda/Gamarue Command-and-Control Cluster Targets APAC Industries

Do Son December 4, 2024 0

Learn about the latest discovery of a new cluster of Andromeda malware servers and its targeted activities in the APAC region.

Akira v2 Emerges: Rust-Based Ransomware Raises the Stakes Akira ransomware v2
  • Malware

Akira v2 Emerges: Rust-Based Ransomware Raises the Stakes

Do Son December 4, 2024 0

Discover the strategic evolution of Akira ransomware with the introduction of Akira v2, a Rust-based variant. Learn how its use of Rust enhances its complexity and cross-platform capabilities.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124917CVSS 9.6
    Sandbox escape due to use-after-free in the Widget: Gtk component. This vulnerability was fixed in Firefox 160 and...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124900CVSS 9.6
    Sandbox escape due to use-after-free in the DOM: Service Workers component. This vulnerability was fixed in Firefox 160.
    📅 Updated: Nov 10, 2026
  • CVE-2026-124903CVSS 9.6
    Sandbox escape due to use-after-free in the IPC component. This vulnerability was fixed in Firefox 160, Firefox ESR...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124864CVSS 9.6
    Sandbox escape due to use-after-free in the DOM: Service Workers component. This vulnerability was fixed in Firefox 160,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124859CVSS 9.6
    Sandbox escape due to incorrect boundary conditions in the Storage: Cache API component. This vulnerability was fixed in...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124861CVSS 9.6
    Sandbox escape due to use-after-free in the Audio/Video: cubeb component. This vulnerability was fixed in Firefox 160, Firefox...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.