Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Phishing Frenzy: Cloudflare Domains Exploited in Latest Attacks Cloudflare phishing
  • Cyber Security

Phishing Frenzy: Cloudflare Domains Exploited in Latest Attacks

Do Son December 4, 2024 0

Discover the alarming increase in Cloudflare phishing attacks. Learn how cybercriminals are exploiting trusted domains for their malicious schemes.
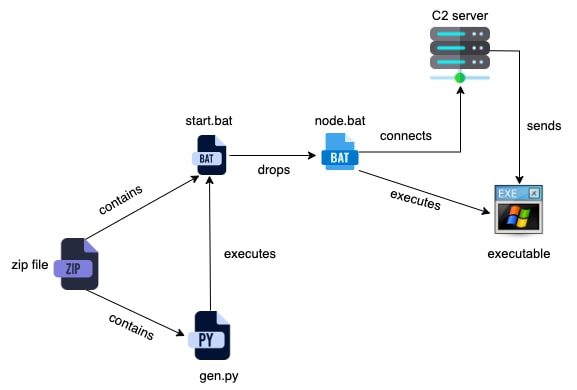
Beware of Celestial Stealer: New MaaS Targets Browsers and Crypto Wallets Celestial Stealer
  • Malware

Beware of Celestial Stealer: New MaaS Targets Browsers and Crypto Wallets

Do Son December 4, 2024 0

Unveiling the inner workings of Celestial Stealer: a powerful infostealer disguised as legitimate applications, targeting developers, gamers, and cryptocurrency users.
Cyberattack Compromises Marin City Housing Project, $950,000 in Public Funds Stolen Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Cyber Security

Cyberattack Compromises Marin City Housing Project, $950,000 in Public Funds Stolen

Do Son December 4, 2024 0

Marin City cyberattack: $950,000 of public funds stolen from Golden Gate Village housing project. Find out how phishing techniques were used in this incident.

DMM Bitcoin Ceases Operations Following $300 Million Cyberattack, Attributed to Lazarus Group CMDSS ZachXBT crypto theft, John Daghita U.S. Marshals investigation Bitfinex Hacker - DMM Bitcoin Cyberattack
  • Cyber Security

DMM Bitcoin Ceases Operations Following $300 Million Cyberattack, Attributed to Lazarus Group

Do Son December 4, 2024 0

Learn about the cybersecurity incident that led to the closure of DMM Bitcoin, a Japanese cryptocurrency exchange. Find out more about the unauthorized transfer of millions of dollars worth of Bitcoins.

RECOPE, Costa Rica’s State-Owned Energy Provider, Grapples with Ransomware Attack and Fuel Supply Disruption AI ransomware, PromptLock Against Ransomware - RECOPE Ransomware Attack
  • Cyber Security
  • Malware

RECOPE, Costa Rica’s State-Owned Energy Provider, Grapples with Ransomware Attack and Fuel Supply Disruption

Do Son December 4, 2024 0

Discover the impact of the RECOPE ransomware attack on Costa Rica's fuel supply chain. Learn about the challenges faced and potential fuel shortages.

Crypto.com Launches $2 Million Bug Bounty Program with HackerOne Crypto Bug Bounty Program
  • Technology

Crypto.com Launches $2 Million Bug Bounty Program with HackerOne

Do Son December 4, 2024 0

Learn about Crypto.com's upgraded bug bounty program, offering a record-breaking $2 million reward pool for identifying potential vulnerabilities.

I-O DATA Routers Under Attack: Urgent Firmware Update Needed! Cisco SD-WAN Vulnerability CVE-2026-20133 FortiGate Compromise Ivanti EPMM Zero-Day CVE-2026-1281 SmarterMail Vulnerability Storm-2603 WatchGuard Zero-Day, IKEv2 Out-of-Bounds Write Cisco Zero-Day, UAT-9686 Chinese APT FortiWeb RCE Exploitation CVE-2025-58034 VMware Zero-Day, Privilege Escalation Sitecore, remote code execution CVE-2025-53690 Windows CLFS, Privilege Escalation CVE-2024-47575 & CVE-2024-11120 CVE-2025-24983 vulnerability
  • Vulnerability

I-O DATA Routers Under Attack: Urgent Firmware Update Needed!

Do Son December 3, 2024 0

Protect your I-O DATA router from CVE-2024-45841 and other vulnerabilities. Learn how to secure your device and prevent credential theft and command execution.

Microsoft Emphasizes TPM 2.0 as a “Necessity” for Secure Windows 11 Deployment Windows 11 TPM 2.0
  • Technology
  • Windows

Microsoft Emphasizes TPM 2.0 as a “Necessity” for Secure Windows 11 Deployment

Do Son December 3, 2024 0

Discover the importance of TPM 2.0 for Windows 11 security. Learn how TPM 2.0 provides hardware-level protection for sensitive data and enhances key management.

PoC Exploit Releases for Critical Zabbix Vulnerability – CVE-2024-42327 (CVSS 9.9) Screenshot 2024-12-03 172203
  • Vulnerability

PoC Exploit Releases for Critical Zabbix Vulnerability – CVE-2024-42327 (CVSS 9.9)

Do Son December 3, 2024 0

Security researcher Alejandro Ramos has published a detailed technical analysis and proof-of-concept (PoC) exploit code for CVE-2024-42327

Solana Web3.js Library Compromised in Targeted Supply Chain Attack Solana Web3.js Supply Chain Attack
  • Malware

Solana Web3.js Library Compromised in Targeted Supply Chain Attack

Do Son December 3, 2024 0

Warning: Security alert for Solana Web3.js users! Learn about a recent supply chain attack on the widely-used JavaScript library and how it puts developers and users at risk.

CVE-2024-42448 (CVSS 9.9): Critical RCE Vulnerability in Veeam VSPC Veeam Backup vulnerability remote code execution Veeam Backup vulnerability Veeam Vulnerabilities CVE-2024-42448 & CVE-2024-42449
  • Vulnerability

CVE-2024-42448 (CVSS 9.9): Critical RCE Vulnerability in Veeam VSPC

Do Son December 3, 2024 0

Stay informed about the critical CVE-2024-42448 vulnerability in Veeam's Service Provider Console (VSPC). Understand the risks and take necessary security measures.

PoC Confirms Root Privilege Exploit in TP-Link Archer AXE75 Vulnerability (CVE-2024-53375) CVE-2024-53375 PoC exploit
  • Vulnerability

PoC Confirms Root Privilege Exploit in TP-Link Archer AXE75 Vulnerability (CVE-2024-53375)

Do Son December 3, 2024 0

Protect your TP-Link Archer AXE75 router from CVE-2024-53375. Learn about the flaw that allows remote execution of arbitrary commands and steps to secure your device.
CISA Flags Three Actively Exploited Vulnerabilities in Critical Systems CISA KEV Catalog Updates Langflow CVE-2025-34291 Exploit SharePoint Spoofing CISA KEV Catalog Actively Exploited Vulnerability
  • Vulnerability

CISA Flags Three Actively Exploited Vulnerabilities in Critical Systems

Do Son December 3, 2024 0

Stay informed about the latest critical security flaws actively exploited in the wild. Learn about CVE-2023-45727, CVE-2024-11680, and CVE-2024-11667.

Threat Actors Exploiting Misconfigured Docker Remote API Servers with Gafgyt Malware CVE-2024-21626
  • Malware

Threat Actors Exploiting Misconfigured Docker Remote API Servers with Gafgyt Malware

Do Son December 3, 2024 0

Discover the new target of Gafgyt malware: misconfigured Docker Remote API servers. Learn how attackers exploit these servers and deploy the malware.

Google Chrome Addresses High-Severity Flaw in V8 JavaScript Engine (CVE-2024-12053) CVE-2024-12053
  • Vulnerability

Google Chrome Addresses High-Severity Flaw in V8 JavaScript Engine (CVE-2024-12053)

Do Son December 3, 2024 0

Find out how Google Chrome's latest update enhances your security. Learn about the high-severity vulnerability (CVE-2024-12053) and how it can be patched.

Protect Your Network: Zyxel Issues Firmware Updates CVE-2023-33009 & CVE-2024-8748 - CVE-2024-9200
  • Vulnerability

Protect Your Network: Zyxel Issues Firmware Updates

Do Son December 3, 2024 0

Protect your Zyxel networking devices from potential attacks. Find out how to patch vulnerabilities like CVE-2024-8748 and CVE-2024-9200.

Cisco Confirms Active Exploitation of Decade-Old WebVPN Vulnerability in ASA Software FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Vulnerability

Cisco Confirms Active Exploitation of Decade-Old WebVPN Vulnerability in ASA Software

Do Son December 3, 2024 0

Stay protected from CVE-2014-2120 vulnerability in Cisco ASA Software. Learn how to mitigate the risks of cross-site scripting attacks on WebVPN users.

Critical Vulnerabilities in mySCADA myPRO Software Pose Significant Risk to Industrial Control Systems mySCADA myPRO Vulnerabilities
  • Vulnerability

Critical Vulnerabilities in mySCADA myPRO Software Pose Significant Risk to Industrial Control Systems

Do Son December 3, 2024 0

Discover the critical vulnerabilities in mySCADA's myPRO software, exposing industrial infrastructure to unauthorized access and control.

Surprise Exit: Gelsinger Retires from Intel After 40 Years CEO Pat Gelsinger
  • Technology

Surprise Exit: Gelsinger Retires from Intel After 40 Years

Do Son December 3, 2024 0

The retirement of Intel CEO Pat Gelsinger marks the end of an era for the semiconductor giant. Discover the impact he made during his 40+ year career.

Zero-Day Exploit Code Released for Windows Task Scheduler Flaw (CVE-2024-49039), Actively Exploited by RomCom Group CVE-2024-49039 PoC exploit
  • Vulnerability

Zero-Day Exploit Code Released for Windows Task Scheduler Flaw (CVE-2024-49039), Actively Exploited by RomCom Group

Do Son December 2, 2024 0

A proof-of-concept (PoC) exploit code for CVE-2024-49039, a zero-day vulnerability in Windows Task Scheduler, has been publicly released

KrbRelayEx: A Kerberos Relaying Tool for Penetration Testing Kerberos Relaying
  • Open Source Tool

KrbRelayEx: A Kerberos Relaying Tool for Penetration Testing

Do Son December 2, 2024 0

Discover the powerful technique of Kerberos relaying and its implications for Active Directory security. Learn how KrbRelayEx tool can help assess vulnerabilities in Windows networks.

Google Chrome Enhances User Security with AI-Powered Website Reviews Google Chrome Reviews
  • Technology

Google Chrome Enhances User Security with AI-Powered Website Reviews

Do Son December 2, 2024 0

Discover Google Chrome's new AI-driven feature: Store Reviews. Find out how it helps users assess website trustworthiness and avoid fraudulent online vendors.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124917CVSS 9.6
    Sandbox escape due to use-after-free in the Widget: Gtk component. This vulnerability was fixed in Firefox 160 and...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124900CVSS 9.6
    Sandbox escape due to use-after-free in the DOM: Service Workers component. This vulnerability was fixed in Firefox 160.
    📅 Updated: Nov 10, 2026
  • CVE-2026-124903CVSS 9.6
    Sandbox escape due to use-after-free in the IPC component. This vulnerability was fixed in Firefox 160, Firefox ESR...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124864CVSS 9.6
    Sandbox escape due to use-after-free in the DOM: Service Workers component. This vulnerability was fixed in Firefox 160,...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124859CVSS 9.6
    Sandbox escape due to incorrect boundary conditions in the Storage: Cache API component. This vulnerability was fixed in...
    📅 Updated: Nov 10, 2026
  • CVE-2026-124861CVSS 9.6
    Sandbox escape due to use-after-free in the Audio/Video: cubeb component. This vulnerability was fixed in Firefox 160, Firefox...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.