Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Malware

FrostyGoop: New ICS Malware Exploits Modbus TCP Protocol

Do Son November 20, 2024 0

Learn about FrostyGoop, an alarming ICS-centric malware that exploits vulnerabilities in internet-exposed devices.

LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms PromptMink Campaign AI Agent Deception LIMINAL PANDA UNC1549 DLL Hijacking, VDI Breakout
  • Cyber Security

LIMINAL PANDA – A Chinese State-Sponsored Espionage Targeting Telecoms

Do Son November 20, 2024 0

Learn about LIMINAL PANDA, a new China-nexus state-sponsored adversary targeting telecommunications providers and posing a cyber threat to critical infrastructure.

Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution Veritas Enterprise Vault server CVE-2025-27816
  • Vulnerability

Veritas Enterprise Vault Vulnerability Could Allow Remote Code Execution

Do Son November 20, 2024 0

Stay informed about the critical remote code execution vulnerability affecting Veritas Enterprise Vault servers and learn how to protect your organization.

New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming Exploited VMware
  • Cyber Security

New Attack Vector: Misconfigured Jupyter Servers Targeted for Illegal Streaming

Do Son November 20, 2024 0

Discover the alarming rise of misconfigured JupyterLab servers and how threat actors exploit them for illegal live sports streaming.

Ruckus Networks Issues Security Advisory for Critical RCE Vulnerability in Access Points libheif Vulnerability CVE-2025-65586 Trend Micro RCE CVE-2025-69258 SessionReaper CVE-2025-54236 VS Code Marketplace, supply chain attack npm Supply Chain, Toptal Compromise Ruckus AP Vulnerability
  • Vulnerability

Ruckus Networks Issues Security Advisory for Critical RCE Vulnerability in Access Points

Do Son November 20, 2024 0

Stay secure with Ruckus APs. Discover the critical vulnerability that allows unauthenticated remote code execution attacks and how to protect your network.

35,000 Bots, 180 Countries: Inside the Criminal Network of the NSOCKS Botnet NSOCKS botnet
  • Malware

35,000 Bots, 180 Countries: Inside the Criminal Network of the NSOCKS Botnet

Do Son November 20, 2024 0

Discover the scale and sophistication of the NSOCKS botnet: a criminal proxy network aiding in DDoS attacks, phishing, and malware obfuscation.

Critical Vulnerability in D-Link EOL Routers Allows Remote Code Execution D-Link Vulnerability - End-of-Life Routers
  • Vulnerability

Critical Vulnerability in D-Link EOL Routers Allows Remote Code Execution

Do Son November 20, 2024 0

Learn about the D-Link vulnerability affecting several router models and the potential risks of unauthenticated users executing remote code.

“Ghost Tap” Emerges: Cybercriminals Exploit NFC Relay for Contactless Cash-Outs Ghost Tap
  • Cyber Security

“Ghost Tap” Emerges: Cybercriminals Exploit NFC Relay for Contactless Cash-Outs

Do Son November 20, 2024 0

Discover the new Ghost Tap tactic in financial cybercrime. Criminals exploit mobile payment services to anonymously cash out stolen credit cards.
Kaspersky Lab’s Report Reveals Surge in Black Friday Shopping Threats BiDi Swap, phishing attacks Cybersecurity Threats
  • Cyber Security

Kaspersky Lab’s Report Reveals Surge in Black Friday Shopping Threats

Do Son November 20, 2024 0

Stay safe while shopping on Black Friday. Learn about the cybercriminal tactics used to exploit consumers and businesses during peak shopping seasons.

Five Critical Privilege Escalation Vulnerabilities Found in Ubuntu’s Default Utility, needrestart CVE-2024-48990 and CVE-2024-48922
  • Linux
  • Vulnerability

Five Critical Privilege Escalation Vulnerabilities Found in Ubuntu’s Default Utility, needrestart

Do Son November 20, 2024 0

Discover the severity of CVE-2024-48990 and other critical vulnerabilities in the needrestart utility. Explore how unprivileged users can exploit these flaws to gain root access.
CVE-2024-51503: Trend Micro Deep Security Agent RCE Vulnerability Fixed Trend Micro Apex One CVE-2025-71210 AI Security Trend Micro Deep Security - CVE-2024-48904 & CVE-2024-51503
  • Vulnerability

CVE-2024-51503: Trend Micro Deep Security Agent RCE Vulnerability Fixed

Do Son November 20, 2024 0

Discover the details of the CVE-2024-51503 vulnerability in Trend Micro Deep Security and the potential impact on affected systems.

Why Are Cyber Security Promotional Campaigns Necessary for Cybersecurity Companies? BlackByte Ransomware Group
  • Technique

Why Are Cyber Security Promotional Campaigns Necessary for Cybersecurity Companies?

Do Son November 20, 2024 0
The cybersecurity employment market is at a record-high level, and it is only going to get bigger...
Read More Read more about Why Are Cyber Security Promotional Campaigns Necessary for Cybersecurity Companies?
Analysis & PoC Exploits Released for Palo Alto Zero-Days – CVE-2024-0012 and CVE-2024-9474 PoC
  • Vulnerability

Analysis & PoC Exploits Released for Palo Alto Zero-Days – CVE-2024-0012 and CVE-2024-9474

Do Son November 19, 2024 0

Security researcher Valentin Lobstein has developed and released PoC exploit code for CVE-2024-0012 & CVE-2024-9474, enabling effortless exploitation

CVE-2024-21697: High Severity Flaw in Sourcetree Enables Remote Code Execution Sourcetree - CVE-2024-21697
  • Vulnerability

CVE-2024-21697: High Severity Flaw in Sourcetree Enables Remote Code Execution

Do Son November 19, 2024 0

Critical security vulnerability in Atlassian Sourcetree software (CVE-2024-21697). Learn how an unauthenticated attacker can execute arbitrary code.
Google Chrome Patches High-Severity Flaw CVE-2024-11395 in Latest Stable Release CVE-2024-11395
  • Vulnerability

Google Chrome Patches High-Severity Flaw CVE-2024-11395 in Latest Stable Release

Do Son November 19, 2024 0

Protect your system from security risks with the new Chrome browser update. Learn about the high-severity CVE-2024-11395 vulnerability and its potential impact.
CVE-2024-21287: Critical Zero-Day Exploited in Oracle Agile PLM Oracle Agile PLM - CVE-2024-21287
  • Vulnerability

CVE-2024-21287: Critical Zero-Day Exploited in Oracle Agile PLM

Do Son November 19, 2024 0

Urgent security alert: Oracle Agile PLM software vulnerability (CVE-2024-21287) exposes critical business information. Take action now!

Gabagool: A Sophisticated Phishing Kit Exploiting Cloudflare R2 Gabagool Phishing Kit
  • Cyber Security

Gabagool: A Sophisticated Phishing Kit Exploiting Cloudflare R2

Do Son November 19, 2024 0

Discover the Gabagool phishing kit that targets corporate and government employees. Learn how it leverages Cloudflare's R2 storage service to bypass security measures.

CVE-2024-47533 (CVSS 9.8): Cobbler Vulnerability Exposes Linux Servers to Compromise CVE-2024-47533
  • Vulnerability

CVE-2024-47533 (CVSS 9.8): Cobbler Vulnerability Exposes Linux Servers to Compromise

Do Son November 19, 2024 0

CVE-2024-47533 exposes Cobbler servers to unauthorized access and control, enabling attackers to manipulate system configurations.

CVE-2024-42057: Exploited by Helldown Ransomware to Target Linux Helldown ransomware Linux
  • Malware
  • Vulnerability

CVE-2024-42057: Exploited by Helldown Ransomware to Target Linux

Do Son November 19, 2024 0

Explore the rising threat of the Helldown ransomware targeting Linux machines. Find out how Sekoia's TDR team uncovered this new variant.

Bitwarden Users Targeted in Malicious Facebook Ad Campaign Bitwarden browser extension
  • Malware

Bitwarden Users Targeted in Malicious Facebook Ad Campaign

Do Son November 19, 2024 0

Stay vigilant! A malvertising campaign is spreading malware disguised as a Bitwarden security update. Read to learn how to avoid falling victim.

Wget Vulnerability (CVE-2024-10524) Opens Door to SSRF Attacks CVE-2024-10524
  • Vulnerability

Wget Vulnerability (CVE-2024-10524) Opens Door to SSRF Attacks

Do Son November 19, 2024 0

Discover the CVE-2024-10524 vulnerability in Wget and learn how attackers can exploit it to launch server-side request forgery attacks.
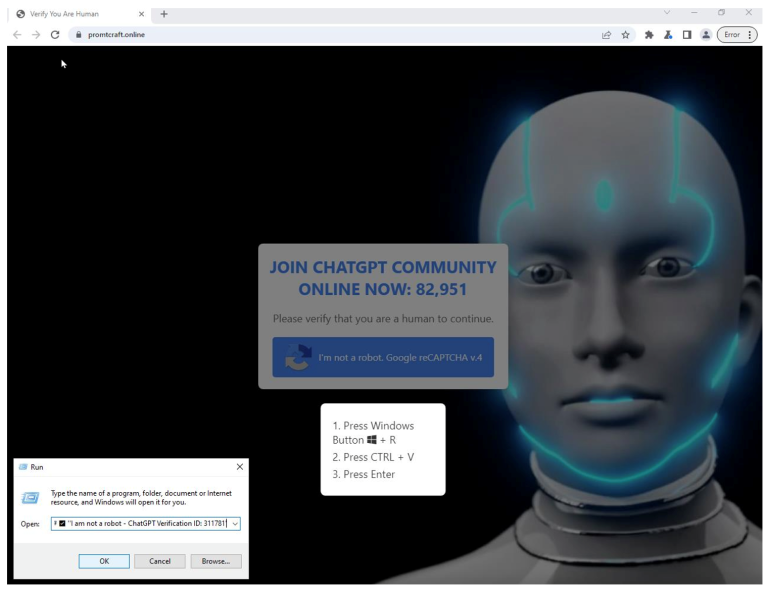
ClickFix: The Rising Threat of Clipboard-Based Social Engineering ChatGPT impersonation used in ClickFix payload delivery
  • Malware

ClickFix: The Rising Threat of Clipboard-Based Social Engineering

Do Son November 19, 2024 0

Discover the alarming rise of ClickFix, a unique social engineering method used to spread malware. Learn how it exploits human behavior and how to protect yourself.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.