Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2024-47208 & CVE-2024-48962: Apache OFBiz Exposed to Remote Code Execution Apache OFBiz RCE, Unrestricted File Upload CVE-2024-47208 and CVE-2024-48962
  • Vulnerability

CVE-2024-47208 & CVE-2024-48962: Apache OFBiz Exposed to Remote Code Execution

Do Son November 19, 2024 0

Urgent security updates for Apache OFBiz: Learn about the critical vulnerabilities (CVE-2024-47208 and CVE-2024-48962) and how they can compromise your business.

DONOT APT Group Targets Pakistan’s Maritime and Defense Sectors in New Campaign DONOT APT group
  • Cyber Security

DONOT APT Group Targets Pakistan’s Maritime and Defense Sectors in New Campaign

Do Son November 19, 2024 0

Uncover the latest campaign by the DONOT APT group targeting Pakistan's maritime and defense manufacturing sectors with advanced tactics.

CVE-2024-44308 and CVE-2024-44309: Apple Addresses Zero-Day Vulnerabilities DarkSword exploit kit iOS 18.7.7 security update CVE-2024-44308 & CVE-2024-44309 Apple appeal, Epic Games lawsuit
  • Vulnerability

CVE-2024-44308 and CVE-2024-44309: Apple Addresses Zero-Day Vulnerabilities

Do Son November 19, 2024 0

Update your Apple devices now! Two critical zero-day vulnerabilities, CVE-2024-44308 and CVE-2024-44309, leave your iPhones, iPads, Macs vulnerable to attacks.
CISA Warns of Actively Exploited Vulnerabilities in Kemp LoadMaster and Palo Alto Networks PAN-OS State-Sponsored Exploitation CISA KEV Catalog F5 BIG-IP RCE CISA KEV Catalog SolarWinds WHD Exploit CVE-2025-40551 Zimbra XSS Zero-Day CVE-2025-27915 Exploited Windows Security Vulnerabilities
  • Vulnerability

CISA Warns of Actively Exploited Vulnerabilities in Kemp LoadMaster and Palo Alto Networks PAN-OS

Do Son November 19, 2024 0

Take action against cyber threats. Learn about the actively exploited vulnerabilities in Kemp LoadMaster & PAN-OS and safeguard your networks
Phobos Ransomware Administrator Extradited to US to Face Charges Evgenii Ptitsyn - Phobos ransomware
  • Cyber Security
  • Malware

Phobos Ransomware Administrator Extradited to US to Face Charges

Do Son November 19, 2024 0

Learn about the global ransomware scheme and the extradition of Evgenii Ptitsyn, accused of administering the Phobos ransomware.
Phishing Alert: Government Impersonation Attacks Surge via DocuSign DocuSign phishing attacks
  • Cyber Security

Phishing Alert: Government Impersonation Attacks Surge via DocuSign

Do Son November 19, 2024 0

Stay informed about the rising threat of DocuSign phishing attacks targeting businesses. Learn how cybercriminals exploit trust and deliver malicious payloads.

From CVE to PoC: A Collection Maps Windows Privilege Escalation Landscape Windows Privilege Escalation Vulnerabilities
  • Vulnerability

From CVE to PoC: A Collection Maps Windows Privilege Escalation Landscape

Do Son November 18, 2024 0

Explore the collection of Windows privilege escalation vulnerabilities disclosed in 2023 and 2024. A valuable resource for security researchers and system administrators.
CVE-2024-52308: GitHub CLI Vulnerability Could Allow Remote Code Execution CVE-2024-52308
  • Vulnerability

CVE-2024-52308: GitHub CLI Vulnerability Could Allow Remote Code Execution

Do Son November 18, 2024 0

Don't overlook the vulnerability (CVE-2024-52308) in GitHub CLI. Learn how to secure your Codespaces and prevent remote code execution

LibreNMS Vulnerability (CVE-2024-51092): Mitigating the Risk of Server Compromise CVE-2024-51092 - LibreNMS
  • Vulnerability

LibreNMS Vulnerability (CVE-2024-51092): Mitigating the Risk of Server Compromise

Do Son November 18, 2024 0

Discover the severe vulnerability CVE-2024-51092 in LibreNMS network monitoring system. Stay informed and take steps to secure your server from potential exploitation.

Actively Exploited VMware Vulnerabilities (CVE-2024-38812 & CVE-2024-38813) Threaten Virtualized Infrastructure Exploited VMware
  • Vulnerability

Actively Exploited VMware Vulnerabilities (CVE-2024-38812 & CVE-2024-38813) Threaten Virtualized Infrastructure

Do Son November 18, 2024 0

Stay protected from exploited VMware vulnerabilities. Learn about the critical risks posed by heap-overflow vulnerabilities on vCenter Server.
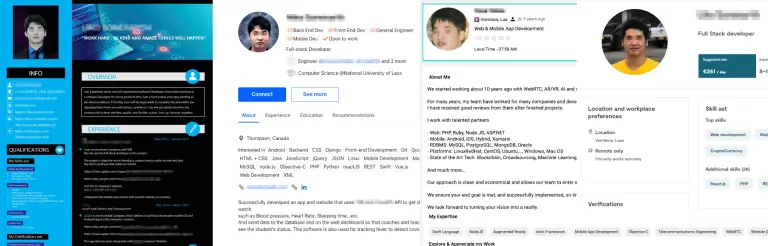
North Korean Hackers Target Job Seekers with Malware-Laced Video Apps CL-STA-0237
  • Cyber Security

North Korean Hackers Target Job Seekers with Malware-Laced Video Apps

Do Son November 18, 2024 0

Explore the complex phishing campaign led by North Korean IT workers CL-STA-0237. Learn how they targeted job seekers with malware-infected video conference apps.

Trio of Apache Tomcat Flaws Disclosed: Authentication Bypass, HTTP/2 Request Mix-Up, and XSS Flaw CVE-2023-45648 Apache Tomcat Security Encryption Bypass
  • Vulnerability

Trio of Apache Tomcat Flaws Disclosed: Authentication Bypass, HTTP/2 Request Mix-Up, and XSS Flaw

Do Son November 18, 2024 0

Stay informed about the latest Apache Tomcat vulnerabilities, including CVE-2024-52316. Learn how to protect your web applications from potential attacks.

BabbleLoader: The Polyglot Malware Evading Both Traditional and AI Defenses BabbleLoader malware
  • Malware

BabbleLoader: The Polyglot Malware Evading Both Traditional and AI Defenses

Do Son November 18, 2024 0

Unmasking the elusive BabbleLoader malware loader: a highly sophisticated tool that evades traditional and AI-based detection systems.

CVE-2024-31141: Apache Kafka Vulnerability Exposes User Data to Potential Attackers Kafka Authentication Bypass JWT Signature Validation Apache Kafka - CVE-2024-27309 & CVE-2024-31141
  • Vulnerability

CVE-2024-31141: Apache Kafka Vulnerability Exposes User Data to Potential Attackers

Do Son November 18, 2024 0

Stay informed about the CVE-2024-31141 vulnerability in Apache Kafka that puts sensitive information at risk.

Critical Vulnerabilities Found in Baxter Life2000 Ventilation System WAGO, vulnerability, industrial automation BlockBlasters, Steam malware Baxter Life2000 Ventilation System - CVE-2024-48966
  • Vulnerability

Critical Vulnerabilities Found in Baxter Life2000 Ventilation System

Do Son November 18, 2024 0

Discover the severe vulnerabilities in the Baxter Life2000 Ventilation System. Understand the risks of unauthorized access and operational disruptions.

DNS Predators Exploit “Sitting Ducks” Attack to Hijack Domains and Expand Cyber Operation Sitting Ducks attack
  • Cyber Security

DNS Predators Exploit “Sitting Ducks” Attack to Hijack Domains and Expand Cyber Operation

Do Son November 18, 2024 0

Uncover the pervasive cyber threat of the 'Sitting Ducks' attack. Learn how cybercriminals exploit trusted domains for malicious campaigns.

CVE-2024-0012 and CVE-2024-9474: Actively Exploited Vulnerabilities Impact Palo Alto Networks PAN-OS CVE-2024-9474
  • Vulnerability

CVE-2024-0012 and CVE-2024-9474: Actively Exploited Vulnerabilities Impact Palo Alto Networks PAN-OS

Do Son November 18, 2024 0

Learn about the critical vulnerabilities in Palo Alto Networks PAN-OS software. CVE-2024-0012 and CVE-2024-9474 pose significant risks to network security.

“Water Barghest” Botnet Hijacks 20,000 IoT Devices for Profit Mozi Botnet AI bots
  • Malware

“Water Barghest” Botnet Hijacks 20,000 IoT Devices for Profit

Do Son November 18, 2024 0

Discover the operations of Water Barghest, a highly sophisticated botnet that exploits vulnerabilities to create a profitable residential proxy network.

Critical Vulnerabilities in Citrix Virtual Apps and Desktops Actively Exploited CVE-2024-8068 & CVE-2024-8069 - Citrix Session Recording Manager
  • Vulnerability

Critical Vulnerabilities in Citrix Virtual Apps and Desktops Actively Exploited

Do Son November 18, 2024 0

Protect your Citrix environment from active exploits. Learn about the vulnerabilities in Citrix Session Recording Manager and how to mitigate them.

Introducing Shadow Dumper: A Powerful Tool for LSASS Memory Extraction LSASS Memory
  • Open Source Tool

Introducing Shadow Dumper: A Powerful Tool for LSASS Memory Extraction

Do Son November 17, 2024 0

Explore how Shadow Dumper extracts data from LSASS memory to assess security posture. Discover its versatility and stealthy techniques.

PoC Exploit Releases for Zero-Day CVE-2024-47575 Flaw in Fortinet FortiManager CVE-2024-47575 PoC exploit
  • Vulnerability

PoC Exploit Releases for Zero-Day CVE-2024-47575 Flaw in Fortinet FortiManager

Do Son November 17, 2024 0

A security researcher recently published technical details and a proof-of-concept (PoC) exploit for a critical zero-day vulnerability CVE-2024-47575

WezRat: The Modular Infostealer Weaponized by Iranian Cyber Group Emennet Pasargad WezRat malware
  • Cyber Security
  • Malware

WezRat: The Modular Infostealer Weaponized by Iranian Cyber Group Emennet Pasargad

Do Son November 17, 2024 0

Discover the sophisticated WezRat infostealer and its role in cyber campaigns targeting the US, Europe, and Israel.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.