Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Future of Cybersecurity: Trends Shaping the Industry Employees Risk
  • Technique

The Future of Cybersecurity: Trends Shaping the Industry

Do Son November 12, 2024 0
The future of cybersecurity is evolving rapidly, navigated by technological advancements and the increasing sophistication of cyber...
Read More Read more about The Future of Cybersecurity: Trends Shaping the Industry
CVE-2024-11068 (CVSS 9.8): Critical D-Link DSL-6740C Flaw, Immediate Replacement Advised D-Link DSL-6740C - CVE-2024-11068
  • Vulnerability

CVE-2024-11068 (CVSS 9.8): Critical D-Link DSL-6740C Flaw, Immediate Replacement Advised

Do Son November 11, 2024 0

Stay informed about the security risks associated with the D-Link DSL-6740C modem. Discover the vulnerabilities and how they can expose you to remote attacks.

VPNs and Clouds: New Tools in the APT Arsenal, ESET Warns APT Activity
  • Cyber Security
  • Malware

VPNs and Clouds: New Tools in the APT Arsenal, ESET Warns

Do Son November 11, 2024 0

Learn about the surge in sophisticated APT attacks targeting various sectors. ESET's report sheds light on tactics and VPN reliance.

Dell Enterprise SONIC OS Patches Critical Security Vulnerabilities CVE-2024-45763, CVE-2024-45764, and CVE-2024-45765
  • Vulnerability

Dell Enterprise SONIC OS Patches Critical Security Vulnerabilities

Do Son November 11, 2024 0

The vulnerabilities, identified as CVE-2024-45763, CVE-2024-45764, and CVE-2024-45765, affect Dell Enterprise SONIC OS

JavaScript Drive-By Attacks: New Exploits without 0-Day in Google Chrome Google Chrome Helper
  • Vulnerability

JavaScript Drive-By Attacks: New Exploits without 0-Day in Google Chrome

Do Son November 11, 2024 0

Ron Masas from Imperva Threat Research has uncovered a new way attackers can target Chrome users without relying on 0-day vulnerabilities

Mozi Botnet Re-Emerges as Androxgh0st in New Wave of IoT Exploits
  • Malware
  • Vulnerability

Mozi Botnet Re-Emerges as Androxgh0st in New Wave of IoT Exploits

Do Son November 11, 2024 0

Uncover the details of the Androxgh0st botnet's resurgence and its operational integration with the Mozi botnet. Explore the heightened attacks on web servers and vulnerable IoT devices.

Ghostscript Update Patches Six Critical Vulnerabilities: Code Execution, Buffer Overflow, and Path Traversal Risks CVE-2024-46951- Ghostscript vulnerability
  • Vulnerability

Ghostscript Update Patches Six Critical Vulnerabilities: Code Execution, Buffer Overflow, and Path Traversal Risks

Do Son November 11, 2024 0

Learn about the security vulnerabilities in Ghostscript and the potential risks they pose. Stay secure by updating to the latest version.
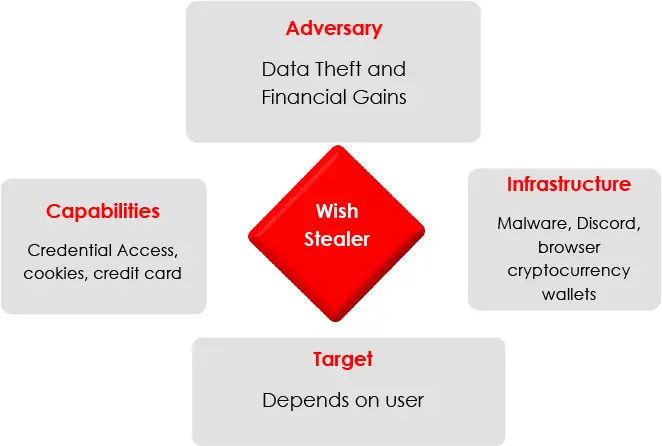
Wish Stealer: New Malware Targets Discord, Browsers, and Cryptocurrency Wallets Wish Stealer
  • Malware

Wish Stealer: New Malware Targets Discord, Browsers, and Cryptocurrency Wallets

Do Son November 11, 2024 0

Learn about Wish Stealer, a potent Node.js-based malware that steals sensitive information from Discord, web browsers, and more.

XStream Security Advisory: Denial-of-Service Vulnerability (CVE-2024-47072) CVE-2024-47072
  • Vulnerability

XStream Security Advisory: Denial-of-Service Vulnerability (CVE-2024-47072)

Do Son November 11, 2024 0

Understand the implications of CVE-2024-47072, a high-severity DoS vulnerability in XStream. Learn how it can be exploited and steps to prevent attacks.

Earth Estries’ Evolving Toolkit: A Deep Dive into Their Advanced Techniques BlueNoroff macOS Attack GhostCall Campaign Carding Underground Bulletproof Hosting DPRK Contagious Interview, npm Flood Stonefly group -HiatusRAT Actors
  • Cyber Security
  • Malware

Earth Estries’ Evolving Toolkit: A Deep Dive into Their Advanced Techniques

Do Son November 11, 2024 0

Uncover the intricate cyberespionage campaign of Earth Estries. Learn how this group targets governments and technology firms with sophisticated attack chains.

Trojan Malware Delivered via ZIP Concatenation: A New Threat to Windows Users ZIP concatenation
  • Malware

Trojan Malware Delivered via ZIP Concatenation: A New Threat to Windows Users

Do Son November 11, 2024 0

Learn about the security implications of ZIP concatenation and how threat actors can exploit this technique to hide malicious contents.

SEO Poisoning: Unmasking the Malware Networks Behind Fake E-Commerce Japanese keyword hack
  • Cyber Security
  • Malware

SEO Poisoning: Unmasking the Malware Networks Behind Fake E-Commerce

Do Son November 11, 2024 0

Stay vigilant against SEO malware. Find out how hackers manipulate search engine results to redirect users to fraudulent online stores and steal personal information.

Unpatched Epson Devices at Risk: CVE-2024-47295 Allows Easy Hijacking CVE-2024-47295
  • Vulnerability

Unpatched Epson Devices at Risk: CVE-2024-47295 Allows Easy Hijacking

Do Son November 11, 2024 0

Stay informed about the latest security vulnerability (CVE-2024-47295) affecting SEIKO EPSON products. Find out how attackers can exploit an insecure password configuration.

GuLoader Campaign Targets European Industrial Sector with Evolving Evasion Techniques matrix-434033_1280
  • Malware

GuLoader Campaign Targets European Industrial Sector with Evolving Evasion Techniques

Do Son November 11, 2024 0

Uncover the targeted GuLoader campaign impacting European industrial and engineering companies. Learn about the evasive malware and its sophisticated tactics.

How to Fix Delay in Receiving Emails in Outlook 2019 on Windows 11? Outlook 2019
  • Technique

How to Fix Delay in Receiving Emails in Outlook 2019 on Windows 11?

Do Son November 11, 2024 0

Troubleshooting delay in receiving emails in Outlook 2019. Learn how to resolve this common issue and ensure timely email communication.

Tor Network Thwarts IP Spoofing Attack Tor IP spoofing Tor Browser, AI privacy
  • Cyber Security

Tor Network Thwarts IP Spoofing Attack

Do Son November 11, 2024 0

Learn about a recent IP spoofing attack on the Tor network and how the Tor community responded swiftly to mitigate the threat.

Palo Alto Networks Investigates Potential Remote Code Execution Vulnerability in PAN-OS PAN-OS vulnerability
  • Vulnerability

Palo Alto Networks Investigates Potential Remote Code Execution Vulnerability in PAN-OS

Do Son November 10, 2024 0

Palo Alto Networks alerts customers to a potential PAN-OS vulnerability. Review your access configurations and follow recommended best practice deployment guidelines.

Frag Ransomware: A New Threat Exploits Veeam Vulnerability (CVE-2024-40711) Frag ransomware
  • Malware
  • Vulnerability

Frag Ransomware: A New Threat Exploits Veeam Vulnerability (CVE-2024-40711)

Do Son November 10, 2024 0

Discover Frag ransomware, a newly observed threat exploiting a vulnerability in Veeam backup servers. Learn about its unique tactics and how to protect yourself.

FakeBat Loader Reemerges: Malicious Google Ads Target Notion Users FakeBat loader
  • Malware

FakeBat Loader Reemerges: Malicious Google Ads Target Notion Users

Do Son November 10, 2024 0

Beware of the return of the FakeBat loader! Learn how threat actors are using malvertising on Google to distribute malware.

QSC Malware Framework: New Tool in CloudComputating Group’s Cyberespionage Arsenal CloudComputating - QSC framework
  • Cyber Security
  • Malware

QSC Malware Framework: New Tool in CloudComputating Group’s Cyberespionage Arsenal

Do Son November 10, 2024 0

Discover QSC, the advanced malware framework used by the CloudComputating group. Learn about its modular design and stealth capabilities.

SpyNote Malware: Fake Antivirus Targets Android Users in Sophisticated New Campaign SpyNote malware
  • Malware

SpyNote Malware: Fake Antivirus Targets Android Users in Sophisticated New Campaign

Do Son November 10, 2024 0

Beware of SpyNote: a highly advanced Android malware posing as a fake antivirus app. Learn how to protect your device from this dangerous threat.

RedLine Stealer Analysis: Inside a Notorious Malware-as-a-Service Operation RedLine
  • Malware

RedLine Stealer Analysis: Inside a Notorious Malware-as-a-Service Operation

Do Son November 10, 2024 0

Learn about RedLine Stealer, a powerful and sophisticated malware-as-a-service operation that allows affiliates to manage cybertheft campaigns targeting credentials and personal information.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.