Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Researcher Uncovers New Phishing Campaign Deploying Remcos RAT with Advanced Evasion Techniques Remcos RAT phishing campaign
  • Malware

Researcher Uncovers New Phishing Campaign Deploying Remcos RAT with Advanced Evasion Techniques

Do Son November 10, 2024 0

Stay informed about the latest phishing campaign using the Remcos RAT. Learn how the CVE-2017-0199 vulnerability is exploited to gain remote access to victims' computers.

Fickle Stealer: The New Rust-Based Malware Masquerading as GitHub Desktop Fickle Stealer malware
  • Malware

Fickle Stealer: The New Rust-Based Malware Masquerading as GitHub Desktop

Do Son November 10, 2024 0

Learn about the dangerous new Rust-based malware, Fickle Stealer, and its threat to cybersecurity. Stay informed to protect your sensitive information.

Silent Skimmer Reemerges: New Tactics Target Payment Gateways Magento Credit Card Stealer npm package reverse shell
  • Cyber Security
  • Malware

Silent Skimmer Reemerges: New Tactics Target Payment Gateways

Do Son November 10, 2024 0

Learn about the renewed activity of Silent Skimmer, a financially motivated cybercriminal group. Explore their tactics for compromising servers and harvesting payment data.

BlueNoroff’s New MacOS Threat: “Hidden Risk” Targets Crypto Enthusiasts Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security
  • Malware

BlueNoroff’s New MacOS Threat: “Hidden Risk” Targets Crypto Enthusiasts

Do Son November 10, 2024 0

Learn about the 'Hidden Risk' campaign targeting macOS users in the cryptocurrency industry. Find out how to defend yourself against this alarming malware attack.

Roblox Developers Targeted in Supply Chain Attack with Malicious npm Packages Skuld infostealer
  • Malware

Roblox Developers Targeted in Supply Chain Attack with Malicious npm Packages

Do Son November 10, 2024 0

Stay informed about the Skuld infostealer attack on Roblox developers. Learn how to detect and defend against malicious npm packages.

Scattered Spider Spins a New Web: Detecting 0ktapus Phishing Domains 0ktapus
  • Cyber Security

Scattered Spider Spins a New Web: Detecting 0ktapus Phishing Domains

Do Son November 10, 2024 0

Stay ahead of the 0ktapus phishing threat. Learn how to identify fake login pages and protect your cloud environments from unauthorized access.

CVE-2024-10470 (CVSS 9.8) in Popular WordPress Theme Exposes Thousands of Sites WPLMS theme - CVE-2024-10470
  • Vulnerability

CVE-2024-10470 (CVSS 9.8) in Popular WordPress Theme Exposes Thousands of Sites

Do Son November 8, 2024 0

Learn about CVE-2024-10470 in the WPLMS theme for WordPress. Discover how attackers can exploit this flaw to read and delete sensitive files.

From Fake Updates to Data Exfiltration: Inside Interlock Ransomware’s Operations Interlock ransomware attack
  • Malware

From Fake Updates to Data Exfiltration: Inside Interlock Ransomware’s Operations

Do Son November 8, 2024 0

Discover the alarming new ransomware attack called Interlock. Understand its intricate attack chain and the risks it poses to businesses.

CVE-2024-10914 (CVSS 9.2): Command Injection Flaw Threatens 61,000+ D-Link NAS Devices CVE-2024-10914
  • Vulnerability

CVE-2024-10914 (CVSS 9.2): Command Injection Flaw Threatens 61,000+ D-Link NAS Devices

Do Son November 7, 2024 0

Critical vulnerability (CVE-2024-10914) in D-Link NAS devices: learn about the risks, impact, affected models, and steps to mitigate this high severity issue.

GodFather Malware Now Targets 500+ Banking and Crypto Apps GodFather malware
  • Malware

GodFather Malware Now Targets 500+ Banking and Crypto Apps

Do Son November 7, 2024 0

Stay informed about the latest variant of the GodFather malware targeting banking and cryptocurrency applications worldwide.

CISA Expands KEV Catalog with Four Actively Exploited Vulnerabilities Actively Exploited Vulnerabilities
  • Vulnerability

CISA Expands KEV Catalog with Four Actively Exploited Vulnerabilities

Do Son November 7, 2024 0

Stay informed of actively exploited vulnerabilities impacting organizations worldwide. Learn about the risks and urgent need for remediation.

Beware Python Developers: Malicious ‘fabrice’ Package Steals AWS Credentials from 37,000+ Downloads exfiltrating AWS credentials - fabrice package
  • Malware

Beware Python Developers: Malicious ‘fabrice’ Package Steals AWS Credentials from 37,000+ Downloads

Do Son November 7, 2024 0

Discover the risks of the fabrice package: a malicious Python package that steals AWS credentials and poses a threat to open-source repositories.

Apache ZooKeeper Security Alert: Important Flaw Impacts Admin Server (CVE-2024-51504) CVE-2024-51504
  • Vulnerability

Apache ZooKeeper Security Alert: Important Flaw Impacts Admin Server (CVE-2024-51504)

Do Son November 7, 2024 0

Learn about the critical security vulnerability CVE-2024-51504 in Apache ZooKeeper and how it exposes the Admin Server to authentication bypass via IP spoofing.

Winos4.0 Malware Spread Through Game Apps Targets Education Sector Winos4.0 malware
  • Malware

Winos4.0 Malware Spread Through Game Apps Targets Education Sector

Do Son November 7, 2024 0

Discover the advanced Winos4.0 malware framework and its highly modular design. Learn how it targets unsuspecting users through game-related applications.
New Rhadamanthys Stealer Rhadamanthys.07 Mimics Copyright Notices to Phish Global Targets Operation IconCat, UNG0801 AFP cyberattack -NetWalker Ransomware VShell RAT
  • Malware

New Rhadamanthys Stealer Rhadamanthys.07 Mimics Copyright Notices to Phish Global Targets

Do Son November 7, 2024 0

Beware of the Rhadamanthys.07 phishing campaign. Discover how this sophisticated malware is distributed through fake Gmail accounts and spear-phishing emails.
CVE-2024-20536: Cisco NDFC Vulnerability Grants Attackers Extensive Control Cisco ISE Root Escalation * Read-Only Admin Exploit Cisco Secure FMC Vulnerability CVE-2026-20131 Cisco Meeting Management Vulnerability CVE-2026-20098 Cisco vulnerability, RCE flaw CVE-2025-20265 Cisco Meraki, VPN Vulnerability Cisco Nexus Dashboard - CVE-2024-20424 CVE-2025-20115 Cisco Vulnerability CVE-2018-0171 Privilege Escalation Cisco Unified Intelligence Center
  • Vulnerability

CVE-2024-20536: Cisco NDFC Vulnerability Grants Attackers Extensive Control

Do Son November 7, 2024 0

Learn about the high-severity SQL injection flaw CVE-2024-20536 in Cisco Nexus Dashboard and the critical risk it poses to network security.

CVE-2024-40715: Authentication Bypass Threat in Veeam Backup Enterprise Manager Veeam Backup Enterprise Manager Vulnerability (CVE-2024-40715)
  • Vulnerability

CVE-2024-40715: Authentication Bypass Threat in Veeam Backup Enterprise Manager

Do Son November 7, 2024 0

Discover the high-severity vulnerability CVE-2024-40715 affecting Veeam Backup Enterprise Manager and the potential risks for your data security
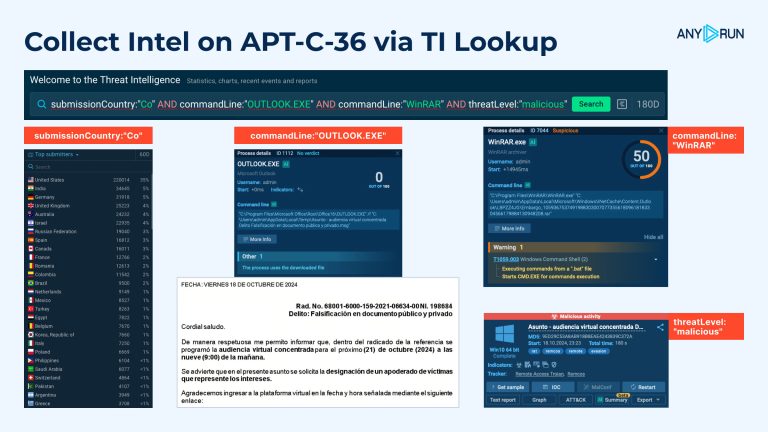
Ongoing Phishing Attack in LATAM Region Ongoing Phishing Attack
  • Cyber Security
  • Malware

Ongoing Phishing Attack in LATAM Region

Do Son November 7, 2024 0

Stay vigilant against the ongoing phishing attack in Latin America. Learn how cybercriminals are using advanced tactics to deceive and compromise users.

Kaspersky Labs Uncovers SteelFox Trojan: 11,000+ Devices Infected SteelFox Trojan
  • Malware

Kaspersky Labs Uncovers SteelFox Trojan: 11,000+ Devices Infected

Do Son November 6, 2024 0

Protect yourself from the SteelFox trojan. Learn how it disguises itself as free software activators and steals user information.

Bengal Cat Lovers in Australia Targeted by Gootloader Malware Bengal cat
  • Malware

Bengal Cat Lovers in Australia Targeted by Gootloader Malware

Do Son November 6, 2024 0

Bengal cat enthusiasts in Australia targeted by a Gootloader campaign. Learn how the attackers used SEO poisoning and malware to spread.

CVE-2024-42509 (CVSS 9.8): Critical Vulnerability Exposes Aruba Access Points to Attack CVE-2024-42509 & CVE-2024-47460 HPE Aruba Fabric Composer CVE-2026-23592 Aruba AOS-CX CVE-2026-23813
  • Vulnerability

CVE-2024-42509 (CVSS 9.8): Critical Vulnerability Exposes Aruba Access Points to Attack

Do Son November 6, 2024 0

Protect your network against critical vulnerabilities in HPE Aruba Access Points. Learn about CVE-2024-42509 & CVE-2024-47460 and how to apply the necessary security patches.

Cybercriminals Exploit DocuSign API to Send Convincing Phishing Invoices at Scale Abuse DocuSign API
  • Cyber Security

Cybercriminals Exploit DocuSign API to Send Convincing Phishing Invoices at Scale

Do Son November 6, 2024 0

Don't fall victim to DocuSign API phishing. Discover how cybercriminals leverage trusted accounts and templates to send fraudulent invoices.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.