Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Ricoh Printers and MFPs Vulnerable to Remote Code Execution – CVE-2024-47939 (CVSS 9.8) Ricoh Printers - CVE-2024-47939
  • Vulnerability

Ricoh Printers and MFPs Vulnerable to Remote Code Execution – CVE-2024-47939 (CVSS 9.8)

Do Son November 3, 2024 0

Learn about the CVE-2024-47939 vulnerability affecting Ricoh printers and MFPs. Stay ahead of potential security risks.

Threat Actor Deploys LummaC2 and Rhadamanthys Stealers in Attacks on Taiwanese Facebook Accounts Facebook phishing campaign
  • Cyber Security
  • Malware

Threat Actor Deploys LummaC2 and Rhadamanthys Stealers in Attacks on Taiwanese Facebook Accounts

Do Son November 3, 2024 0

Beware of a new Facebook phishing campaign in Taiwan targeting business account users. Learn how to protect yourself from this malware-ridden scam.

121 Fake Web Shops and 1,000 Infected Websites: Inside the Phish ‘n’ Ships Scam Edited Payment Provider
  • Cyber Security

121 Fake Web Shops and 1,000 Infected Websites: Inside the Phish ‘n’ Ships Scam

Do Son November 3, 2024 0

Uncover the sophisticated Phish 'n' Ships scheme: a network of fraudulent online stores that exploited the digital advertising ecosystem to steal millions of dollars

Six Vulnerabilities Uncovered in Ollama: Risks of AI Model Theft and Poisoning Ollama vulnerability
  • Vulnerability

Six Vulnerabilities Uncovered in Ollama: Risks of AI Model Theft and Poisoning

Do Son November 3, 2024 0

Discover the security risks of using Ollama and the vulnerabilities that could lead to malicious actions and attacks.

Typosquat Campaign Targets Puppeteer Users: Researcher Warns of Malware in npm Packages Puppeteer malware
  • Malware

Typosquat Campaign Targets Puppeteer Users: Researcher Warns of Malware in npm Packages

Do Son November 3, 2024 0

Beware of a new typosquatting campaign targeting developers using open-source packages like Puppeteer. Learn how to protect yourself from malicious packages

Pacific Rim: Sophos Exposes 5 Years of Chinese Cyber Espionage Pacific Rim APT
  • Cyber Security

Pacific Rim: Sophos Exposes 5 Years of Chinese Cyber Espionage

Do Son November 3, 2024 0

Uncover the sophisticated cyberattack campaign known as 'Pacific Rim.' Discover how China-based threat groups target high-value infrastructure and government organizations

Nvidia Releases Security Update for ConnectX and BlueField DPUs Amid High-Severity Flaws NVIDIA Nsight Vulnerability CVE-2025-33206 NVIDIA ConnectX Firmware - CVE-2024-0105
  • Vulnerability

Nvidia Releases Security Update for ConnectX and BlueField DPUs Amid High-Severity Flaws

Do Son November 3, 2024 0

Stay informed about the latest security update for Nvidia ConnectX and BlueField DPUs. Learn about the vulnerabilities and potential risks.

CrossBarking Vulnerability in Opera Browser Allows Malicious Extensions to Hijack User Accounts CrossBarking vulnerability
  • Vulnerability

CrossBarking Vulnerability in Opera Browser Allows Malicious Extensions to Hijack User Accounts

Do Son November 2, 2024 0

Discover the security risks of CrossBarking, a vulnerability in the Opera browser. Learn how attackers can exploit Private APIs and compromise user accounts

SYS01 Infostealer Campaign Exploits Meta Ads to Target Millions Worldwide SYS01 Infostealer
  • Cyber Security
  • Malware

SYS01 Infostealer Campaign Exploits Meta Ads to Target Millions Worldwide

Do Son November 2, 2024 0

Find out about the SYS01 Infostealer campaign: a sophisticated malvertising attack using social media ads to distribute a powerful malware tool.

Okta Discloses Authentication Vulnerability in AD/LDAP DelAuth, Urges Customer Review Okta Authentication Vulnerability
  • Vulnerability

Okta Discloses Authentication Vulnerability in AD/LDAP DelAuth, Urges Customer Review

Do Son November 2, 2024 0

Stay updated on the Okta Authentication Vulnerability and the steps you can take to protect your organization's data and users.

PoC Exploit Releases for Spring WebFlux Authorization Bypass – CVE-2024-38821 CVE-2024-38821 PoC exploit
  • Vulnerability

PoC Exploit Releases for Spring WebFlux Authorization Bypass – CVE-2024-38821

Do Son November 1, 2024 0

Discover the technical details of CVE-2024-38821 exploit in Spring WebFlux and understand the potential risks it poses to your application's security.

LUNAR SPIDER Resurfaces: Financial Sector Targeted in Latest Malvertising Campaign LUNAR SPIDER
  • Cyber Security
  • Malware

LUNAR SPIDER Resurfaces: Financial Sector Targeted in Latest Malvertising Campaign

Do Son November 1, 2024 0

Uncover the latest cyber threat: LUNAR SPIDER. Learn about their tactics and the adoption of Brute Ratel C4 in their malvertising campaigns.

PythonRatLoader: The Malware Loader That’s Turning Phishing Into a Multi-Stage Attack At
  • Malware

PythonRatLoader: The Malware Loader That’s Turning Phishing Into a Multi-Stage Attack

Do Son November 1, 2024 0

Protect your organization from PythonRatLoader: a sophisticated malware loader that distributes harmful remote access trojans (RATs).

CVE-2024-38094 Exploited: Attackers Gain Domain Access via Microsoft SharePoint Server Microsoft SharePoint server
  • Cyber Security
  • Vulnerability

CVE-2024-38094 Exploited: Attackers Gain Domain Access via Microsoft SharePoint Server

Do Son October 31, 2024 0

Learn about a serious compromise of a Microsoft SharePoint server and the importance of swift vulnerability detection and response.

PoC Exploit Releases for Critical Flaw in Synology TC500 and BC500 Camera to Get Shell Synology TC500
  • Vulnerability

PoC Exploit Releases for Critical Flaw in Synology TC500 and BC500 Camera to Get Shell

Do Son October 31, 2024 0

Learn about the format string vulnerability in Synology TC500 security camera, and how it enables attackers to bypass memory protection.

Iranian Cyber Group Emennet Pasargad’s Expanding Operations Targeting Global Networks CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Cyber Security

Iranian Cyber Group Emennet Pasargad’s Expanding Operations Targeting Global Networks

Do Son October 31, 2024 0

Stay vigilant against the evolving cyber operations of Emennet Pasargad (ASA). Learn about their expanded targeting techniques and infrastructure.

Cryptocurrency Users Targeted by Invasive New Malware Campaign CryptoAITools
  • Cyber Security
  • Malware

Cryptocurrency Users Targeted by Invasive New Malware Campaign

Do Son October 31, 2024 0

Beware of the CryptoAITools malware campaign targeting cryptocurrency users. Learn how this sophisticated attack steals data and drains wallets.
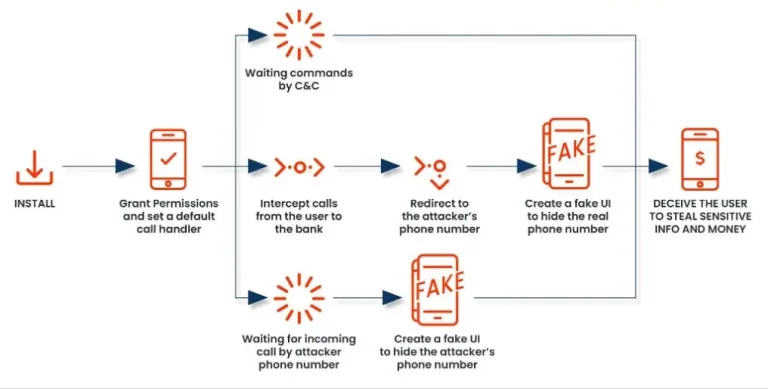
FakeCall Malware: Sophisticated Vishing Attack Targets Mobile Users in Banking Fraud FakeCall malware
  • Malware

FakeCall Malware: Sophisticated Vishing Attack Targets Mobile Users in Banking Fraud

Do Son October 31, 2024 0

New FakeCall malware variant alert! Stay informed about this vishing threat that disguises as a banking app to target mobile banking users through fraudulent phone calls.

CVE-2024-9632: 18-Year-Old Bug in X.Org Server Leaves Systems Vulnerable to Attack CVE-2024-9632
  • Vulnerability

CVE-2024-9632: 18-Year-Old Bug in X.Org Server Leaves Systems Vulnerable to Attack

Do Son October 31, 2024 0

Protect your system from CVE-2024-9632, a severe security flaw discovered in the X.Org Server that could be exploited for system takeover.

EMERALDWHALE Operation Exposes Over 15,000 Cloud Credentials in Widespread Git Exploit EMERALDWHALE
  • Cyber Security

EMERALDWHALE Operation Exposes Over 15,000 Cloud Credentials in Widespread Git Exploit

Do Son October 31, 2024 0

Sysdig TRT uncovers EMERALDWHALE: a large-scale cyber operation stealing cloud credentials by exploiting exposed Git configuration files.
Hikvision Patches Security Flaw in Network Cameras, Preventing Cleartext Credential Transmission Hikvision Vulnerability CVE-2026-0709 Hikvision Vulnerability CVE-2025-66176 Hikvision, vulnerability Canada Hikvision Ban, National Security Hikvision firmware updates
  • Vulnerability

Hikvision Patches Security Flaw in Network Cameras, Preventing Cleartext Credential Transmission

Do Son October 31, 2024 0

Keep your Hikvision network cameras secure with firmware updates that protect against a vulnerability that exposes Dynamic DNS credentials.

North Korean Threat Group “Jumpy Pisces” Linked to Play Ransomware Attack Andariel hacking group - Jumpy Pisces
  • Cyber Security
  • Malware

North Korean Threat Group “Jumpy Pisces” Linked to Play Ransomware Attack

Do Son October 31, 2024 0

Discover the alarming collaboration between North Korean hackers and ransomware gangs. Learn how Jumpy Pisces is involved in a Play ransomware attack.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.