Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Pygmy Goat Malware: A Sophisticated Network Device Backdoor Targets Firewalls critical server patch Pygmy Goat malware - Fuji Electric Ransomware Attack
  • Malware

Pygmy Goat Malware: A Sophisticated Network Device Backdoor Targets Firewalls

Do Son November 4, 2024 0

Discover Pygmy Goat, a new malware threat targeting network devices. Find out how it evades detection and captures sensitive data.

GOOTLOADER Malware Continues to Evolve: Google Researchers Uncover Advanced Tactics GOOTLOADER
  • Malware

GOOTLOADER Malware Continues to Evolve: Google Researchers Uncover Advanced Tactics

Do Son November 4, 2024 0

Discover the tactics used by threat actors to deploy ransomware with GOOTLOADER. Find out how they trick victims into downloading the malicious JavaScript file.

Century Systems Routers Vulnerable to Remote Exploitation – CVE-2024-50357 (CVSS 9.8) FutureNet NXR - CVE-2024-50357
  • Vulnerability

Century Systems Routers Vulnerable to Remote Exploitation – CVE-2024-50357 (CVSS 9.8)

Do Son November 4, 2024 0

Protect your FutureNet NXR router from remote attacks! Century Systems Co., Ltd. issues security advisory for CVE-2024-50357 vulnerability.

Xiū Gǒu Phishing Kit: The ‘Doggo’ of Phishing Campaigns with Global Reach Xiū Gǒu Phishing Kit
  • Cyber Security

Xiū Gǒu Phishing Kit: The ‘Doggo’ of Phishing Campaigns with Global Reach

Do Son November 4, 2024 0

Uncover the details of Xiū Gǒu, a new phishing kit targeting organizations in the public sector, postal, digital services, and banking sectors.

Beyond Keylogging: HookBot’s Advanced Techniques for Data Theft Screenshot 2024-11-03 152517
  • Malware

Beyond Keylogging: HookBot’s Advanced Techniques for Data Theft

Do Son November 4, 2024 0

Protect your banking credentials and sensitive information from the advanced Android Trojan, HookBot. Stay updated on the latest cyber threats.

Storm-0940 and CovertNetwork-1658: Insights into Chinese Cyberattack Infrastructure Storm-0940 - CovertNetwork-1658
  • Cyber Security

Storm-0940 and CovertNetwork-1658: Insights into Chinese Cyberattack Infrastructure

Do Son November 4, 2024 0

One notable actor using CovertNetwork-1658’s credentials is the Chinese threat group Storm-0940. Known for its relentless attacks on organizations

ZoneMinder’s CVE-2024-51482: A 10/10 Severity Vulnerability Exposes SQL Databases CVE-2024-51482
  • Vulnerability

ZoneMinder’s CVE-2024-51482: A 10/10 Severity Vulnerability Exposes SQL Databases

Do Son November 4, 2024 0

Learn about CVE-2024-51482, a critical security vulnerability in ZoneMinder that could compromise data confidentiality and system integrity.

Obfuscated JavaScript and WebDAV: Strela Stealer’s New Tools for Credential Theft Strela Stealer
  • Cyber Security
  • Malware

Obfuscated JavaScript and WebDAV: Strela Stealer’s New Tools for Credential Theft

Do Son November 4, 2024 0

Stay informed about the Strela Stealer phishing campaign targeting Europe. Learn how this sophisticated malware steals sensitive data from compromised systems.

Critical Vulnerabilities Found in Rockwell Automation FactoryTalk ThinManager CVE-2024-10386 - Rockwell Automation FactoryTalk ThinManager
  • Vulnerability

Critical Vulnerabilities Found in Rockwell Automation FactoryTalk ThinManager

Do Son November 4, 2024 0

Stay informed about the critical flaws in Rockwell Automation's FactoryTalk ThinManager and the need for increased security measures.
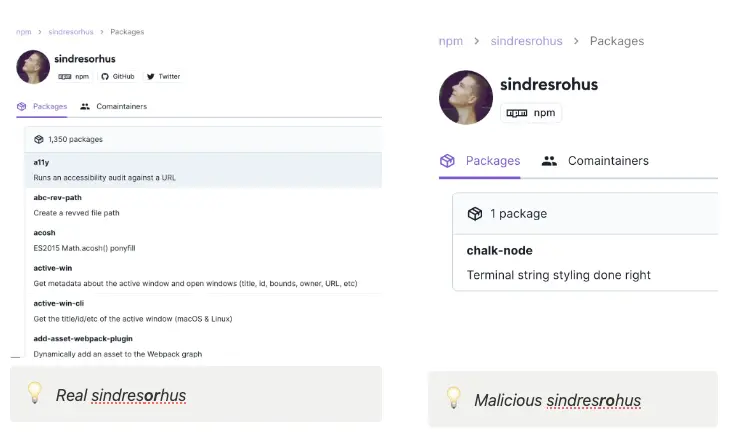
Beware of chalk-node: Malicious Package Steals Developer Data Malicious Package
  • Malware

Beware of chalk-node: Malicious Package Steals Developer Data

Do Son November 4, 2024 0

Beware of the latest npm threat! Learn how a malicious package called 'chalk-node' is posing as a popular library to steal sensitive data.

U.S. Soccer Federation Discloses Data Security Incident U.S. Soccer security incident
  • Data Leak

U.S. Soccer Federation Discloses Data Security Incident

Do Son November 4, 2024 0

U.S. Soccer Federation data security incident: Personal information exposed. Learn more about the breach and steps taken to protect fans and employees.

QNAP Patches Zero-Day Flaw CVE-2024-50389 in QuRouter Following Pwn2Own Ireland 2024 Exploits CVE-2024-50387 & CVE-2024-50389 QuRouter
  • Vulnerability

QNAP Patches Zero-Day Flaw CVE-2024-50389 in QuRouter Following Pwn2Own Ireland 2024 Exploits

Do Son November 4, 2024 0

Learn about the latest zero-day vulnerability, CVE-2024-50389, in QNAP's QuRouter network security appliance and how it was exploited during the Pwn2Own hacking contest.
How Threat Intelligence Exchange Enhances Cybersecurity Posture Employees Risk
  • Technique

How Threat Intelligence Exchange Enhances Cybersecurity Posture

Do Son November 4, 2024 0

Enhance your cybersecurity with threat intelligence exchange. Learn how it works and why it's essential for protecting your organization.

CVE-2024-46538: Unpatched XSS Flaw in pfSense Allows Remote Exploits, PoC Published CVE-2024-46538 pfsense vulnerability
  • Vulnerability

CVE-2024-46538: Unpatched XSS Flaw in pfSense Allows Remote Exploits, PoC Published

Do Son November 4, 2024 0

Stay informed about pfSense vulnerability CVE-2024-46538. Find out how this XSS flaw can be exploited to execute arbitrary web scripts or HTML on affected systems

KDE Sets Sights on New Horizons with “Project Banana” Linux Distro Project Banana - KDE Linux distribution
  • Linux

KDE Sets Sights on New Horizons with “Project Banana” Linux Distro

Do Son November 4, 2024 0

Experience the future of Linux with Project Banana. This innovative distribution, based on KDE technologies, aims to redefine the user experience.

Genzai: Secure Your IoT Devices with Automated Security Vulnerability Scanning IoT Security Toolkit
  • Open Source Tool

Genzai: Secure Your IoT Devices with Automated Security Vulnerability Scanning

Do Son November 4, 2024 0

Protect your IoT devices with Genzai. An open-source toolkit that offers a cohesive solution for enhanced IoT security.

MediaTek Security Bulletin Highlights High Severity Vulnerabilities in Mobile Chipsets MediaTek Modem Vulnerabilities, January 2026 Security Bulletin MediaTek Vulnerabilities, Chipset Security CVE-2024-20103 & CVE-2024-20100 - CVE-2024-20154 - February 2025 Product Security Bulletin
  • Vulnerability

MediaTek Security Bulletin Highlights High Severity Vulnerabilities in Mobile Chipsets

Do Son November 4, 2024 0

Stay informed about the latest MediaTek security vulnerabilities. Find out how the CVE-2024-20104 & CVE-2024-20106 can impact your devices.

Halberd: Your Swiss Army Knife for Multi-Cloud Security Testing Cloud Security Testing
  • Open Source Tool

Halberd: Your Swiss Army Knife for Multi-Cloud Security Testing

Do Son November 4, 2024 0

Enhance cloud security with Halberd's multi-cloud security testing tool. Proactively assess defenses and simulate real-world attack scenarios.

Okta Patches Vulnerability (CVE-2024-9191) in Verify Desktop MFA for Windows CVE-2024-10327 - Okta Verify Desktop
  • Vulnerability

Okta Patches Vulnerability (CVE-2024-9191) in Verify Desktop MFA for Windows

Do Son November 3, 2024 0

Okta addresses high-severity vulnerability in Okta Verify Desktop MFA for Windows. Learn how attackers could exploit this flaw to steal user passwords.

New Trojan “MiyaRat” Unleashed by Bitter Group (APT-Q-37) Bitter Group - Miyarat trojan
  • Malware

New Trojan “MiyaRat” Unleashed by Bitter Group (APT-Q-37)

Do Son November 3, 2024 0

Discover the latest threat from the Bitter Group: MiyaRat, a new Trojan targeting South Asian entities with diverse attack methods.

CVE-2024-8956 & CVE-2024-8957: Two Actively Exploited Vulnerabilities in PTZ Cameras PTZ cameras - CVE-2024-8956 and CVE-2024-8957
  • Vulnerability

CVE-2024-8956 & CVE-2024-8957: Two Actively Exploited Vulnerabilities in PTZ Cameras

Do Son November 3, 2024 0

GreyNoise Labs identified two critical vulnerabilities (CVE-2024-8956 and CVE-2024-8957) in popular pan-tilt-zoom (PTZ) cameras

EDRsandblast Exploited: How Attackers are Weaponizing Open-Source Code AV/EDR bypass tool
  • Cyber Security
  • Malware

EDRsandblast Exploited: How Attackers are Weaponizing Open-Source Code

Do Son November 3, 2024 0

Find out how an attacker used an EDR evasion tool to bypass security defenses and the important discovery that followed.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 10, 2026
  • CVE-2026-91241CVSS 9.1
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Analytics Web Administration). Supported versions...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121683CVSS 9.4
    Missing authentication in Ivanti Cloud Services Application version 5.0.8 allows a remote unauthenticated attacker to add and delete...
    📅 Updated: Nov 10, 2026
  • CVE-2026-83283CVSS 9.8
    Vulnerability in the Oracle Business Intelligence Enterprise Edition product of Oracle Analytics (component: Platform Security). The supported version...
    📅 Updated: Nov 10, 2026
  • CVE-2026-108186CVSS 9.6
    Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of...
    📅 Updated: Nov 10, 2026
  • CVE-2026-121653CVSS 9.8
    SQL injection in the Core of Ivanti Endpoint Manager before version 2024 SU8 allows a remote unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125758CVSS 9.1
    Aptabase before commit 61d4c01 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge sign-in links by...
    📅 Updated: Nov 10, 2026
  • CVE-2026-125757CVSS 9.4
    mailcow: dockerized before 2026-11 contains a server-side template injection vulnerability that allows domain administrators to execute commands in...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.