Skip to content
November 21, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • Google makes Go to become the preferred language for cloud app development
  • Technology

Google makes Go to become the preferred language for cloud app development

Do Son July 28, 2018 2 minutes read
Go cloud app development

Google’s Go language is one of the fastest growing programming languages today and currently has around 1 million active developers worldwide. But Google believes that Go still has growth potential, especially in writing cloud applications. To this end, Google recently launched a new open source project, Go Cloud, to make it easier to build cloud applications using Go.

Google said that while Go is very popular with developers, the language lacks a standard library for connecting to cloud services, and developers often need to write their libraries to use the various cloud features. The emergence of Go Cloud is the desire to easily migrate between clouds, providing a set of open, universal cloud APIs for accessing Blob storage, MySQL databases and runtime configuration, as well as built-in logging, tracing, and health checks. HTTP server.


Go Cloud currently provides support for AWS and Google Cloud Platform. Over time, Google plans to add more features to Go Cloud and support more cloud providers.

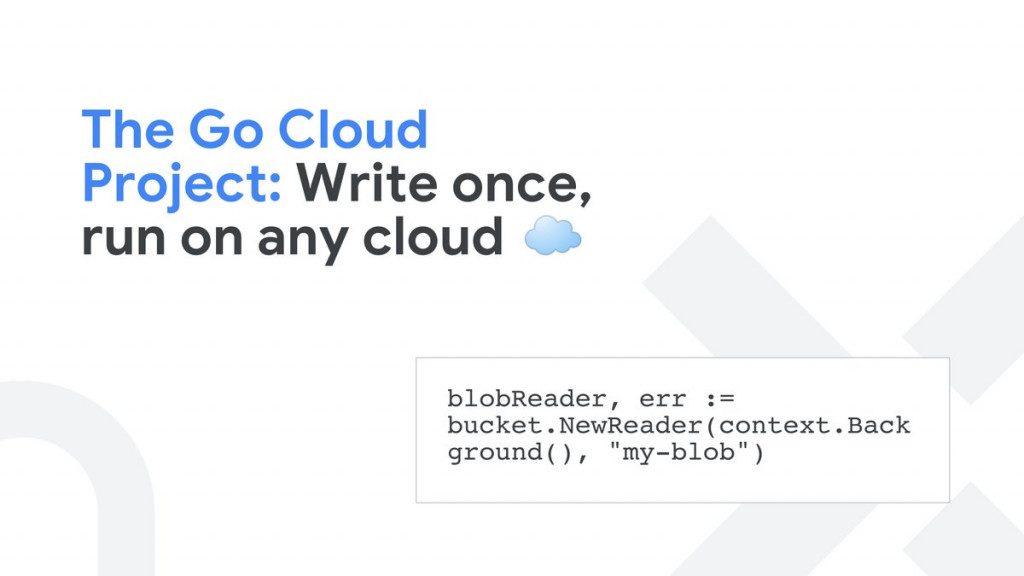
Go Cloud’s slogan is “Write once, run on any cloud”, and Google believes that Go Cloud will allow development teams to build applications that run quickly on any supported cloud without having to rebuild most of their applications.

The Go Cloud Project: Write once, run on any cloud.

One set of objects & methods that work w/ any cloud provider means your application code doesn't need to be aware of which backend provider you use or even if you are using multiple providers → https://t.co/7nbGqZym81 pic.twitter.com/JLhNNTtEfQ

— Google Cloud Tech (@GoogleCloudTech) July 26, 2018

As Google VP Adam Seligman said, the company hopes that this move will lead to an explosion of standard libraries around Go, ultimately accelerating Go as the language of choice for cloud application development.

Via: TechCrunch 

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Samsung Teases Galaxy Z Fold7 “Ultra”: AI, VR & Next-Gen Foldable Tech!
  • Clarity Fix: iOS 26.1 Launches with Liquid Glass Tint Option & Camera Gesture Toggle
  • From Vision to Validation: Ericsson Unveils the “Superbrain” of 6G with First Live OTA Trials at MWC 2026
  • Claude Sonnet 4 Gets a Massive 1-Million-Token Context Window for Enterprise Developers
  • Gmail’s Identity Revolution: How to Change Your Email Address Without Losing Data
  • Google Unveils Enhanced Baseband Security for Pixel 9
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: cloud app development go

🚨 Active Exploits in the Wild

  • CVE-2026-133968CVSS 9.8
    monailabel (aka MONAI Label) through 0.8.5 allows directory traversal, with resultant remote code execution, via the image parameter...
    Watchtower Verified📅 Updated: Nov 21, 2026
  • CVE-2025-42884CVSS 6.5
    SAP NetWeaver Enterprise Portal allows an unauthenticated attacker to inject JNDI environment properties or pass a URL used...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-76466CVSS 9.8
    A vulnerability in the database service feature of Cisco Expressway Series could allow an unauthenticated, remote attacker with...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-129448CVSS 9.8
    Deserialization of Untrusted Data in Apache Roller versions 4.0.0 through 6.1.4 allows an unauthenticated remote attacker to execute...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    CISA KEV📅 Added to KEV: Nov 20, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-123710CVSS 9.8
    A flaw was found in Red Hat Quay. An unauthenticated client can obtain an anonymous registry token with...
    📅 Updated: Nov 21, 2026
  • CVE-2026-110697CVSS 9.9
    A flaw was found in Quay where the robot account listing function constructs a SQL LIKE pattern from...
    📅 Updated: Nov 21, 2026
  • CVE-2026-133968CVSS 9.8
    monailabel (aka MONAI Label) through 0.8.5 allows directory traversal, with resultant remote code execution, via the image parameter...
    📅 Updated: Nov 20, 2026
  • CVE-2026-130158CVSS 9.0
    RepoManager is a self-hosted deb/rpm package repository. Prior to 5.13.3, a registered host or a party with its...
    📅 Updated: Nov 20, 2026
  • CVE-2026-125294CVSS 9.8
    The Nexter Blocks Pro plugin for WordPress is vulnerable to Privilege Escalation in all versions up to, and...
    📅 Updated: Nov 20, 2026
  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    CISA KEV📅 Added to KEV: Nov 20, 2026📅 Updated: Nov 20, 2026
  • CVE-2026-76466CVSS 9.8
    A vulnerability in the database service feature of Cisco Expressway Series could allow an unauthenticated, remote attacker with...
    CISA KEV📅 Added to KEV: Nov 20, 2026📅 Updated: Nov 20, 2026
  • CVE-2026-129448CVSS 9.8
    Deserialization of Untrusted Data in Apache Roller versions 4.0.0 through 6.1.4 allows an unauthenticated remote attacker to execute...
    CISA KEV📅 Added to KEV: Nov 20, 2026📅 Updated: Nov 20, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.